

deepsecrets
 ntoskernel/deepsecrets
Offline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
defensive-toolsstatic-analysisvulnerability-scanners+5
184
ntoskernel/deepsecretsOffline secrets scanner combining regex rules, lexer-based semantic analysis, and hashed-value matching to detect exposed credentials in code with…
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 project-oak/oak
Meaningful control of data in distributed systems.
 github/advisory-database
Security vulnerability database inclusive of CVEs and GitHub originated security advisories from the world of open source software.
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 betterleaks/betterleaks
Fast, configurable secrets scanner for filesystems, git history, containers, and cloud sources, with Expr-based filtering, credential validation, and…

 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
 odomojuli/regextokens
list of regex patterns for oauth / api tokens with provided source
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 disrex-group/stylesmuggler-adobe-patches-mageos
composer require delivery of Adobe's official APSB26-146 (CVE-2026-75650) fix for Mage-OS stores, via cweagans/composer-patches. Companion to…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 fluidattacks/makes
A software supply chain framework powered by Nix.
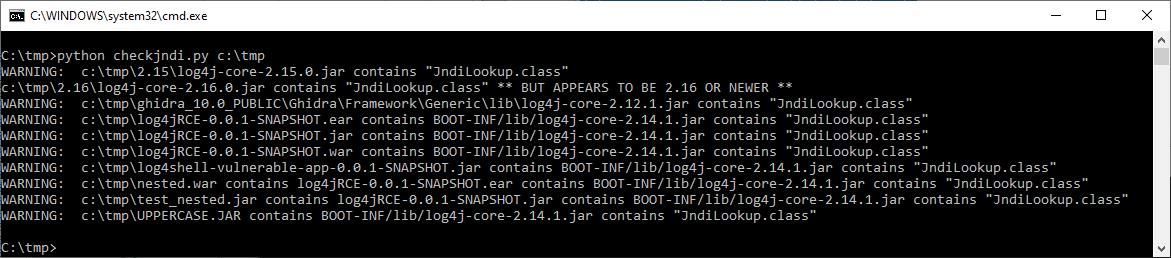 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228