
wrongsecrets-binaries
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
binary-analysiscode-analysisctf+6
122 days ago
owasp/wrongsecrets-binariesSource code for the Binaries of OWASP WrongSecrets
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
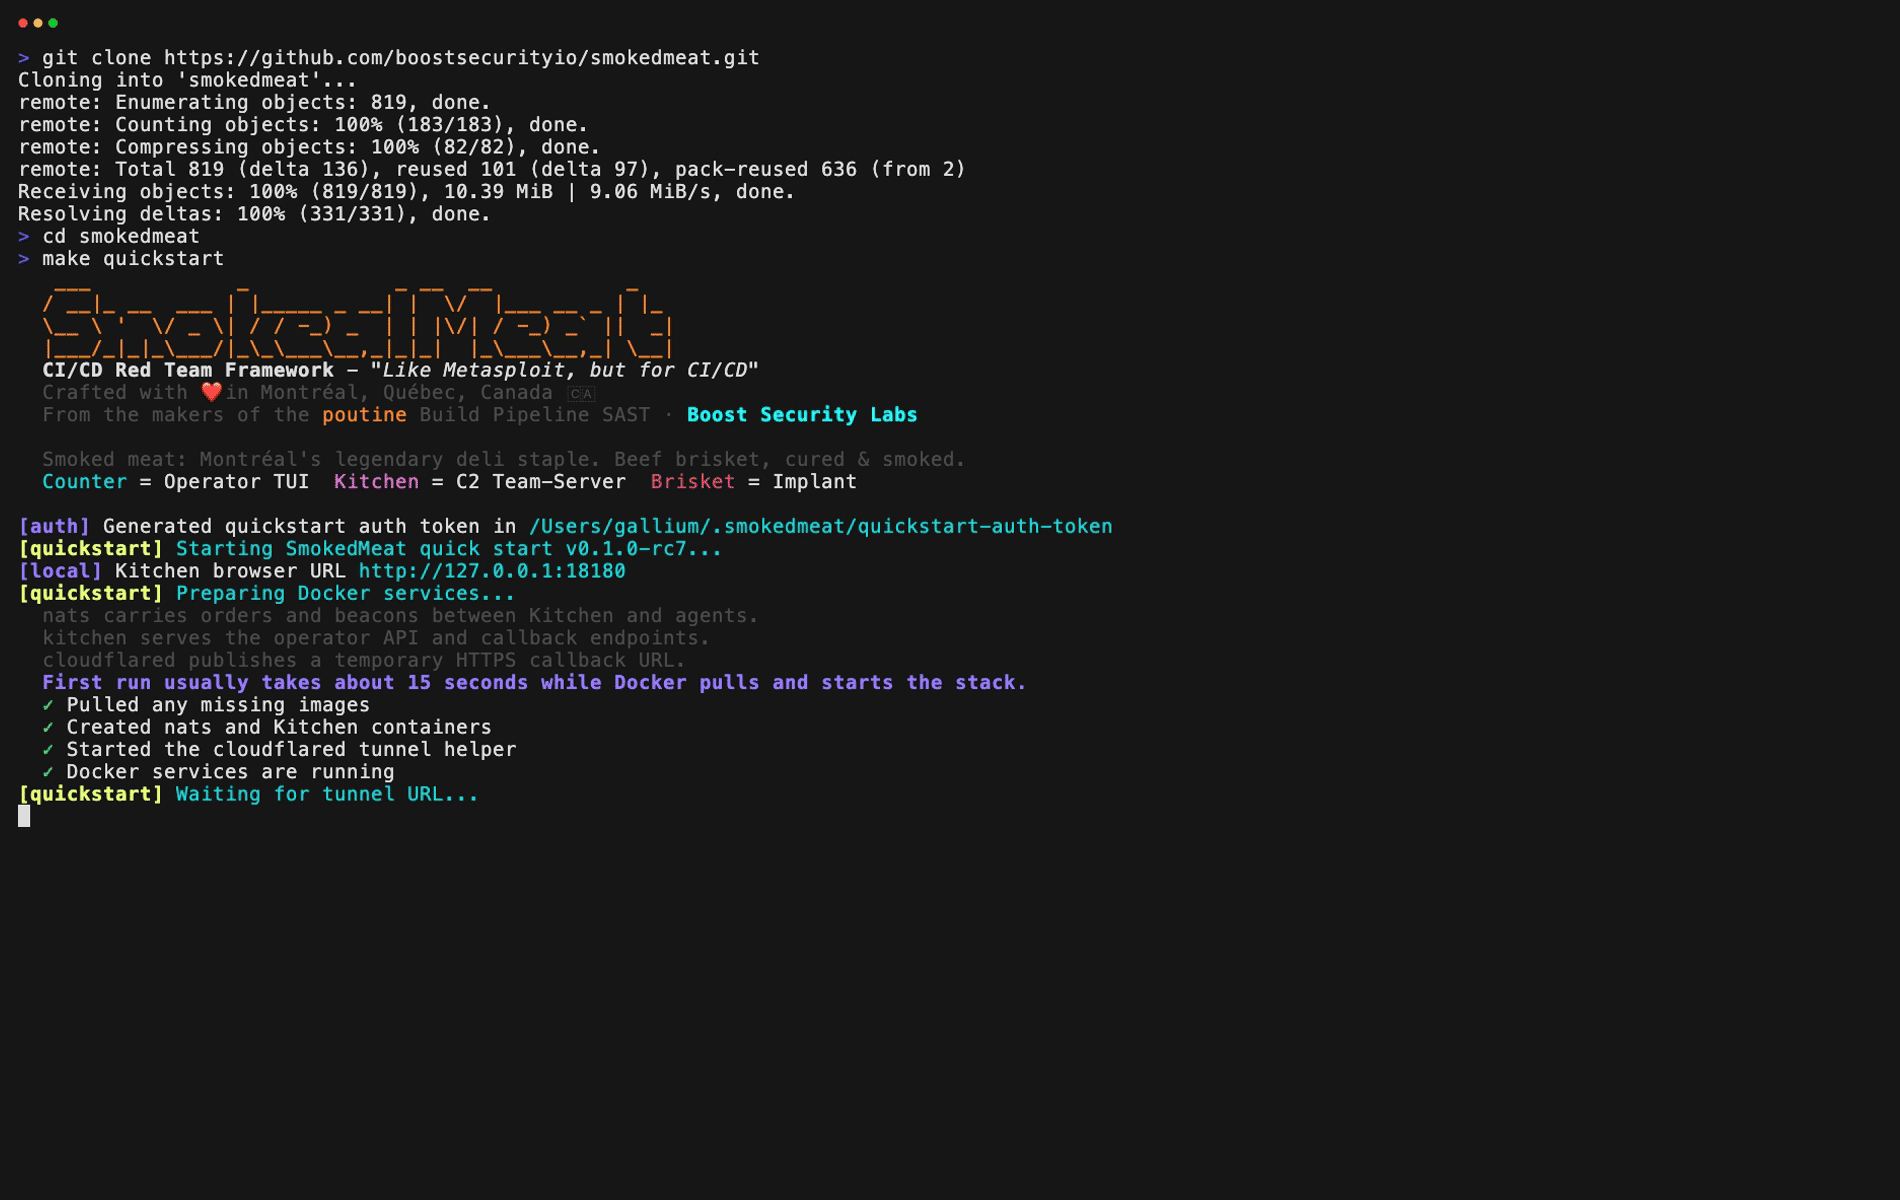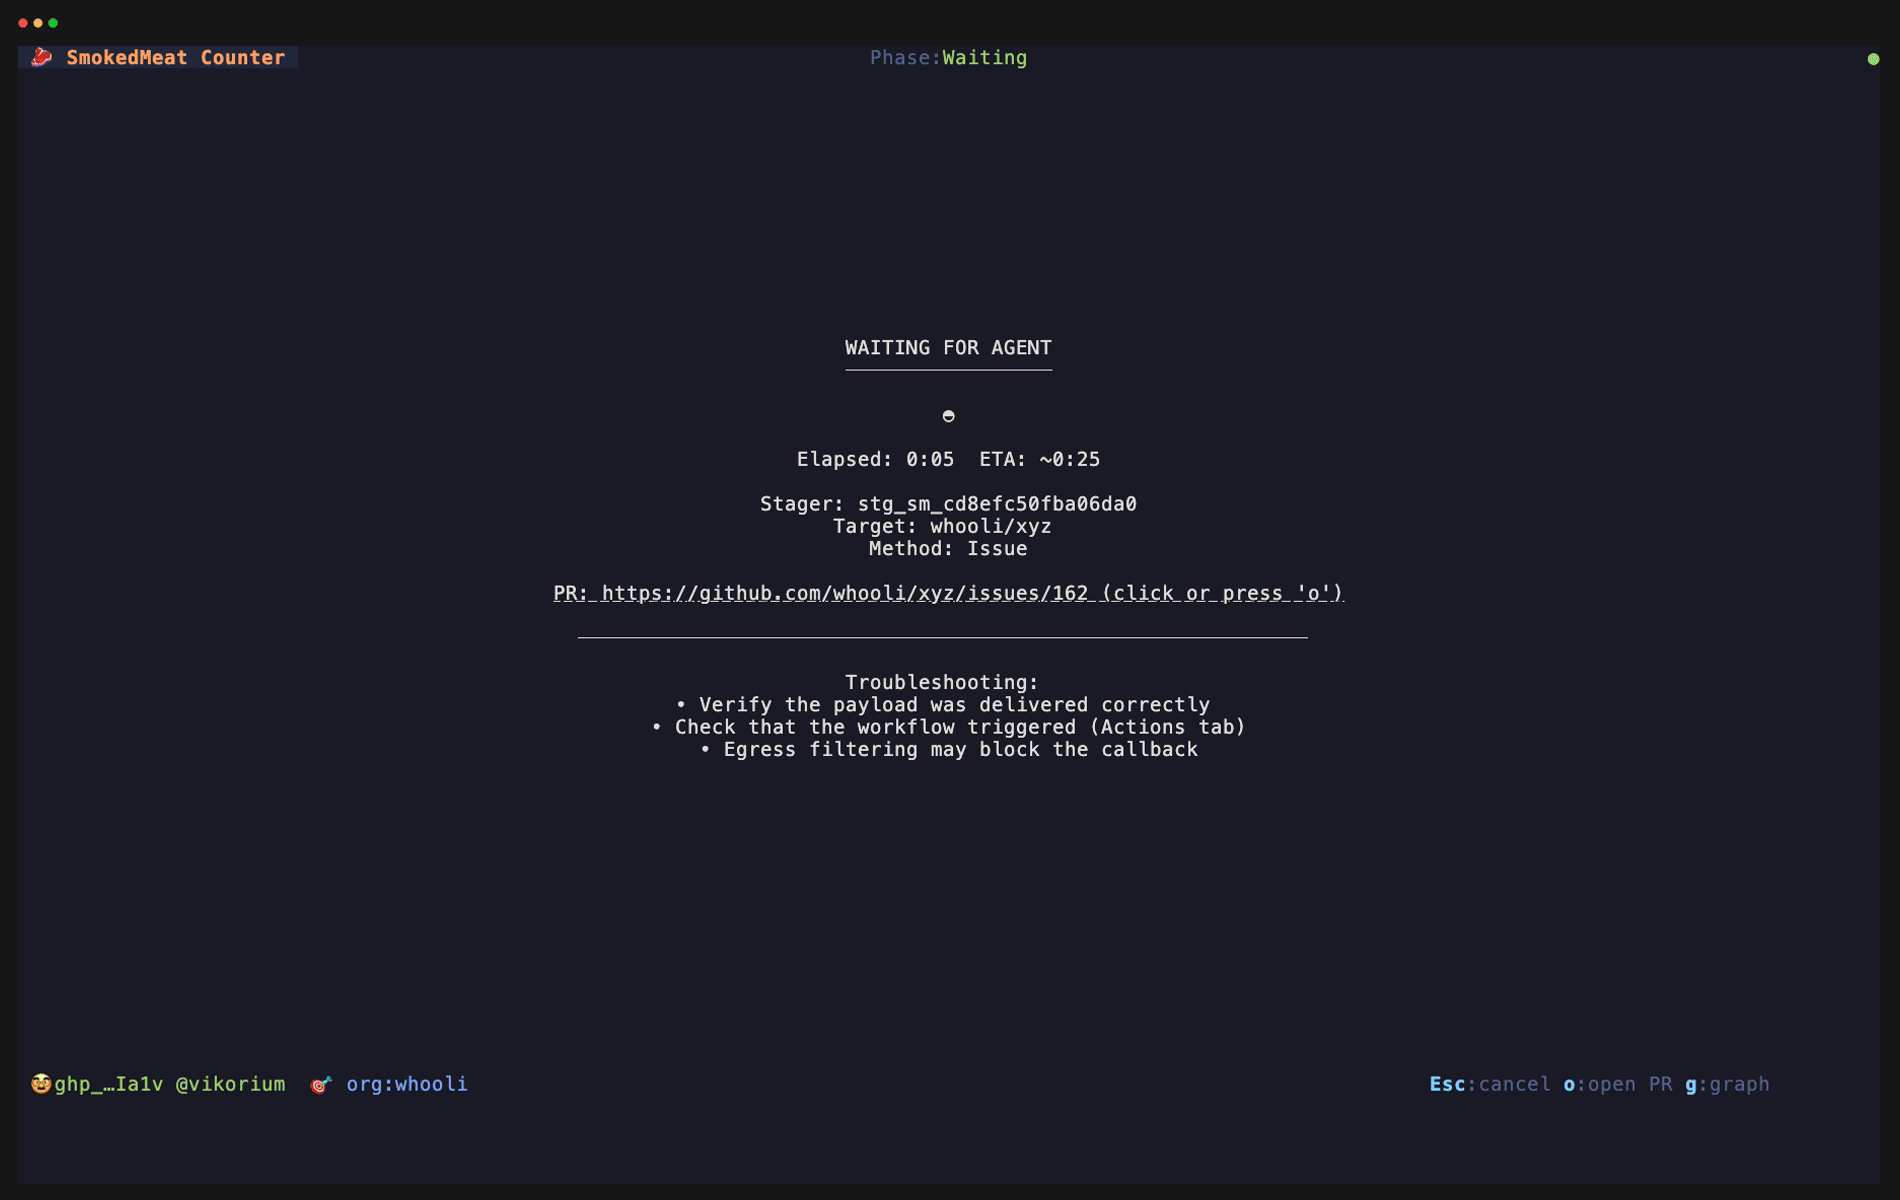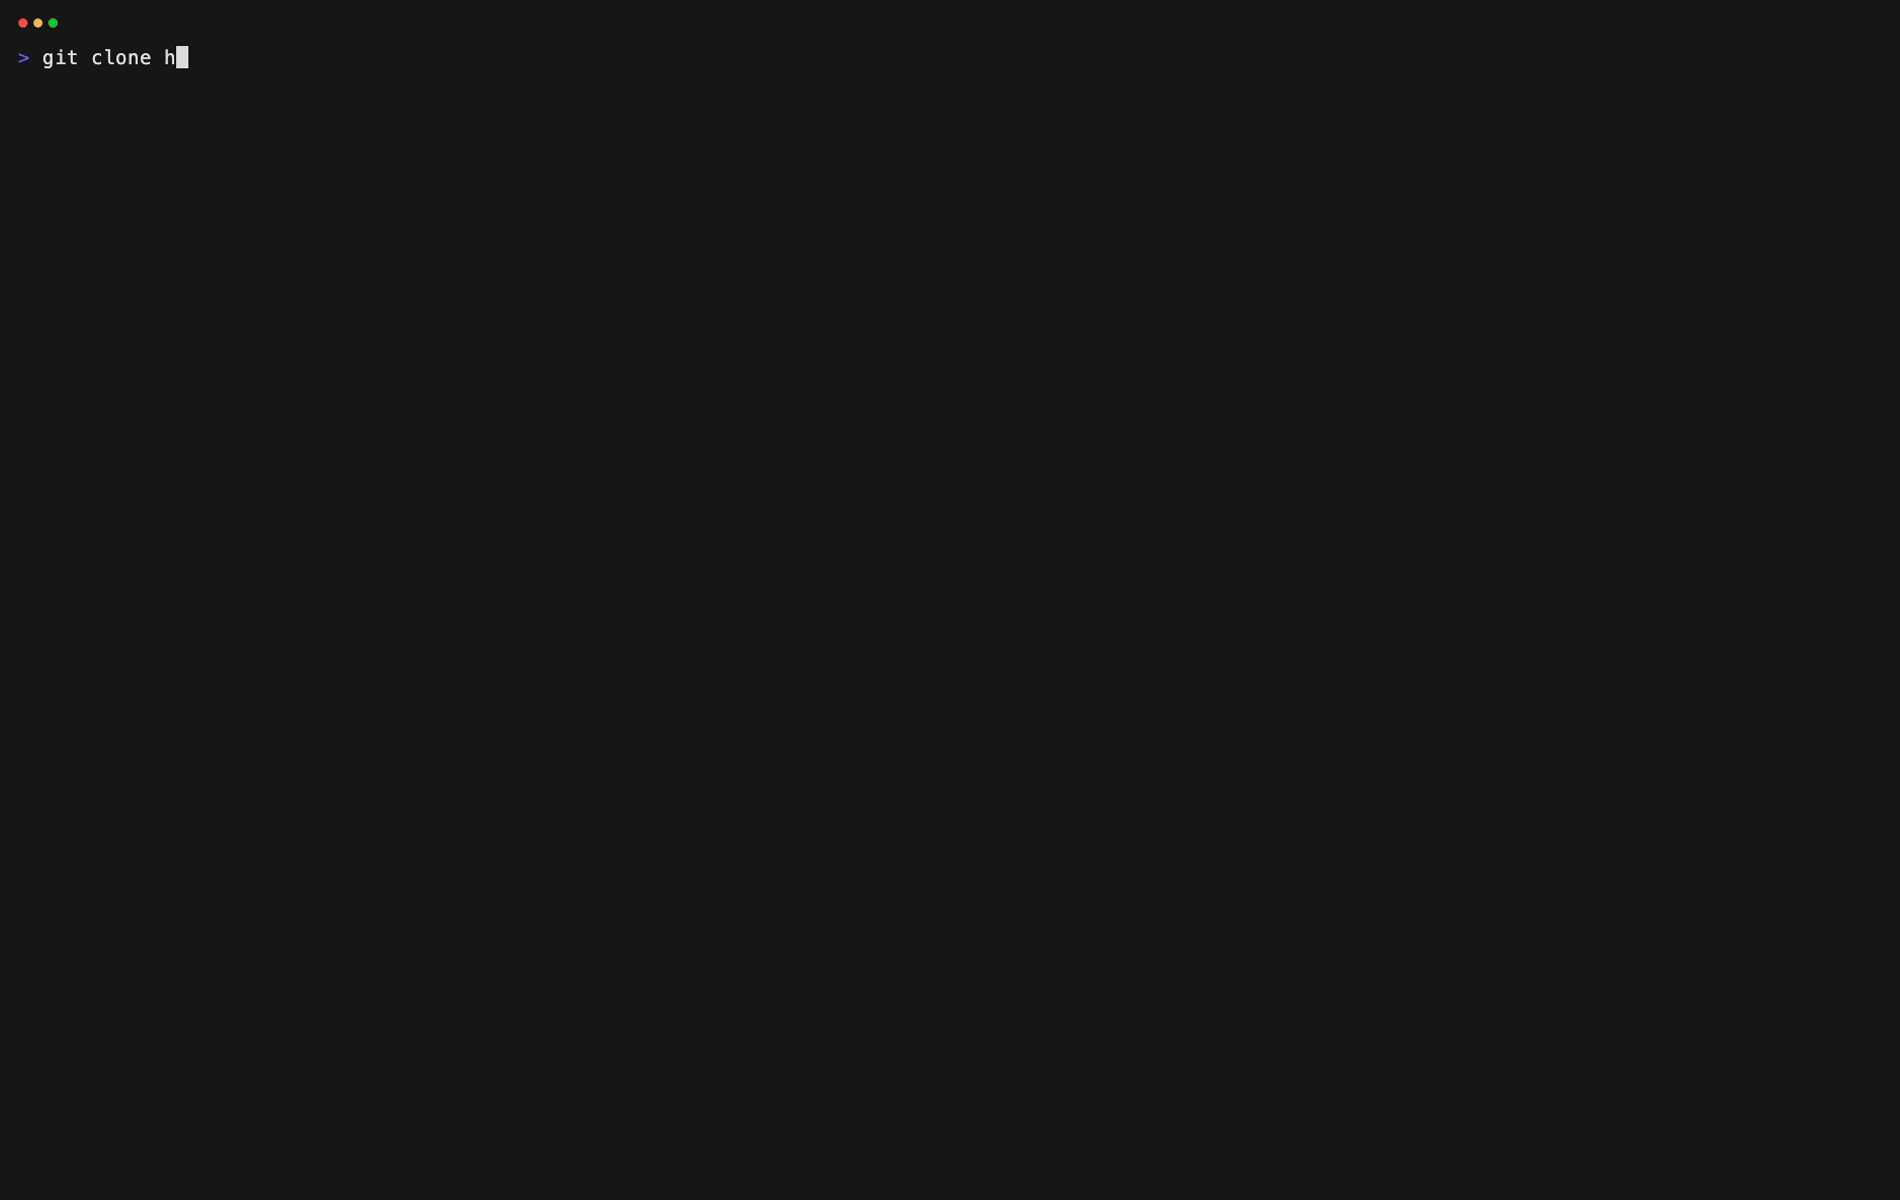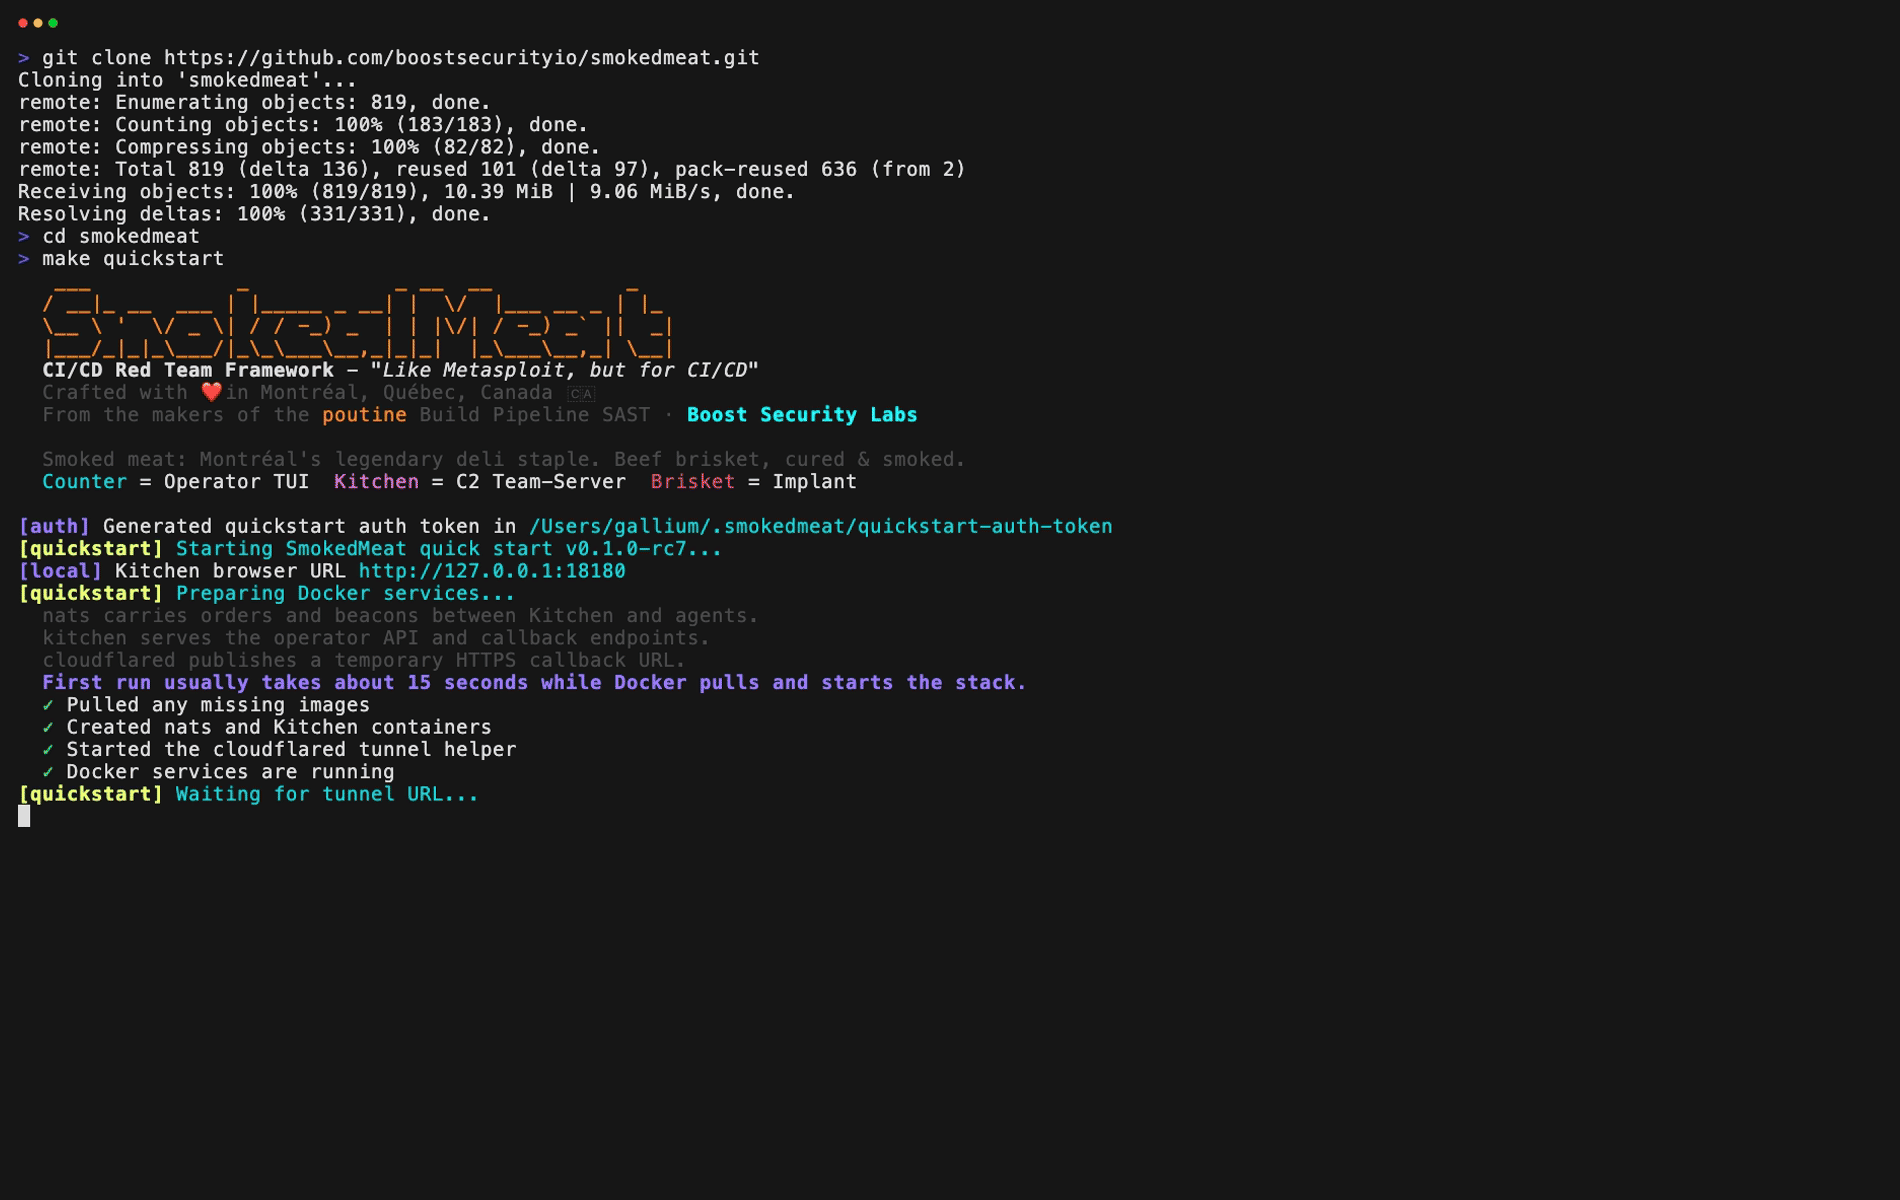 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 namegabevictoire01-sys/cs50-cybersecurity-final-project
CS50 Cybersecurity Final Project - Analysis of CVE-2024-3094
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 saku0512/cve-2026-84361-poc
Proof-of-concept for CVE-2026-84361, demonstrating command injection in Composer's Perforce driver via malicious P4PORT, with Docker-based…
 pvharmo2/gha-lab-40e23db109
Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…
 sshwarts/skillscript
Skillscript — a small declarative language for authoring agent workflows. Runtime, compiler, and CLI.
 pvharmo2/gha-lab-232af4821f
Security-research lab reproducing CVE-2021-4281 (GHSA-3796-3f93-cfvx): shell command injection via PR head-branch name in…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…