
spring-cvss-check
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
configuration-auditingdevsecopssupply-chain-security+2
xiaoqimikko/spring-cvss-checkScans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 super-vulnerable-org/compromised-action
Test repo: simulates CVE-2025-30066 style compromised GitHub Action (for security research/testing chainradar)
 paspke/scavenger_scanner
Detect CVE-2025-54313 eslint-config-prettier supply chain attack IOCs on Windows
 hexbornestudio/atlas-tj-actions-poc
PoC for CVE-2025-54416 tj-actions/branch-names command injection
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
 graypixel2121/cve-2025-69604
Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…
 nurjaman2004/jspdf-bulk-detector-cve-2025-68428-
Asset-wide detection tool for identifying jsPDF usage related to CVE-2025-68428 Detection only — no exploitation
 soliantconsulting/cve-2025-46295-fix-fms
Automated script suite to detect and remediate CVE-2025-46295 by replacing vulnerable Apache Commons JARs in FileMaker Server installations with…
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 rashedhasan090/cve-2025-55182-mitigator
CLI scanner that detects likely vulnerable React/Next.js dependencies for CVE-2025-55182 and provides mitigation targets. Supports JSON output and…
 vignesh21-git/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning
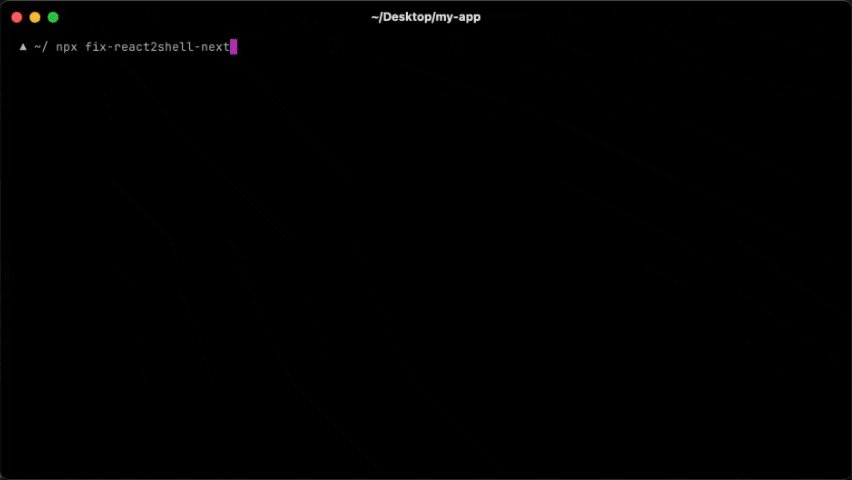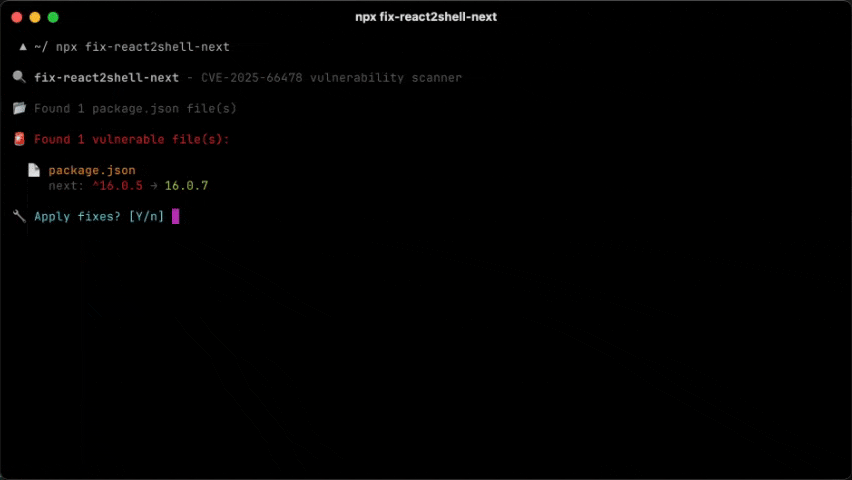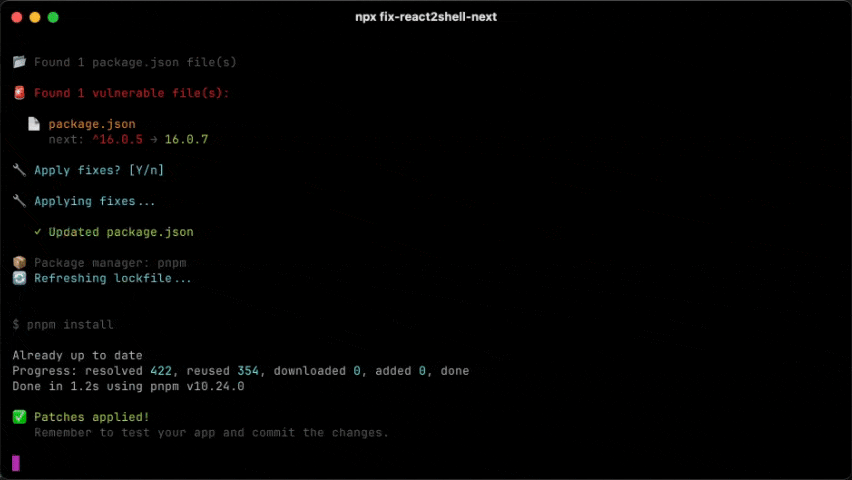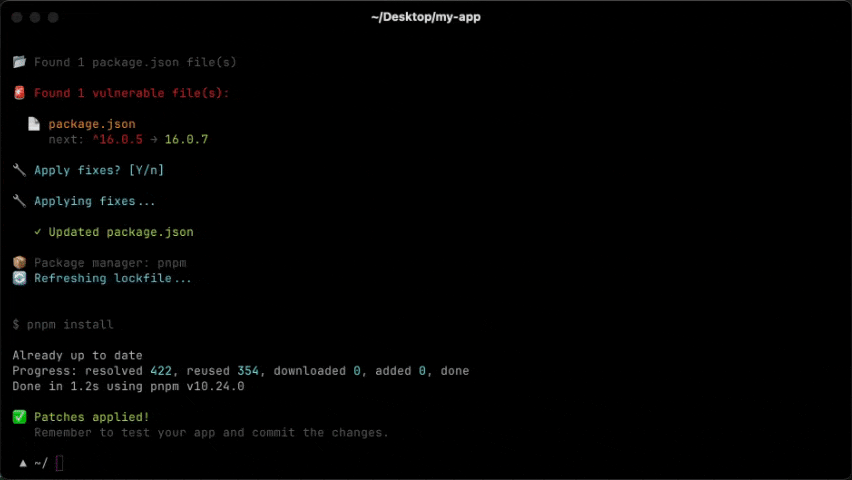 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 amir-malek/react-cve-2025-55182
Detects and fixes CVE-2025-55182 (React2Shell) in React Server Components and Next.js apps. Scans package versions, suggests safe upgrades, and…