

grype
 anchore/grype
A vulnerability scanner for container images and filesystems
container-escapecontainer-securitydevsecops+4
anchore/grypeA vulnerability scanner for container images and filesystems
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 sigstore/fulcio
Certificate authority issuing short-lived code-signing certificates tied to OpenID Connect identities, enabling verifiable software supply chain…
 sigstore/cosign
Code signing and transparency for containers and binaries
 certifi/python-certifi
(Python Distribution) A carefully curated collection of Root Certificates for validating the trustworthiness of SSL certificates while verifying the…
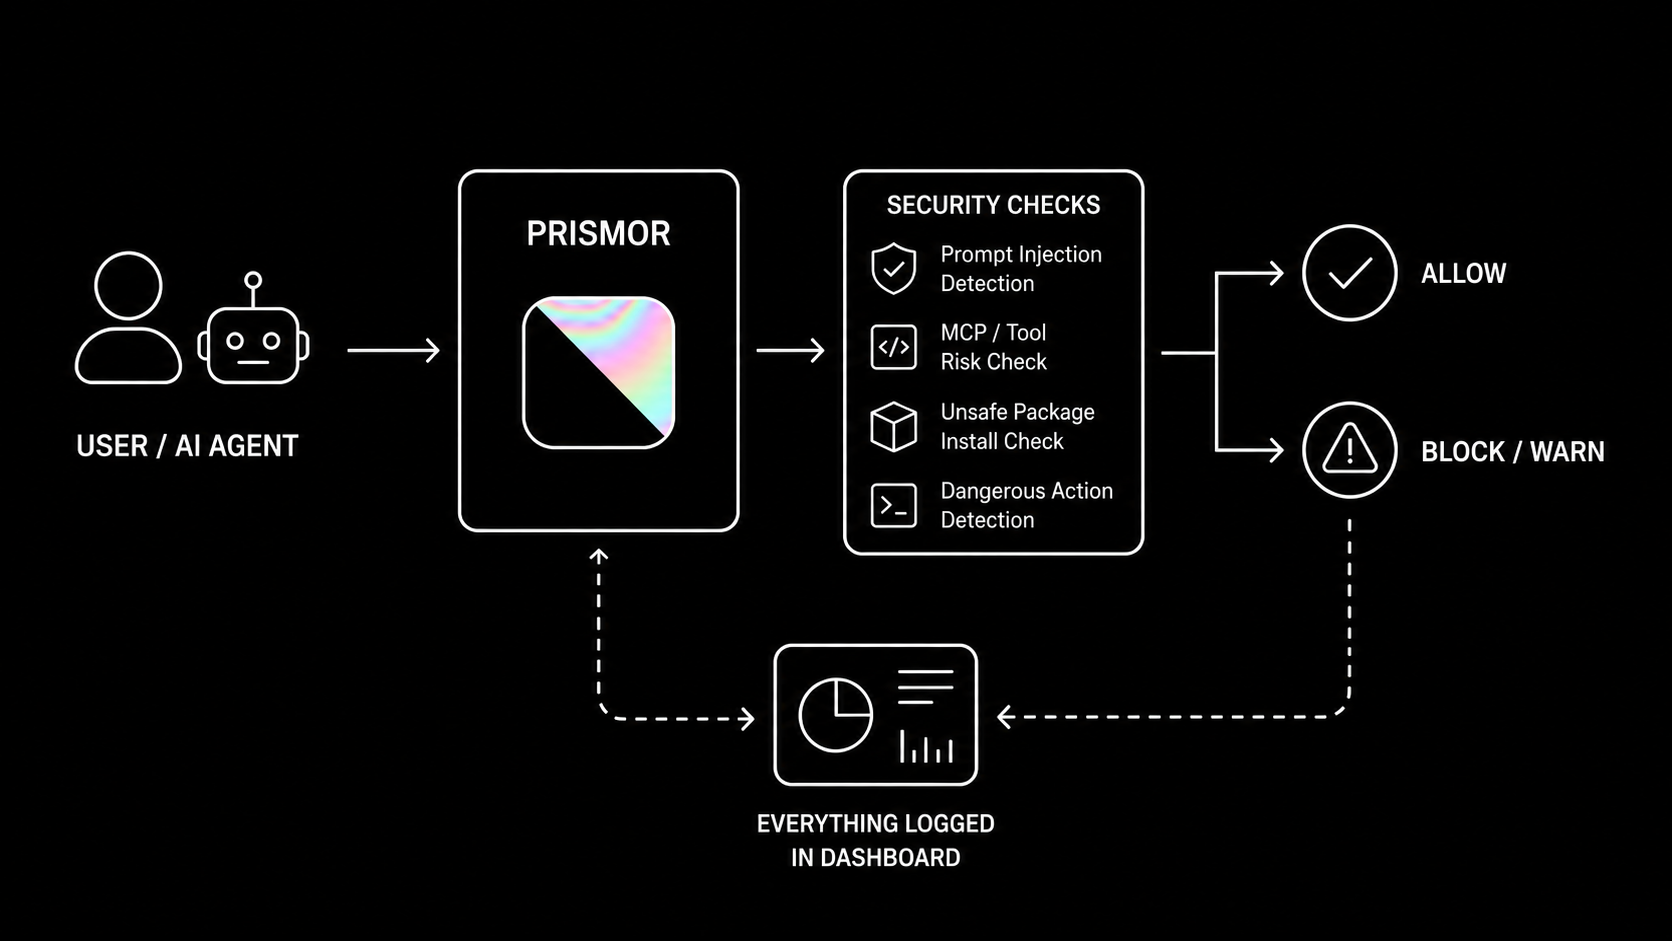 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 scopeblind/scopeblind-gateway
Fail-closed Cedar policy gate plus signed receipts for AI agent tool calls. npx protect-mcp
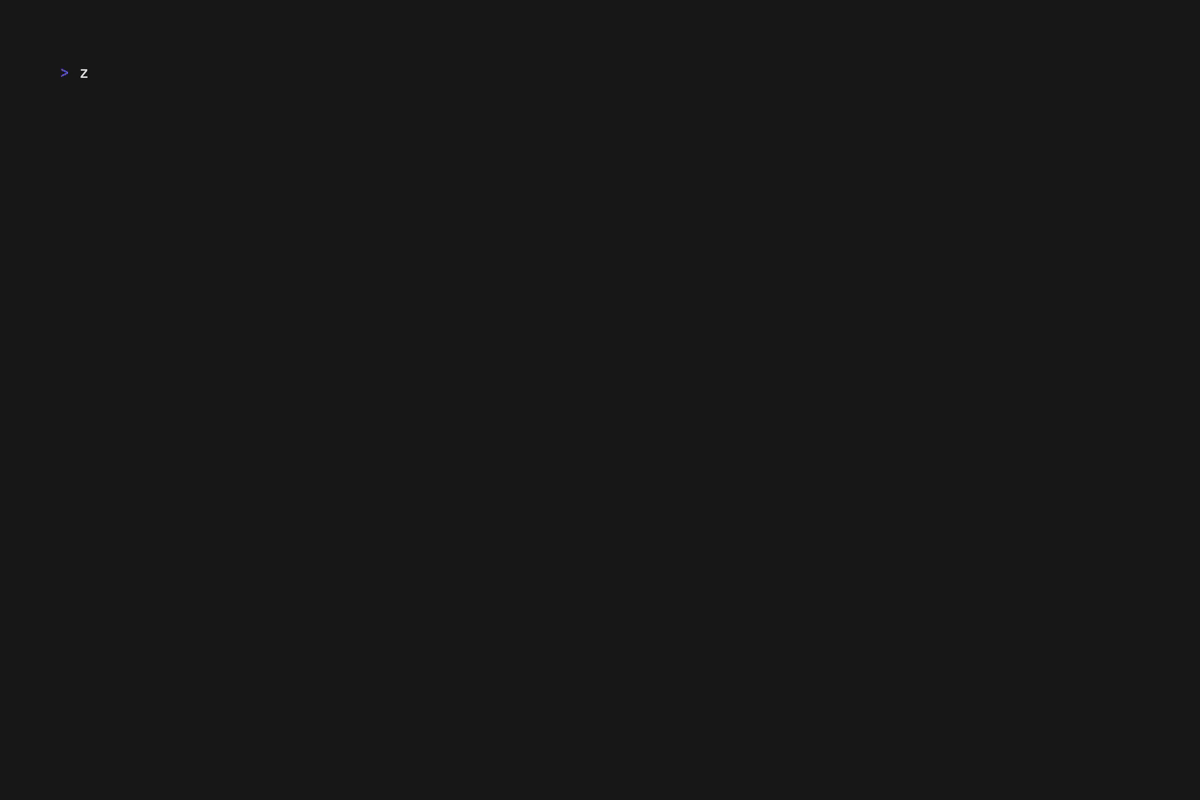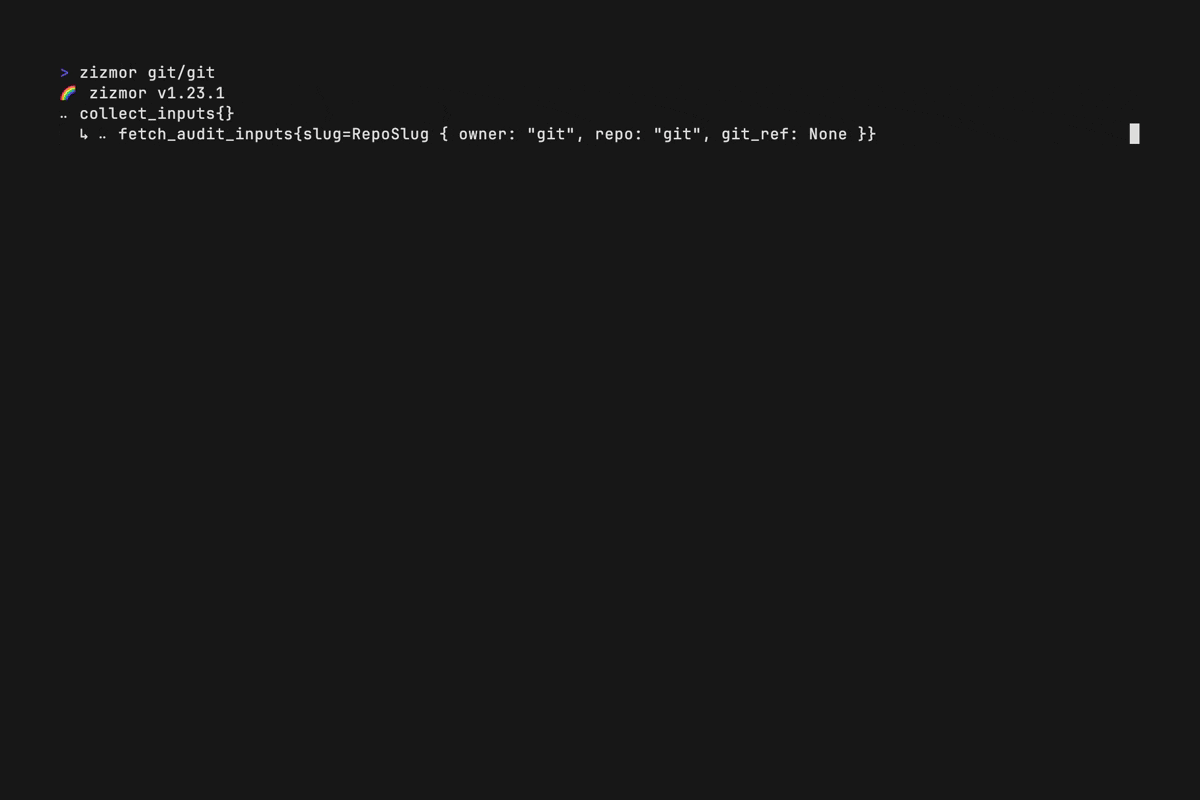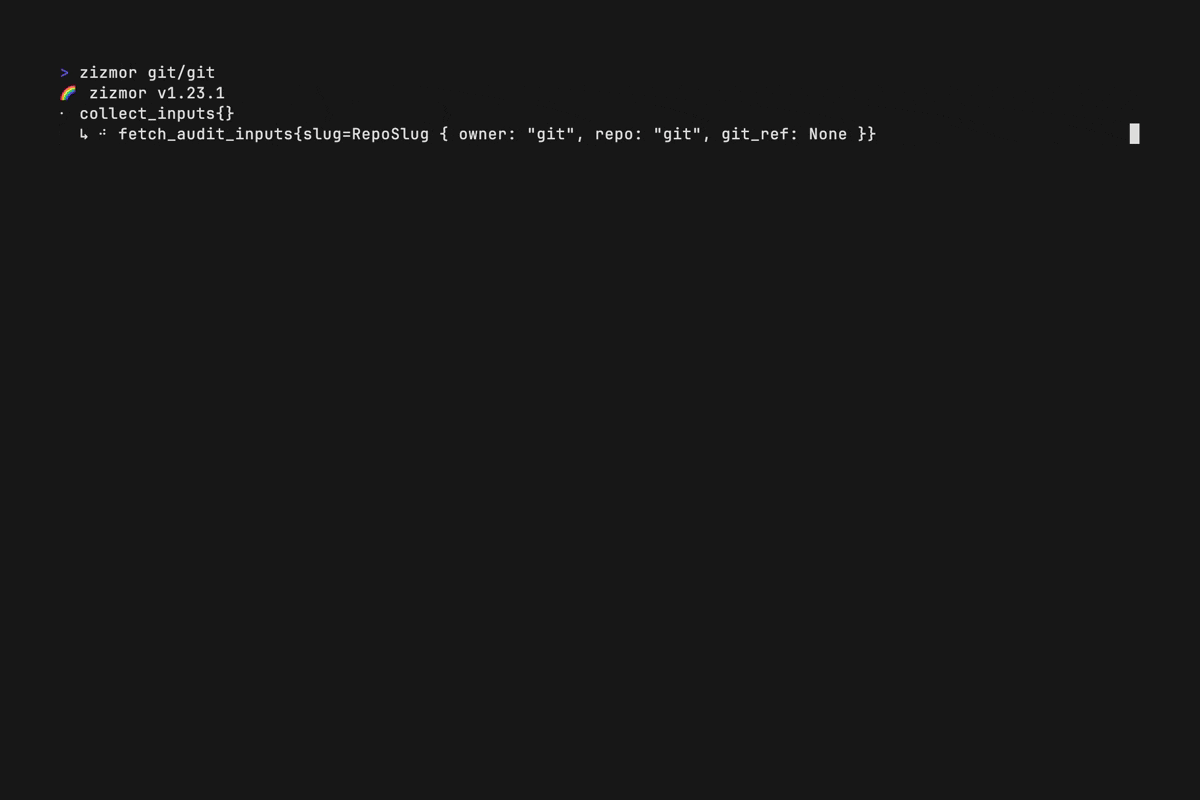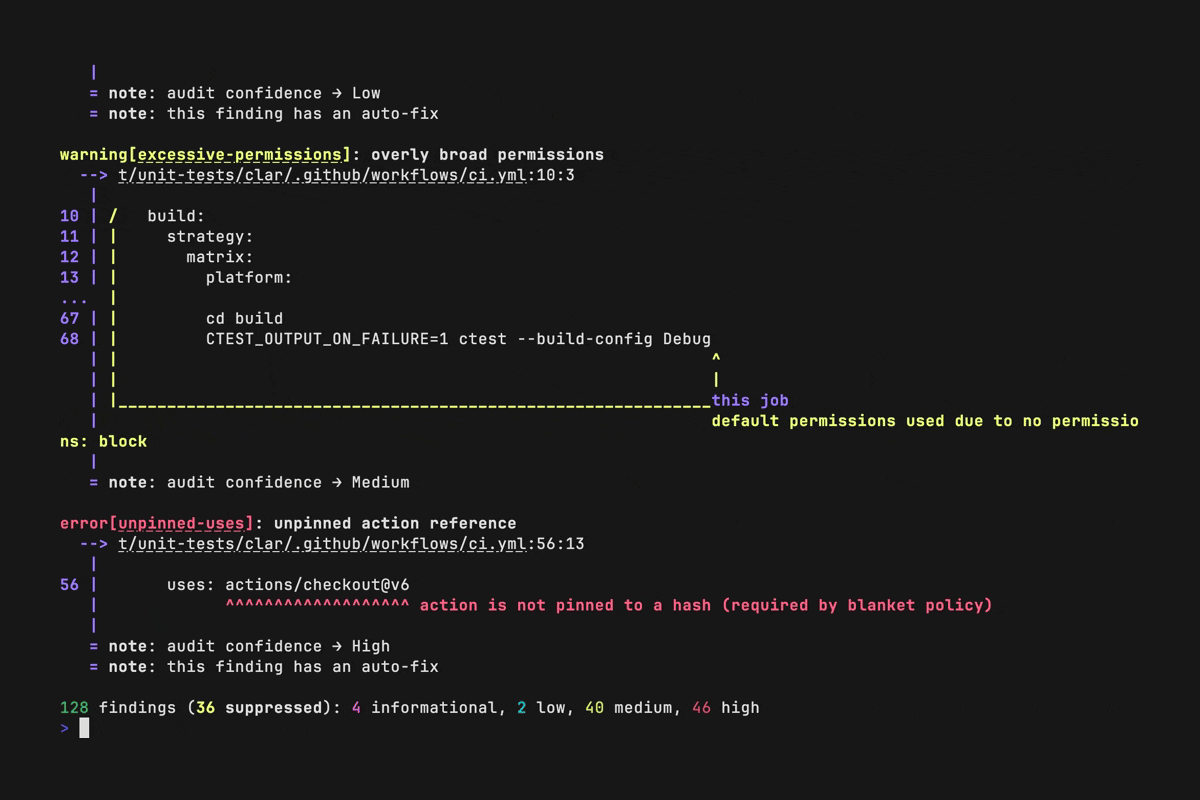 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
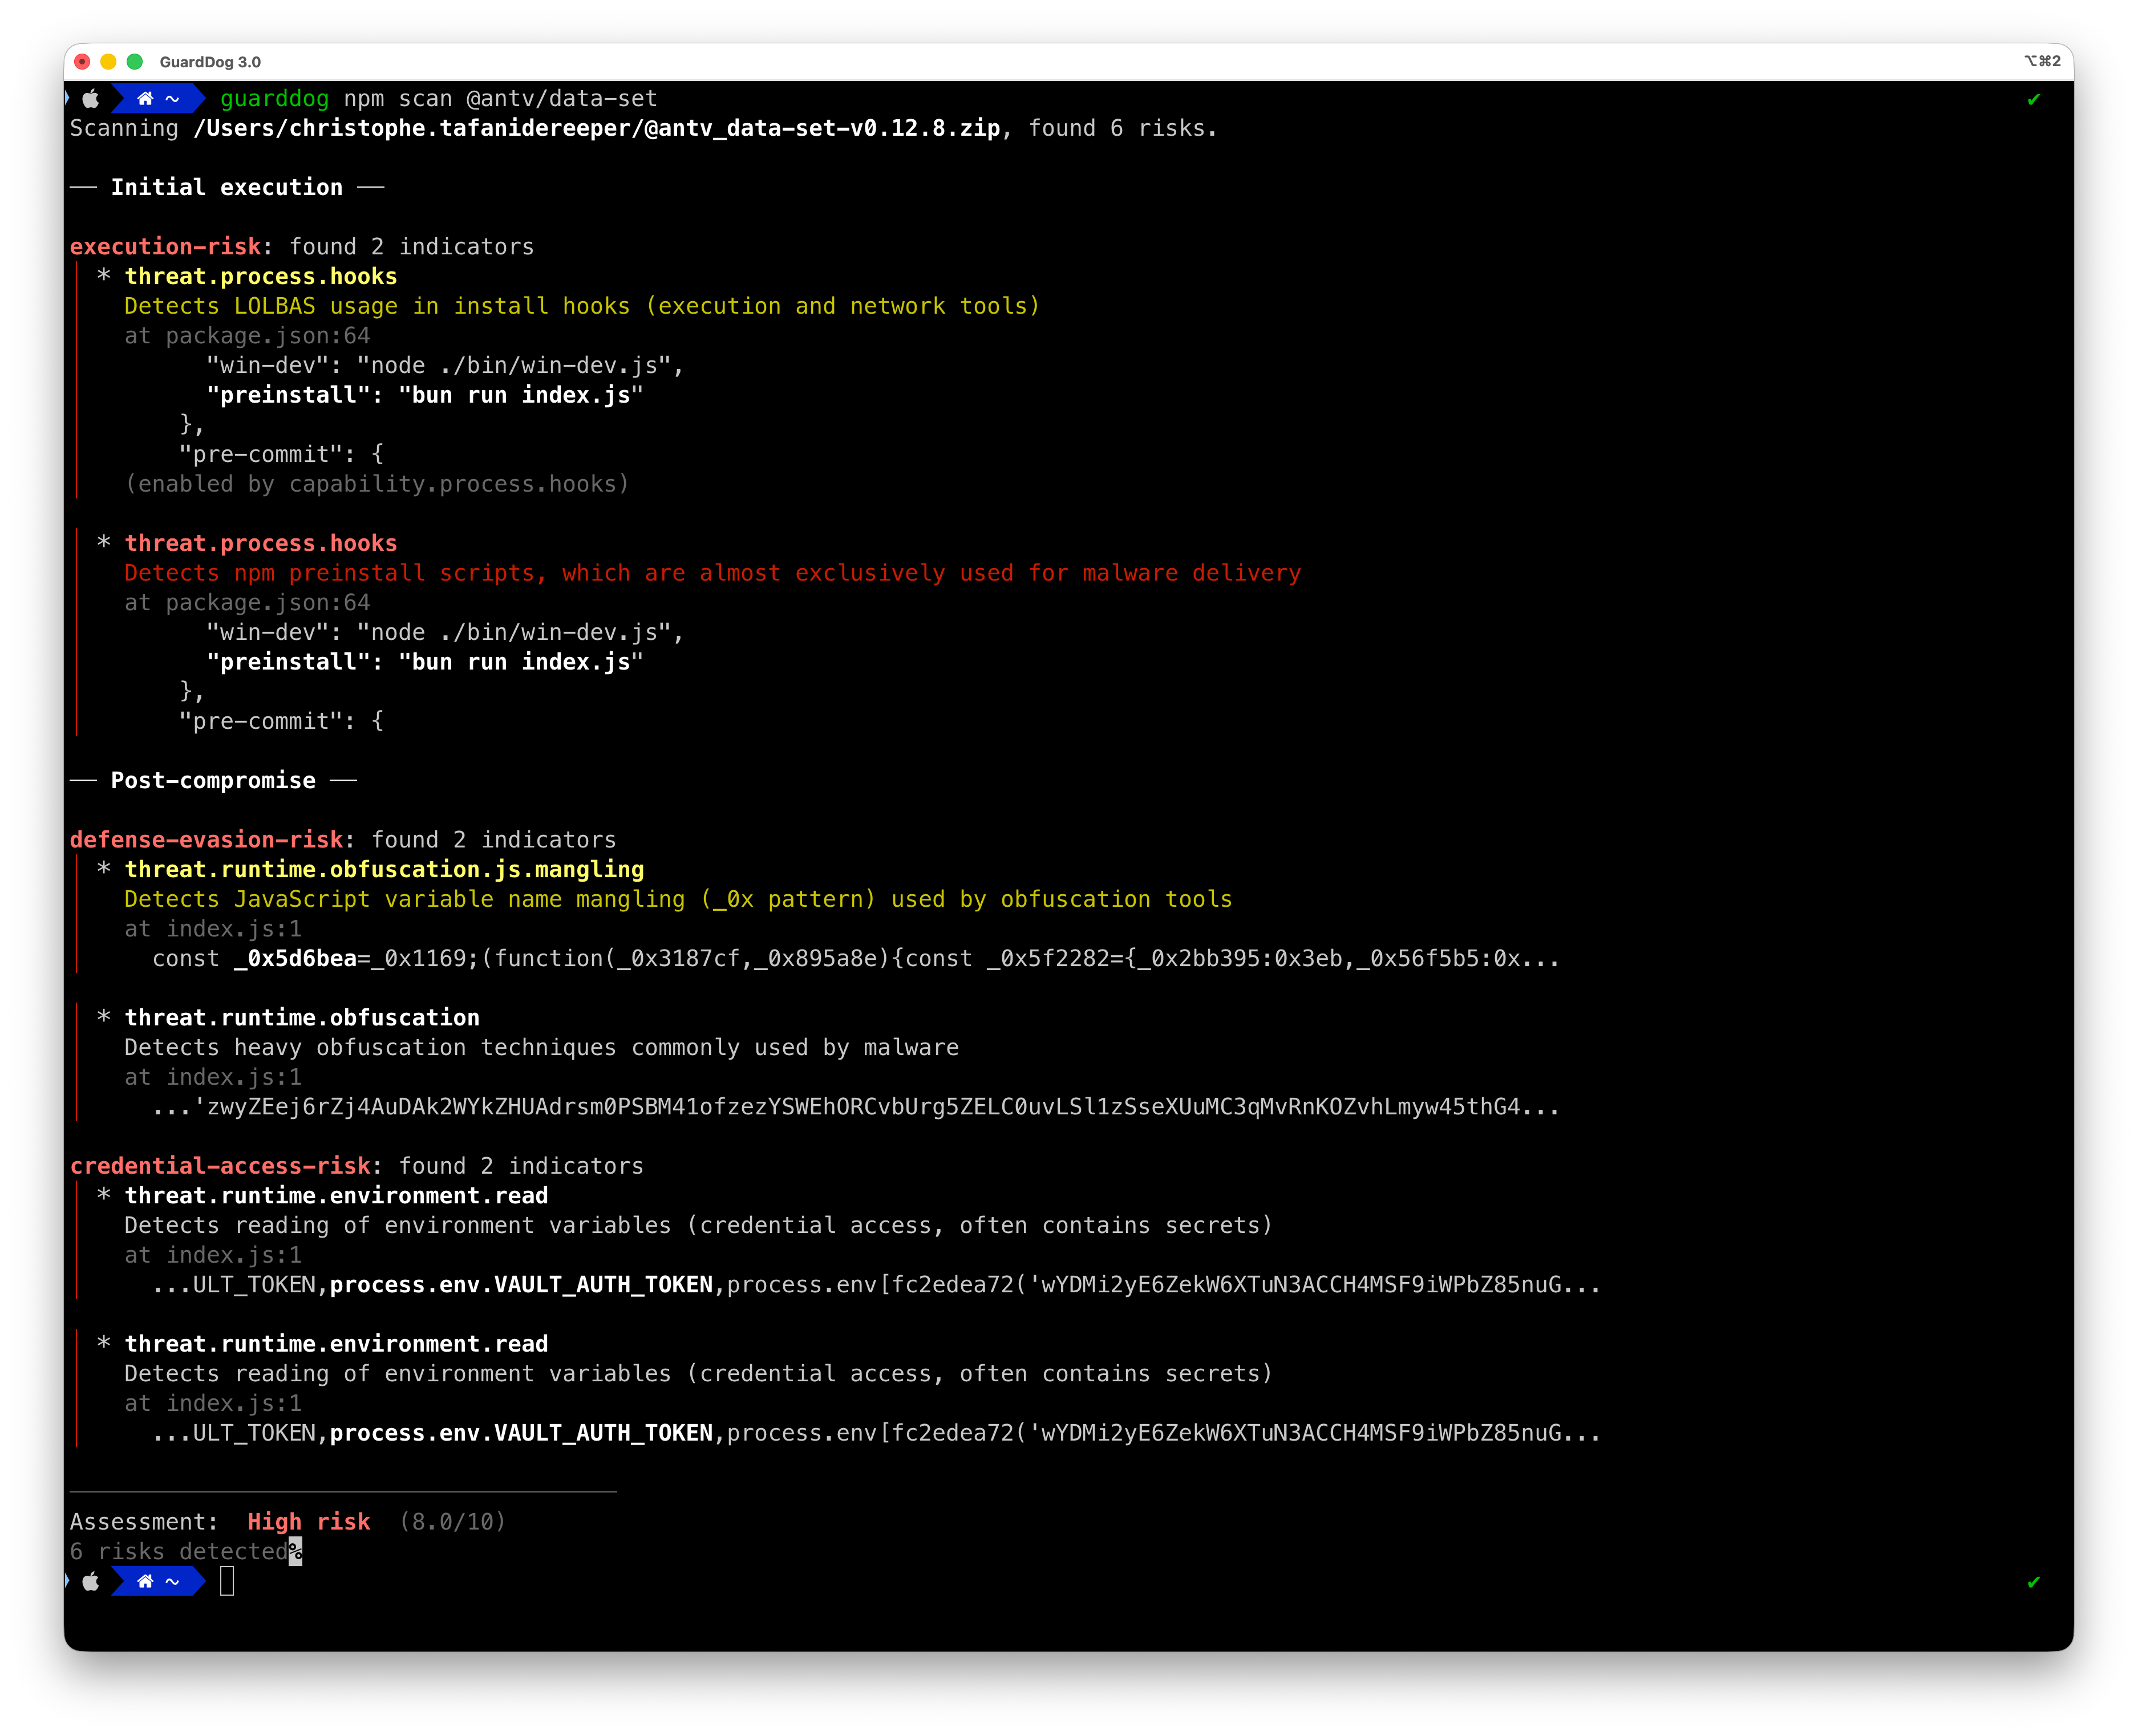 datadog/guarddog
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages
 vulncheck-oss/cli
VulnCheck's official command line tool
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…