

cdxgen
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
ai-securitycloud-securityconfiguration-auditing+6
1.1k
cdxgen/cdxgenCreates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…

 divyanshukumar0014/shipproof
SOC 2 evidence that collects itself in GitLab CI: every merge emits a signed bundle, an OPA gate blocks releases with missing proof, and auditors get…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 blackvectorops/semantic_firewall
Generate deterministic semantic fingerprints for Go functions. Detect xz-style backdoors and verify semantic equivalence using Static Single…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 platanor/hardware-compliance-handbook
AI-ready knowledge base of security & compliance regulations for hardware and connected-device manufacturers - structured, indexed, and…
 katekeiroz-dev/golang-x-text
golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24
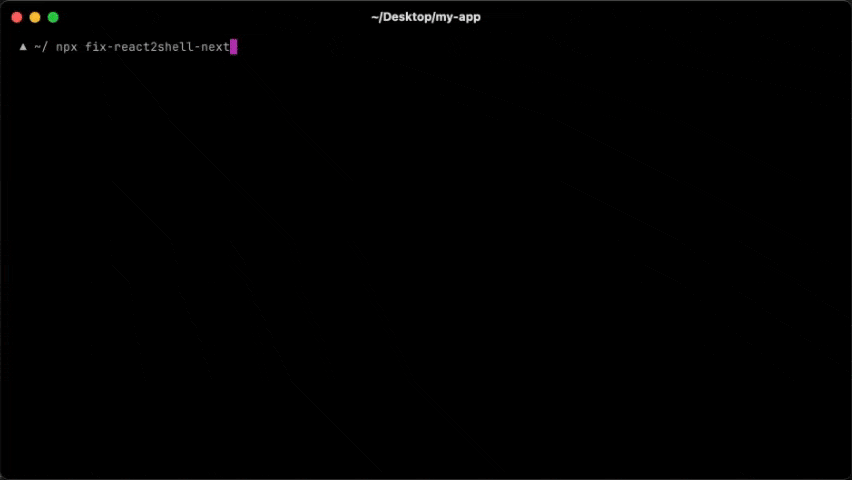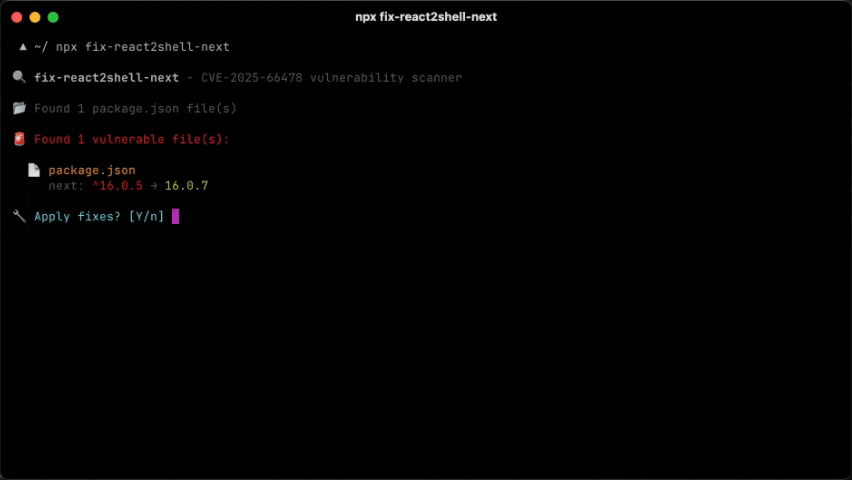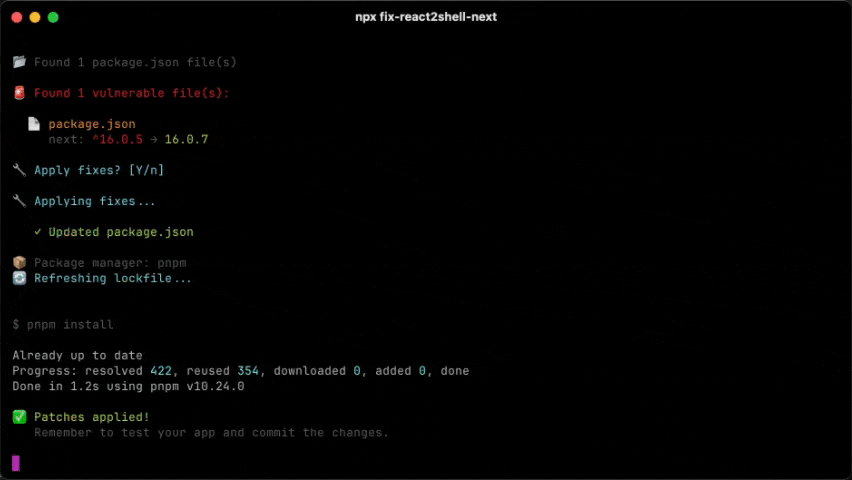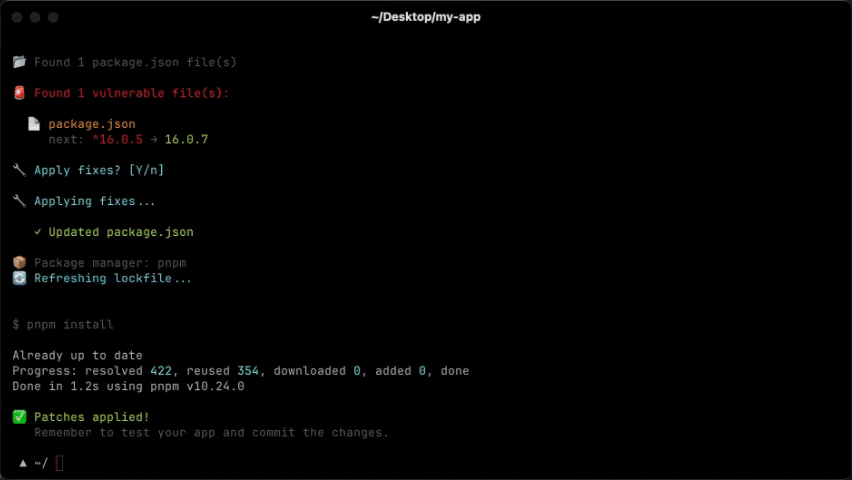 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 oopsiewoopsie/mc-log4j-patcher
CVE-2021-44228 server-side fix for minecraft servers.
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 mhaggis/package-inferno
A Public Package Scanner for The Community
 crazycatmyopic/cve
Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 graypixel2121/cve-2025-69604
Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…