
owasp-aibom
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
ai-securitycurated-resourcesdevsecops+3
12
owasp/owasp-aibomOWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
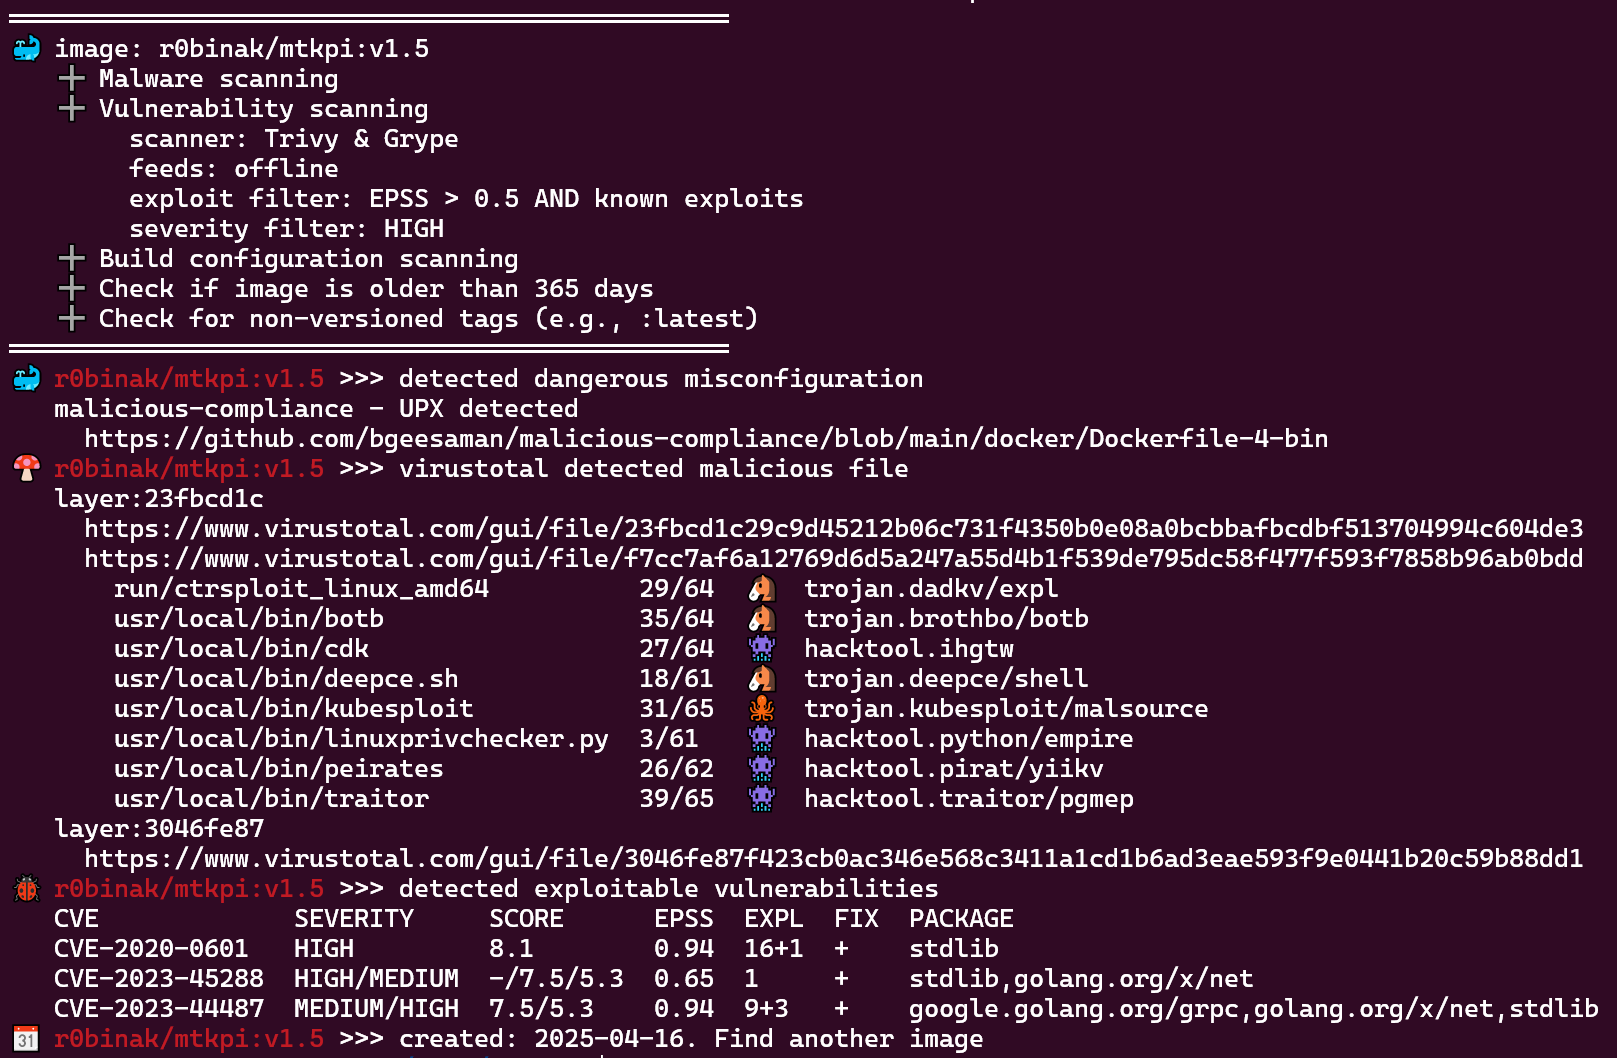 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
 rtvkiz/minimal
Minimal CVE Hardened container image collection
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning
 anchore/grype
A vulnerability scanner for container images and filesystems
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities