
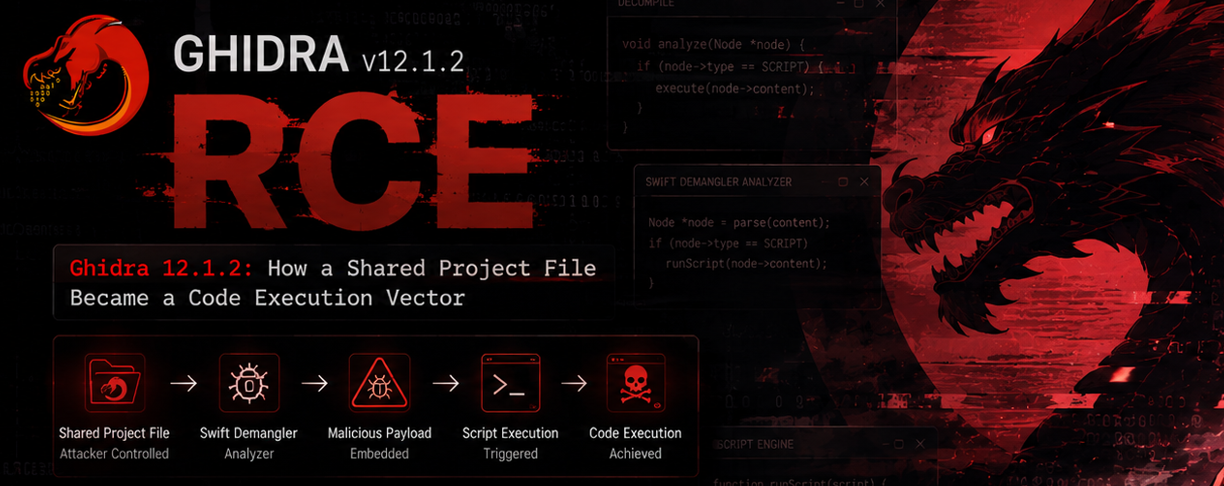
CVE-2026-18718
 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
code-analysisexploitationpayload-generation+2
1
sn0x-sharma/cve-2026-18718Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 george0papasotiriou/cve-2026-23001-hugging-face-transformers-model-deserialization-arbitrary-code-via-pickle-
Proof-of-concept for CVE-2026-23001: demonstrates RCE through unsafe pickle deserialization in Hugging Face Transformers by crafting a malicious…
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 bfengj/cve-2024-32002-exploit
Proof-of-concept exploit for CVE-2024-32002, a Git submodule vulnerability enabling arbitrary code execution via crafted repositories and symlinks.
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 theth1nk3r/cve-2020-27955
cve-2020-27955
 tiger3080/cve-2025-9267
Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
 matheuzsecurity/elfdoor-gcc
LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.