Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
22 results
OWASP-Top-10-Neocloud-and-AI-Data-Center-Security-Risks preview

OWASP-Top-10-Neocloud-and-AI-Data-Center-Security-Risks

GitHubowasp/owasp-top-10-neocloud-and-ai-data-center-security-risks

OWASP framework cataloging the top 10 security risks in neocloud and AI data center infrastructure, covering hardware, networking, isolation,…

ai-securitycloud-securitycontainer-security+8

20
2 days ago
TriSuElla-AIDLCA-Framework preview

TriSuElla-AIDLCA-Framework

GitHubowasp/trisuella-aidlca-framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

ai-securitycloud-securitycode-analysis+7
31 month ago
AWS-Tough-Library-Multiple-CVEs preview

AWS-Tough-Library-Multiple-CVEs

GitHubmurataydemir/aws-tough-library-multiple-cves

Issue with tough, versions prior to 0.20.0 (Multiple CVEs)

educationpapers-researchsupply-chain-security+1
11 year ago
FIASSE preview

FIASSE

GitHubowasp/fiasse

A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)

code-analysiscurated-resourcesdevsecops+7
144 days ago
PSCF preview

PSCF

GitHubowasp/pscf

OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…

curated-resourcesdevsecopseducation+2
2915 days ago
Software-Component-Verification-Standard preview

Software-Component-Verification-Standard

GitHubowasp/software-component-verification-standard

Software Component Verification Standard (SCVS)

configuration-auditingcurated-resourceseducation+2
1712 years ago
LlamaStack-RCE-Deterministic-Supply-Chain-Exploitation-Hardening-Framework-CVE-2024-50050- preview

LlamaStack-RCE-Deterministic-Supply-Chain-Exploitation-Hardening-Framework-CVE-2024-50050-

GitHubsastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-

LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…

ai-securitybinary-exploitationcommand-and-control+9
9 months ago
springhound preview

springhound

GitHubmebibite/springhound

Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…

code-analysismisconfigurationstatic-analysis+2
4 years ago
Log4j-Updater preview

Log4j-Updater

GitHubvinnimarcon/log4j-updater

Log4J Updater Bash Script to automate the framework update process on numerous machines and prevent the CVE-2021-44228

configuration-auditingdevsecopsgeneral-purpose-utilities+3
24 years ago
raptor preview

raptor

GitHubgadievron/raptor

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…

ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+7
3.9k4 days ago
openclaw-defender preview

openclaw-defender

GitHubnightfullstar/openclaw-defender

Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…

ai-securitycode-analysiscurated-resources+8
38 months ago
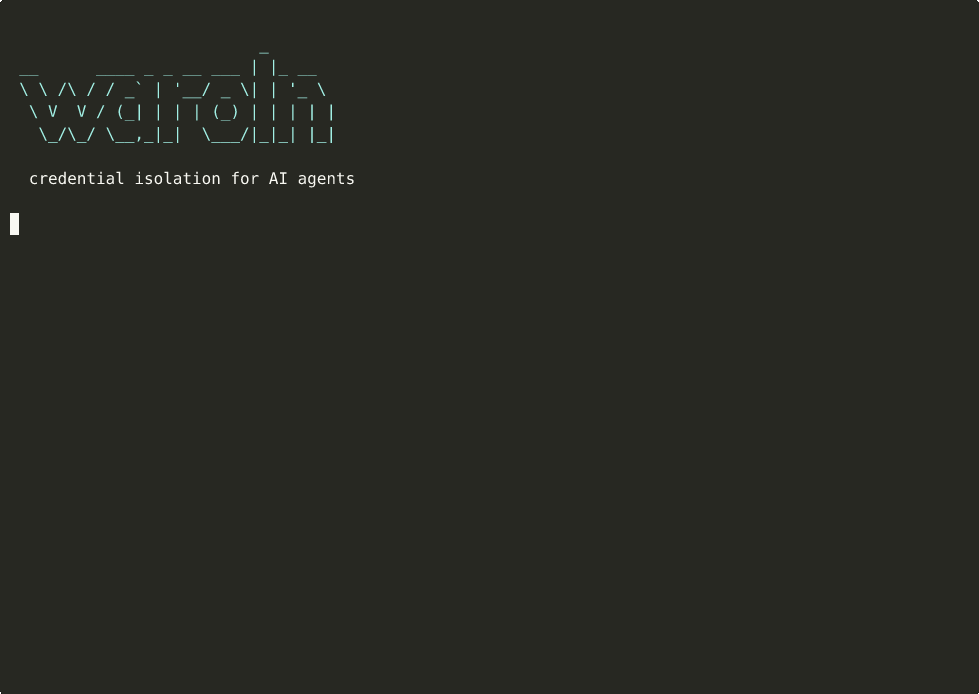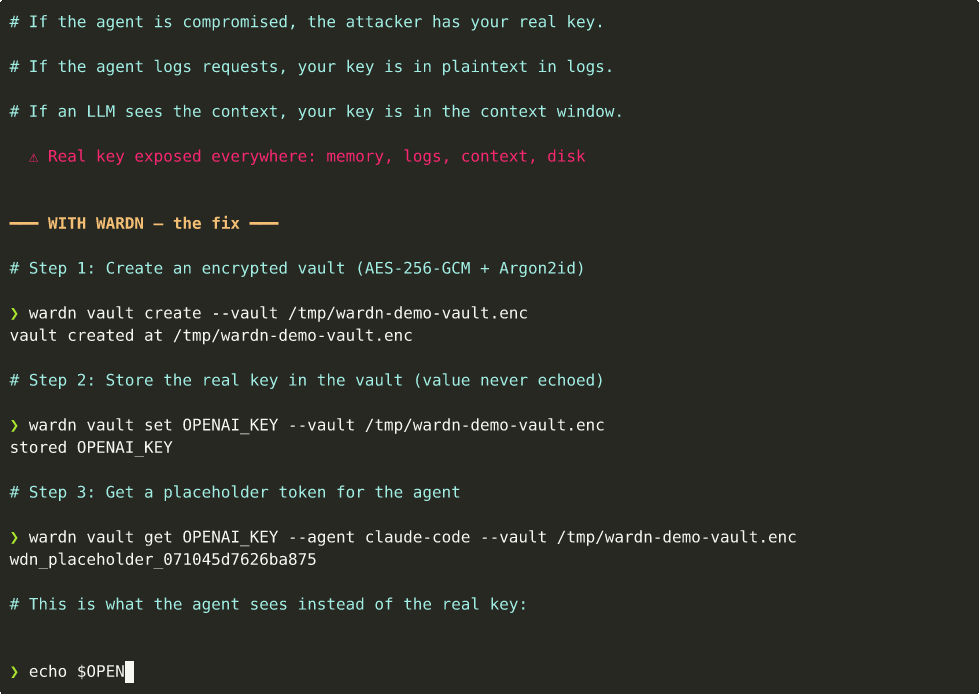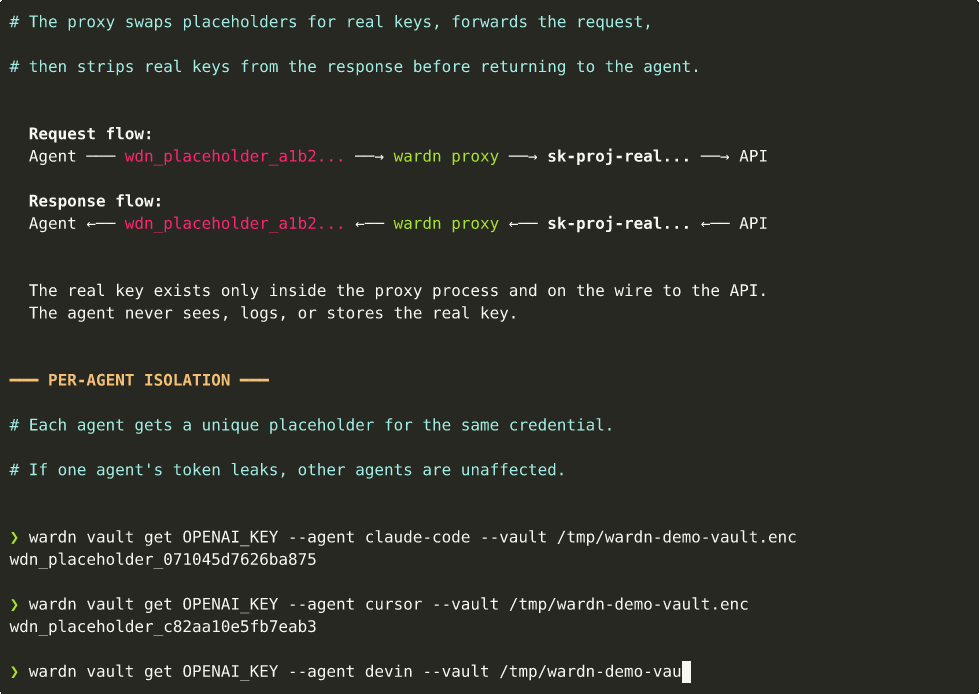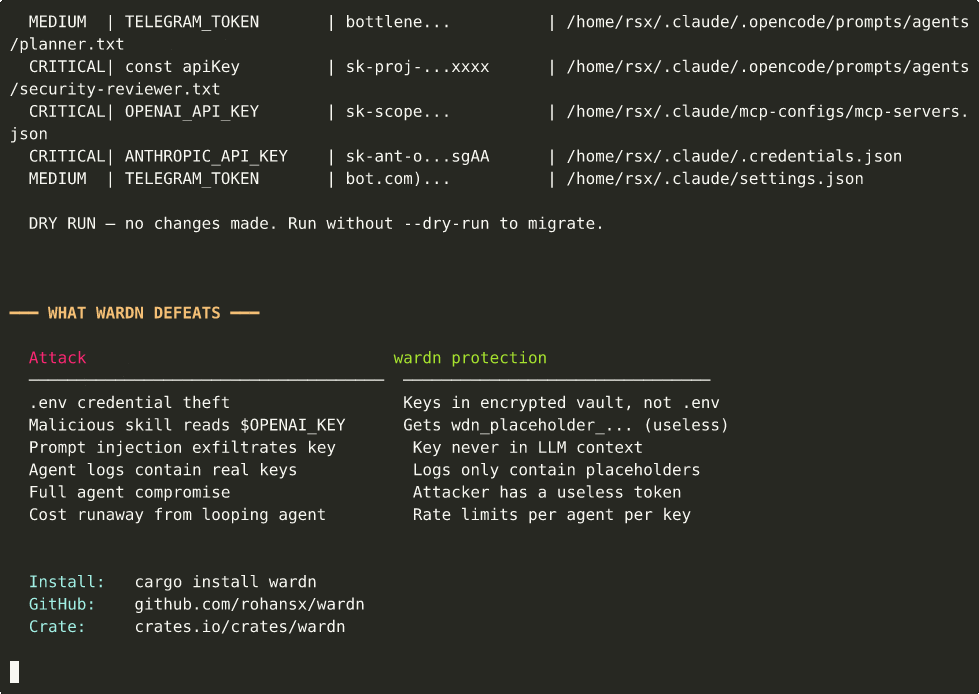
wardn preview

wardn

GitHubrohansx/wardn

credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.

api-securityauthentication-authorizationcloud-security+6
3723 days ago
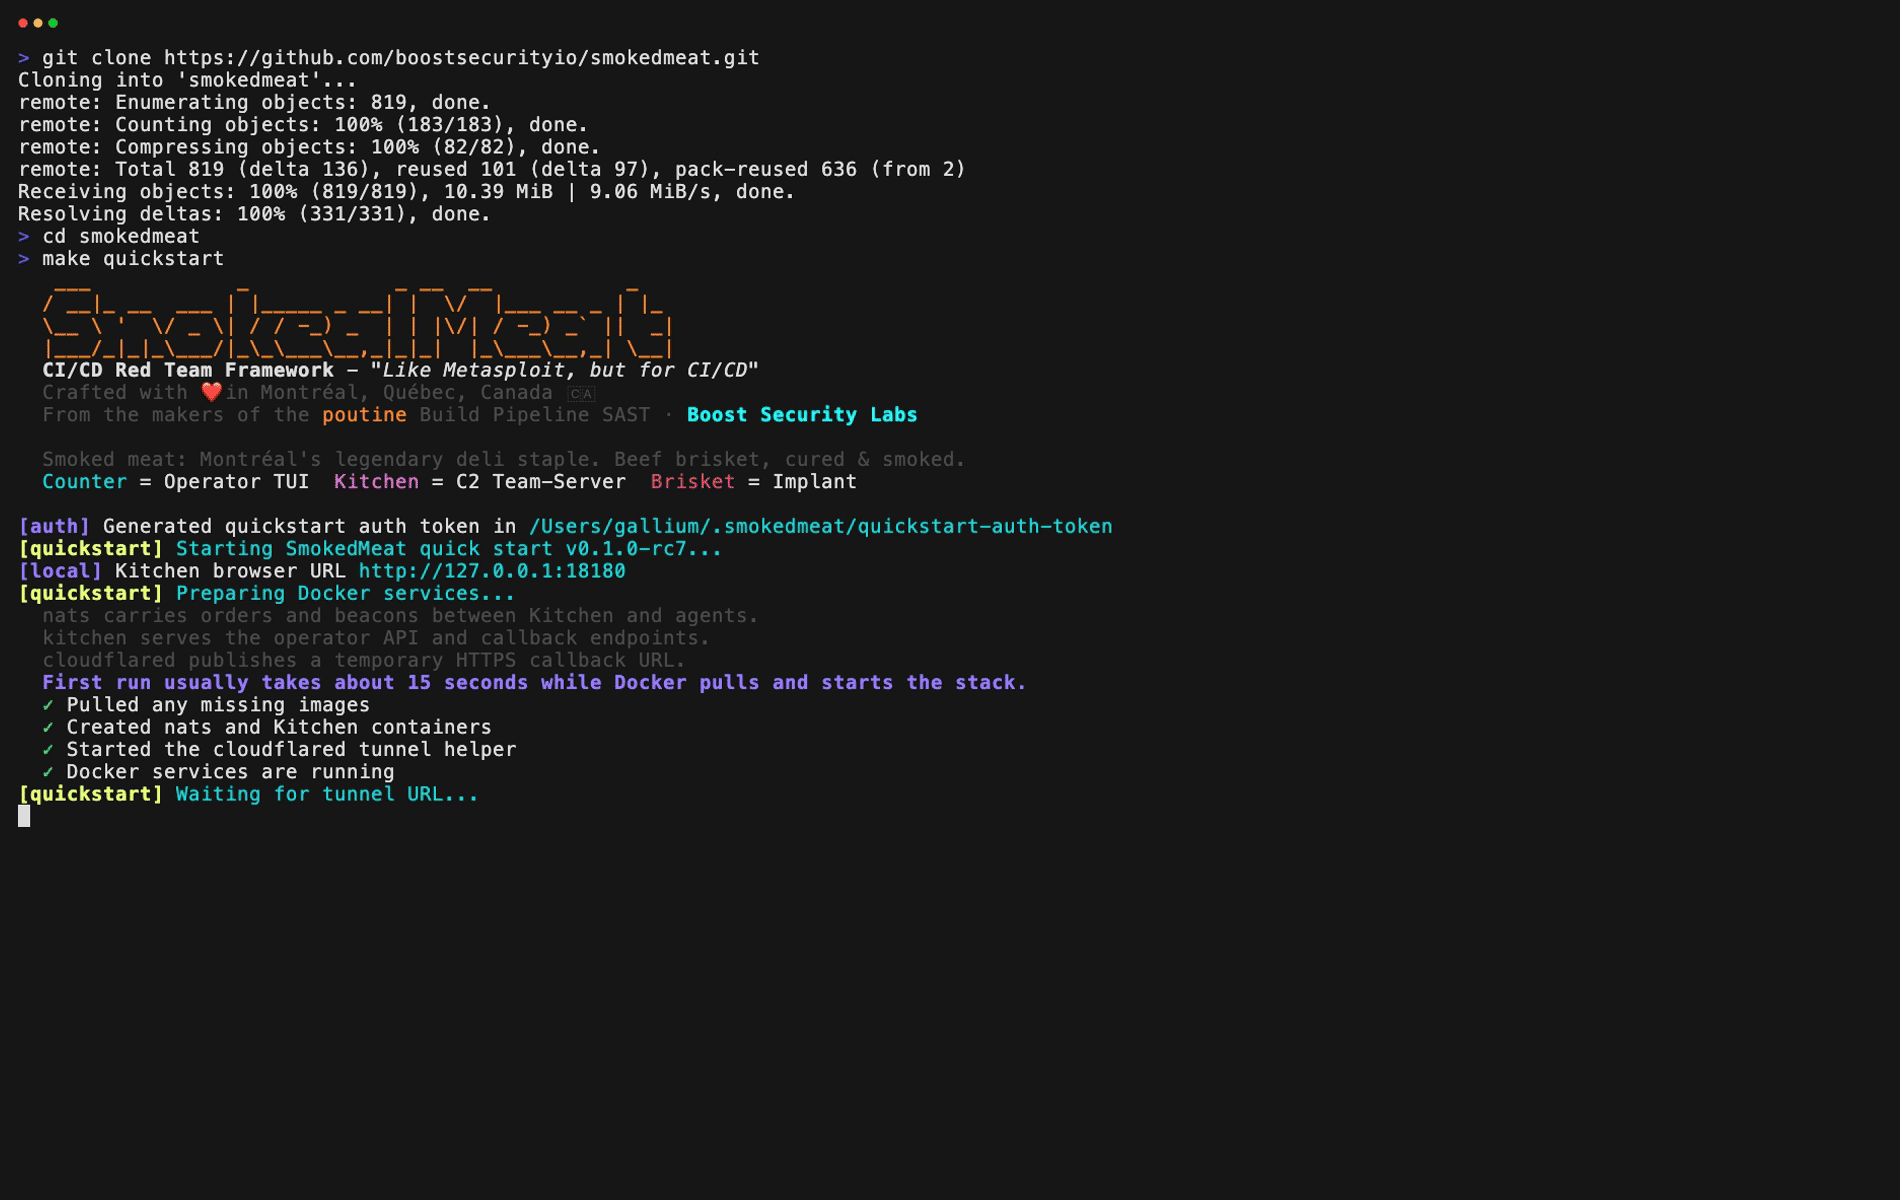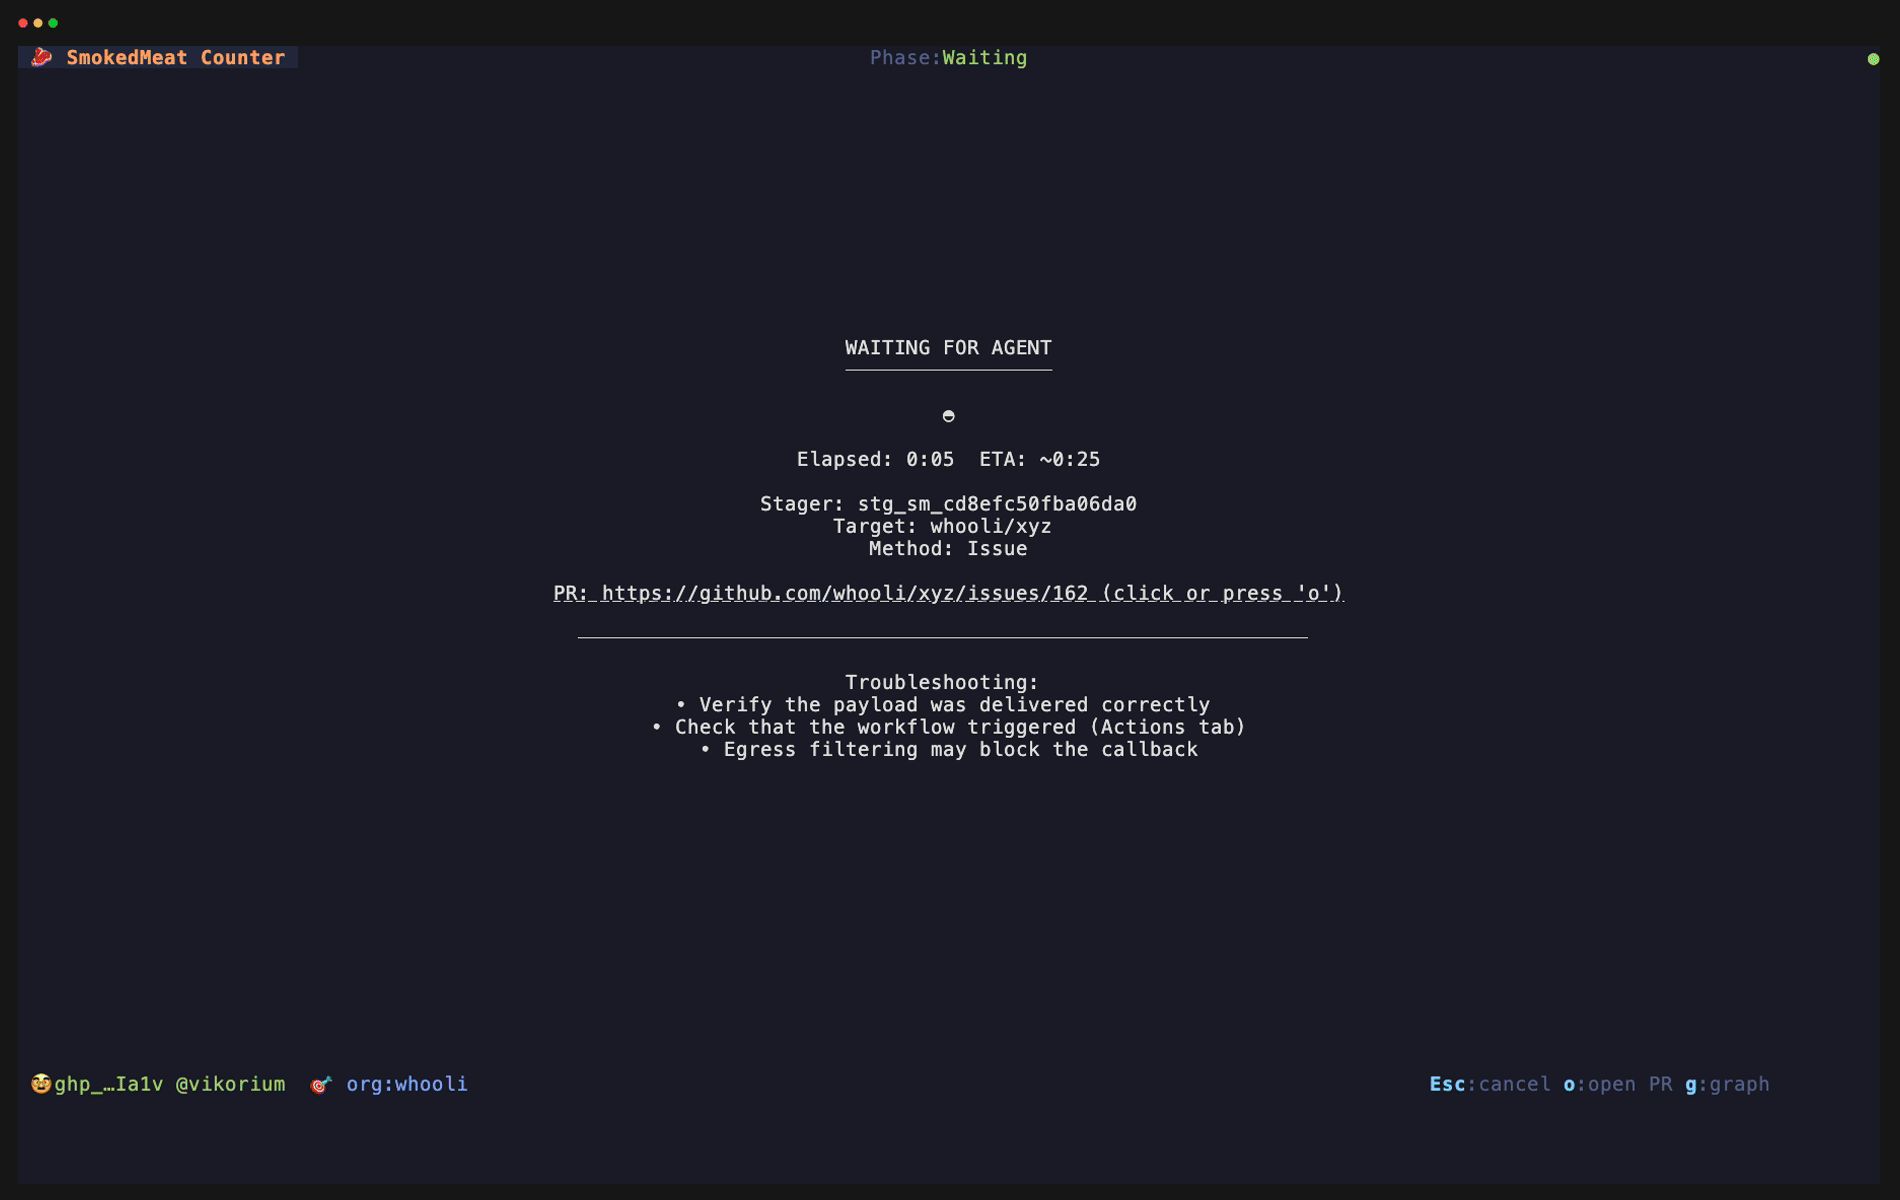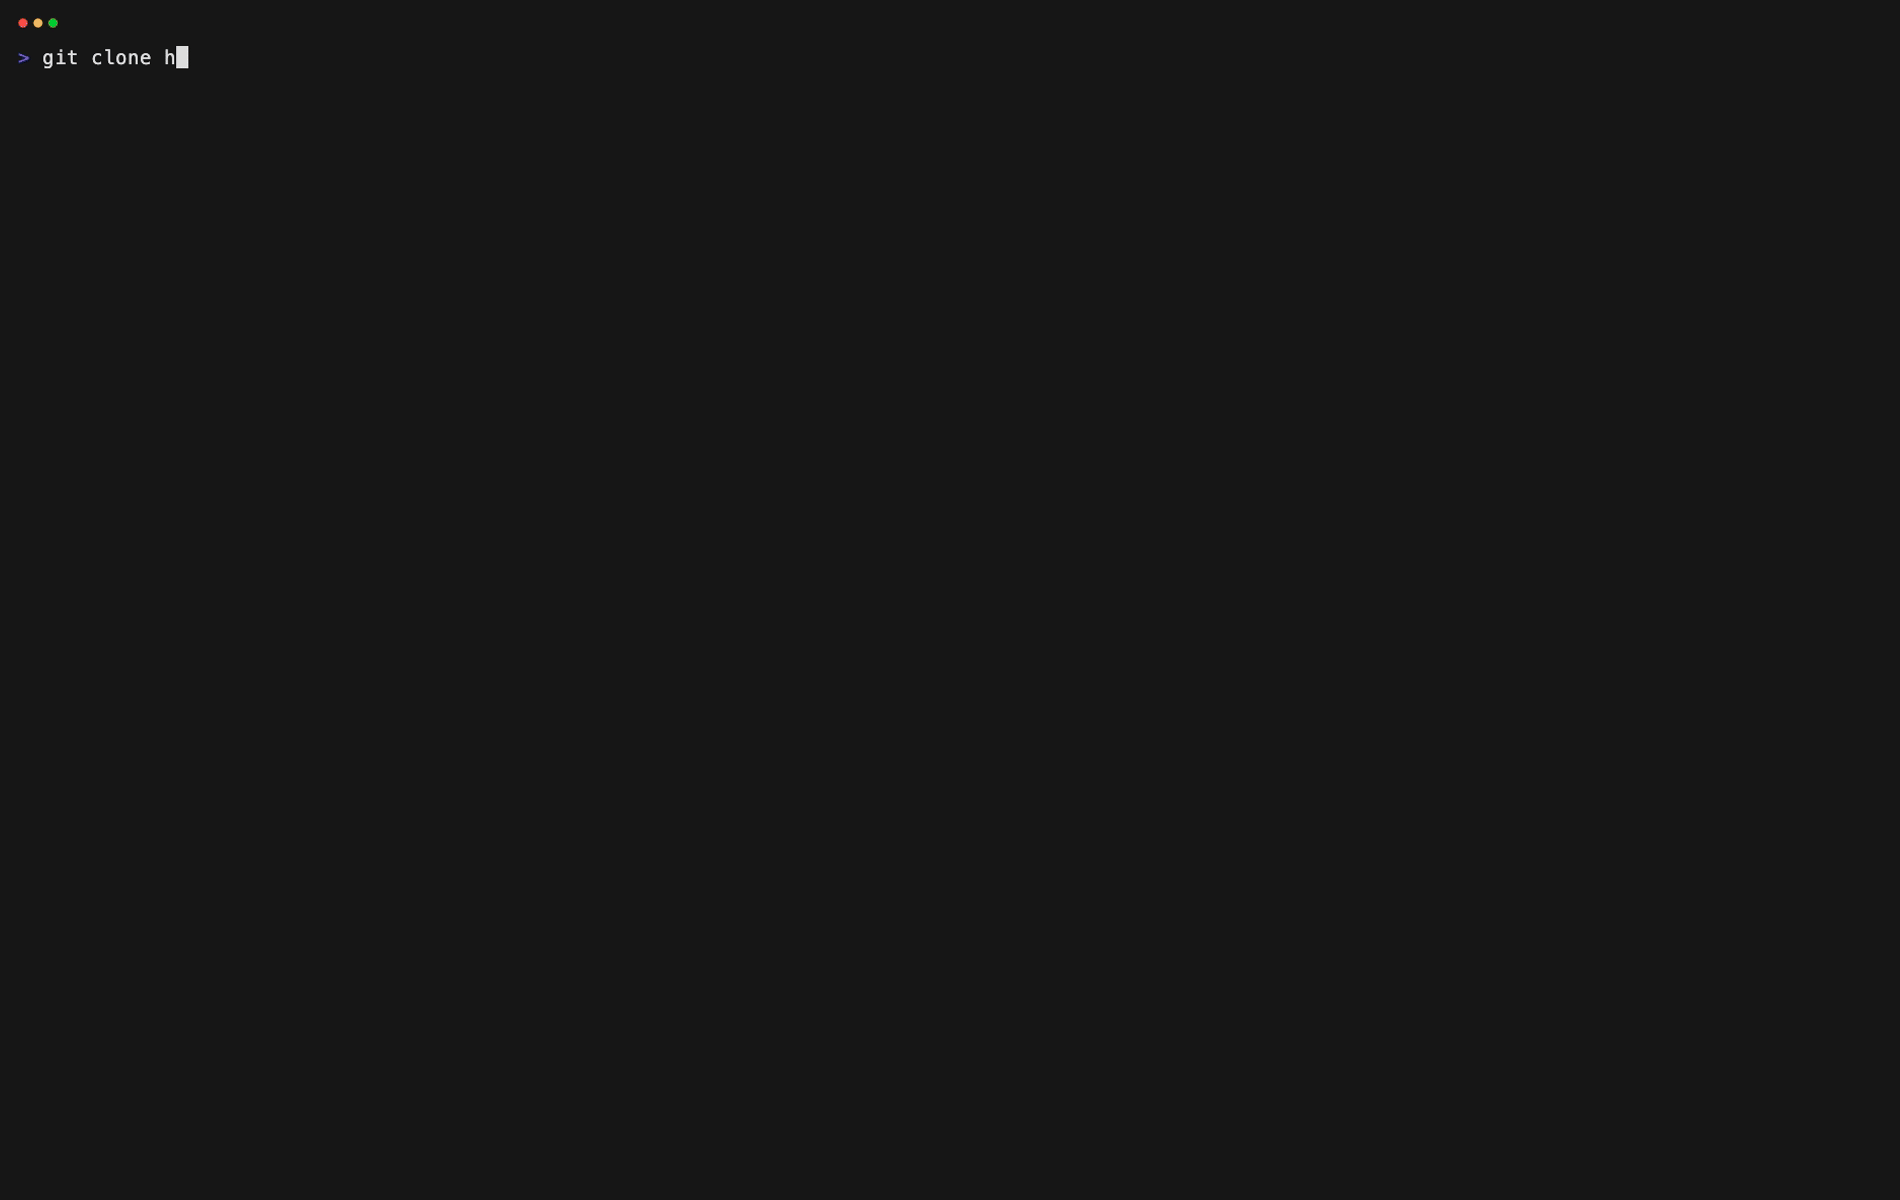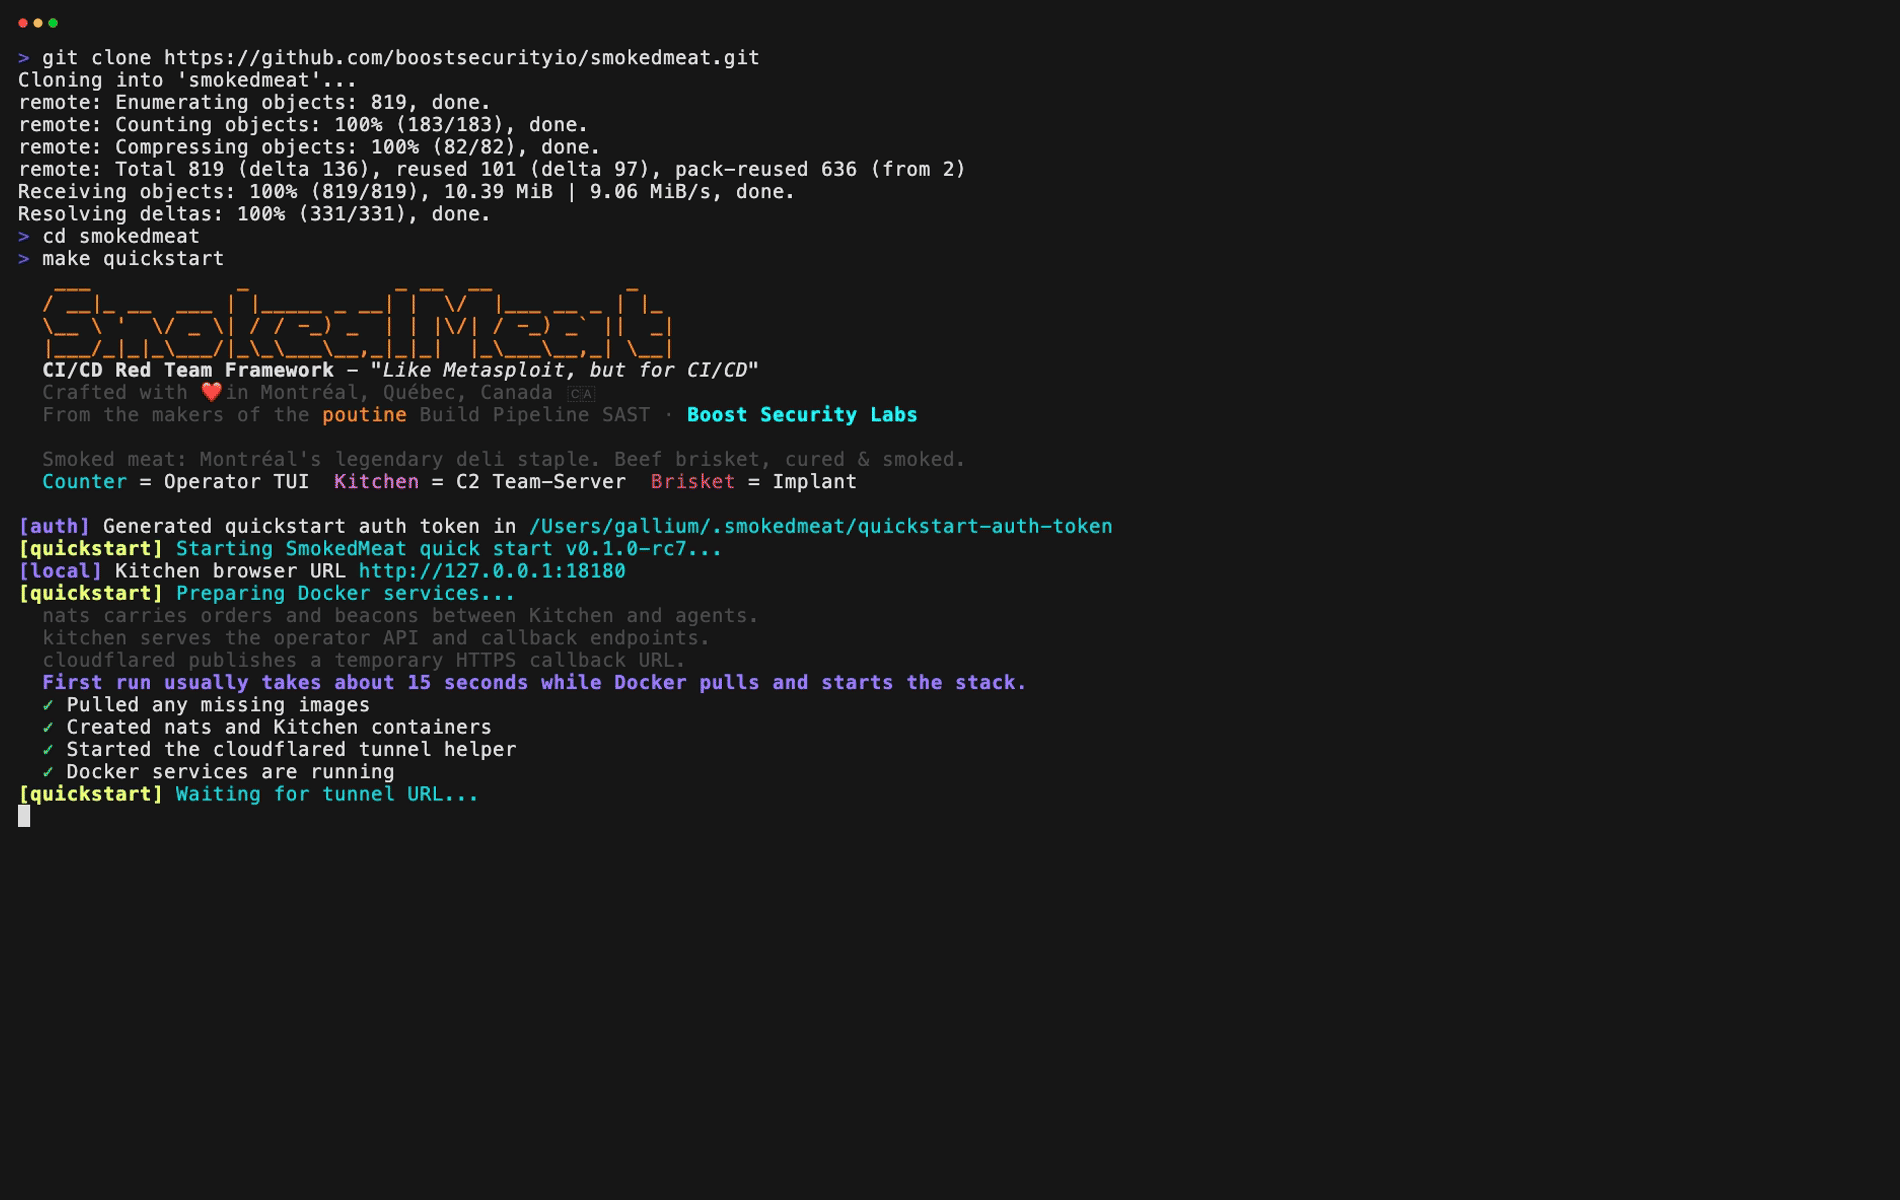
smokedmeat preview

smokedmeat

GitHubboostsecurityio/smokedmeat

A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.

cloud-securitycommand-and-controleducation+9
3961 month ago
aura preview

aura

GitHubsourcecode-ai/aura

Python source code auditing and static analysis on a large scale

code-analysiseducationmalware-analysis+4
4963 years ago
slsa preview

slsa

GitHubslsa-framework/slsa

Supply-chain Levels for Software Artifacts

curated-resourceseducationpapers-research+1
1.9k4 days ago
sh4d0wup preview

sh4d0wup

GitHubkpcyrd/sh4d0wup

Signing-key abuse and update exploitation framework

command-and-controlexploitationpayload-development+3
1312 months ago
python-tuf preview

python-tuf

GitHubtheupdateframework/python-tuf

Python reference implementation of The Update Framework (TUF)

cryptographysupply-chain-securityutilities-frameworks
1.7k9 days ago
Argus preview

Argus

GitHubpurs3lab/argus

Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…

code-analysisdevsecopseducation+4
562 years ago
Previous12Next