
CVE-2026-23947-PoC
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
code-analysisexploitationsupply-chain-security+2
boroeurnprach/cve-2026-23947-pocProof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 george0papasotiriou/cve-2026-21016-malicious-pypi-package-install-hook-setup.py-execution-
Demonstrates how a malicious Python package executes arbitrary commands during pip install via setup.py, highlighting PyPI supply chain and…
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE
 hyperps/cve-2026-0848
nltk.tokenize.StanfordSegmenter dynamically loads external Java .jar files without verification or sandboxing. If an attacker can supply or replace…
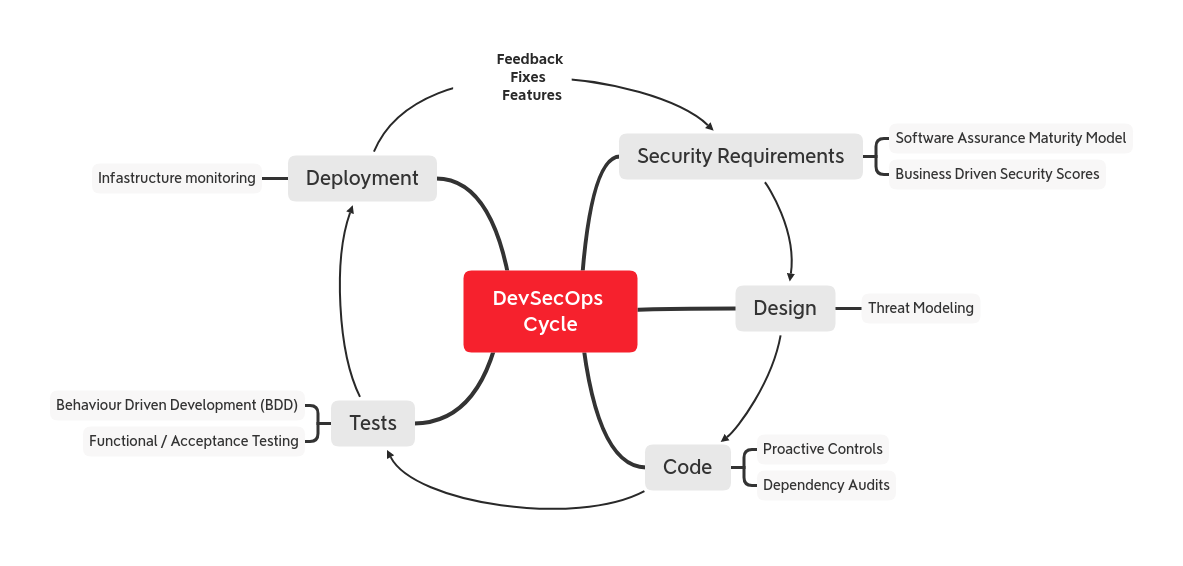 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
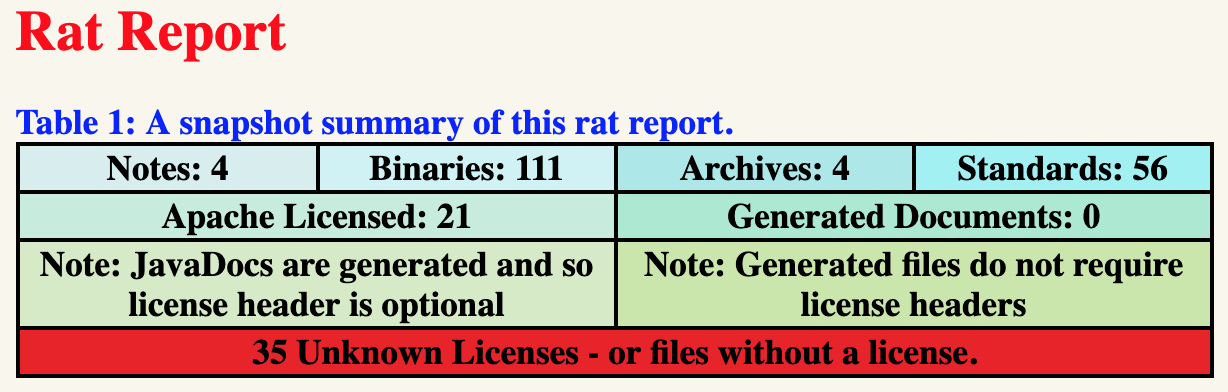 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
 u-maxx/magento-swf-patched-cve-2011-2461
Patched version of the uploader.swf and uploaderSingle.swf to fix CVE-2011-2461
 roy-aladin/infratest
DO NOT FORK, DEPLOY, OR USE FOR ANYTHING BUT LEARNING. These requirements are vulnerable to CVE-2024-39689
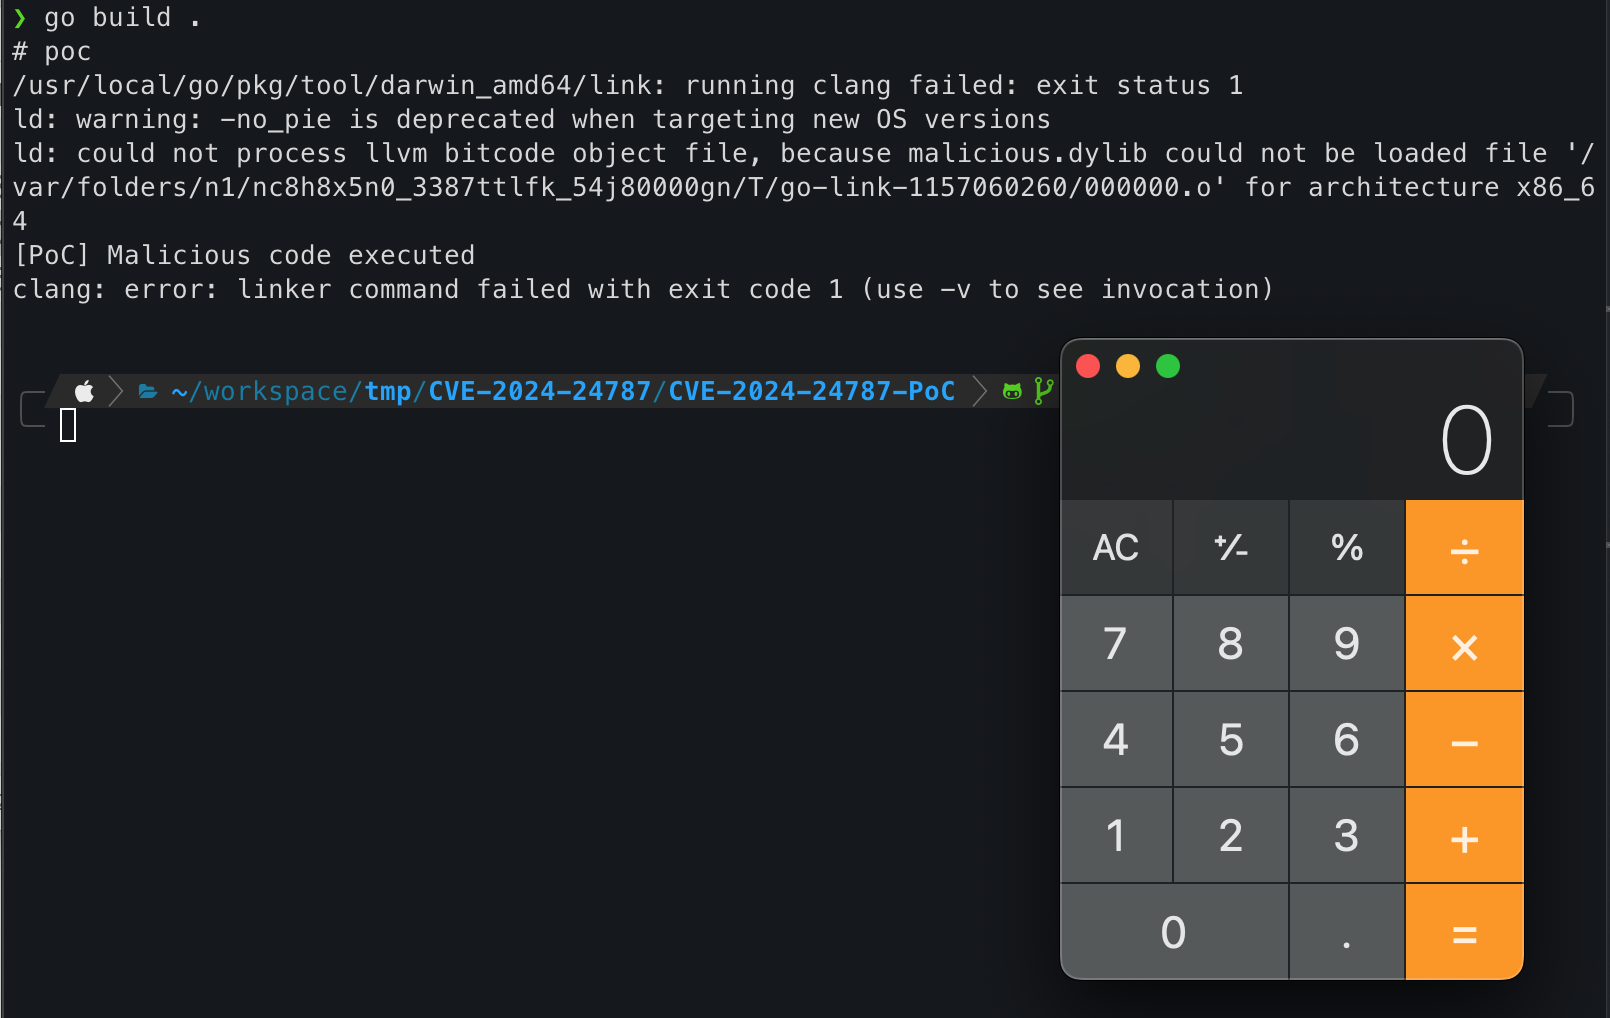 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 moshe-ship/bidi-guard
Scan code for invisible bidirectional Unicode characters (Trojan Source attack prevention, CVE-2021-42574)
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 timwr/cve-2017-1000117
Proof of concept of CVE-2017-1000117