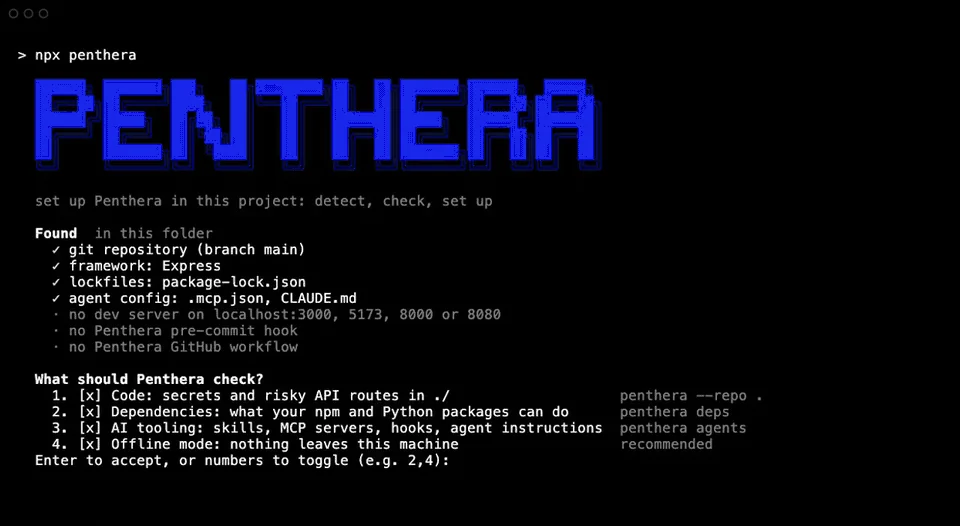
penthera
 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
ai-securitycode-analysisconfiguration-auditing+7
78
danoszz/pentheraOffline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 ahmed-elmahgob/poc-cve-2026-102282
CVE-2026-102282: adm-zip LPE via SUID/SGID preservation during archive extraction (fixed in 0.6.1)
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 spdx/tools-python
A Python library to parse, validate and create SPDX documents.
 nightwatchcyber/gh_release_test
Demonstration script simulating a supply chain attack through GitHub releases, highlighting the risk of malicious code in release artifacts.
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 sionnx/cve-2003-0282
Portable zipfile extraction utility with broad OS support, decryption, and security fixes for path traversal and symlink vulnerabilities.
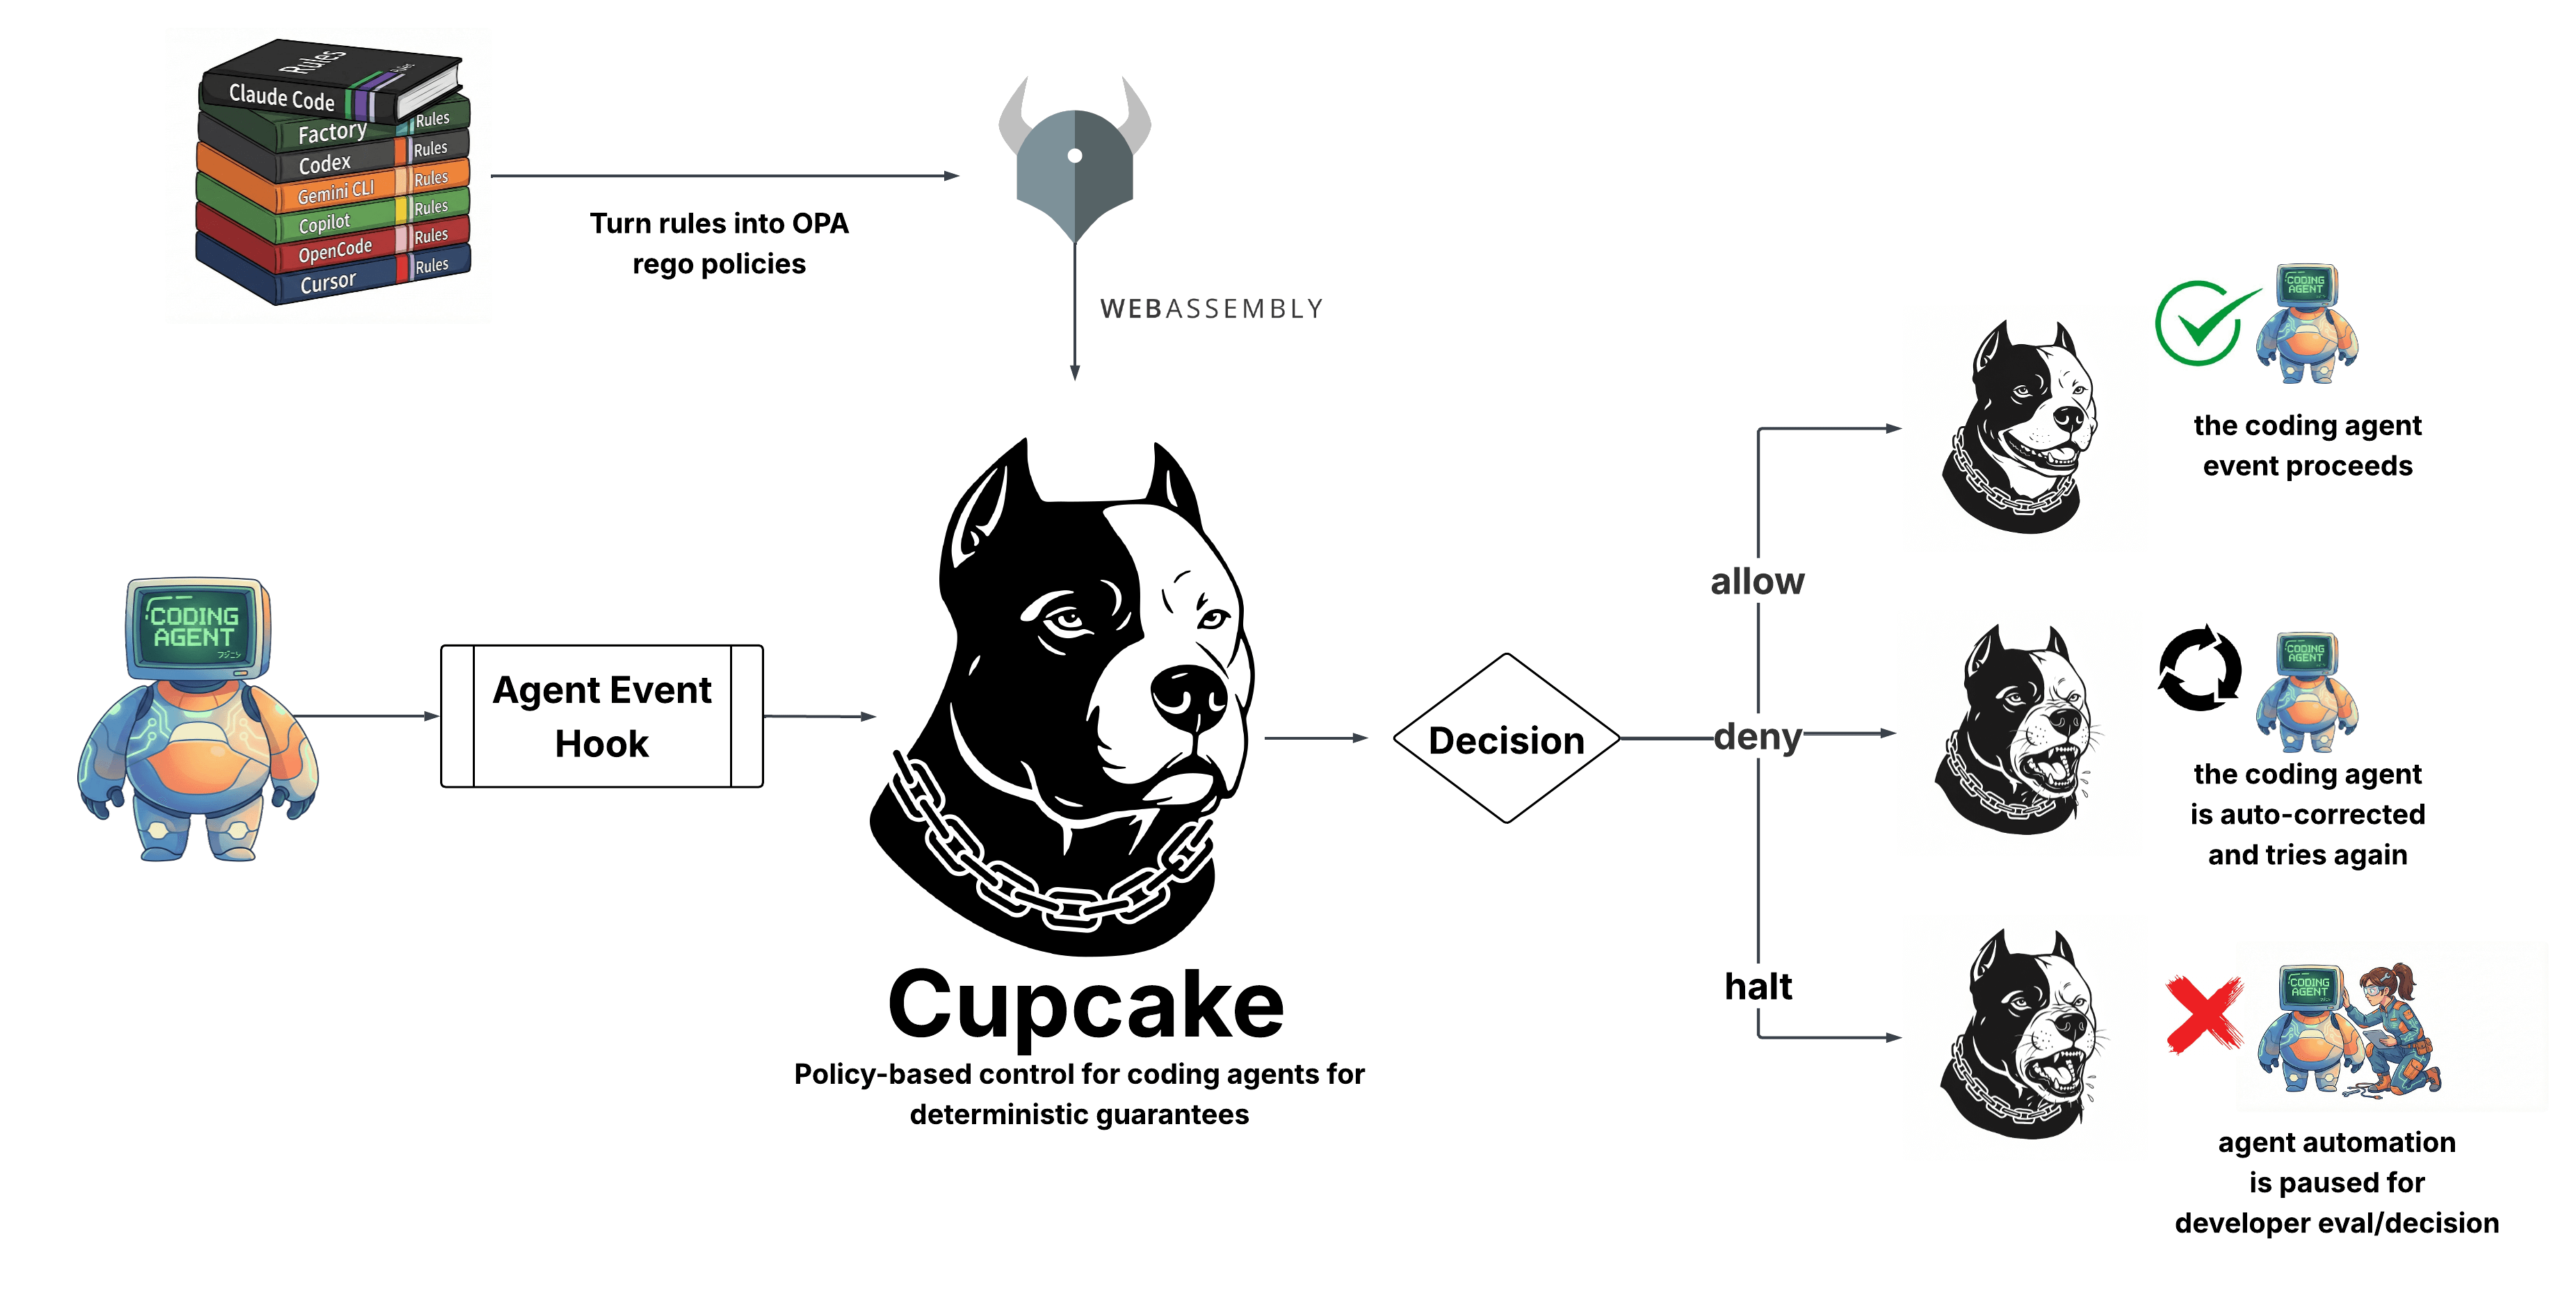 eqtylab/cupcake
A native policy enforcement layer for AI coding agents. Built on OPA/Rego.
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
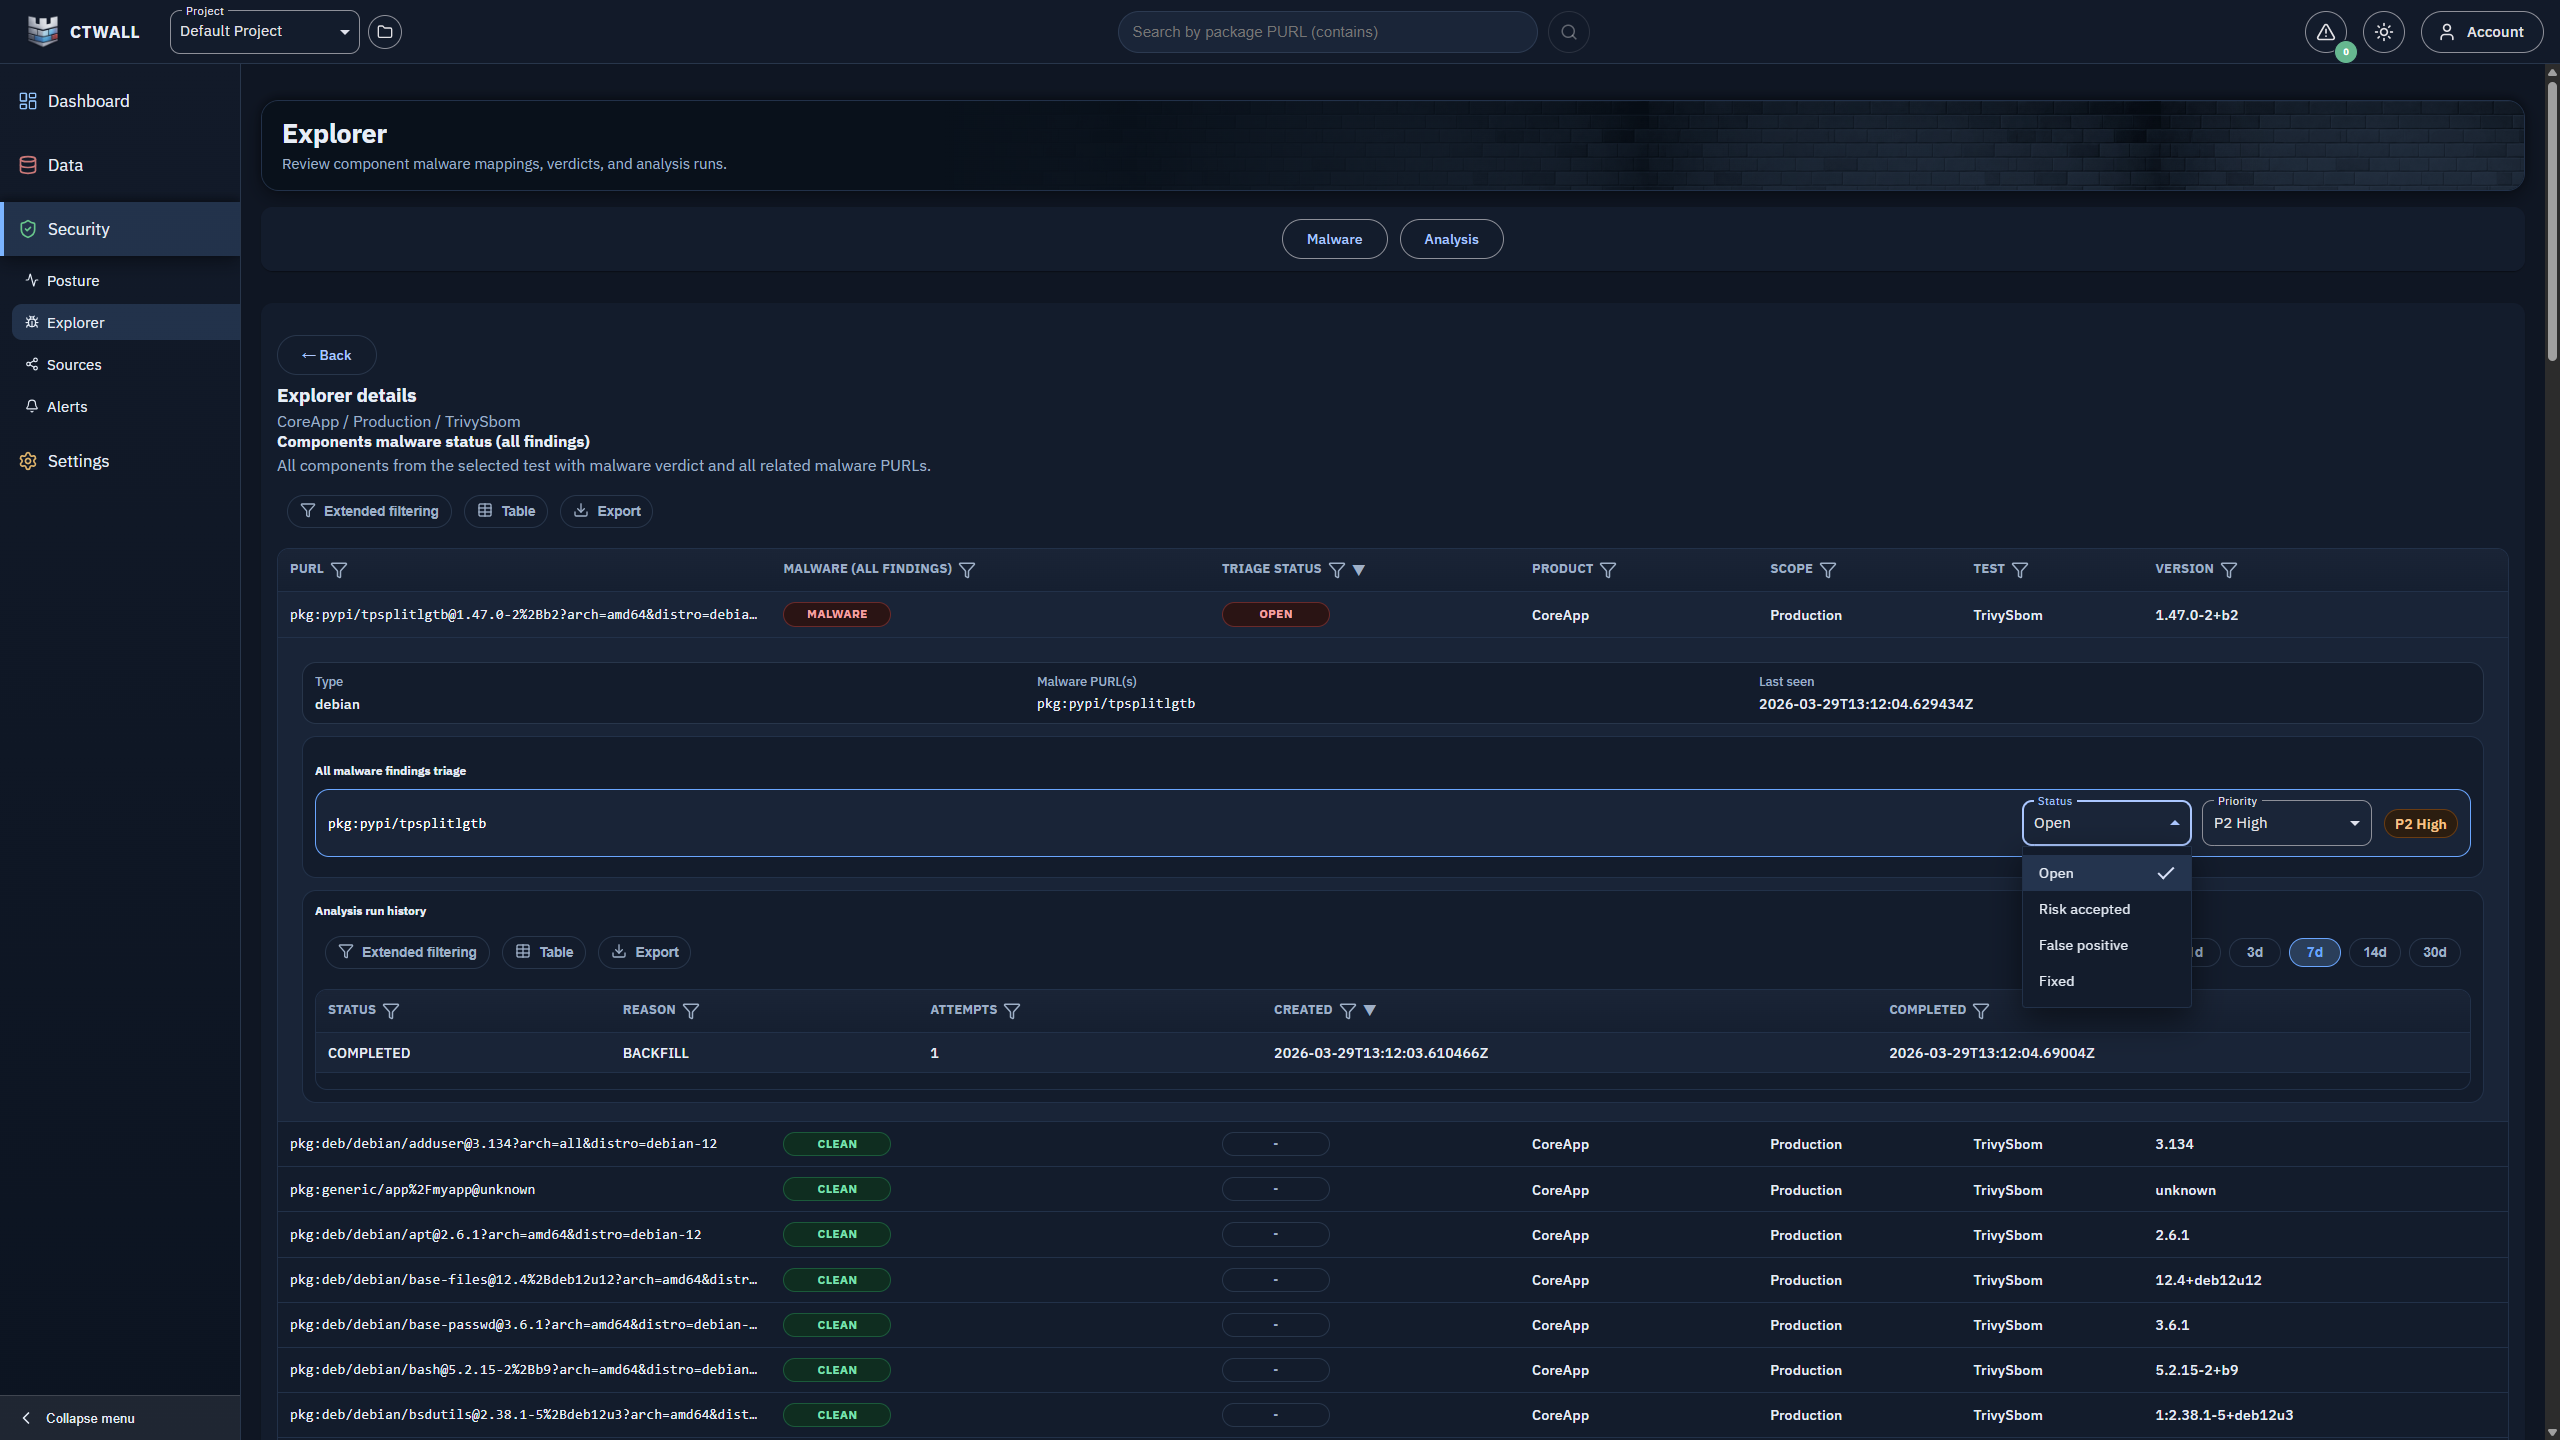 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…