

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
10.8k10h 40m ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
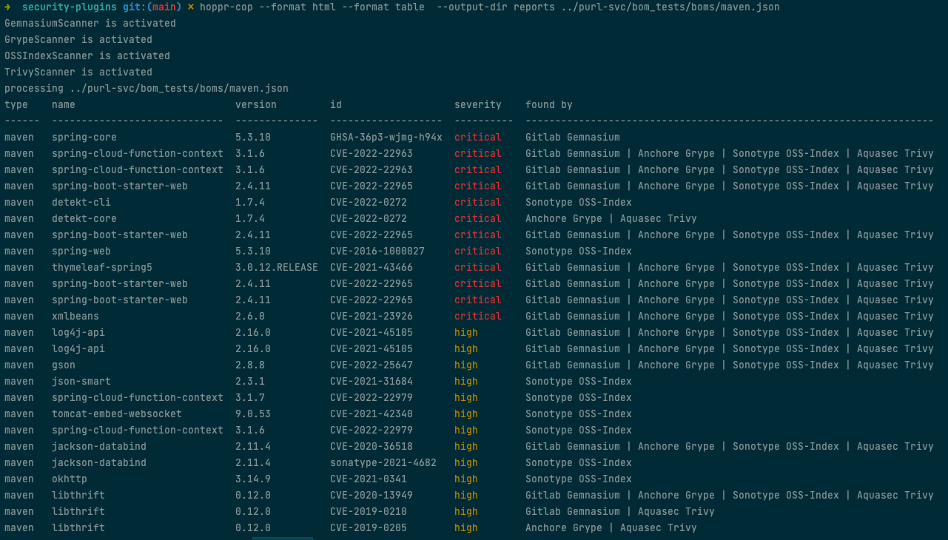
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 vulncheck-oss/cli
VulnCheck's official command line tool
 fazmin/cve-intel
Local security intelligence for CVE triage - 40 data sources and 41 tools, risk scores and an MCP server for AI agents, all in native Rust. Private…
 niffyhunt/wraithwall-toolkit
Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…
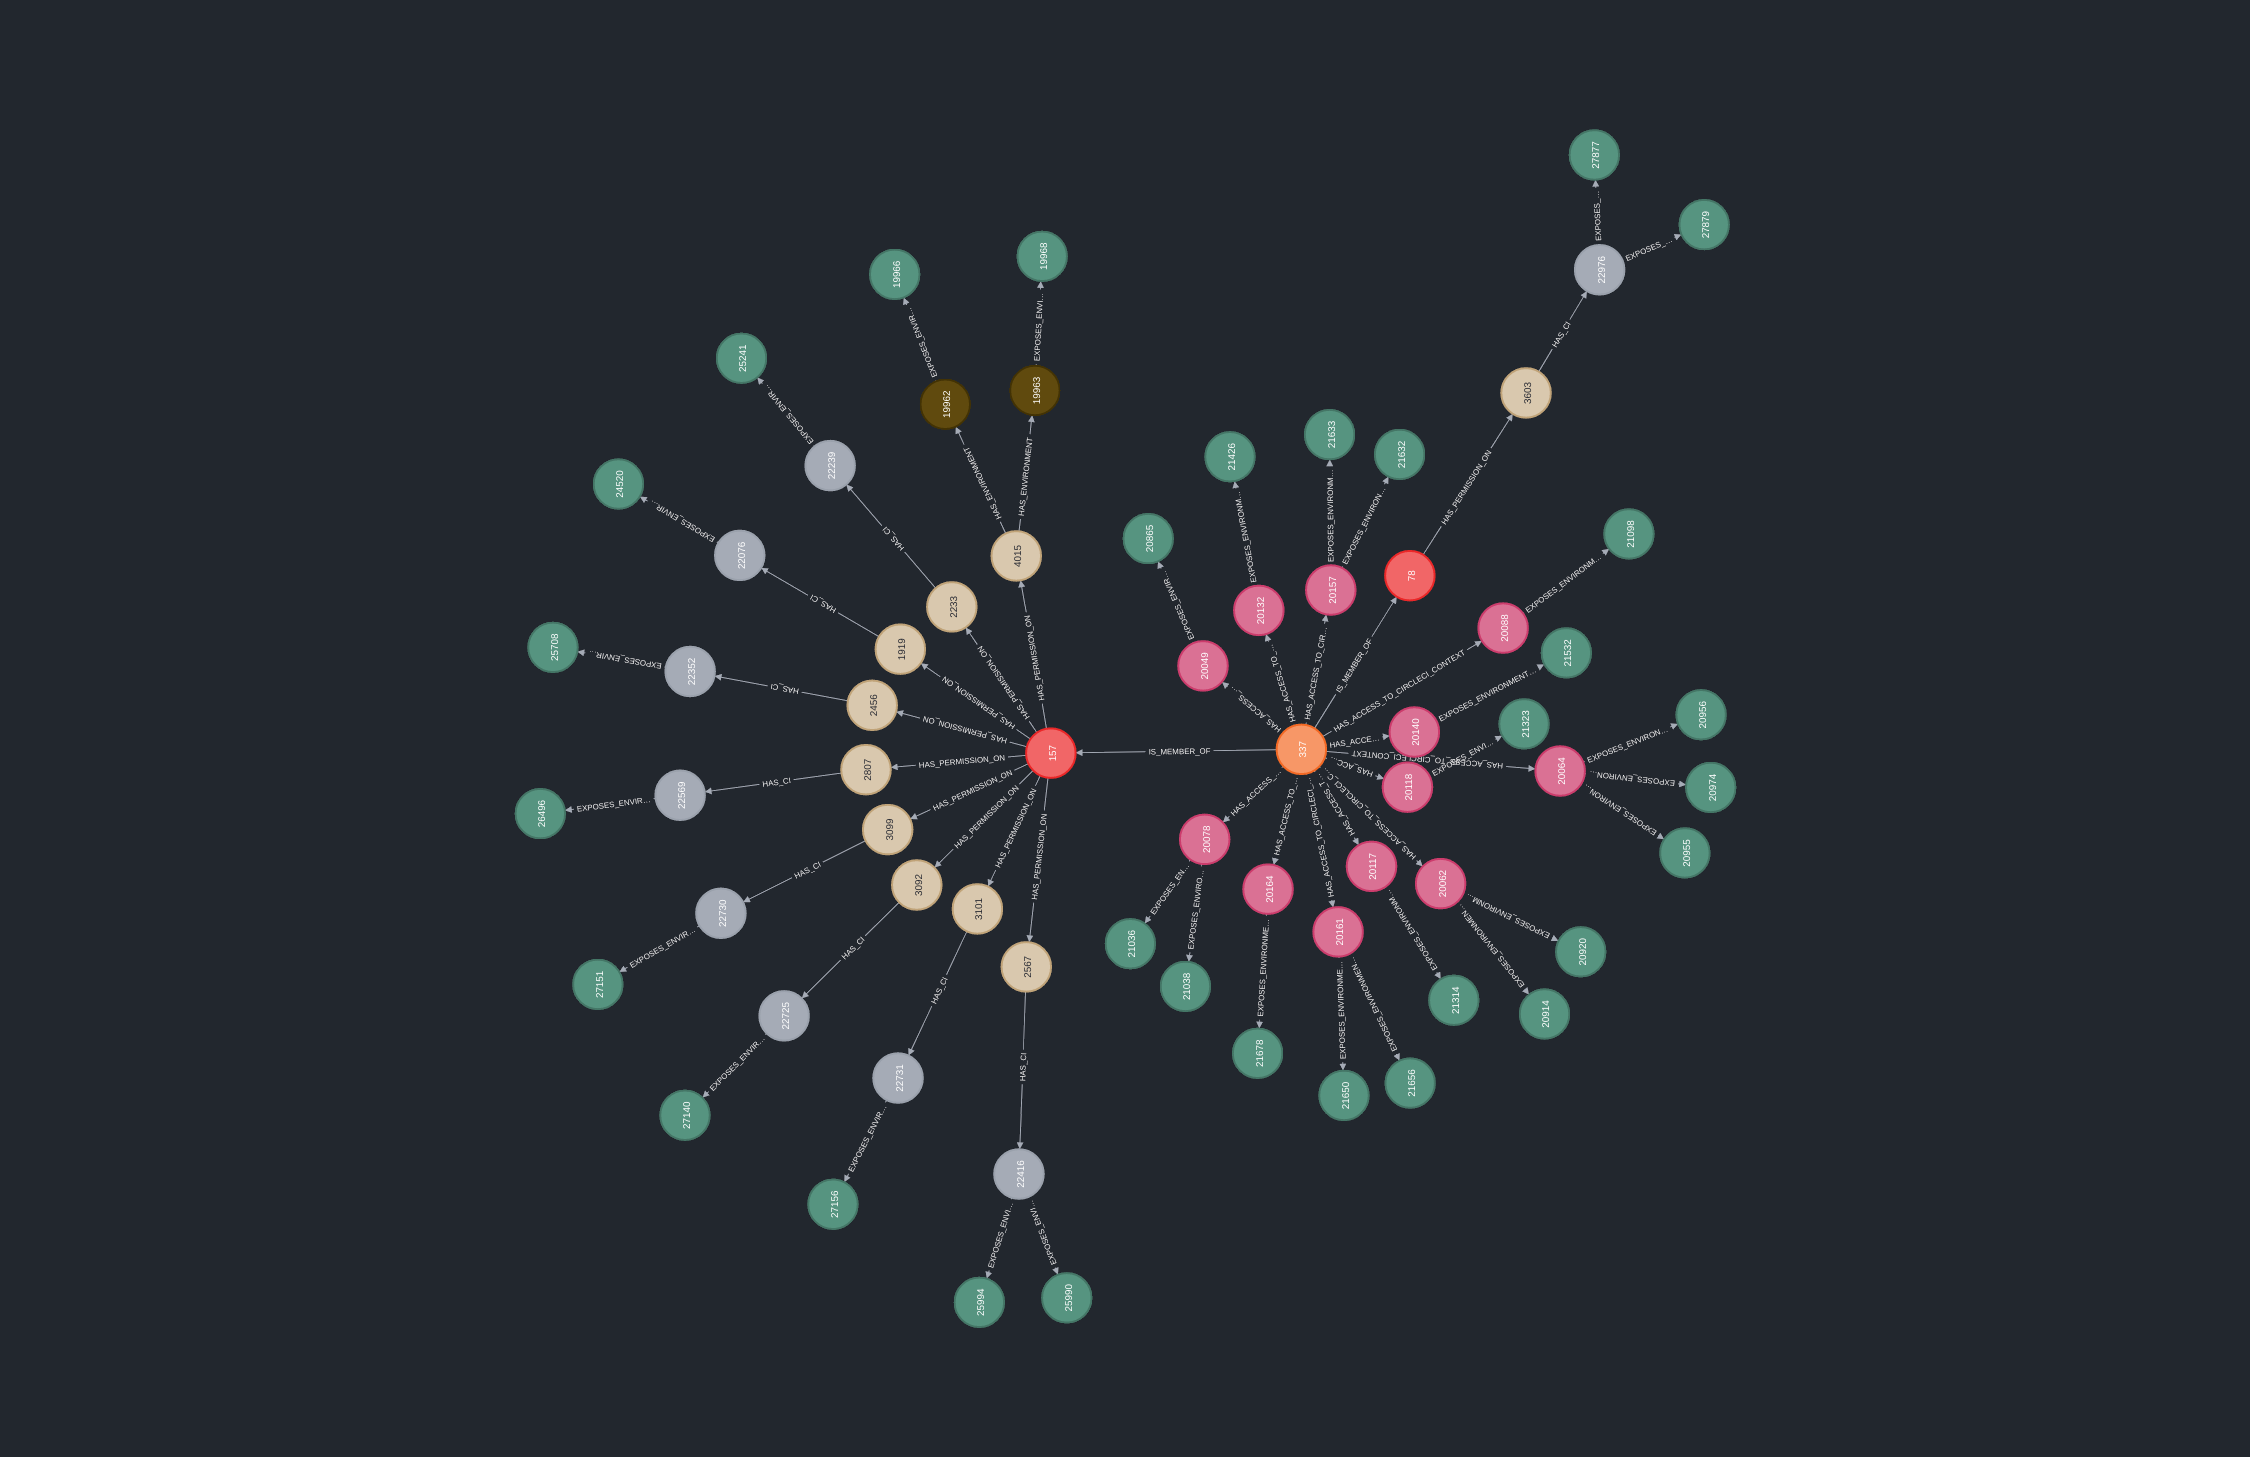
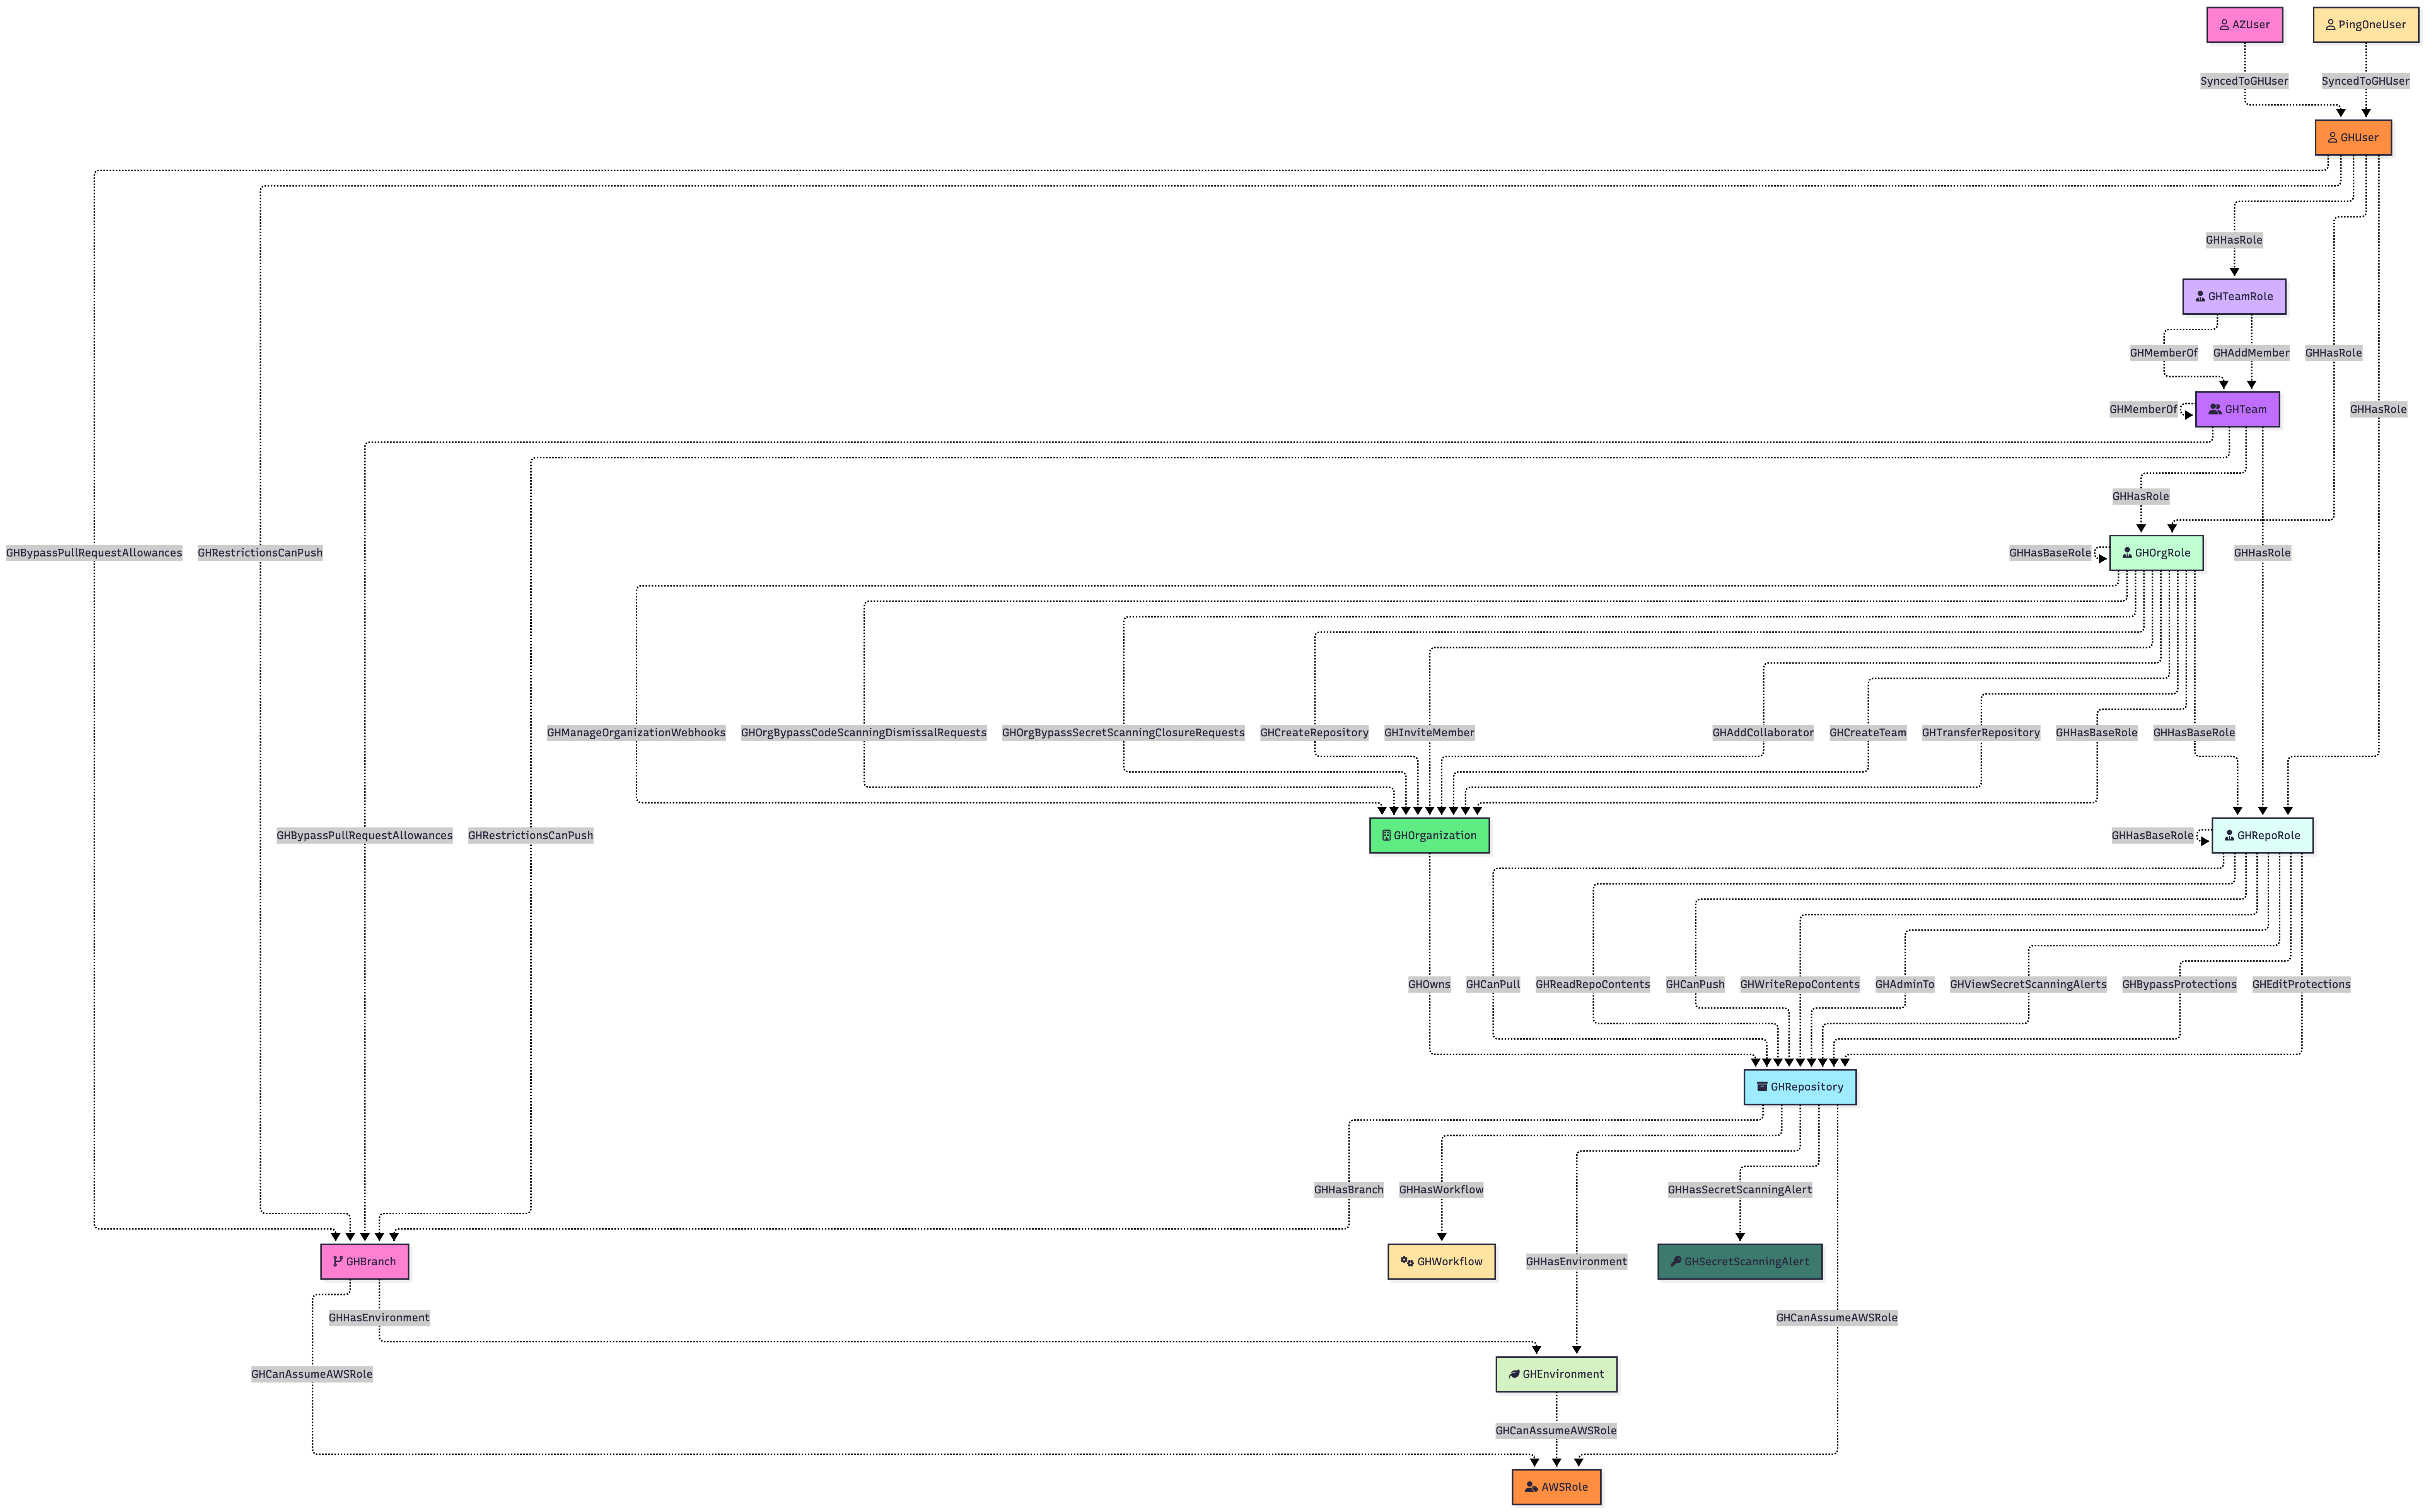 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 aquasecurity/vexhub
Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 qubesos/qubes-secpack
Curated repository of Qubes OS security bulletins, canaries, PGP keys, and ISO digests, with authenticated verification via git tags and detached…
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 byinarie/cve-2024-3094-info
Information for CVE-2024-3094
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 putget/cve-2024-38526
CVE-2024-38526 - Polyfill Scanner