
Startup-SBOM
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
cloud-securityconfiguration-auditingcontainer-security+4
17
morpheuslord/startup-sbomA tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
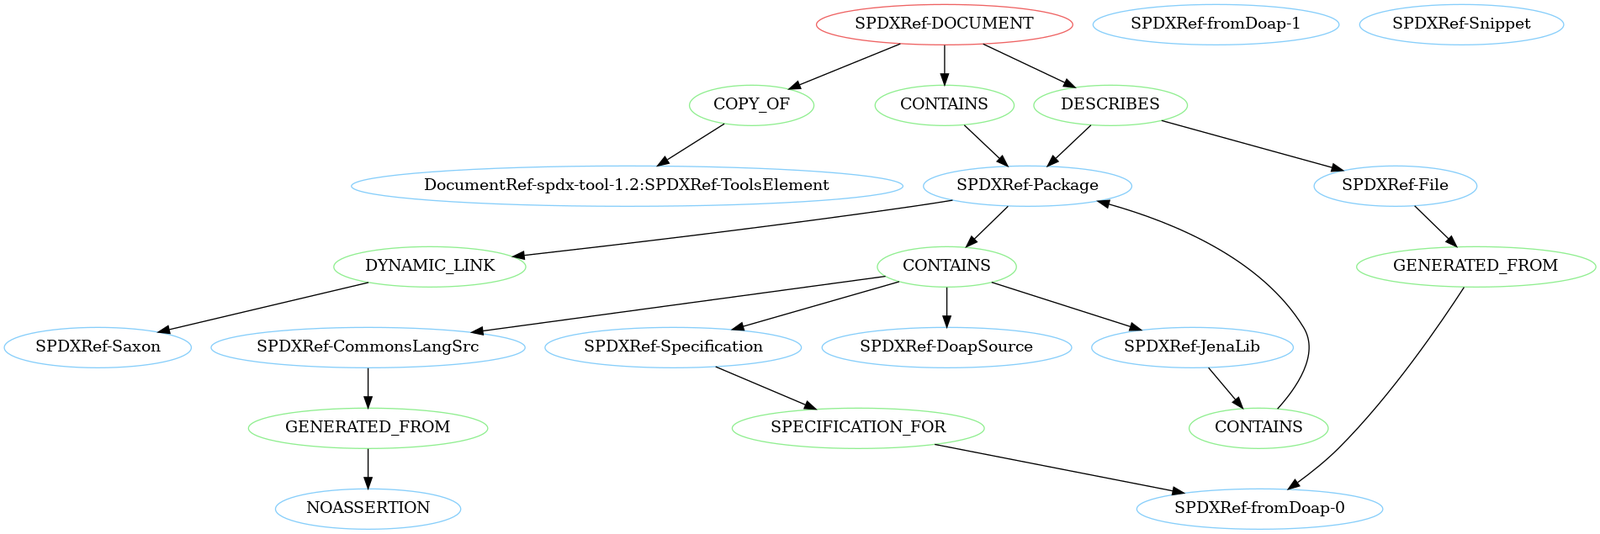 spdx/tools-python
A Python library to parse, validate and create SPDX documents.
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2023-37460_4-7-1
Java library for creating and extracting archives (ZIP, tar, JAR) with integrated security patch for a reported vulnerability, used as a dependency…
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
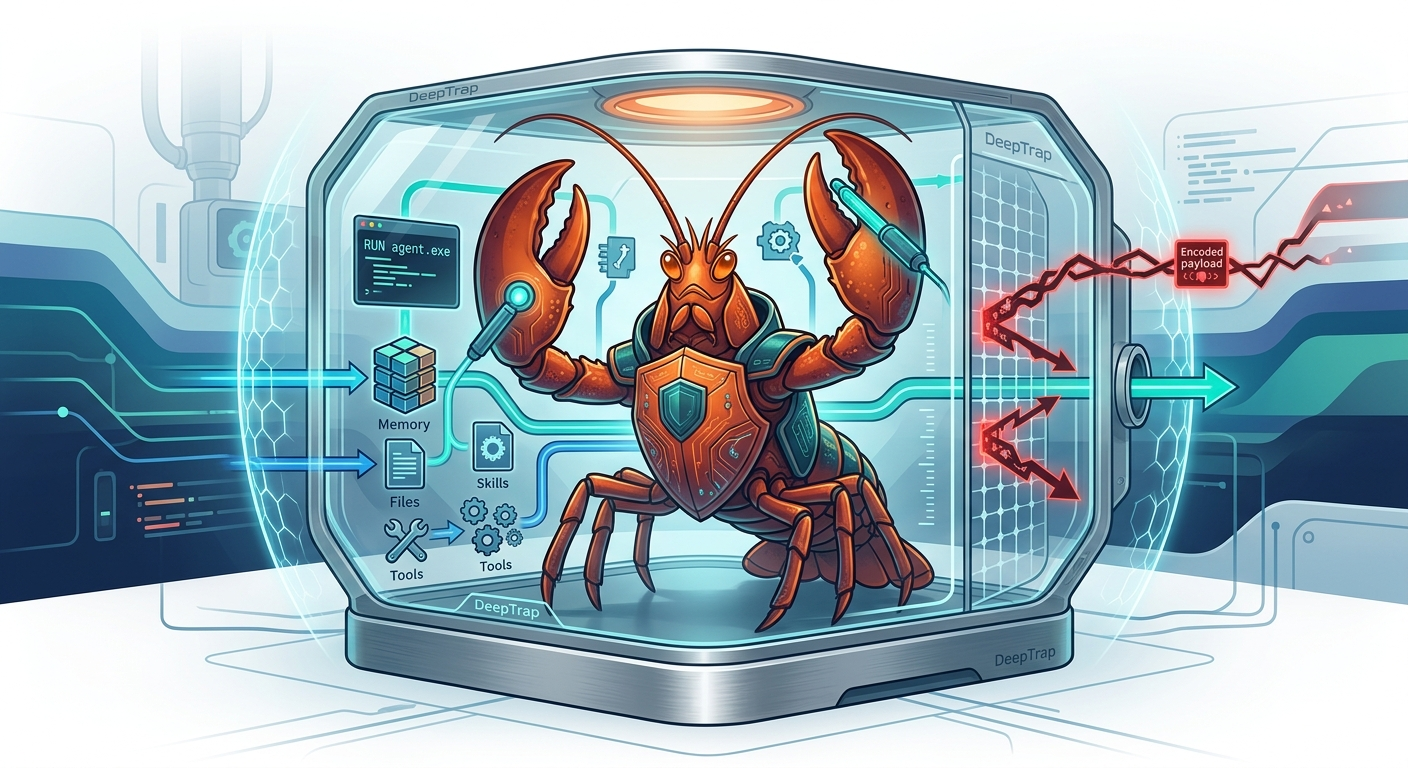 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 kevinslin/safe-npm
Safely install NPM packages
 fractal-tess/cve-2024-3094
Bash script to detect and remediate vulnerable xz-utils versions (5.6.0/5.6.1) by replacing them with a stable, uncompromised build from source.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 khayashi4337/lodash.template-fixed
Fork of lodash.template with CVE-2021-23337 fix (command injection via variable option)
 knqyf263/go-rpmdb
RPM DB bindings for go
 workshops-de/google_gax
Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)
 ryancnelson/patched-bash-4.3
patched-bash-4.3 for CVE-2014-6271
 sionnx/cve-2003-0282
Portable zipfile extraction utility with broad OS support, decryption, and security fixes for path traversal and symlink vulnerabilities.
 nanopathi/external_expat_aosp10_r33_cve-2022-22822tocve-2022-22827
Patched version of the Expat XML parser library addressing multiple CVEs (CVE-2022-22822 through CVE-2022-22827) for AOSP 10 r33, providing…
 jbnetwork-git/cve-2024-3094-xz-utils-check
Shell script to check if your system has a vulnerable version of XZ Utils affected by CVE-2024-3094, enabling quick detection of the supply-chain…
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2018-1002200_3-5
Java library for creating and extracting archives (ZIP, TAR, JAR) with support for various compression formats. Note: version 3.5 contains a fix for…
 katekeiroz-dev/golang-x-text
golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24