TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428

DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.

Vulnerability Scanner for Detecting Publicly Disclosed Vulnerabilities in Application Dependencies

Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them

Advisory and proof-of-concept for OS command injection in an MCP ffmpeg helper, with root-cause analysis, detector guidance, and mitigations for an…

This tool patches the CVE-2021-44228 Log4J vulnerability present in all minecraft versions NOTE THIS TOOL MUST BE RE-RUN after downloading or…

Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…

[Moved to Codeberg] Simple local scanner for vulnerable log4j instances

A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…

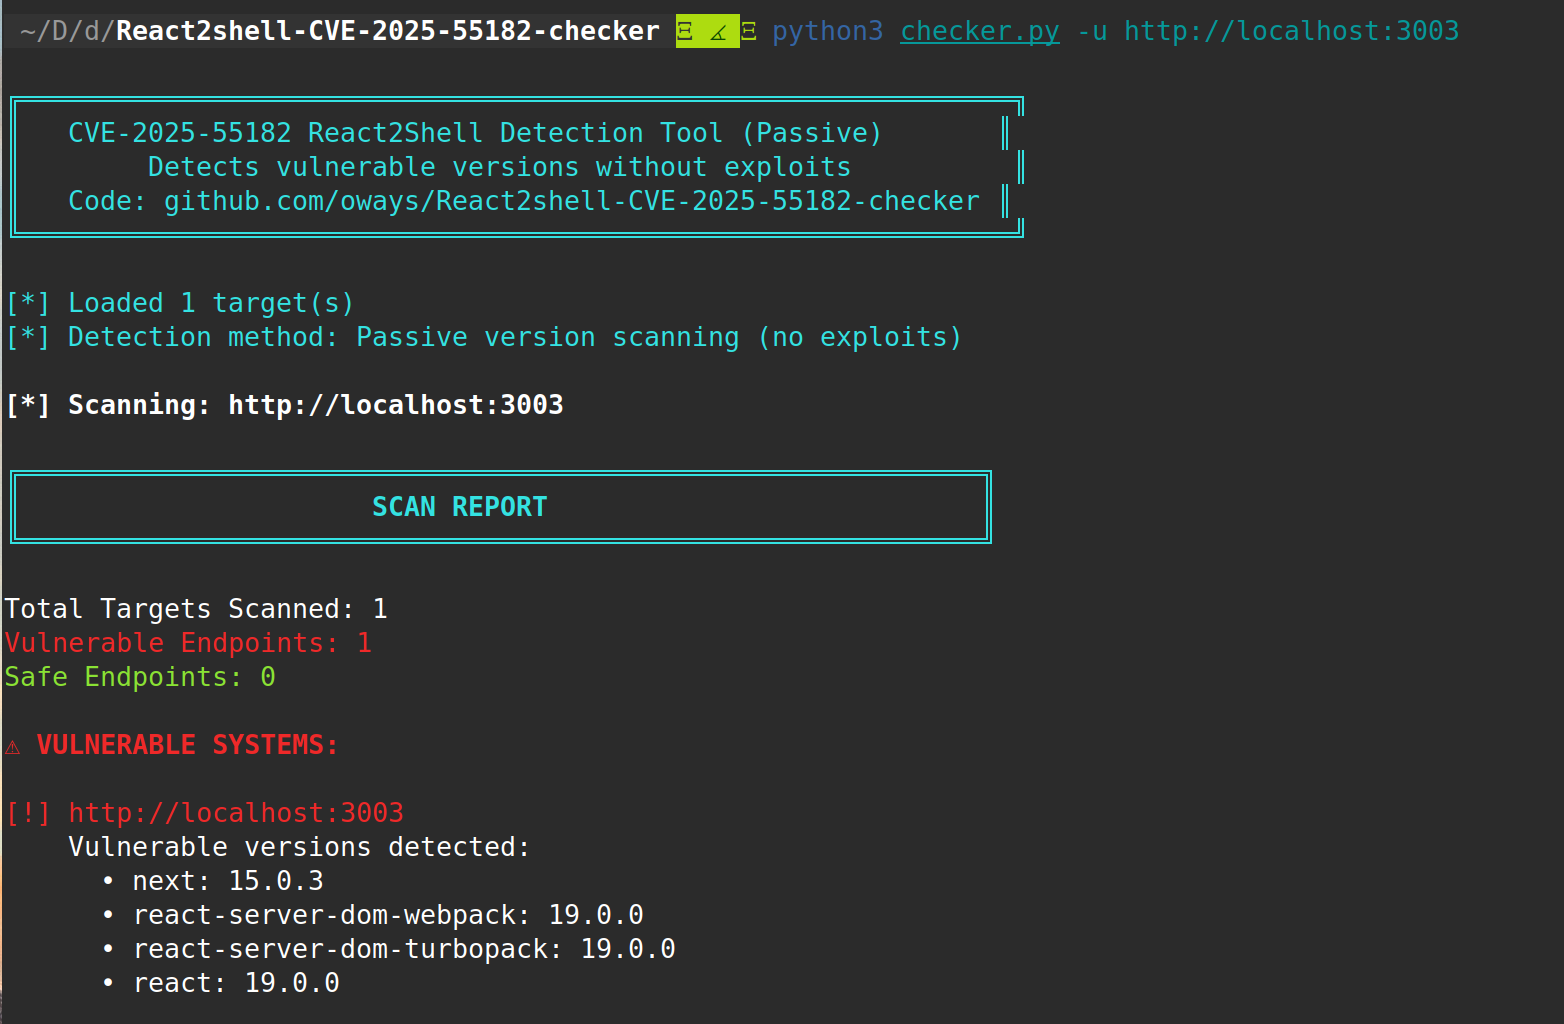
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…

Backport of the CVE-2020-6950 security fix to Mojarra 2.2.13, providing a patched jsf-impl JAR with minimal, reviewable changes for legacy…

go CVE-2023-24538 patch issue resolver - Dunfell

Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).

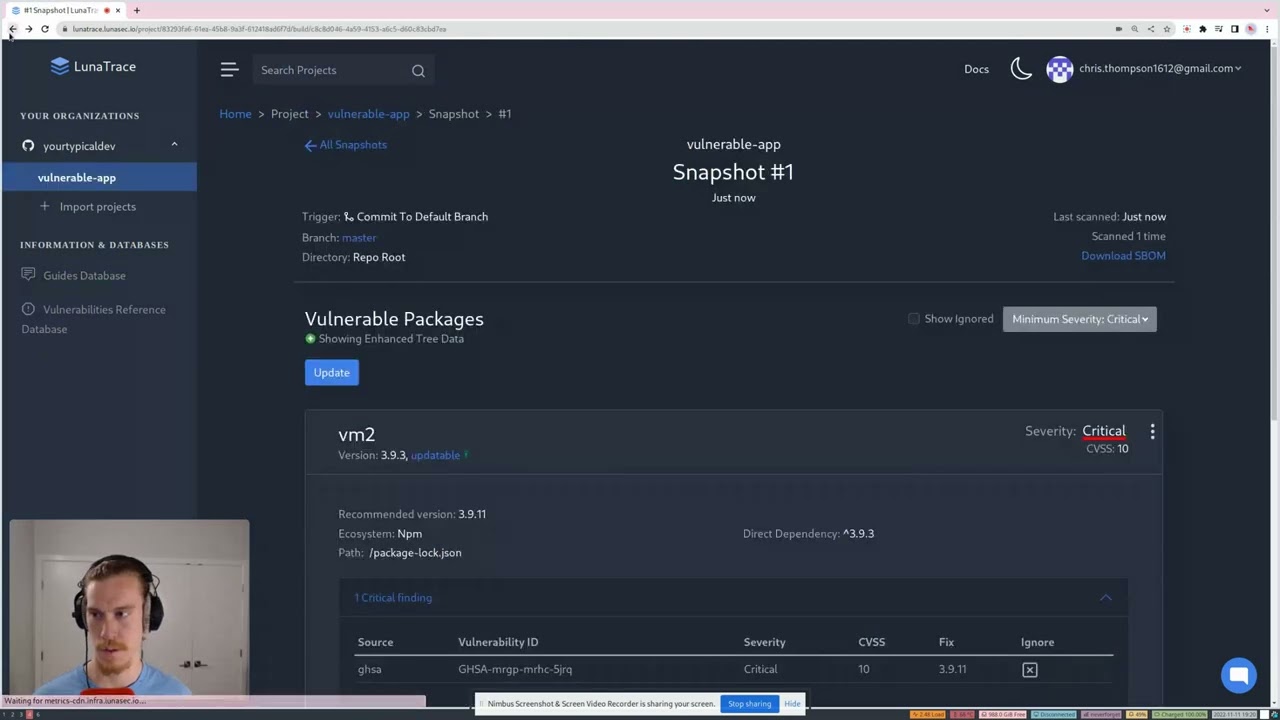
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…

Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…

PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…

Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…