
ClearML-CVE-2024-24590
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
ai-securityexploitationpayload-generation+3
6
oxydev2/clearml-cve-2024-24590Proof of concept for CVE-2024-24590
 s0ld13rr/claude-code-backdoor
Backdooring Claude Code via hooks in settings.json. Authorized use only!
 joaoleonello/cve-2024-32002-poc
Proof of Concept for CVE-2024-32002: Git submodule path injection vulnerability.
 justinsteven/cve-2020-10759-poc
Proof of Concept for CVE-2020-10759 (fwupd signature validation bypass)
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 ahmedreda38/cve-2025-47273-poc
CVE-2025-47273 is a high-severity path traversal vulnerability in the setuptools library ,specifically version 78.1.0 .
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
 jvr2022/cve-2026-31802
Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 timwr/cve-2017-1000117
Proof of concept of CVE-2017-1000117
 csirttrizna/cve-2024-55587
Proof-of-concept exploit for CVE-2024-55587 in libarchive, demonstrating unsafe extraction via malicious ZIP files.
 alielkhatteb/cve-2025-47273-poc
CVE-2025-47273 — setuptools path traversal PoC
 h4mr3r/cve-2024-5082
Proof-of-concept exploit for CVE-2024-5082, a remote code execution vulnerability in Sonatype Nexus Repository Manager 2 via crafted Maven artifacts…
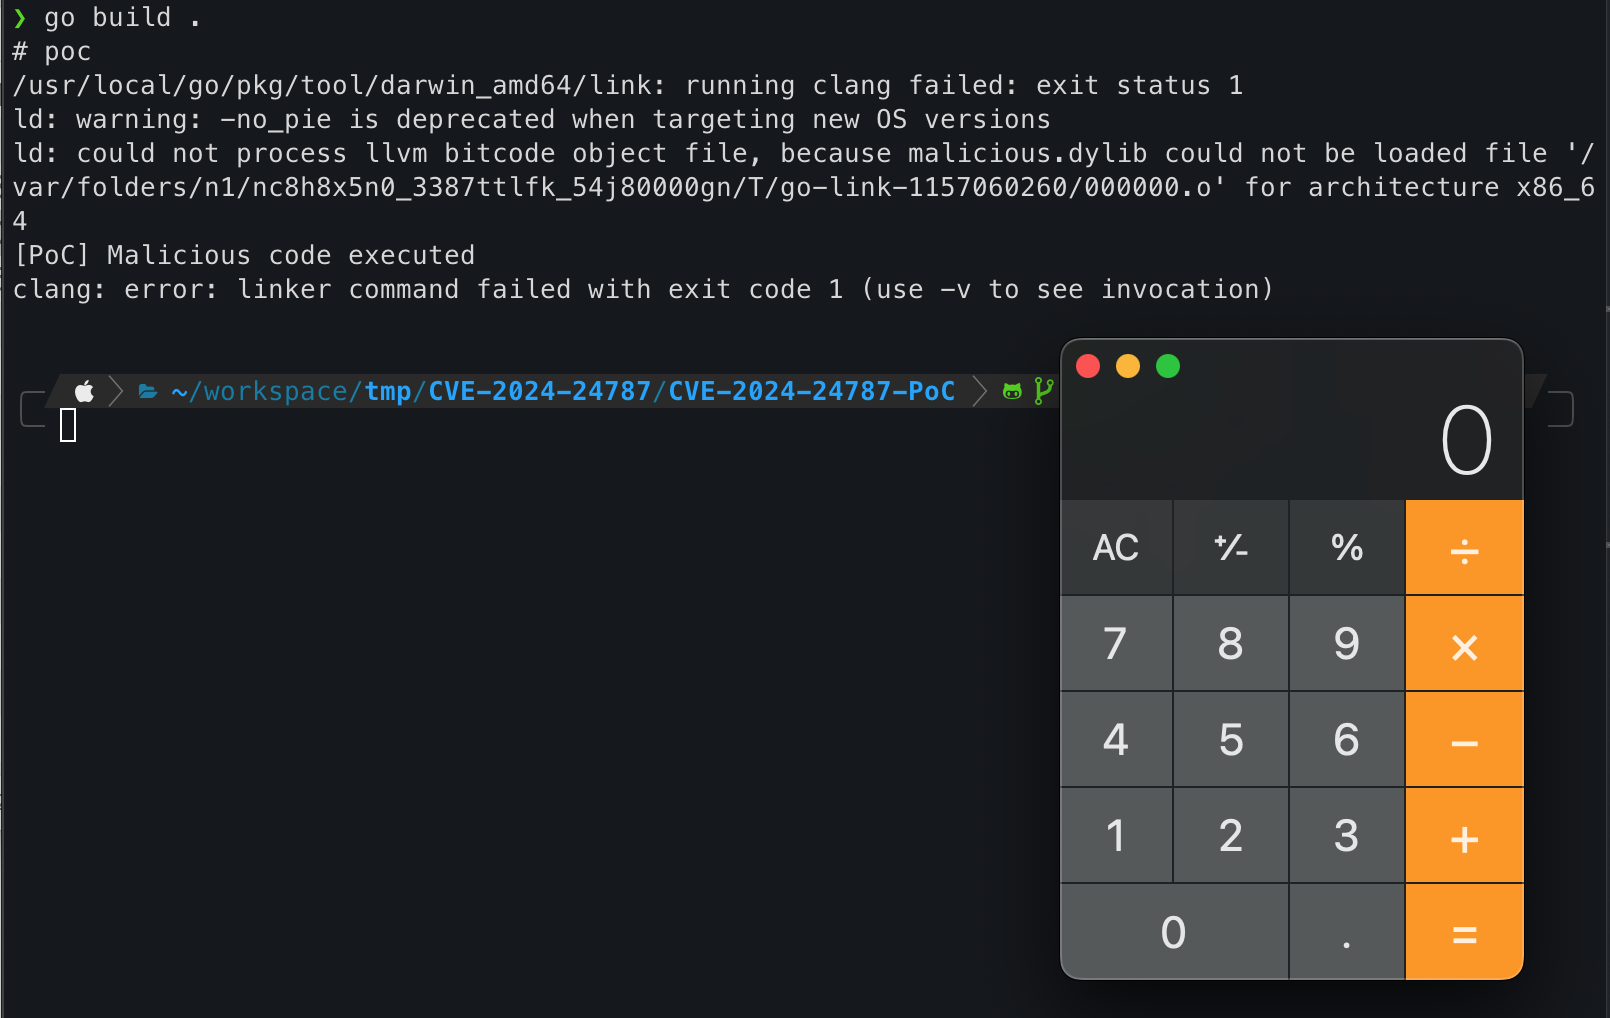 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept
 grassplatypus/cve-2026-45033-class
CVE-2026-45033 PoC for Claude Code, not Github Copilot. Worked for Haiku 4.5.
 markuta/cve-2024-32002
A proof of concept for the git vulnerability CVE-2024-32002
 ammaraskar/github-dev-token-steal-poc
Proof-of-concept exploit demonstrating a GitHub OAuth token-stealing vulnerability via crafted developer workflow triggers, enabling unauthorized…