

nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.3k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
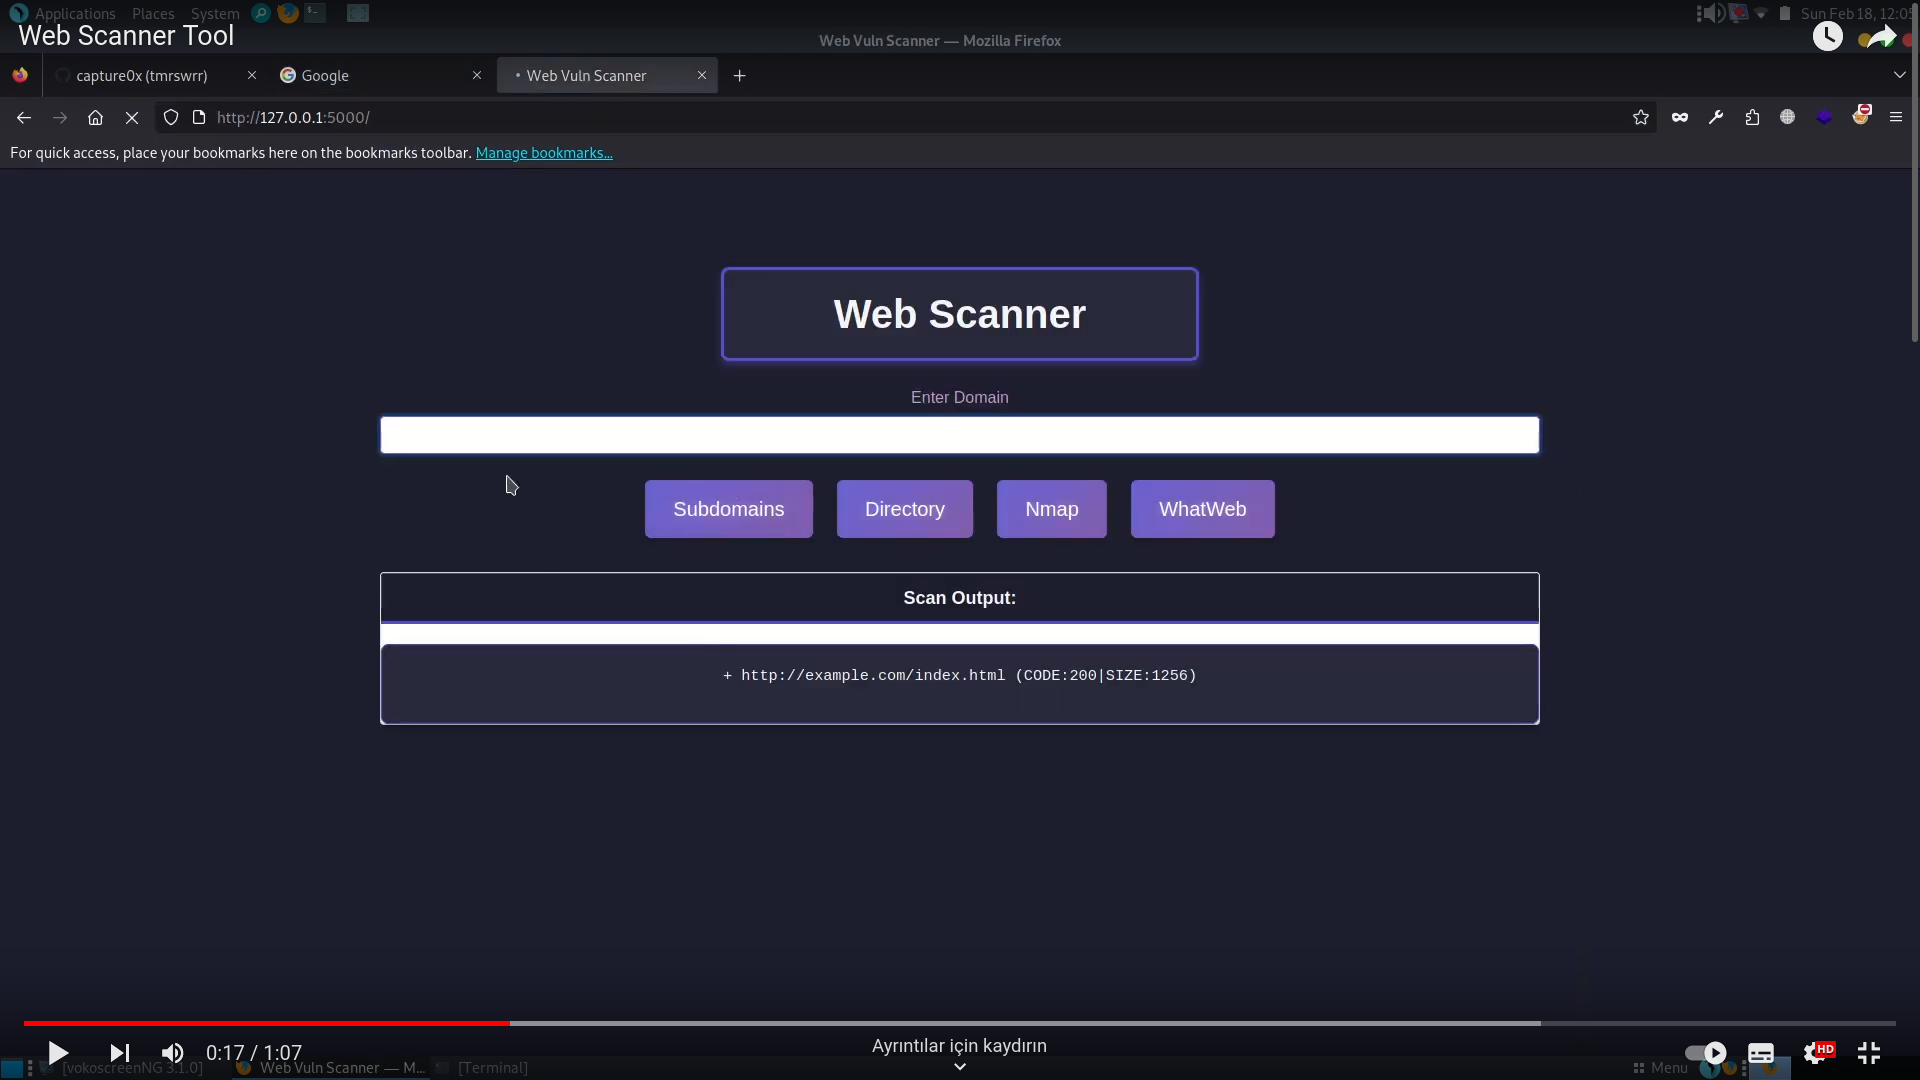 capture0x/web-scanner
Python-based web domain scanner integrating Sublist3r, Dirble, Nmap, and WhatWeb for subdomain discovery, directory enumeration, network scanning,…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 chrismaddalena/odin
Automated network asset, email, and social media profile discovery and cataloguing.
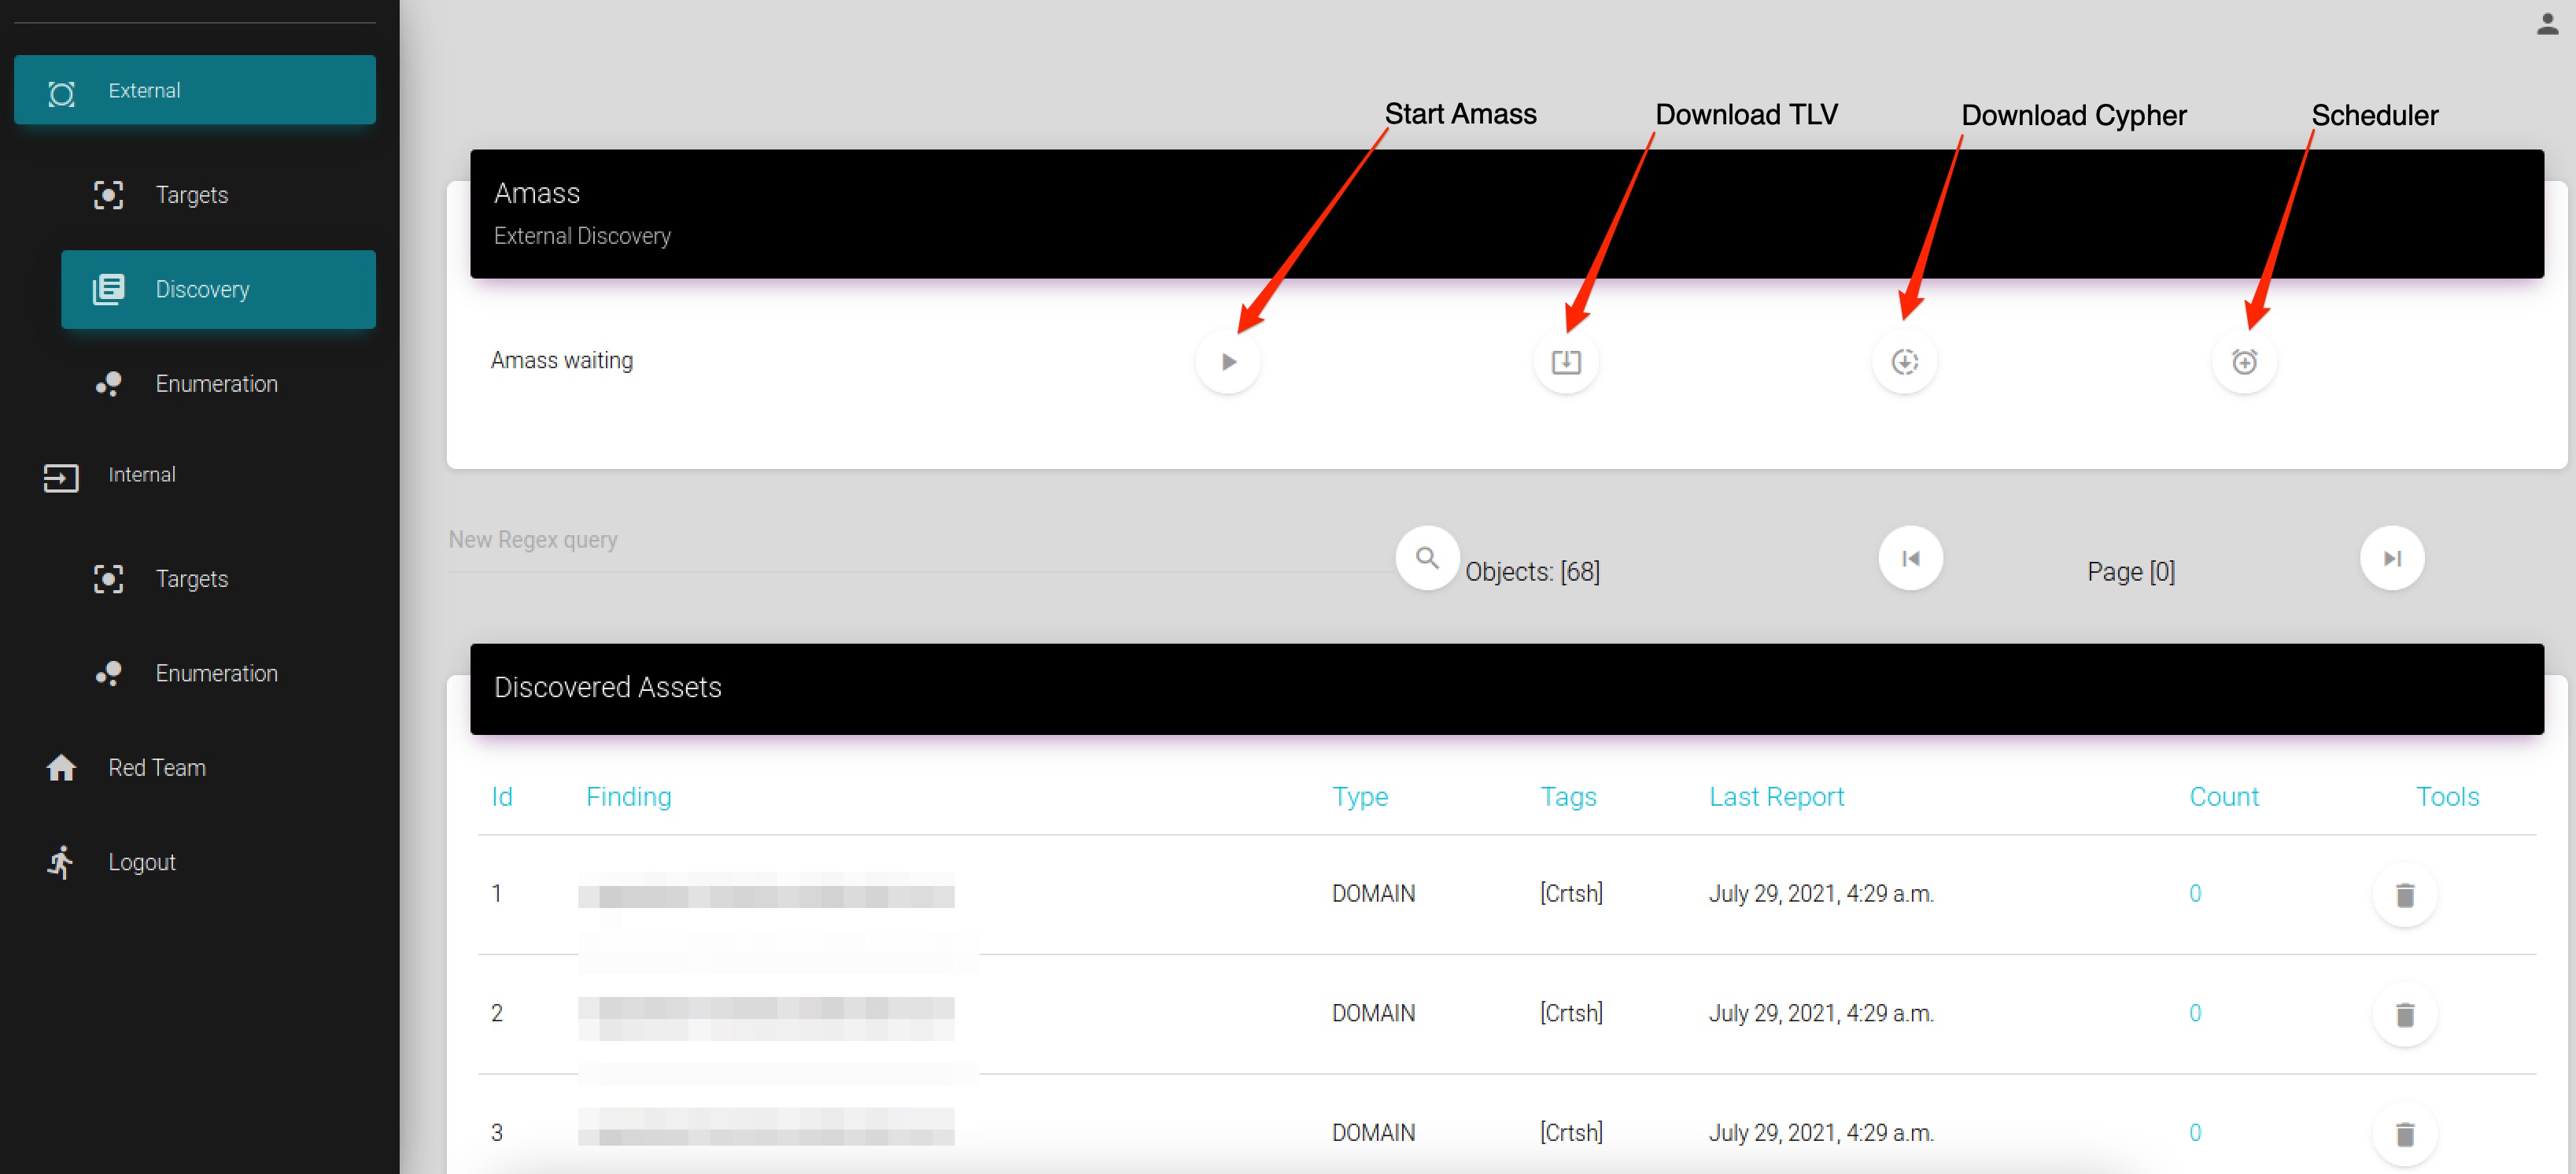 vmware-labs/attack-surface-framework
Tool to discover external and internal network attack surface
 hueristiq/xsubfind3r
Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…
 a3h1nt/sububy
Modular subdomain enumeration suite with certificate transparency, DNS brute-force, and API-based discovery. Includes post-enumeration modules for…
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT
 franccesco/getaltname
Extract subdomains from SSL certificates in HTTPS sites.
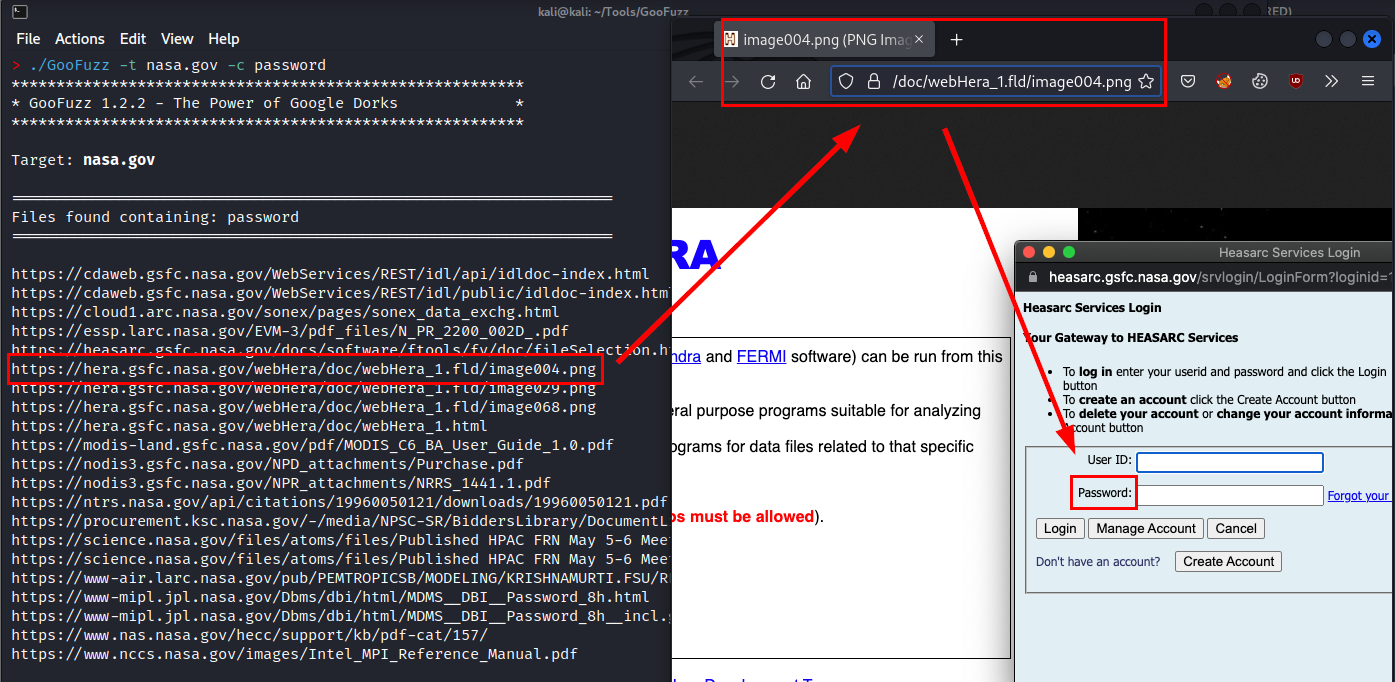 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 bountystrike/bountystrike-sh
Poor (rich?) man's bug bounty pipeline https://dubell.io
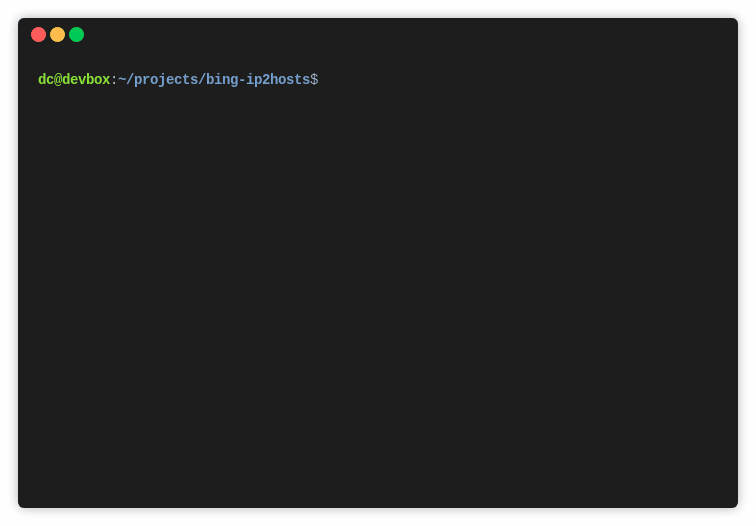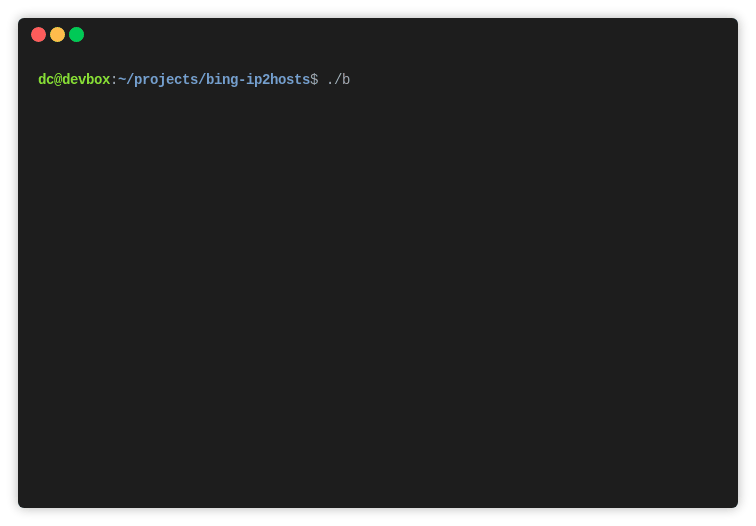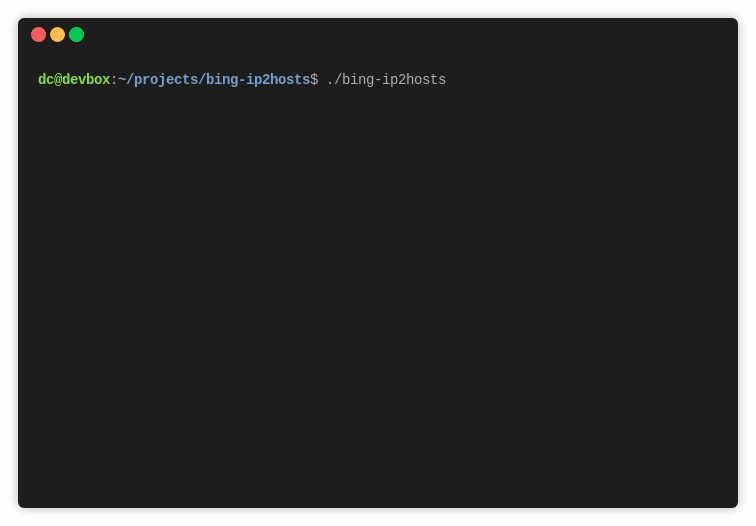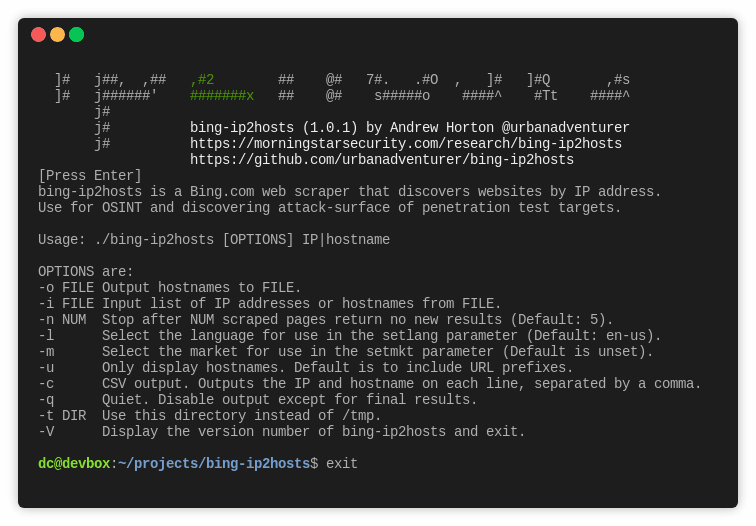 urbanadventurer/bing-ip2hosts
bingip2hosts is a Bing.com web scraper that discovers websites by IP address
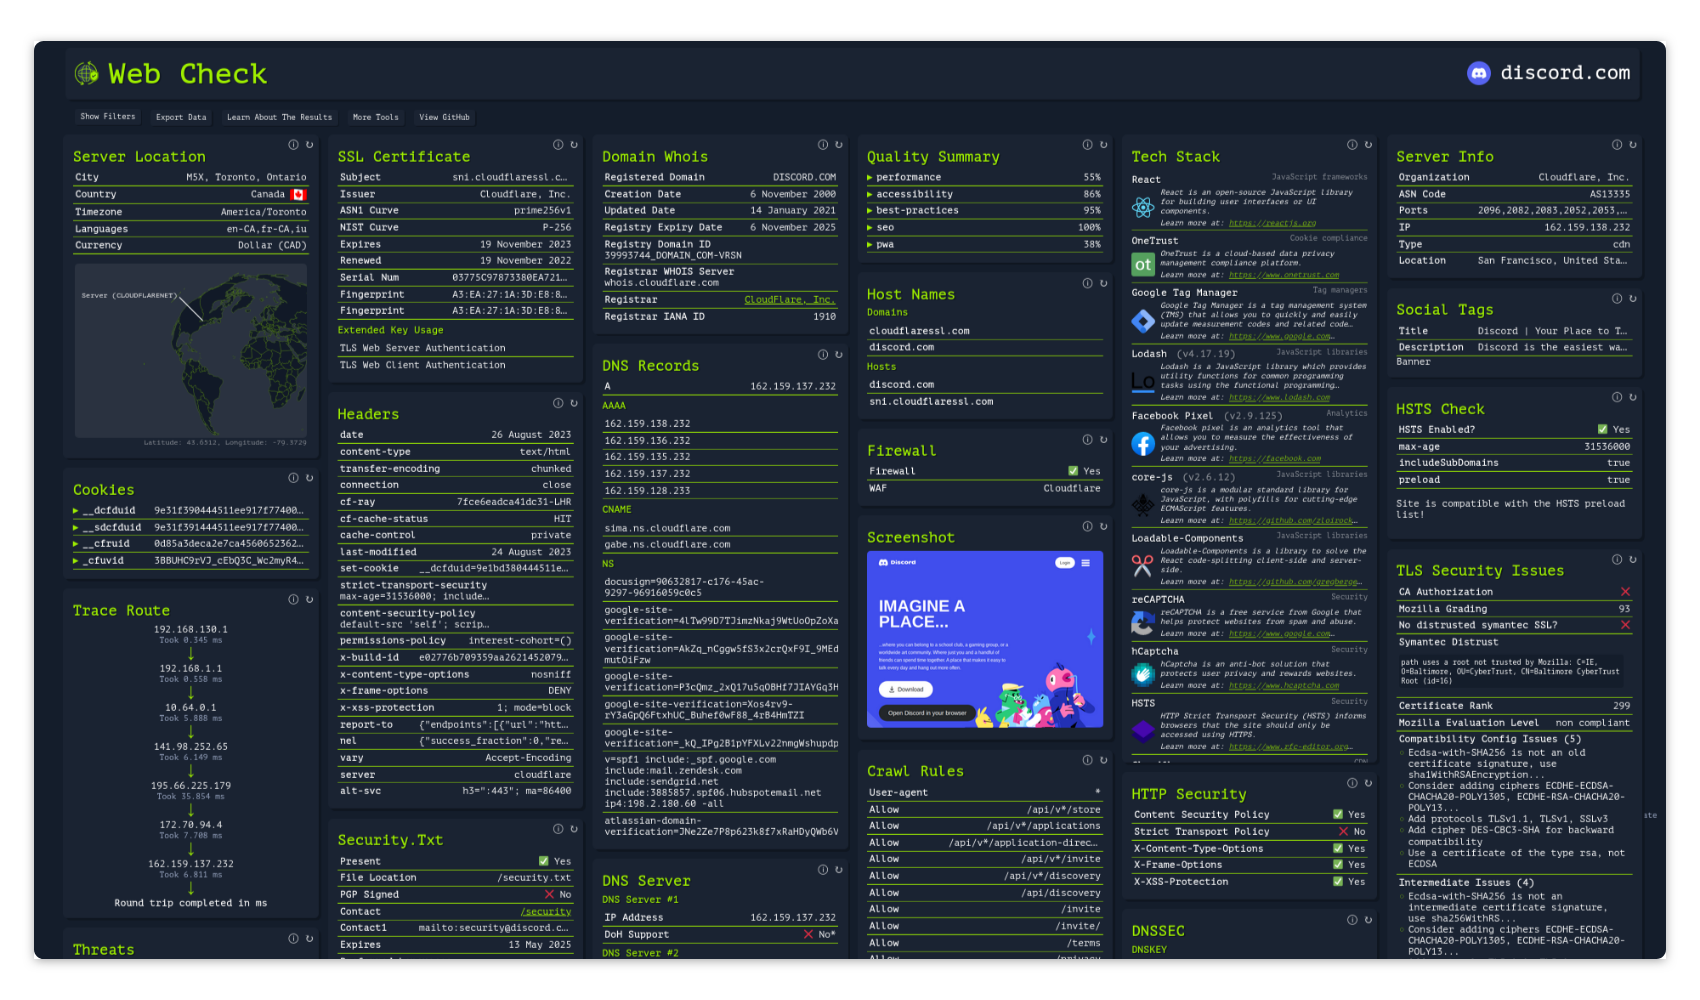 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
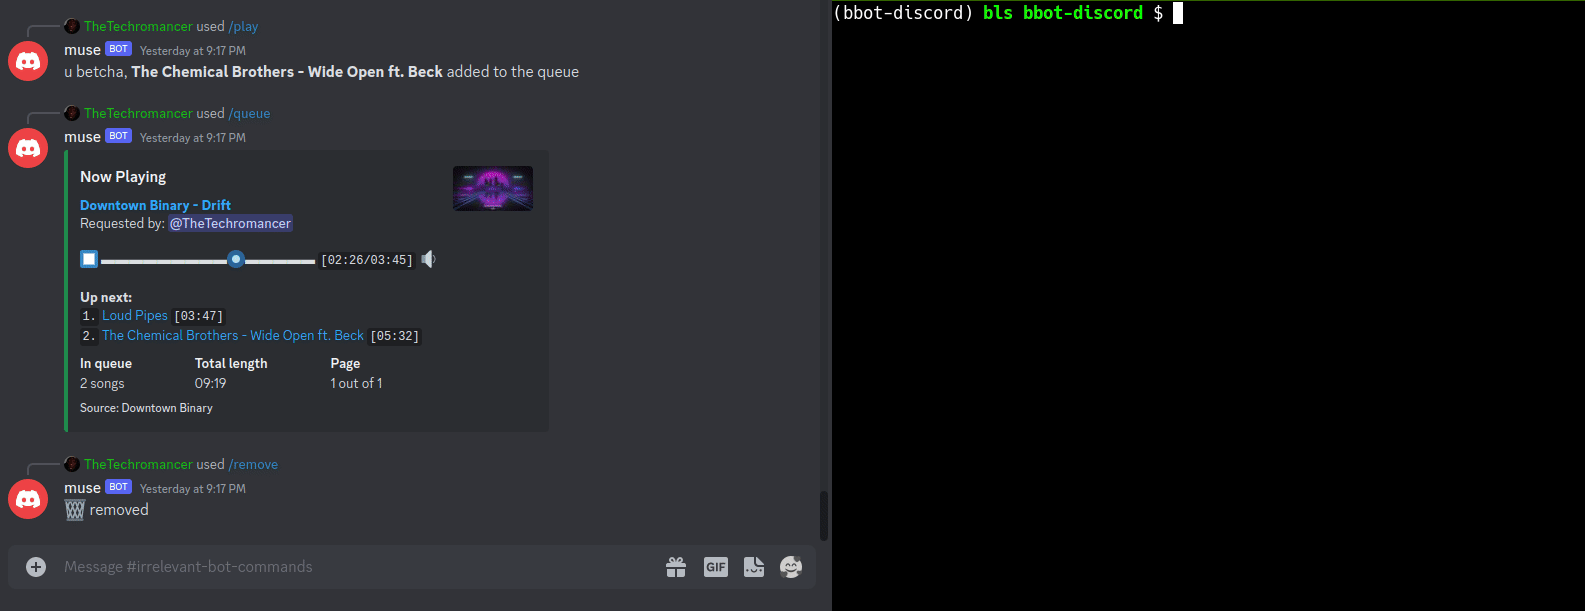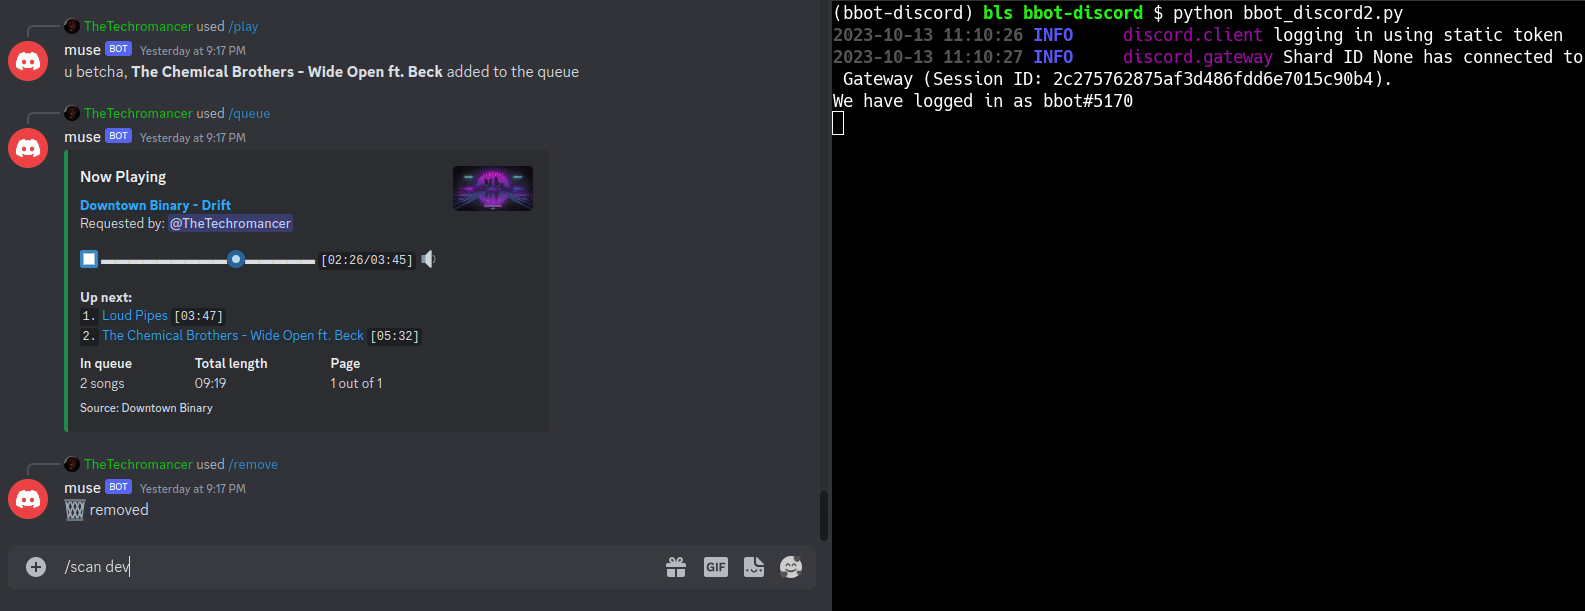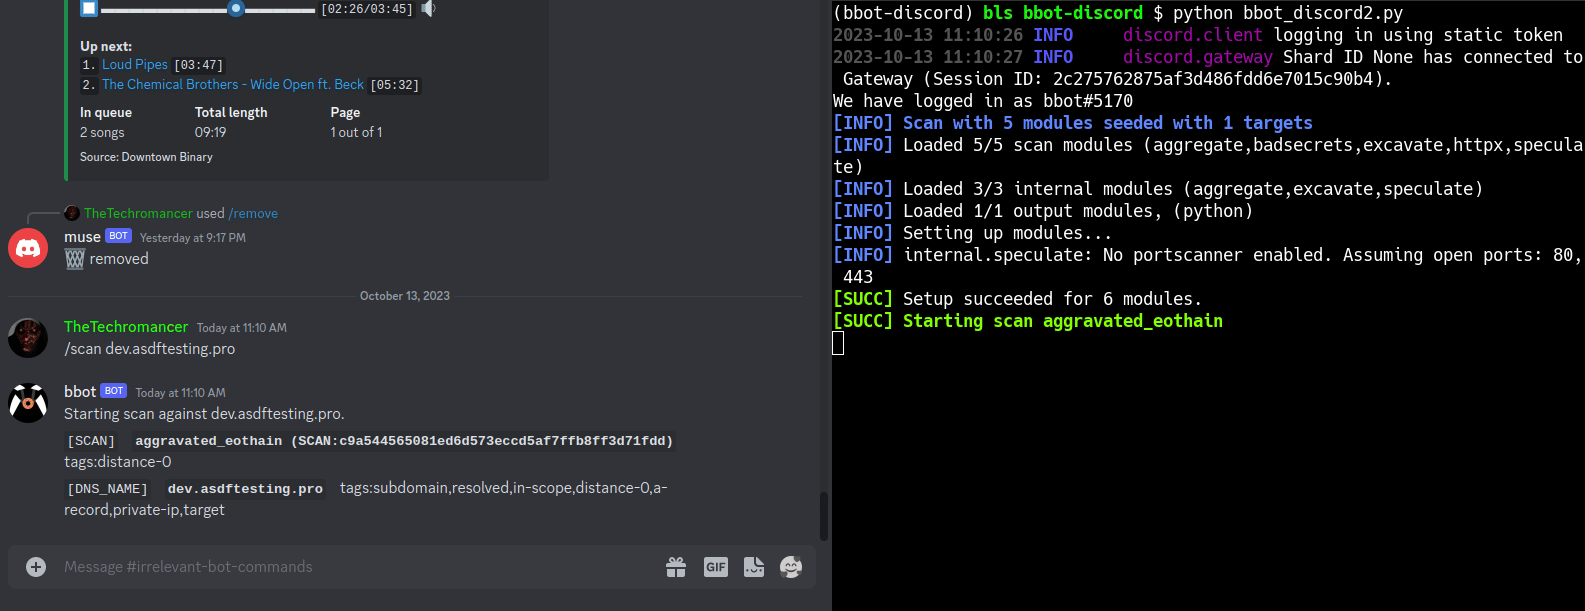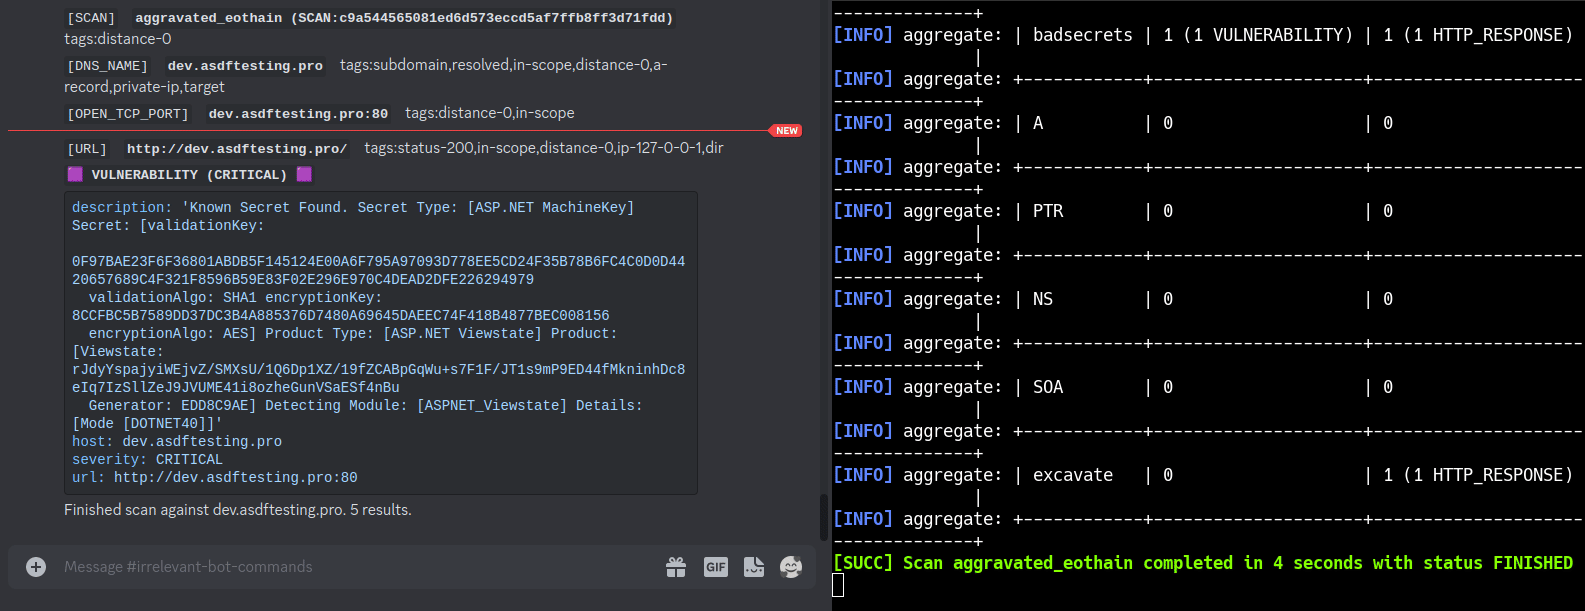 blacklanternsecurity/bbot
The recursive internet scanner for hackers. 🧡
 datasploit/datasploit
An #OSINT Framework to perform various recon techniques on Companies, People, Phone Number, Bitcoin Addresses, etc., aggregate all the raw data, and…
 kpcyrd/sn0int
Semi-automatic OSINT framework and package manager