

PocketPentester
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
dns-analysisfuzzinghash-analysis+9
9
tegal1337/pocketpentesterOffline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 fleetcaptain/turbolist3r
Subdomain enumeration tool with analysis features for discovered domains
 thewhiteh4t/finalrecon
Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 threatunknown/jsubfinder
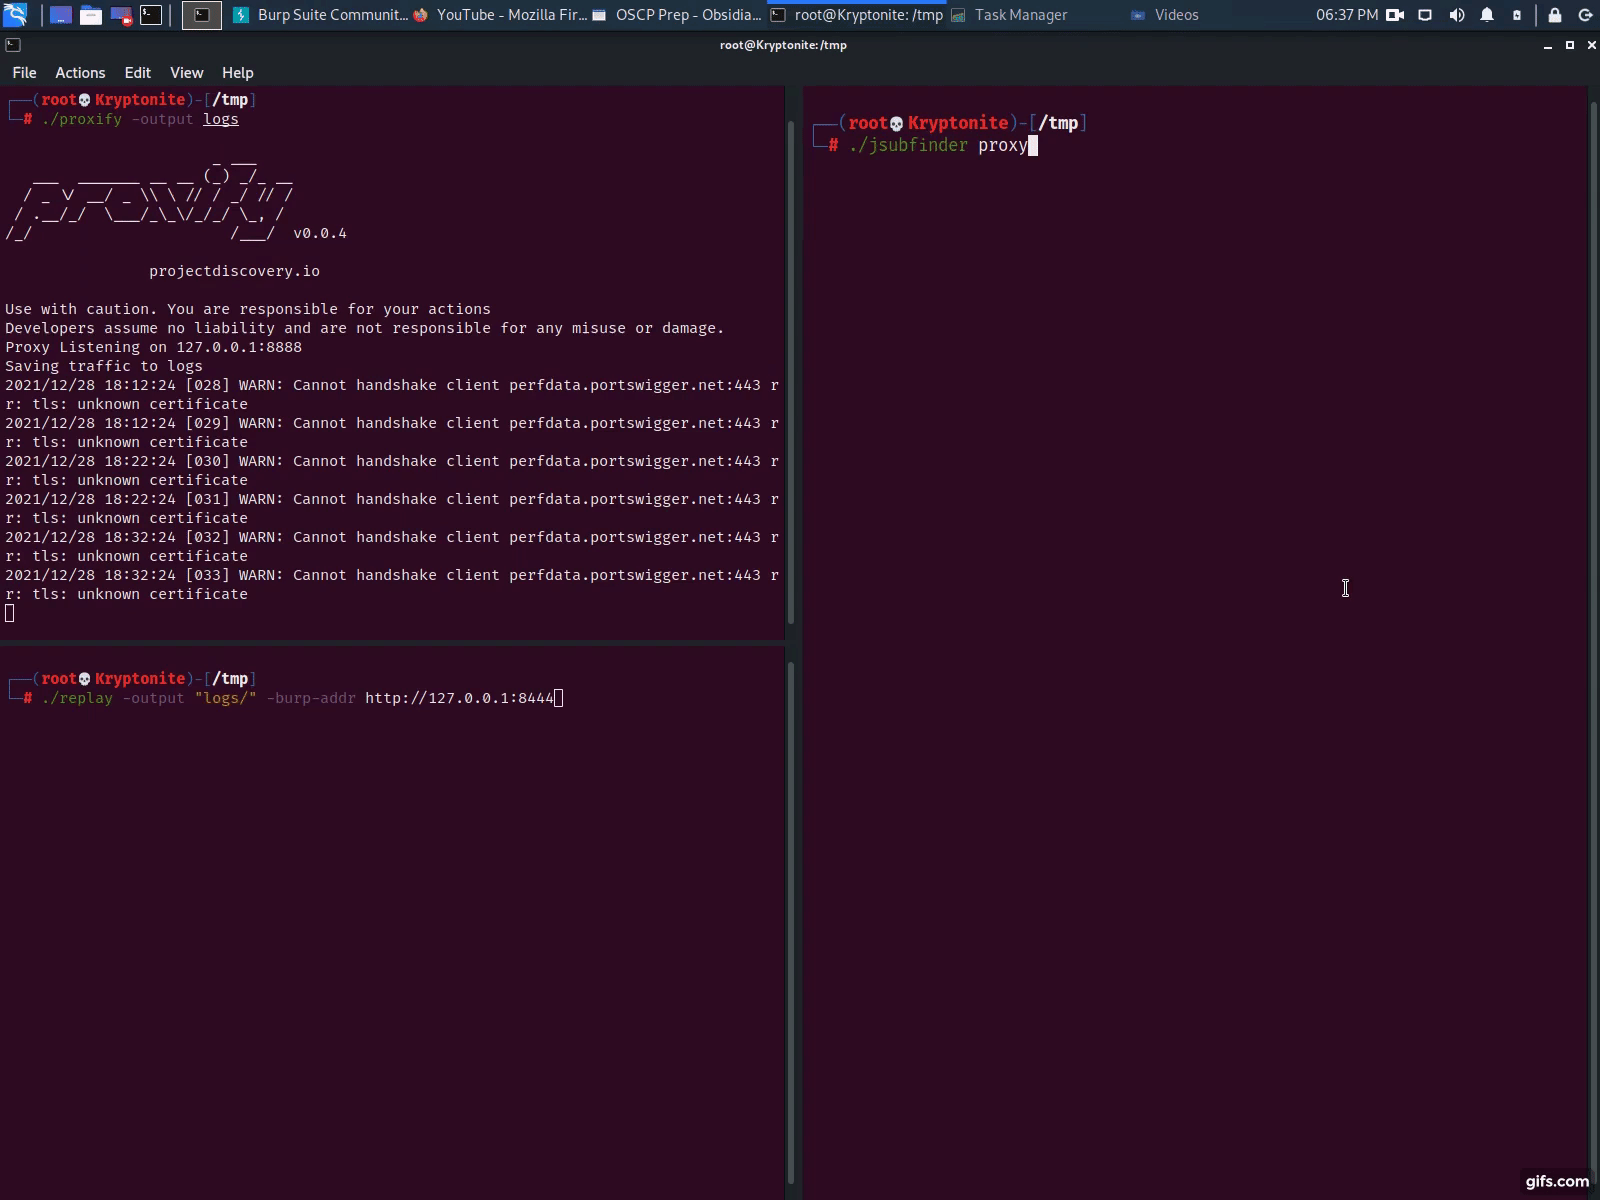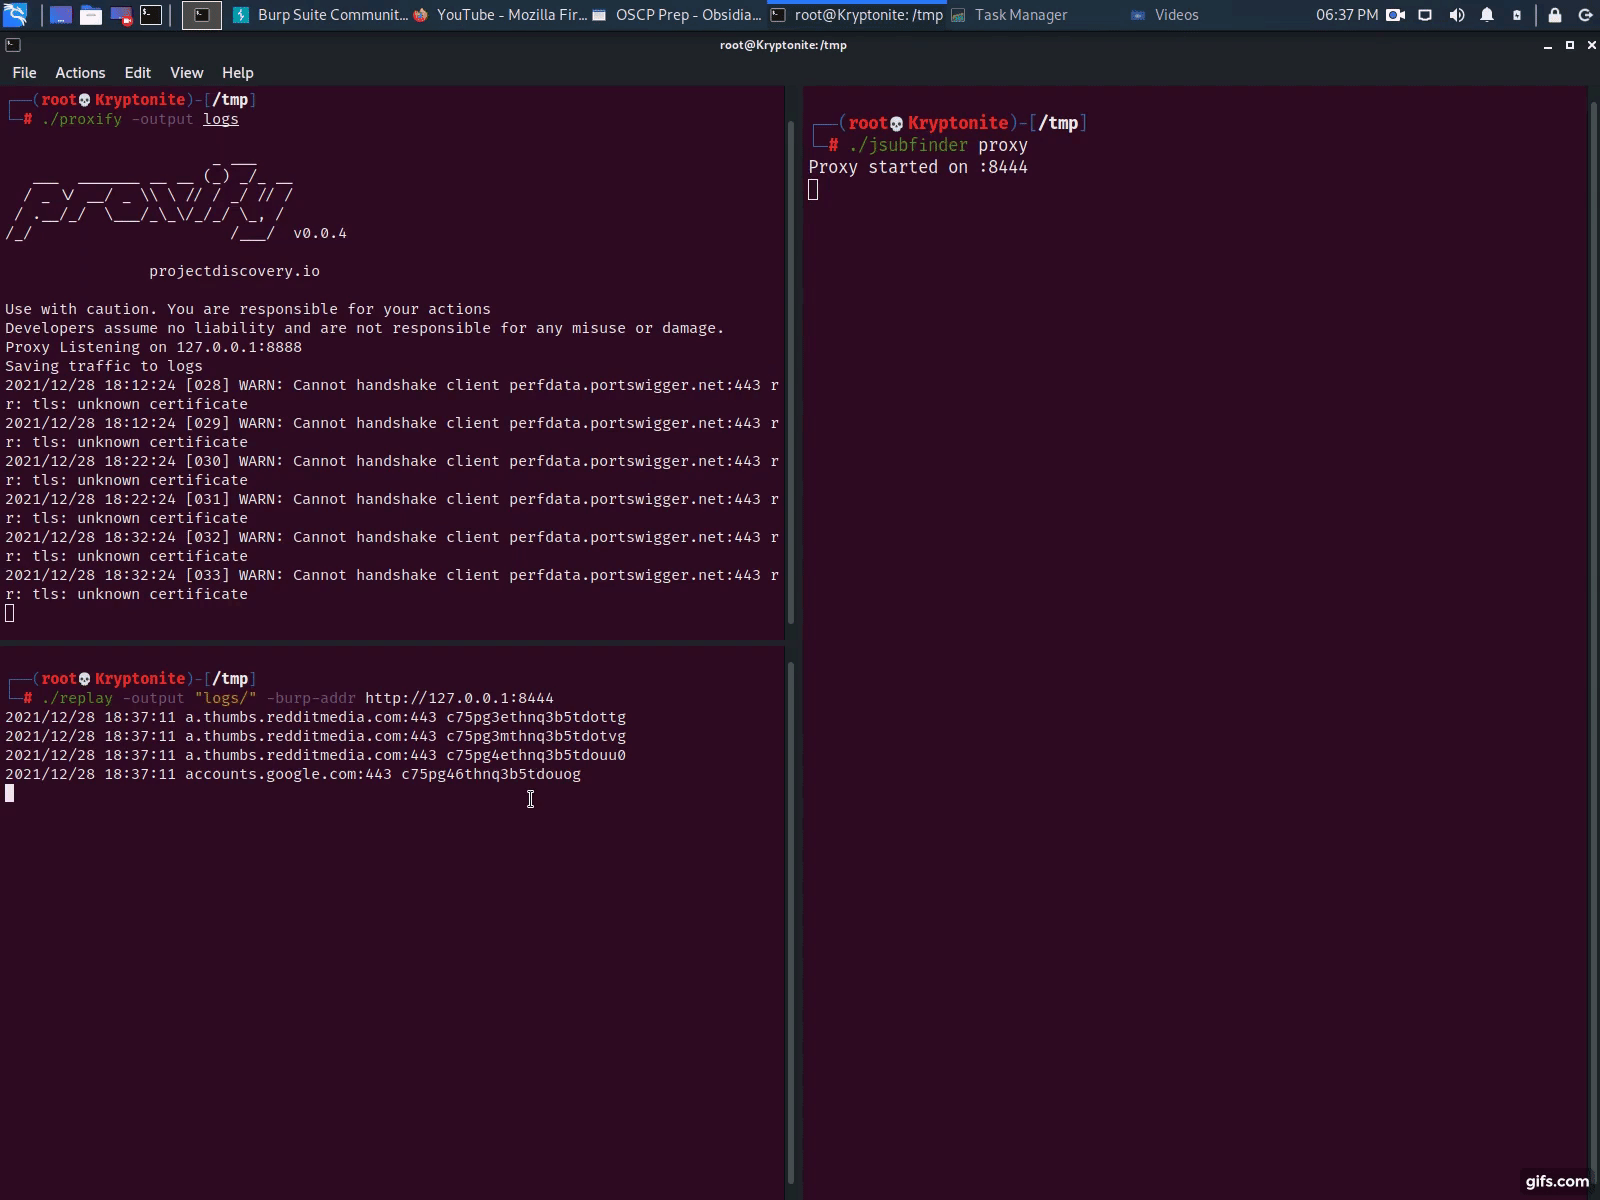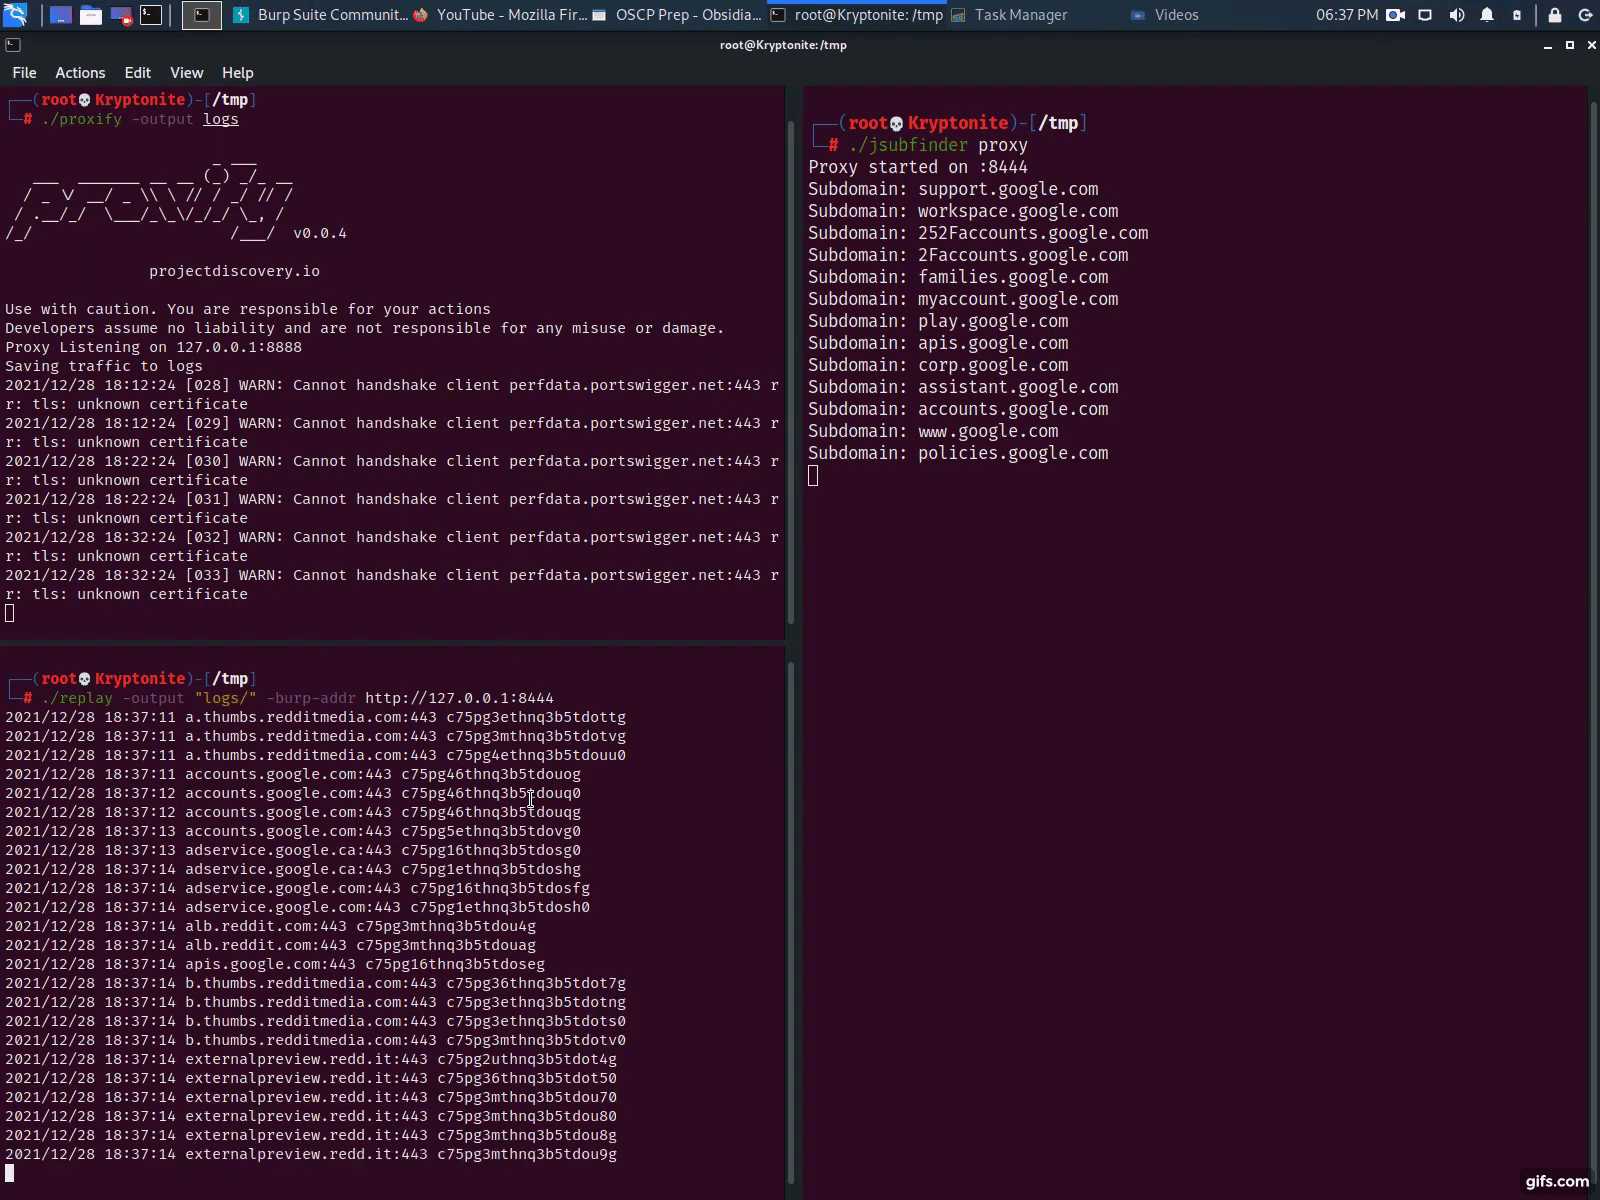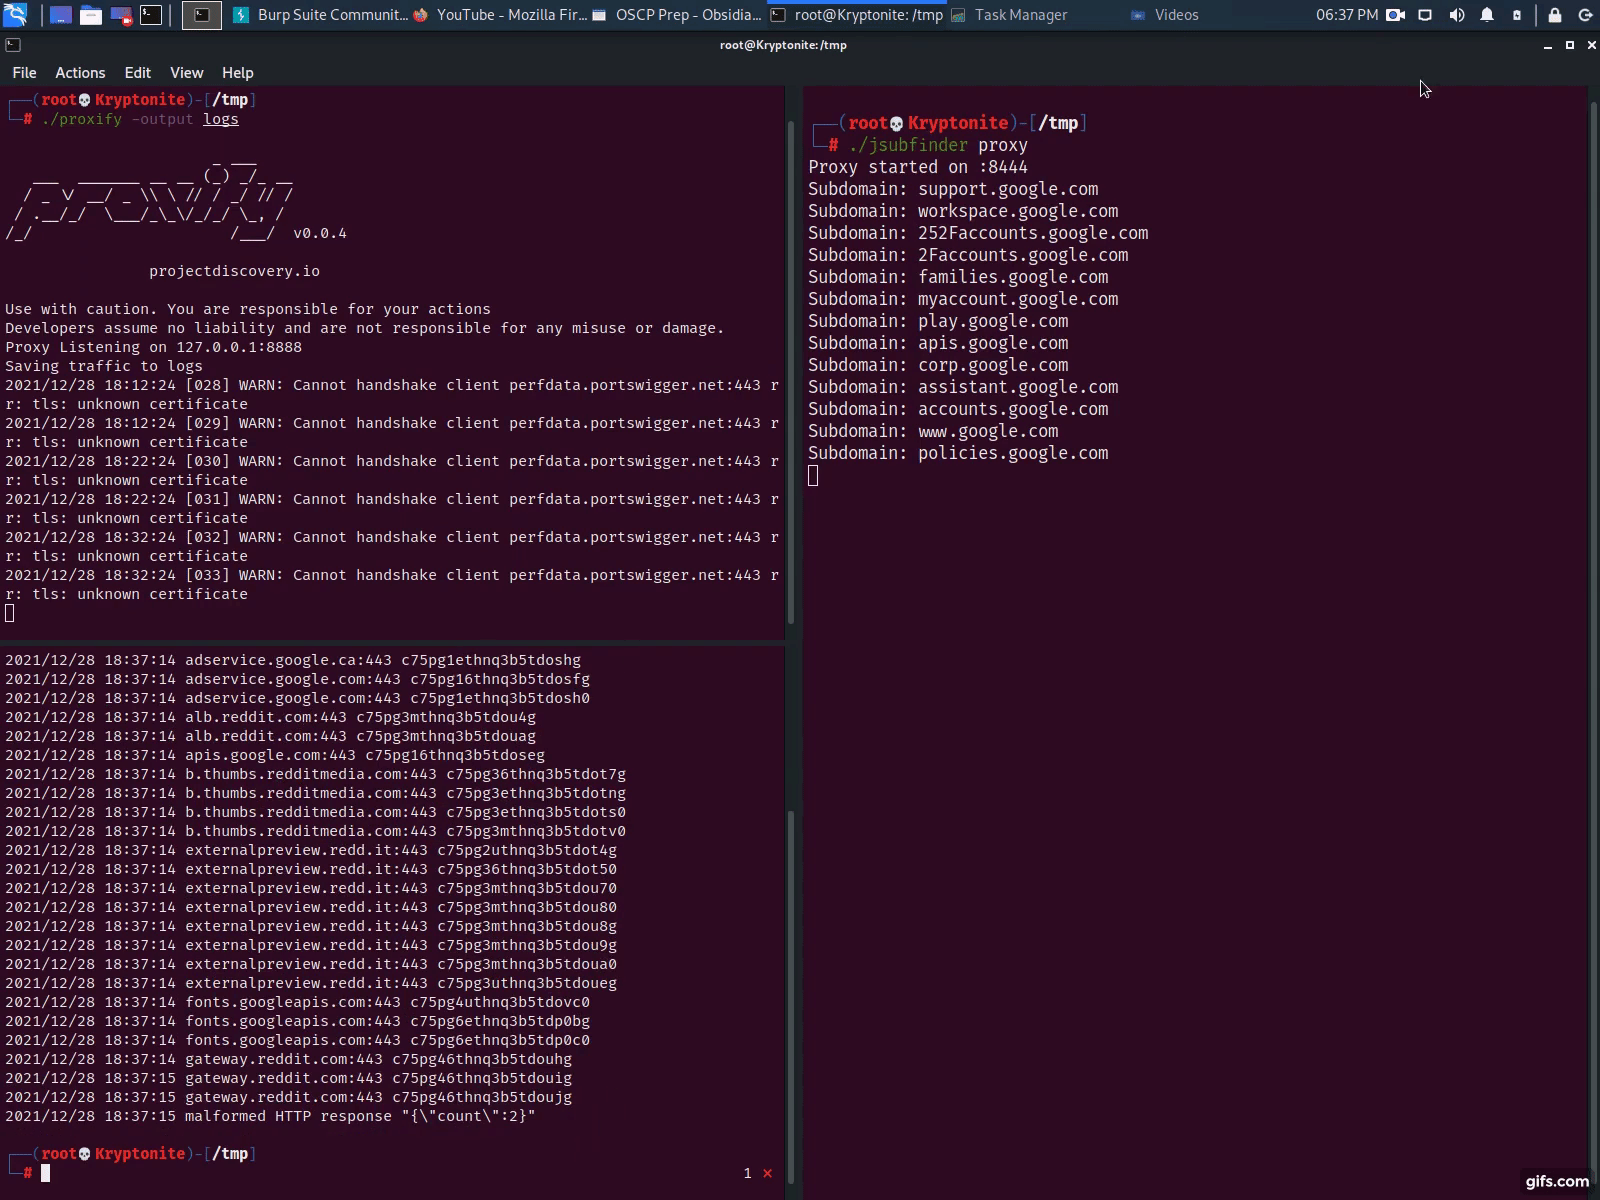
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
 netspi/ateam
Python reconnaissance tool for discovering Azure services and attributing tenant ownership via DNS validation, multi-service probing, and response…
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
 shamo0/cve-2021-44228
log4shell (CVE-2021-44228) scanning tool
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
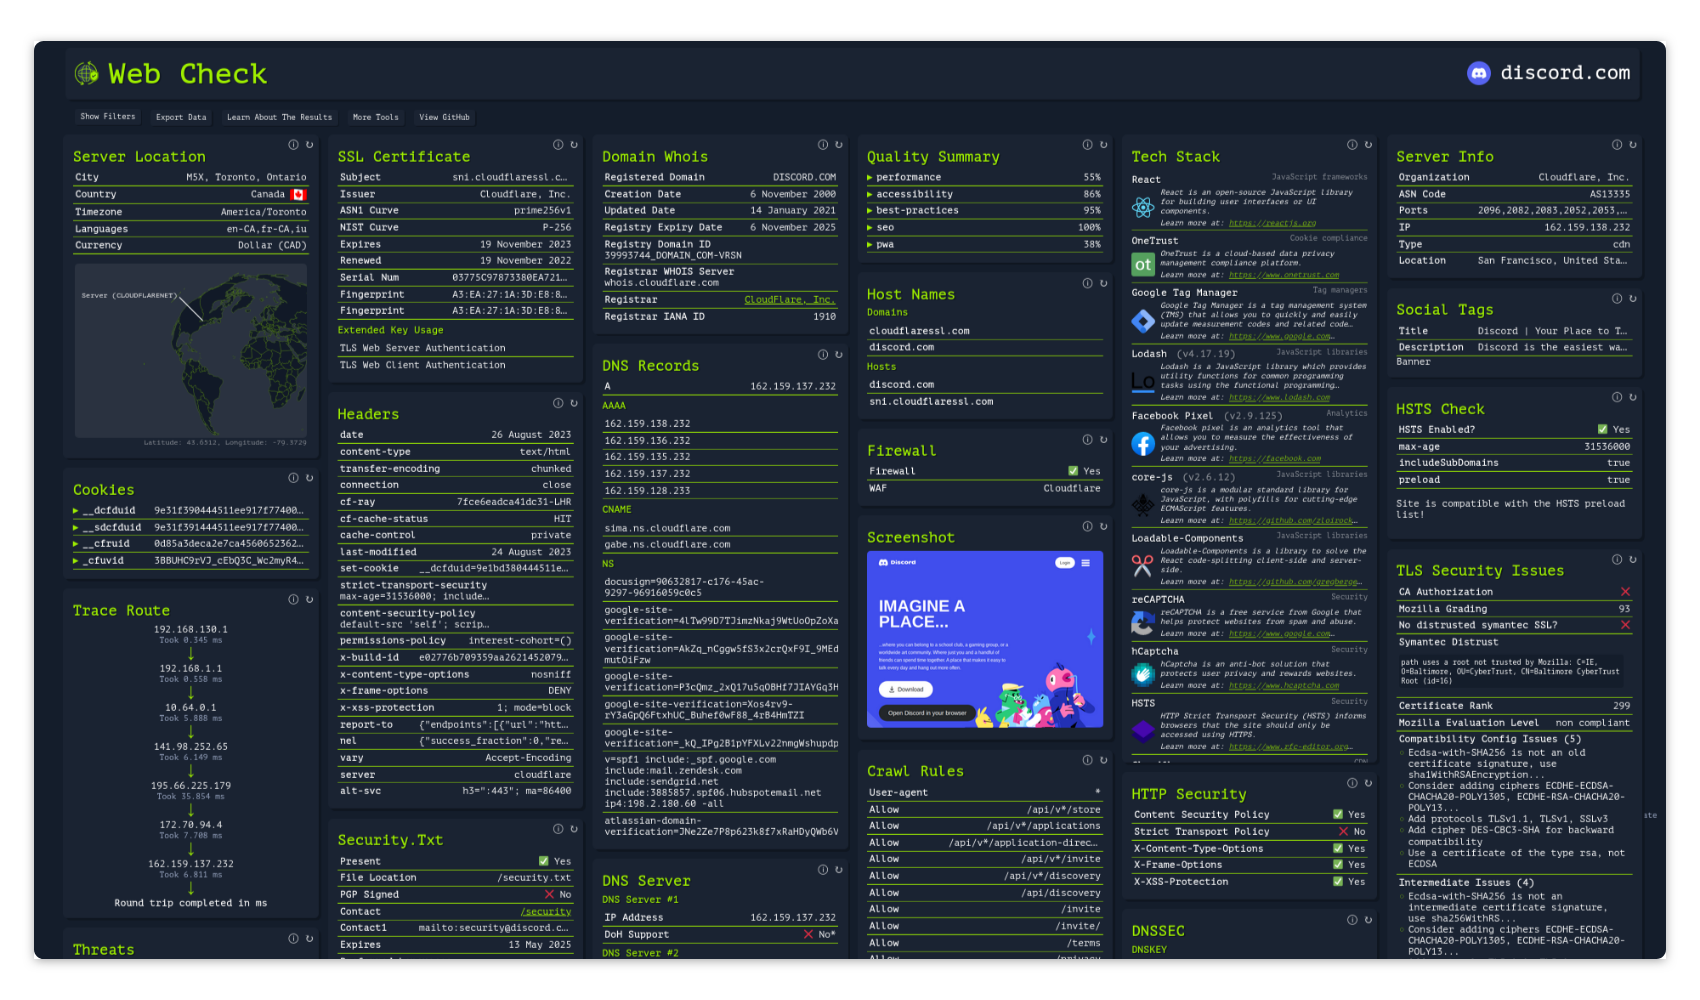 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
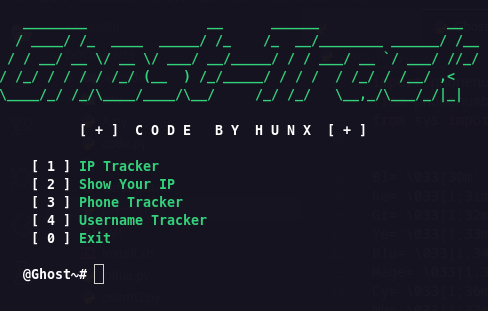 hunxbyts/ghosttrack
Useful tool to track location or mobile number
 projectdiscovery/subfinder
Fast passive subdomain enumeration tool.
 six2dez/reconftw
reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…
 borntoberoot/networkmanager
A powerful open-source tool for managing networks and troubleshooting network problems!
 aboul3la/sublist3r
Fast subdomains enumeration tool for penetration testers
 tuhinshubhra/red_hawk
All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
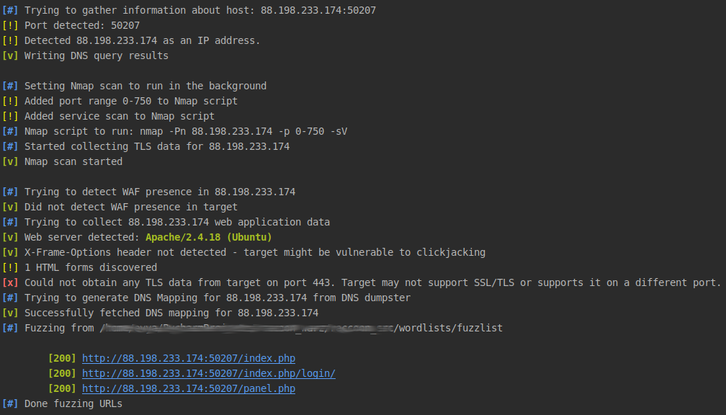 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 moham3driahi/th3inspector
Th3Inspector 🕵️ Best Tool For Information Gathering 🔎