
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…

 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
 projectdiscovery/shuffledns
MassDNS wrapper written in go to enumerate valid subdomains using active bruteforce as well as resolve subdomains with wildcard filtering and easy…
 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 nahamsec/hostilesubbruteforcer
Subdomain brute-forcing tool that enumerates existing subdomains and detects misconfigured cloud-hosted subdomains vulnerable to takeover across AWS,…
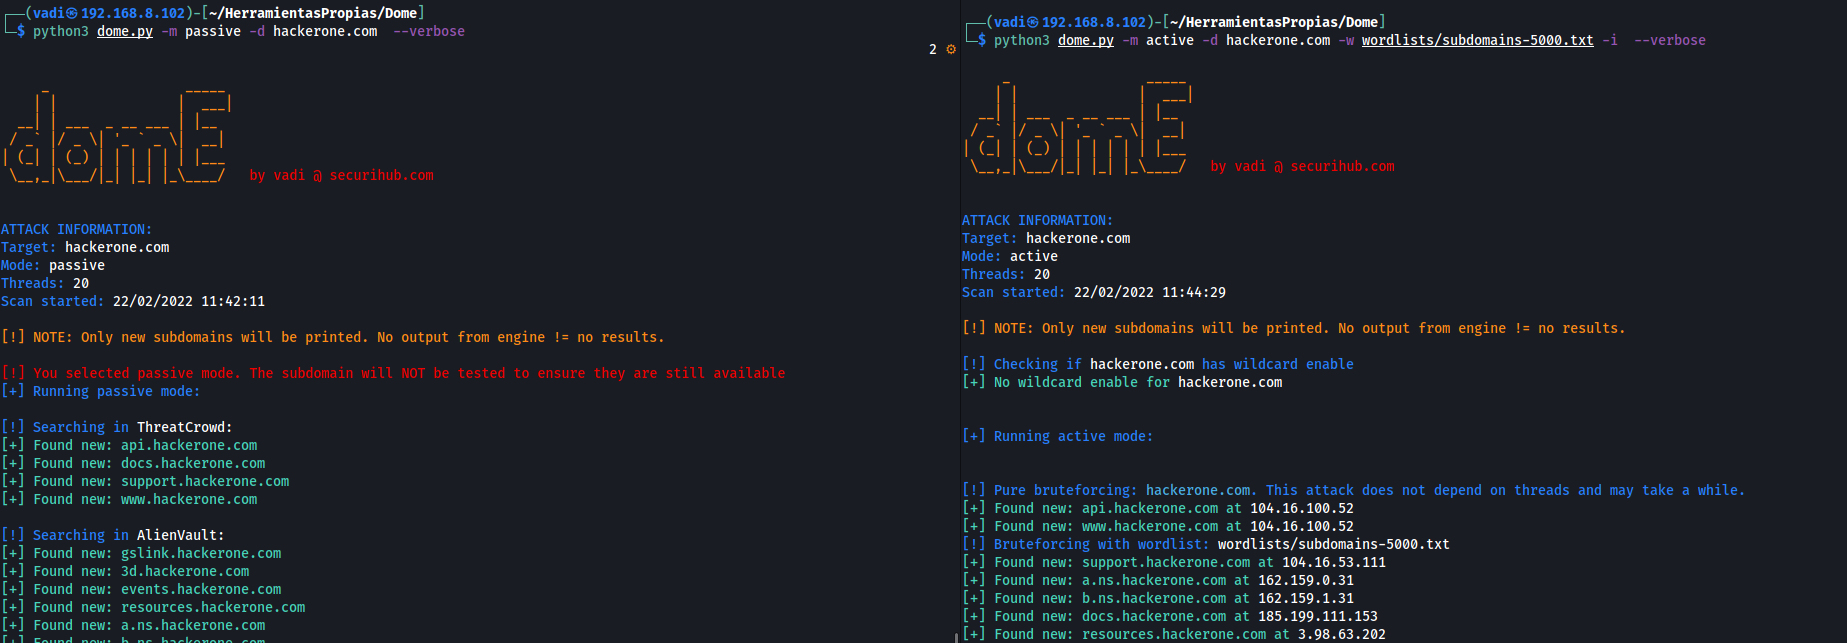 v4d1/dome
Fast Python-based subdomain enumeration tool combining passive OSINT and active brute-force scanning with DNS wildcard detection, port scanning, and…
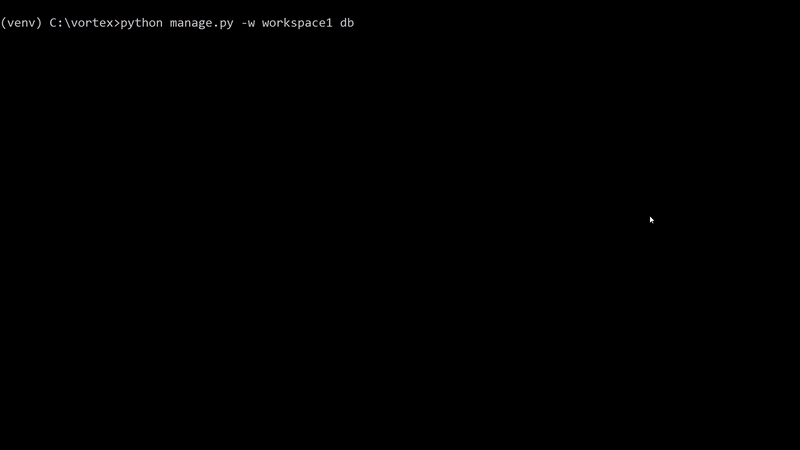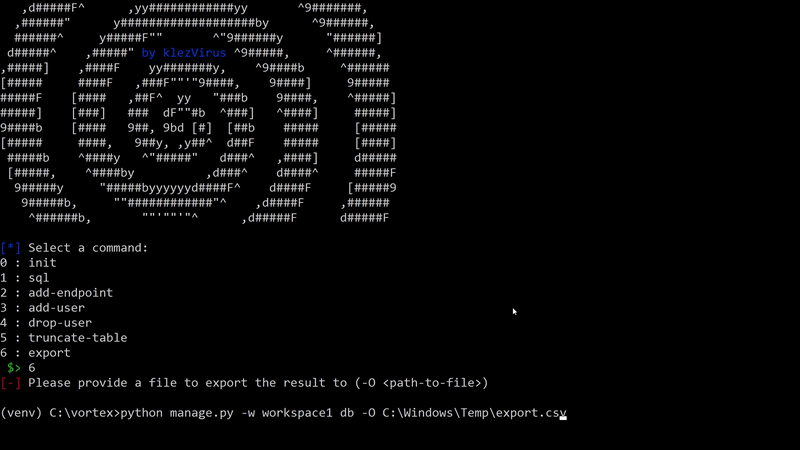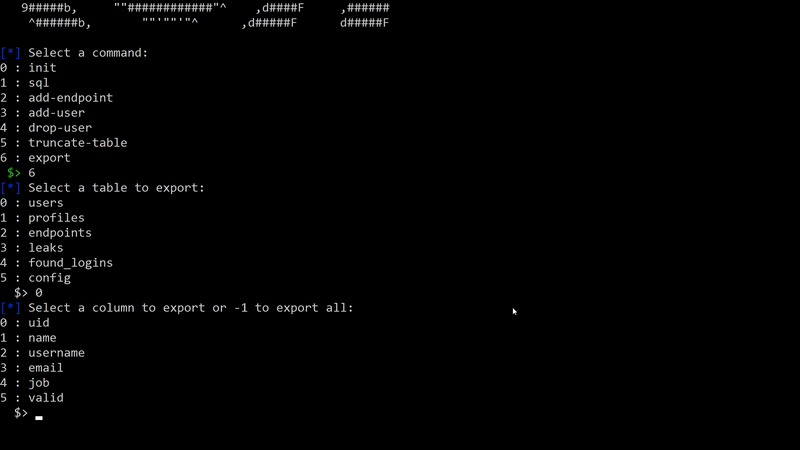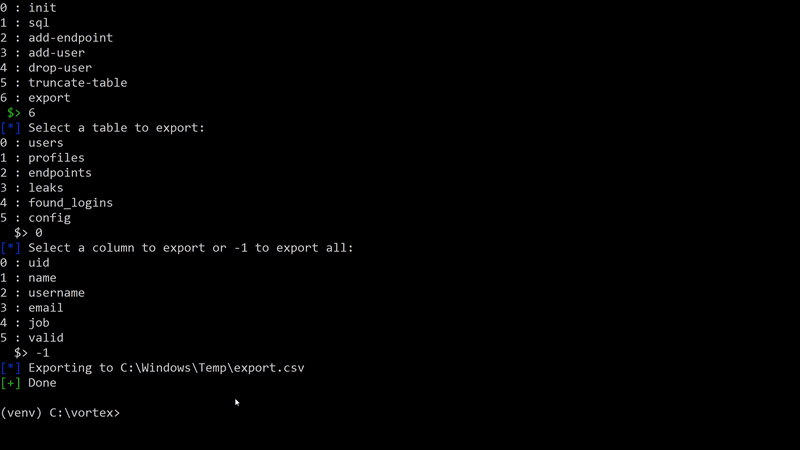 klezvirus/vortex
VPN Overall Reconnaissance, Testing, Enumeration and eXploitation Toolkit
 samhaxr/recox
Master script for web reconnaissance
 ya551n3/bug-bounty-wordlists
Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.
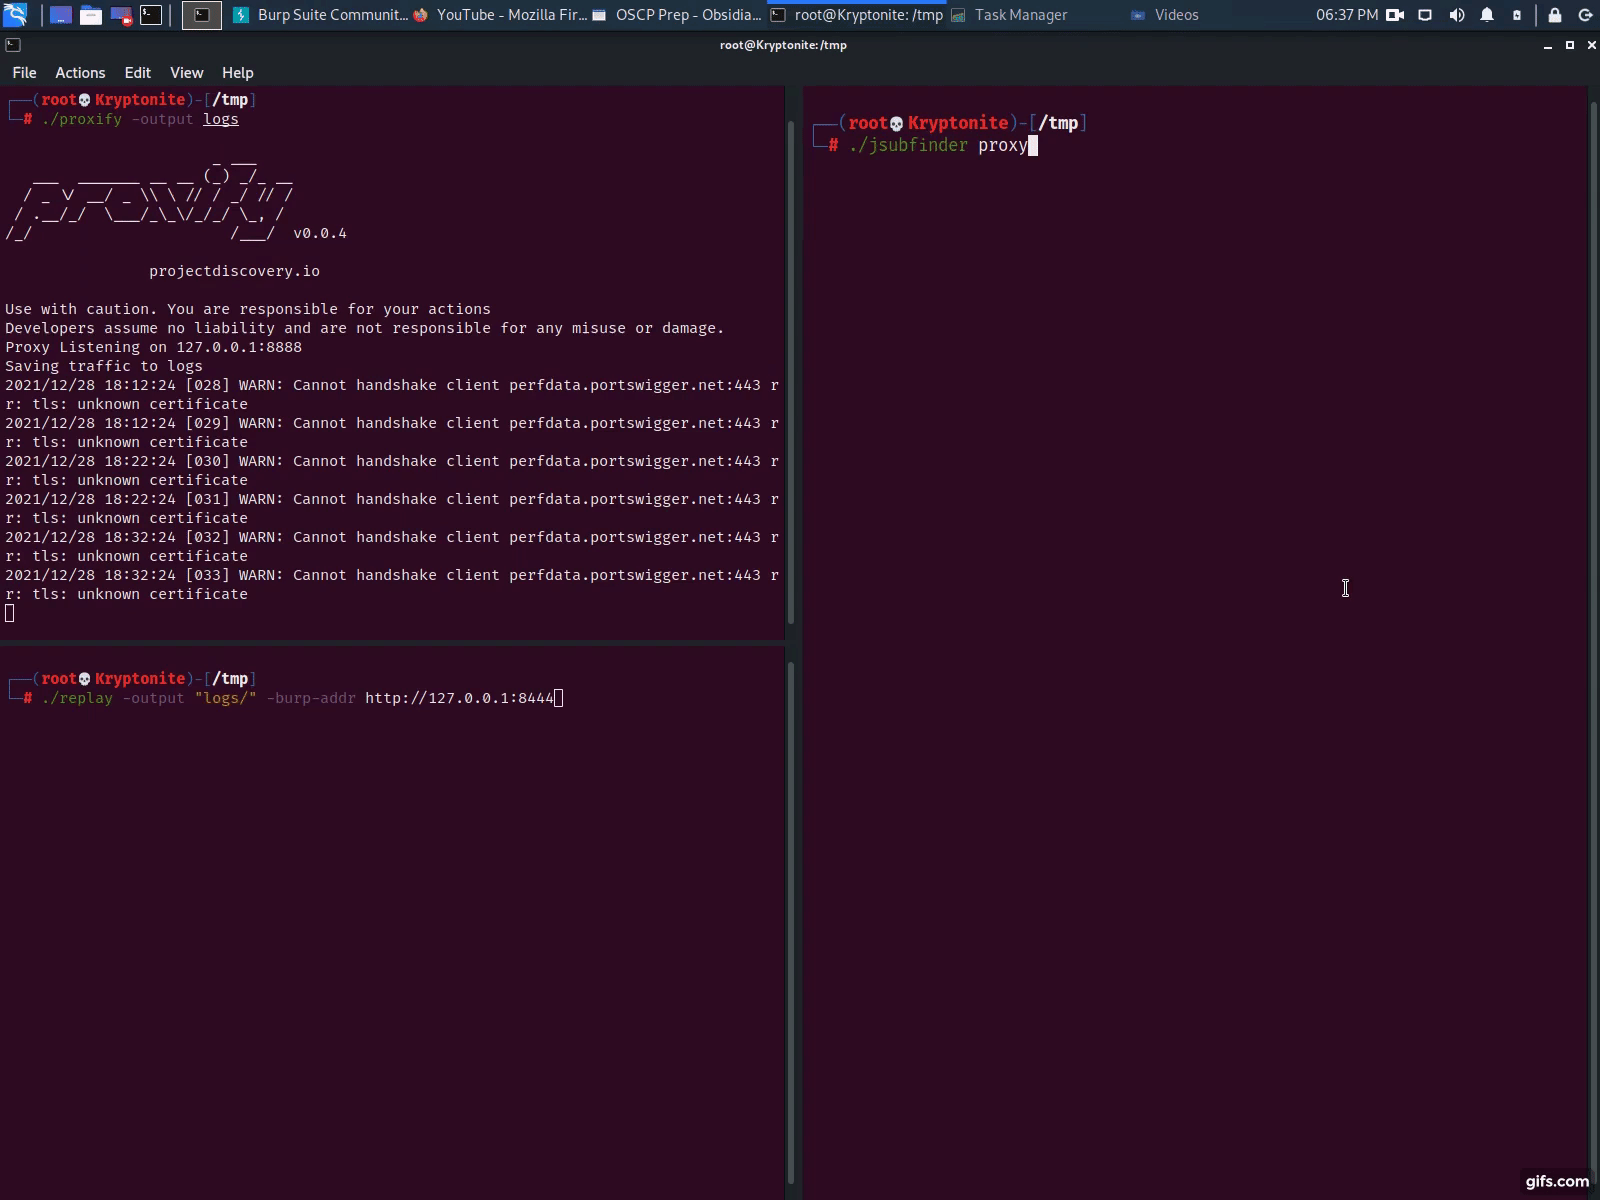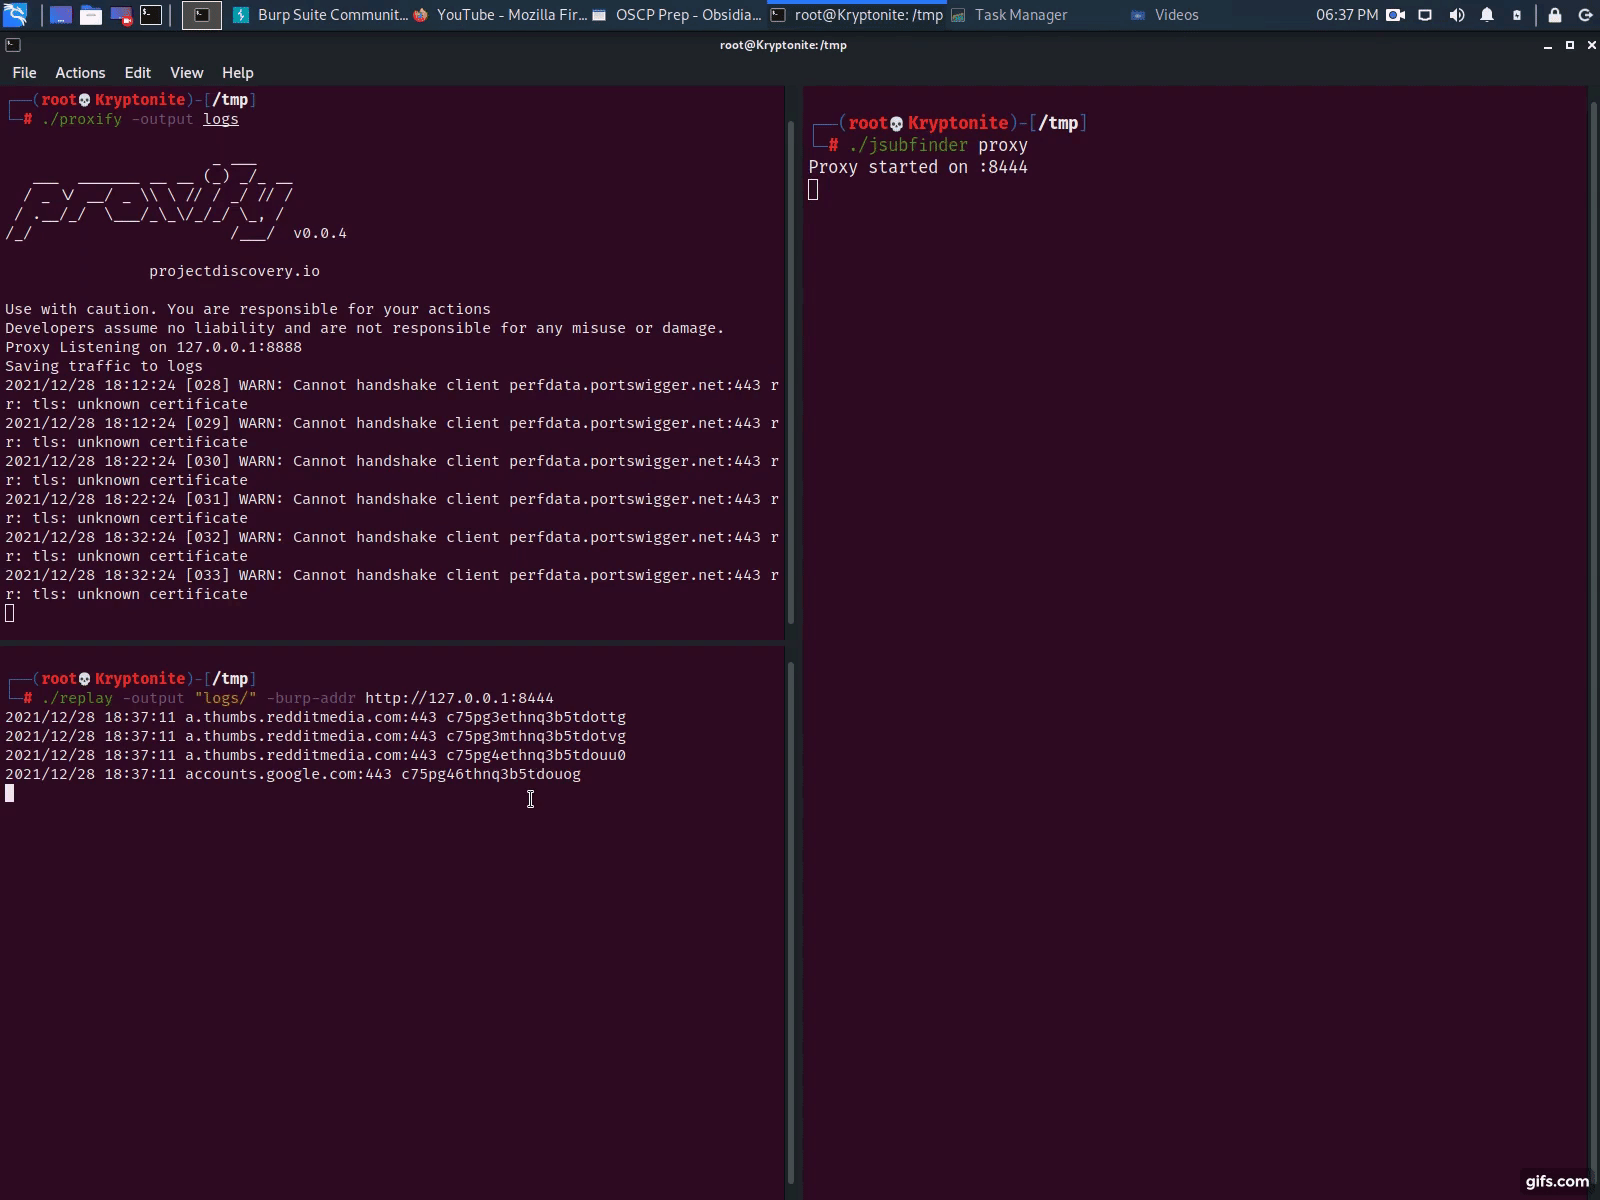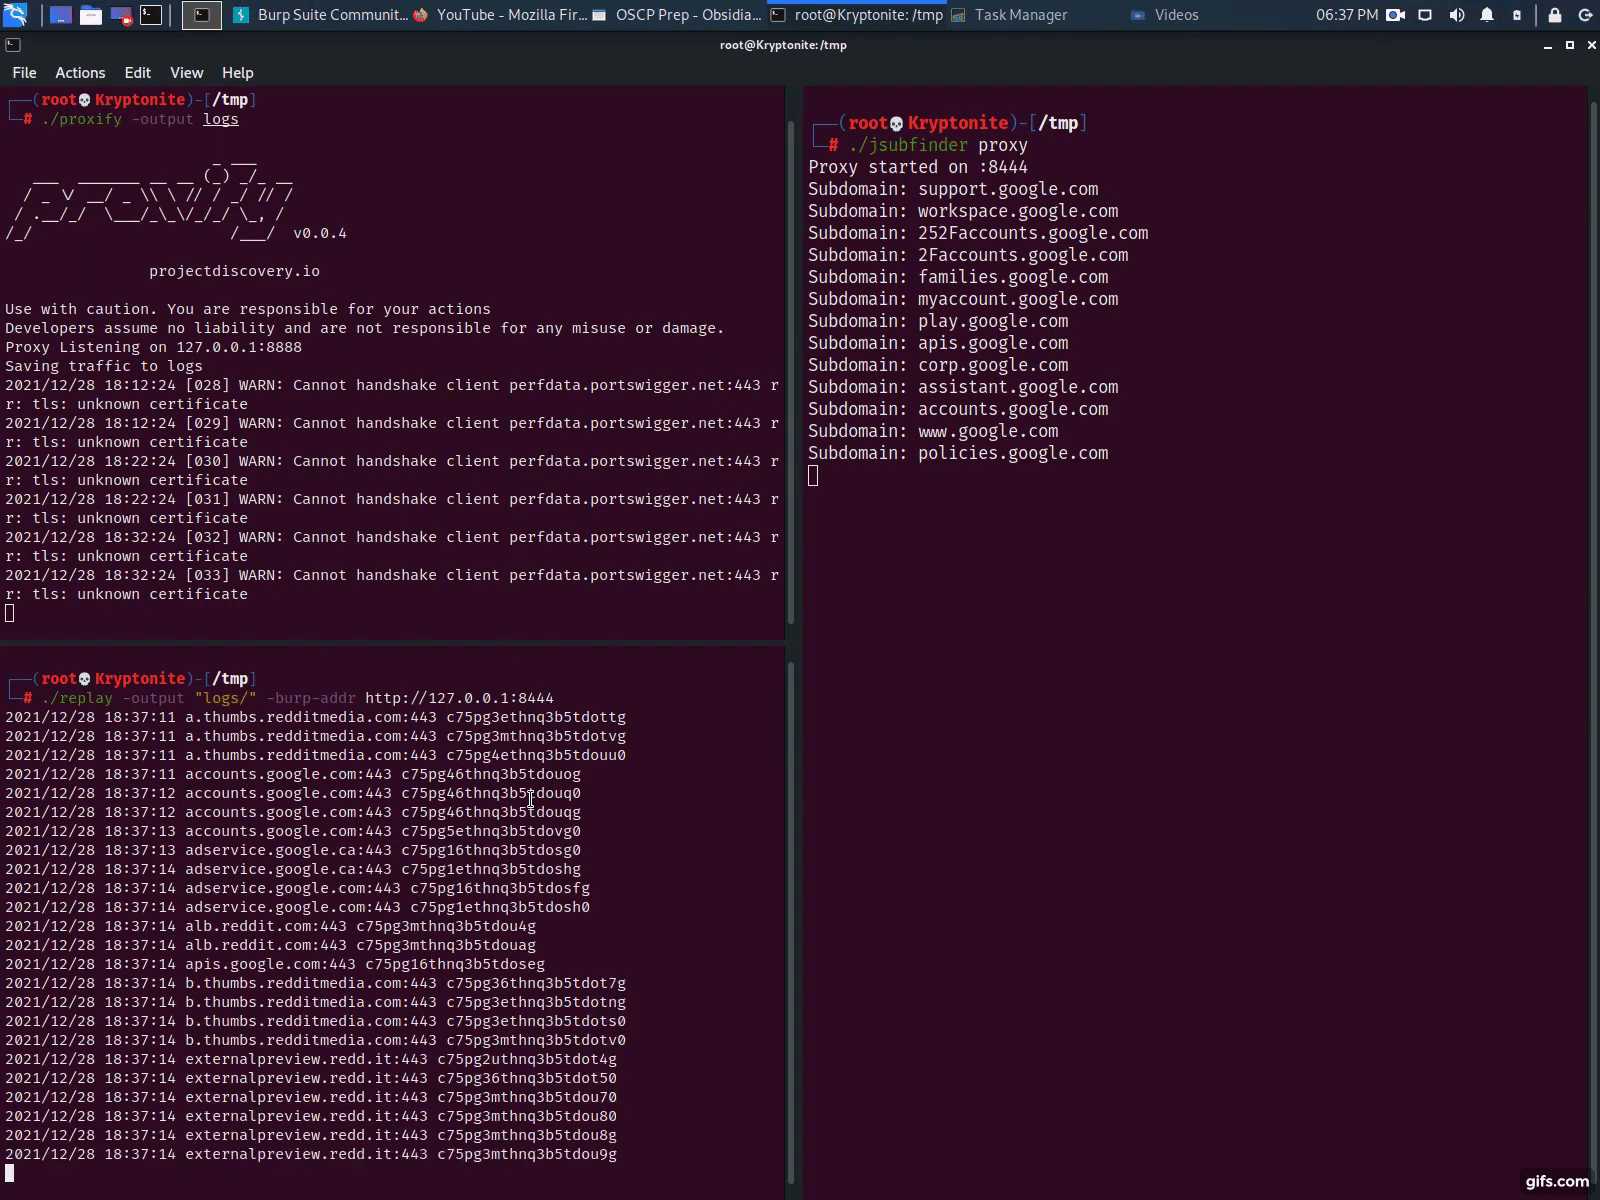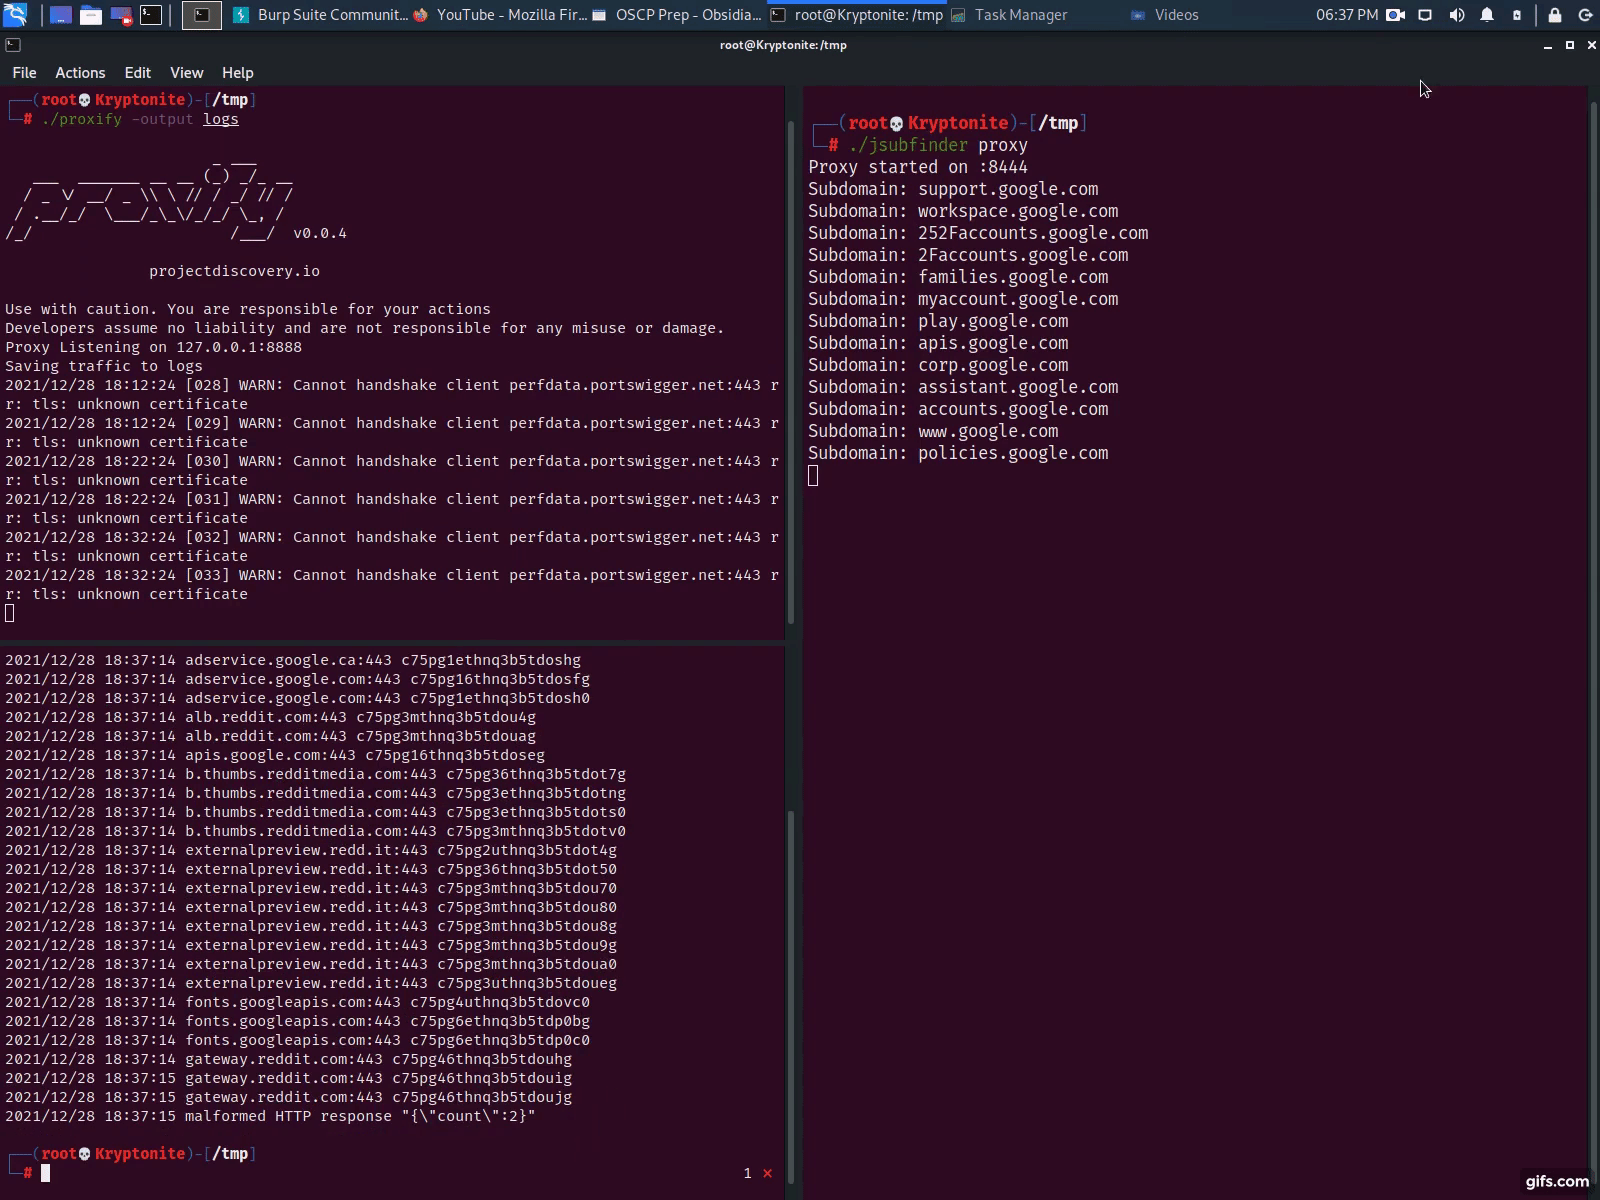 threatunknown/jsubfinder
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
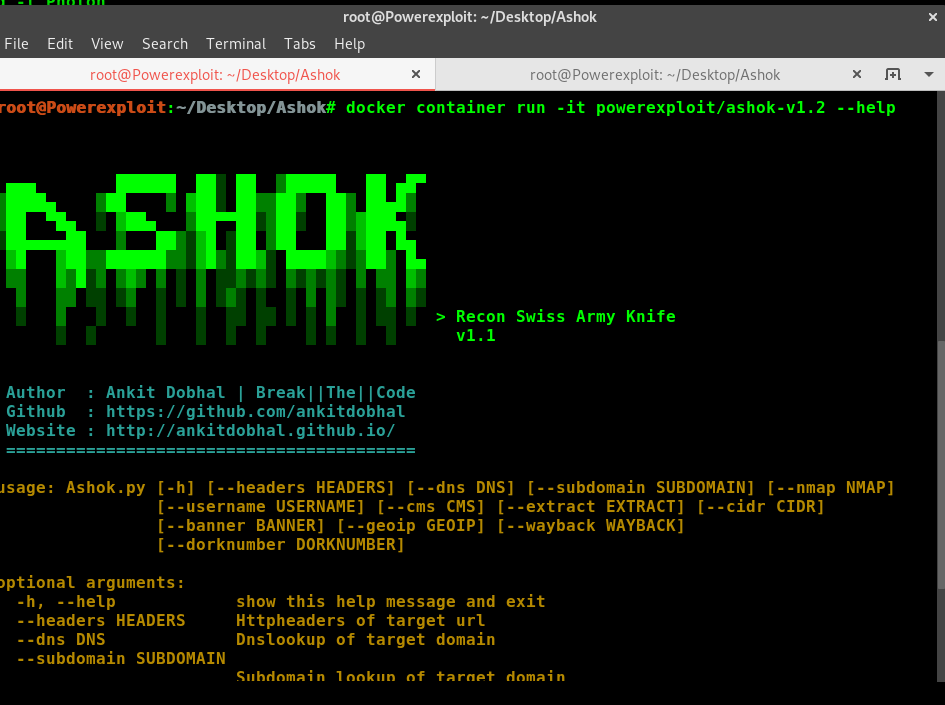 powerexploit/ashok
Ashok is a OSINT Recon Tool , a.k.a 😍 Swiss Army knife .
 mhmdiaa/second-order
Crawls web applications to detect second-order subdomain takeover vulnerabilities by collecting URLs and matching configurable rules for non-200…
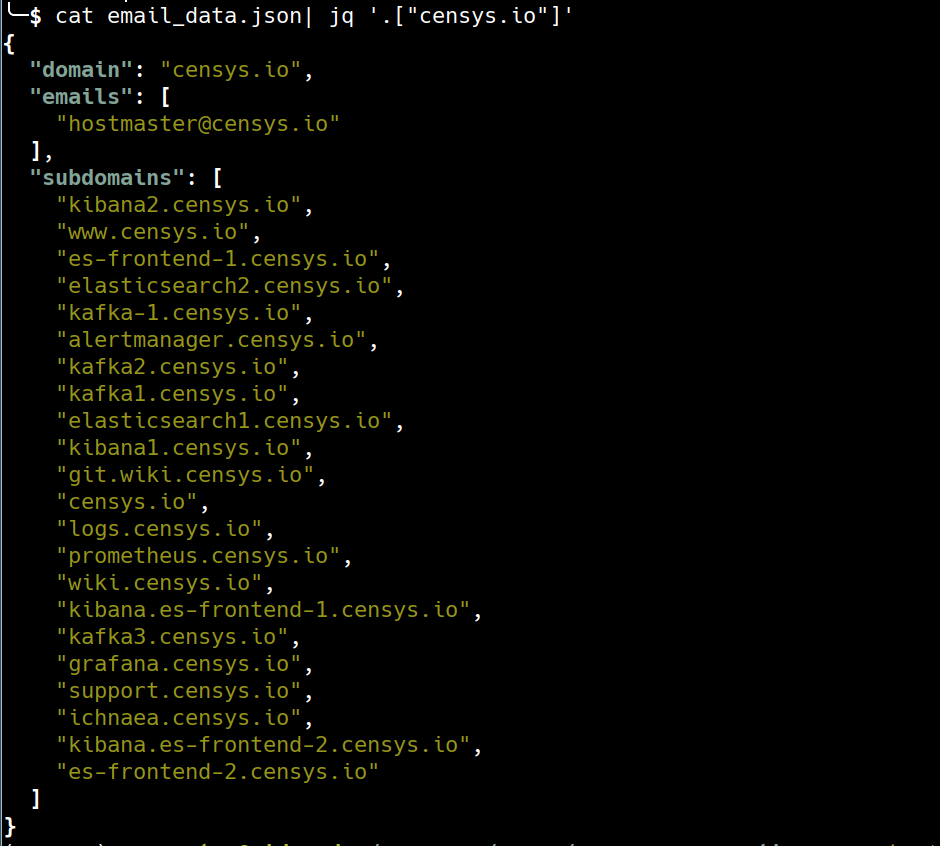 0xbharath/censys-enumeration
A script to extract subdomains/emails for a given domain using SSL/TLS certificate dataset on Censys
 pwnwriter/kanha
🦚 A web-app pentesting suite written in rust .
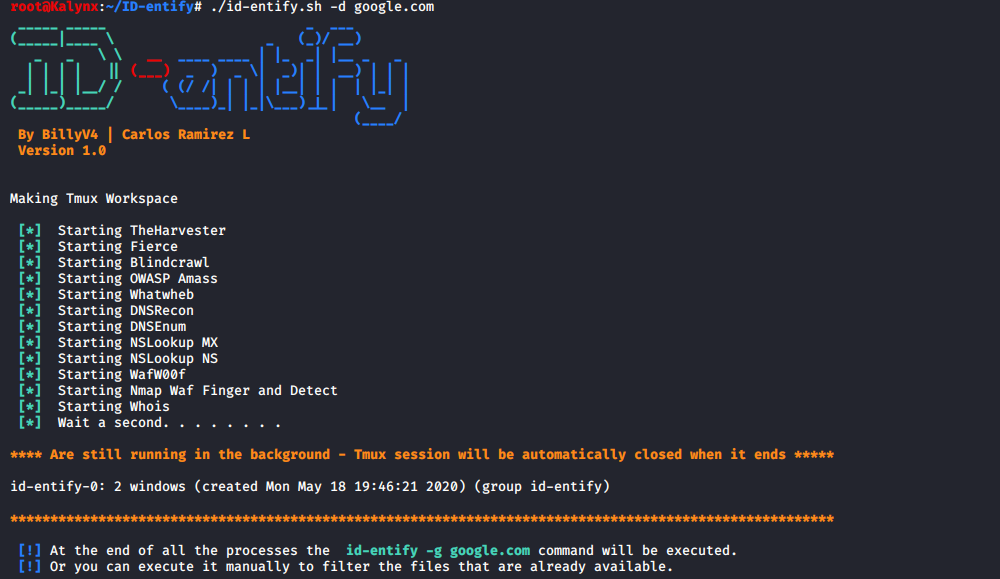 billyv4/id-entify
Search for information related to domain: Emails - IP addresses - Sub-Domains - Information on WEB technology - Type of Firewall - NS and MX records.
 0xbharath/domains-from-csp
A script to extract domain names from Content Security Policy(CSP) headers