
chomp-scan
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
dns-analysisinformation-gatheringpenetration-testing+6
394
solomonsklash/chomp-scanA scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 g0ldencybersec/easyeasm
Zero-dollar attack surface management tool
 caio-ishikawa/netscout
OSINT tool that finds domains, subdomains, directories, endpoints and files for a given seed URL.
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 smiegles/mass3
Multi-threaded DNS-based enumeration tool for discovering AWS S3 buckets using pre-compiled wordlists and custom DNS resolvers, with optional Docker…
 offxec/pavelow
PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…
 pry0cc/subgen
A really simple utility to concate wordlists to a domain name - to pipe into your favourite resolver!
 josekutty-k/frontpage-server-extensions-vulnerability-scanner
Python script to scan for CVE-2000-0114 vulnerability in Frontpage Server Extensions. Automates subdomain enumeration and vulnerability scanning…
 typeerror/domained
Multi Tool Subdomain Enumeration
 d3mondev/puredns
High-speed DNS resolver and subdomain bruteforcer with accurate wildcard filtering and DNS poisoning validation for precise reconnaissance.
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 s0md3v/subgpt
Find subdomains with GPT, for free
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 k8gege/ladon
Ladon大型内网渗透扫描器,PowerShell、Cobalt Strike插件、内存加载、无文件扫描。含端口扫描、服务识别、网络资产探测、密码审计、高危漏洞检测、漏洞利用、密码读取以及一键GetShell,支持批量A段/B段/C段以及跨网段扫描,支持URL、主机、域名列表扫描等。网络资产探测32…
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
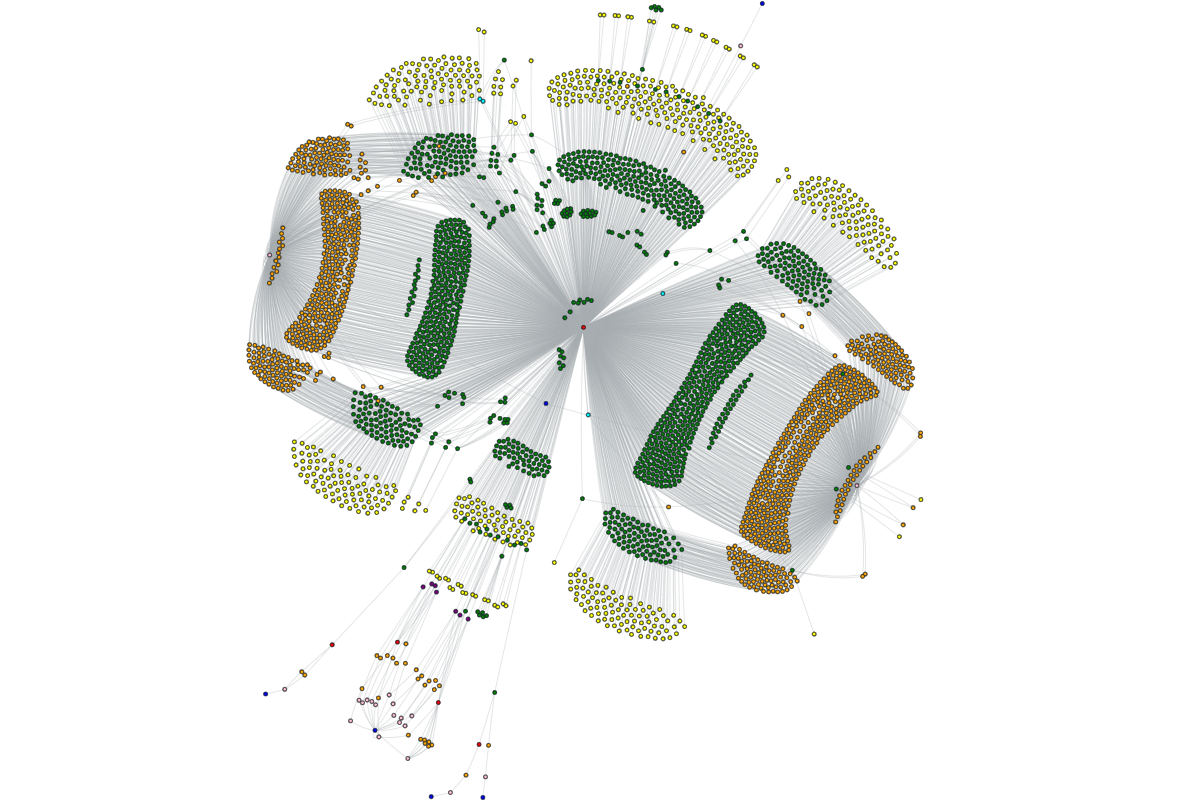 owasp-amass/amass
In-depth attack surface mapping and asset discovery
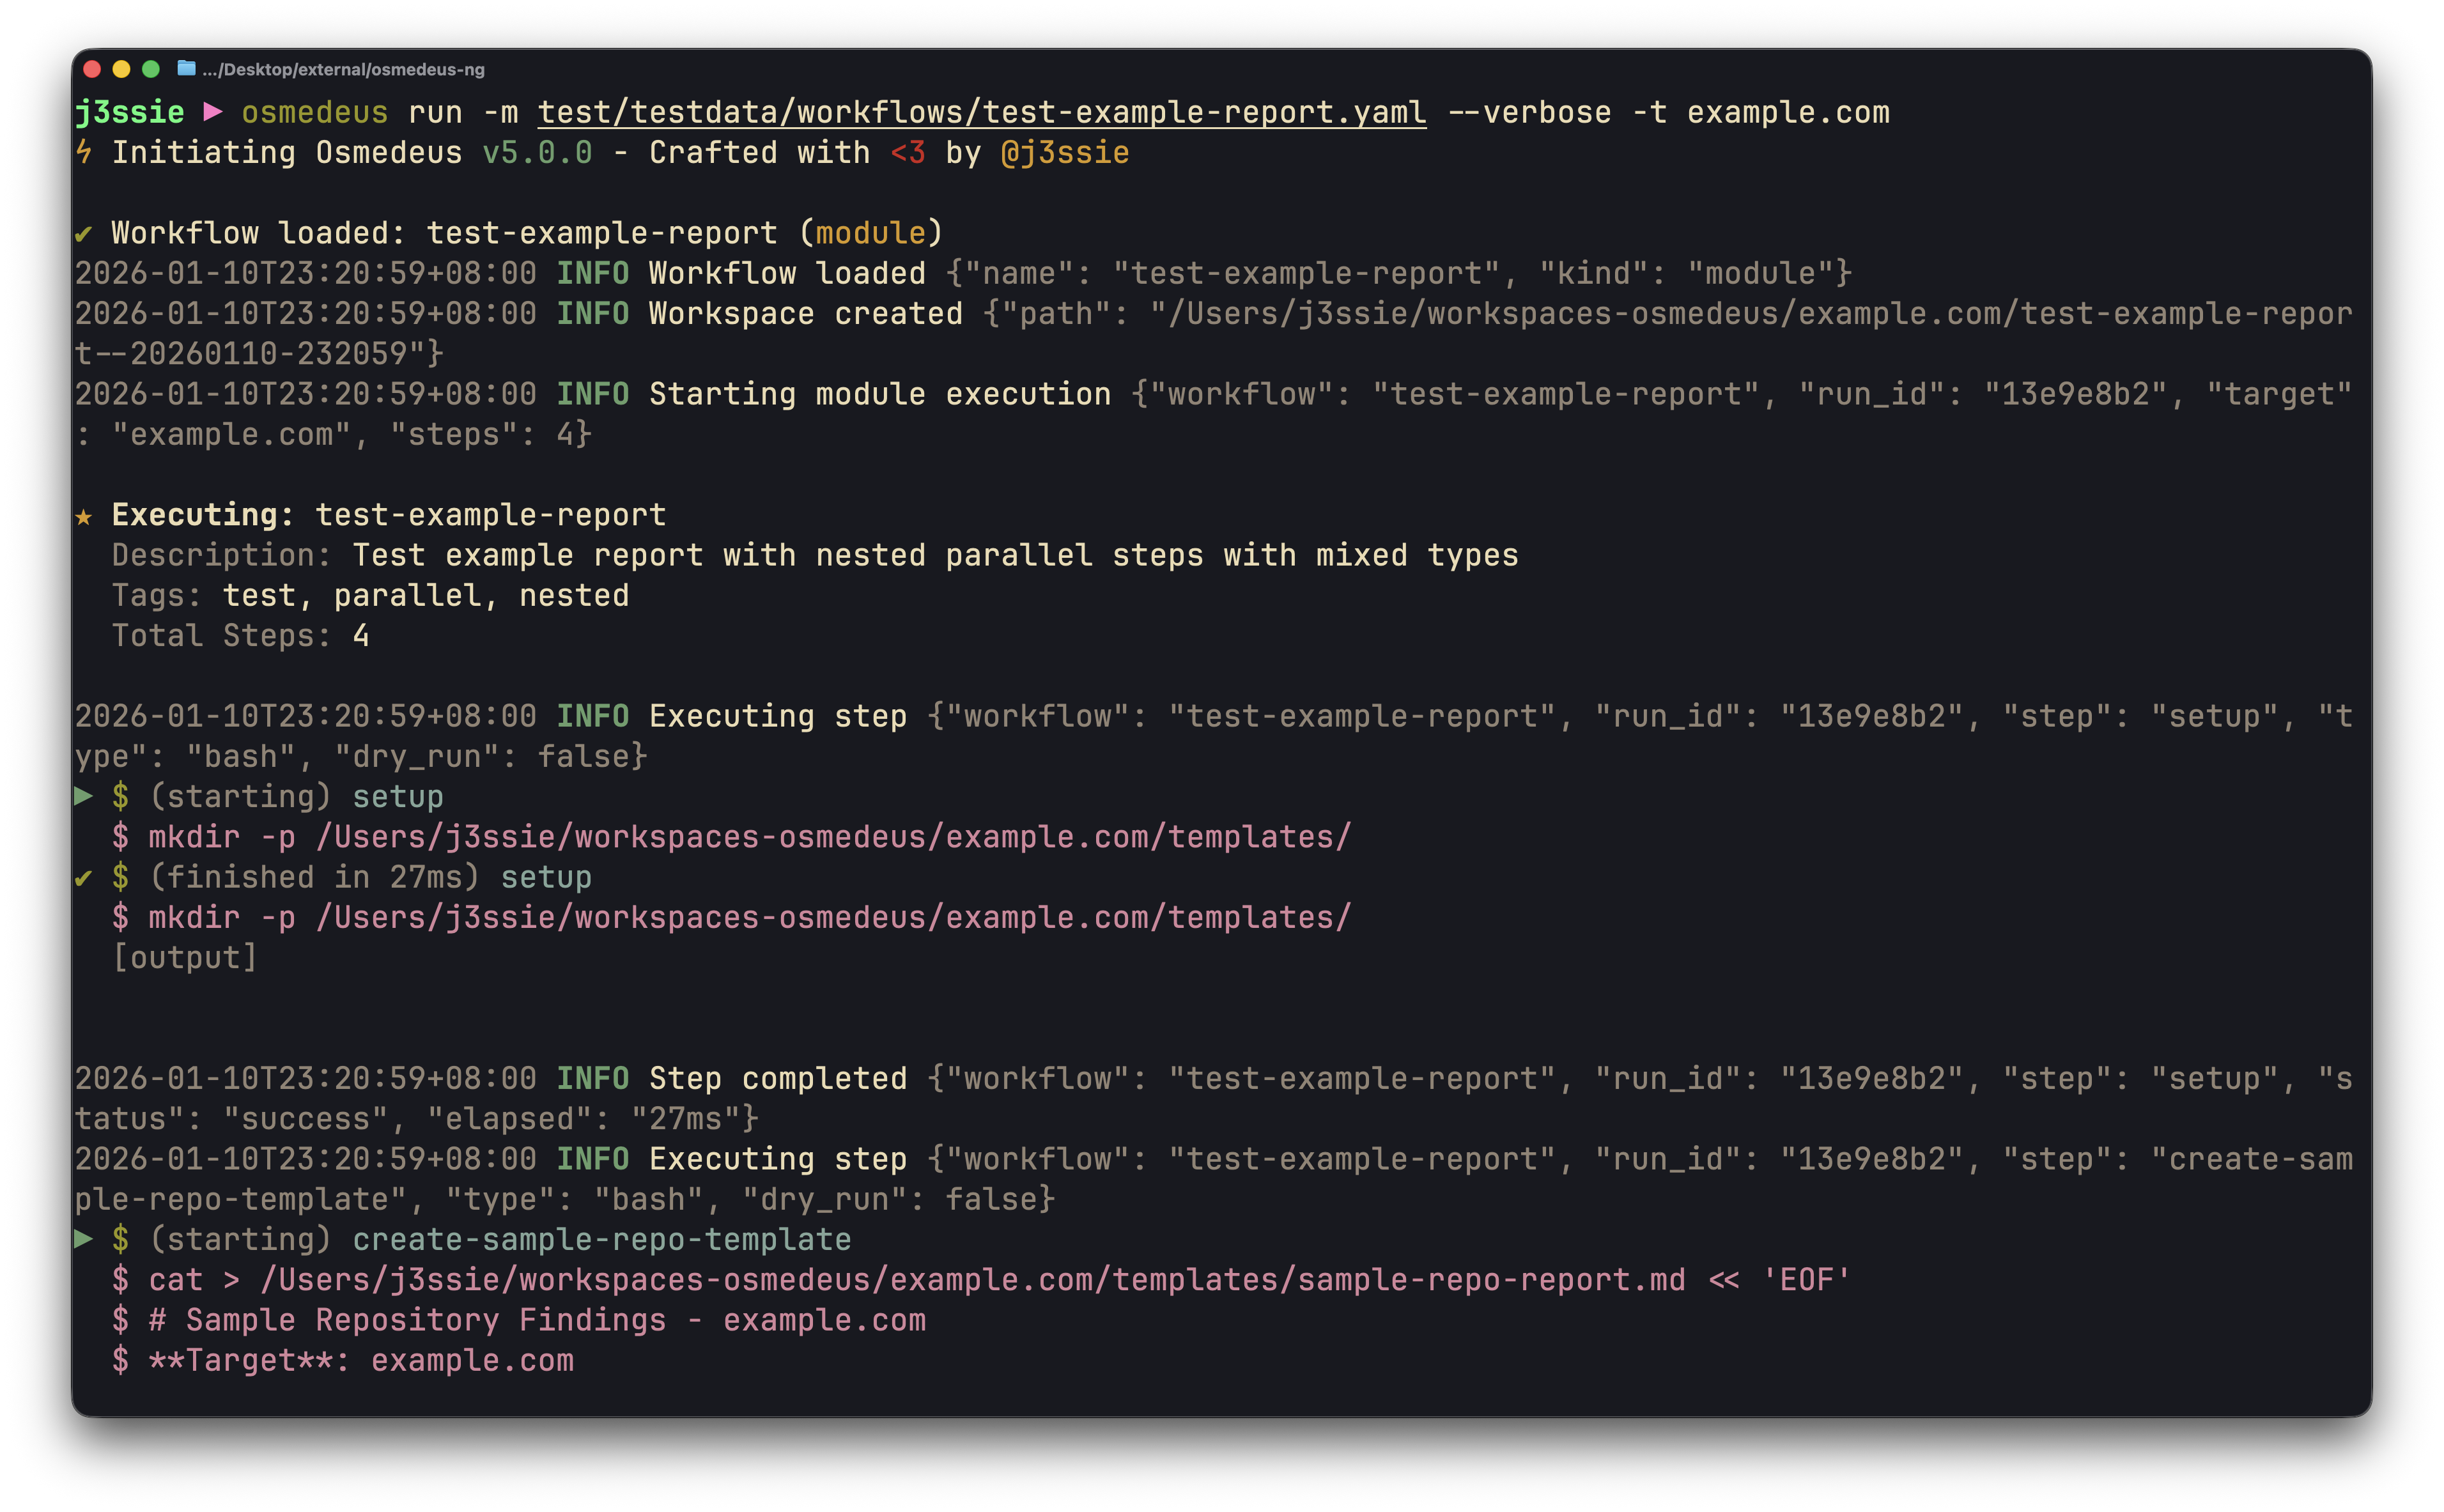 j3ssie/osmedeus
A Modern Orchestration Engine for Security