osint_stuff_tool_collection

Curated collection of 1000+ online OSINT tools and services for geolocation, social media, domain/IP, email, image and archive investigations.

Curated collection of 1000+ online OSINT tools and services for geolocation, social media, domain/IP, email, image and archive investigations.

Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…

Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…

reconFTW is a tool designed to perform automated recon on a target domain by running the best set of tools to perform scanning and finding out…

A collection of awesome one-liner scripts especially for bug bounty tips.

A collection of scripts for assessing Microsoft Azure security

Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…

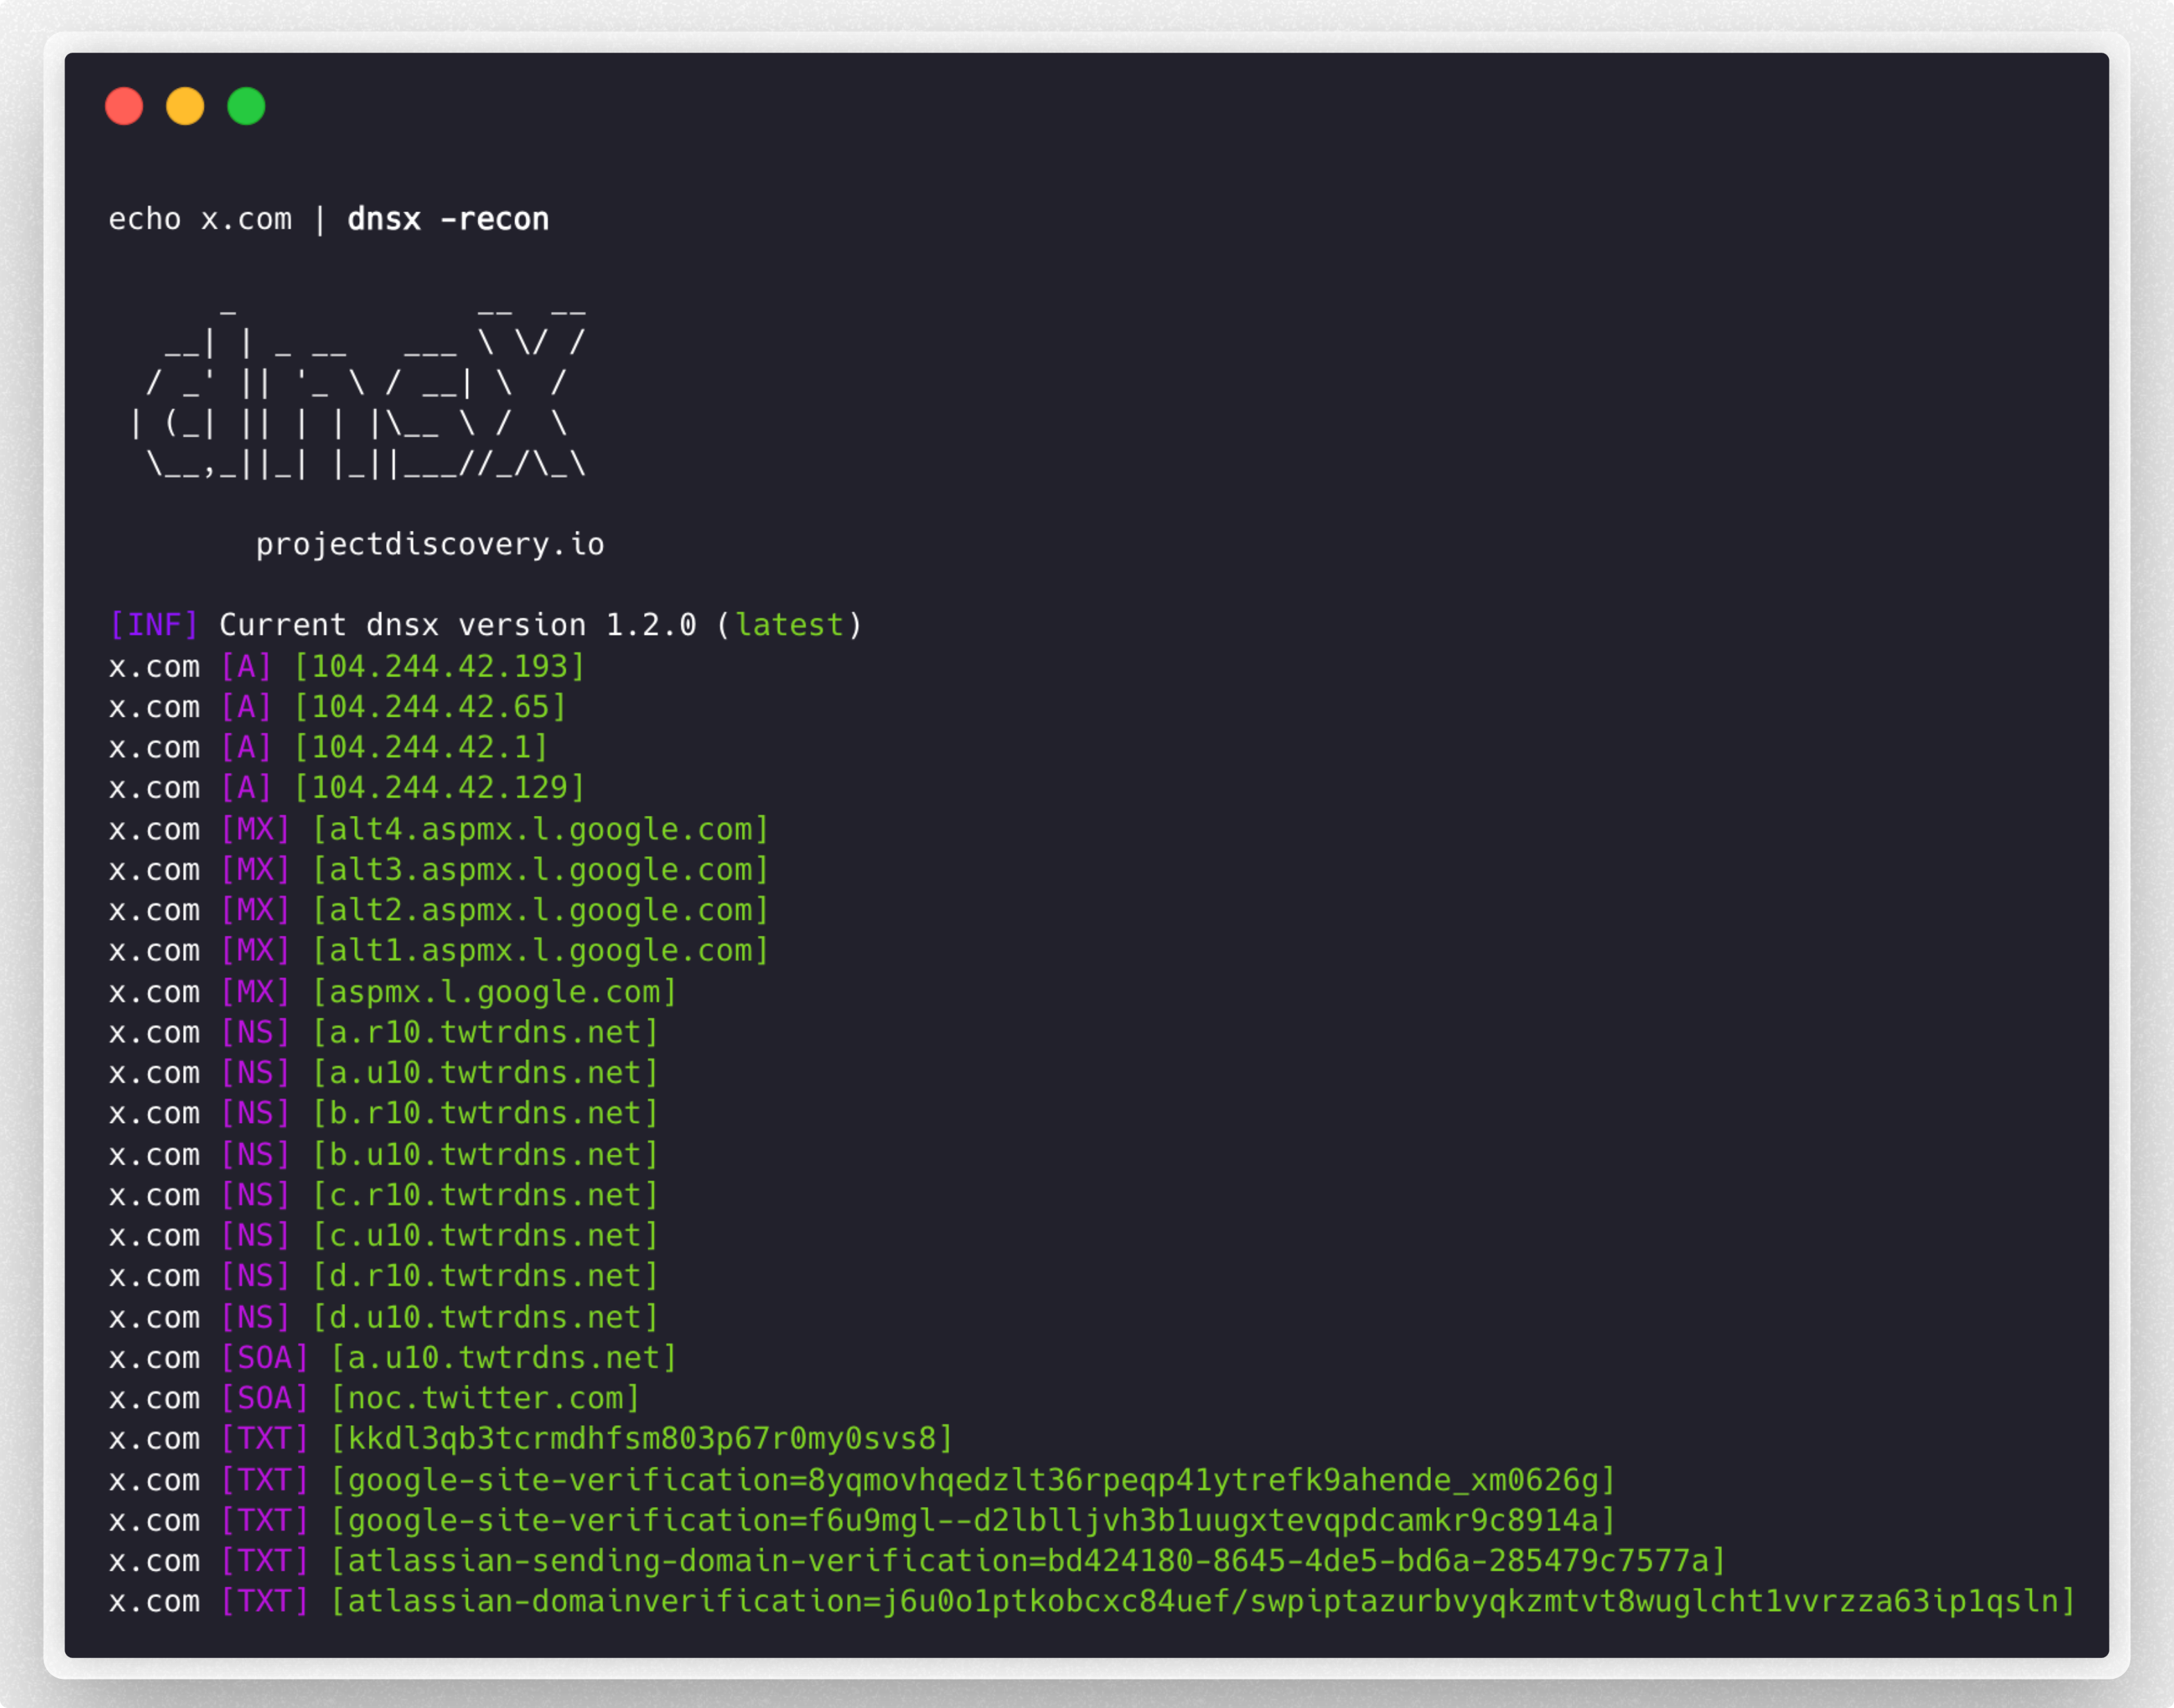
dnsx is a fast and multi-purpose DNS toolkit allow to run multiple DNS queries of your choice with a list of user-supplied resolvers.

Generates permutations, alterations and mutations of subdomains and then resolves them

Curated list of OSINT tools for offensive security, covering email harvesting, subdomain enumeration, threat intelligence, and social engineering for…

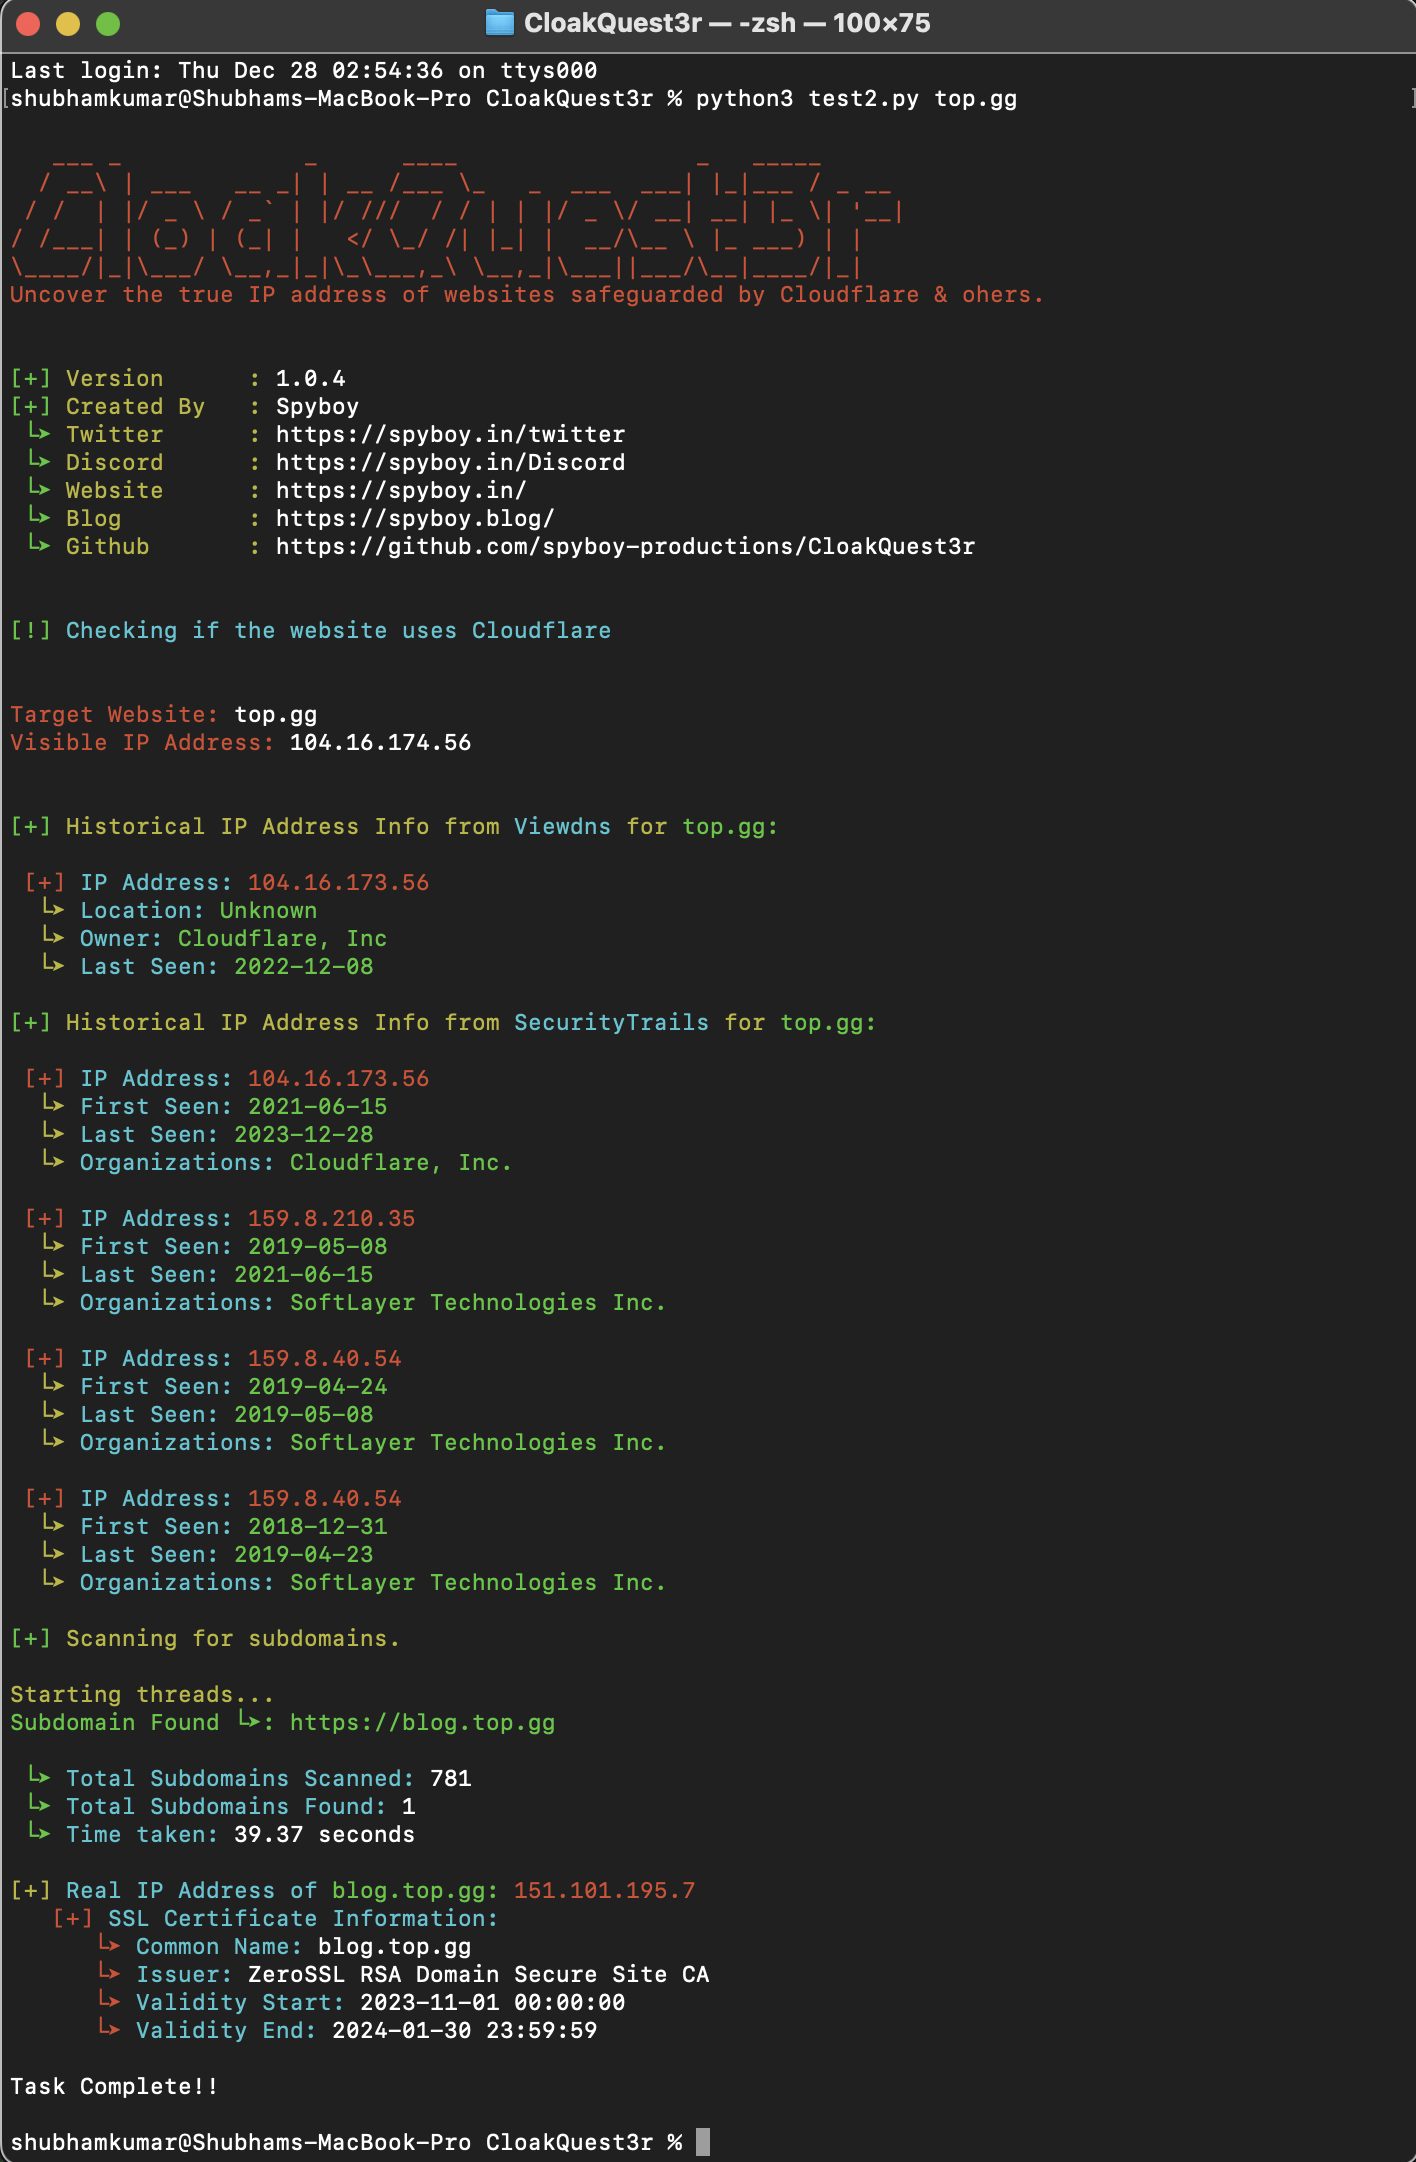
Open-source security research tool for identifying origin IP exposure of websites protected by Cloudflare and similar reverse proxy services.

Take a list of domains and probe for working HTTP and HTTPS servers

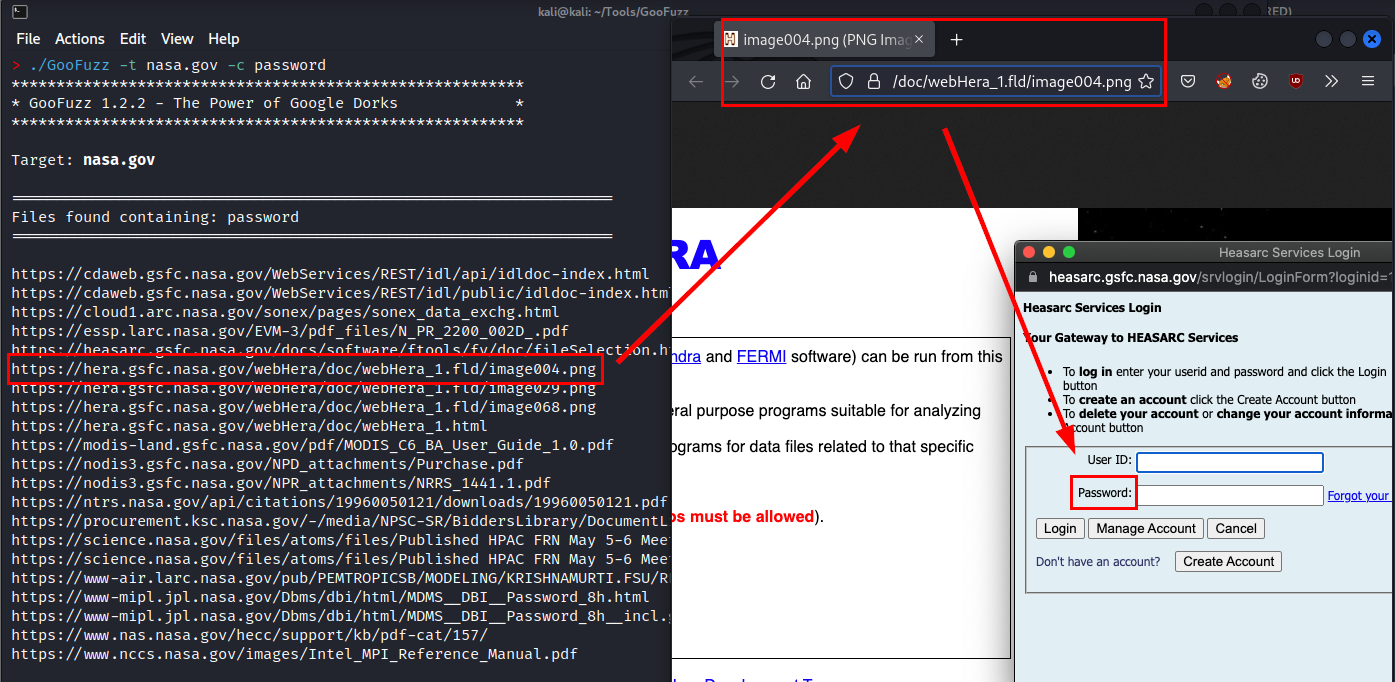
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…

Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…

Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…

Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.

Rock-On is a all in one Recon tool that will just get a single entry of the Domain name and do all of the work alone.

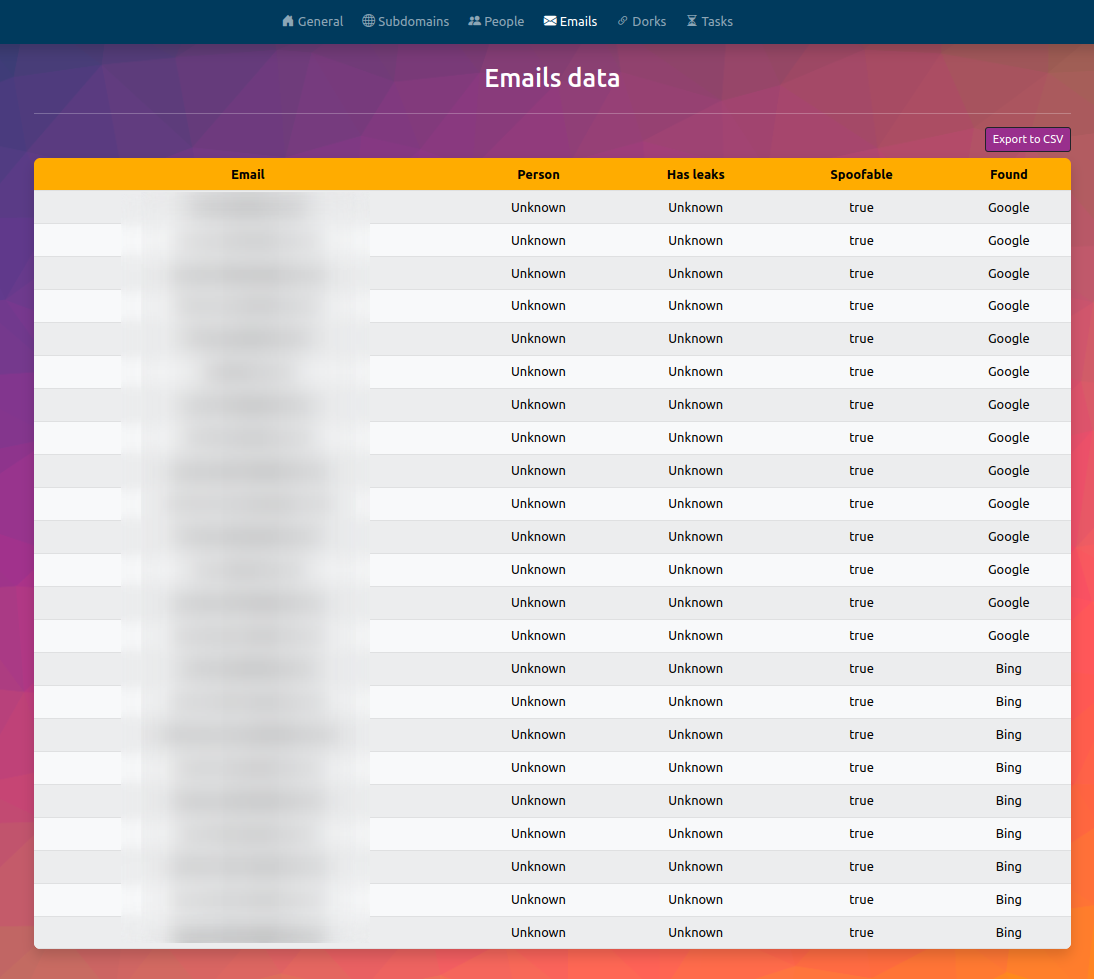
InfoHound is an OSINT to extract a large amount of data given a web domain name.