

wordlists
 trickest/wordlists
Real-world infosec wordlists, updated regularly
curated-resourcesinformation-gatheringpenetration-testing+3
trickest/wordlistsReal-world infosec wordlists, updated regularly
 shuvonsec/claude-bug-bounty
AI-powered bug bounty hunting toolkit that works with or without subscription.
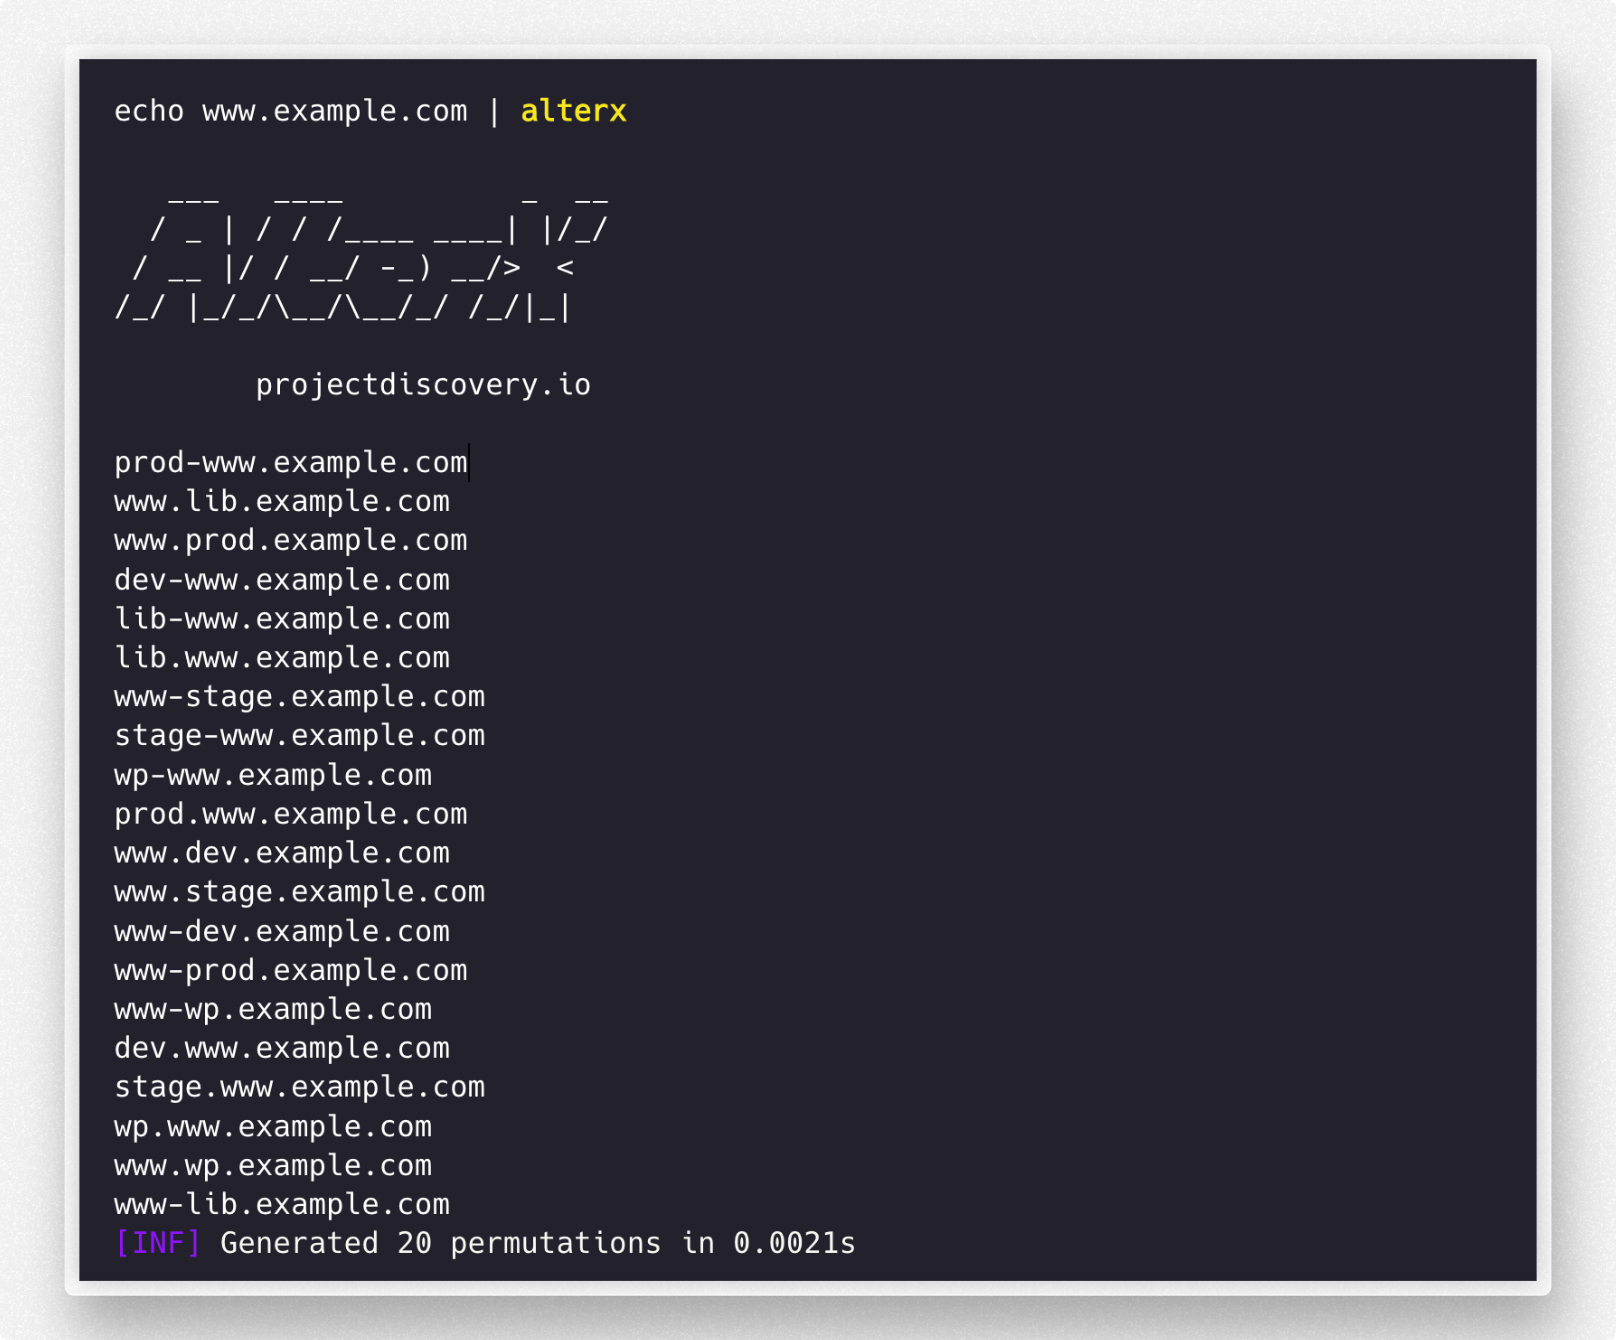 projectdiscovery/alterx
Fast and customizable subdomain wordlist generator using DSL
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
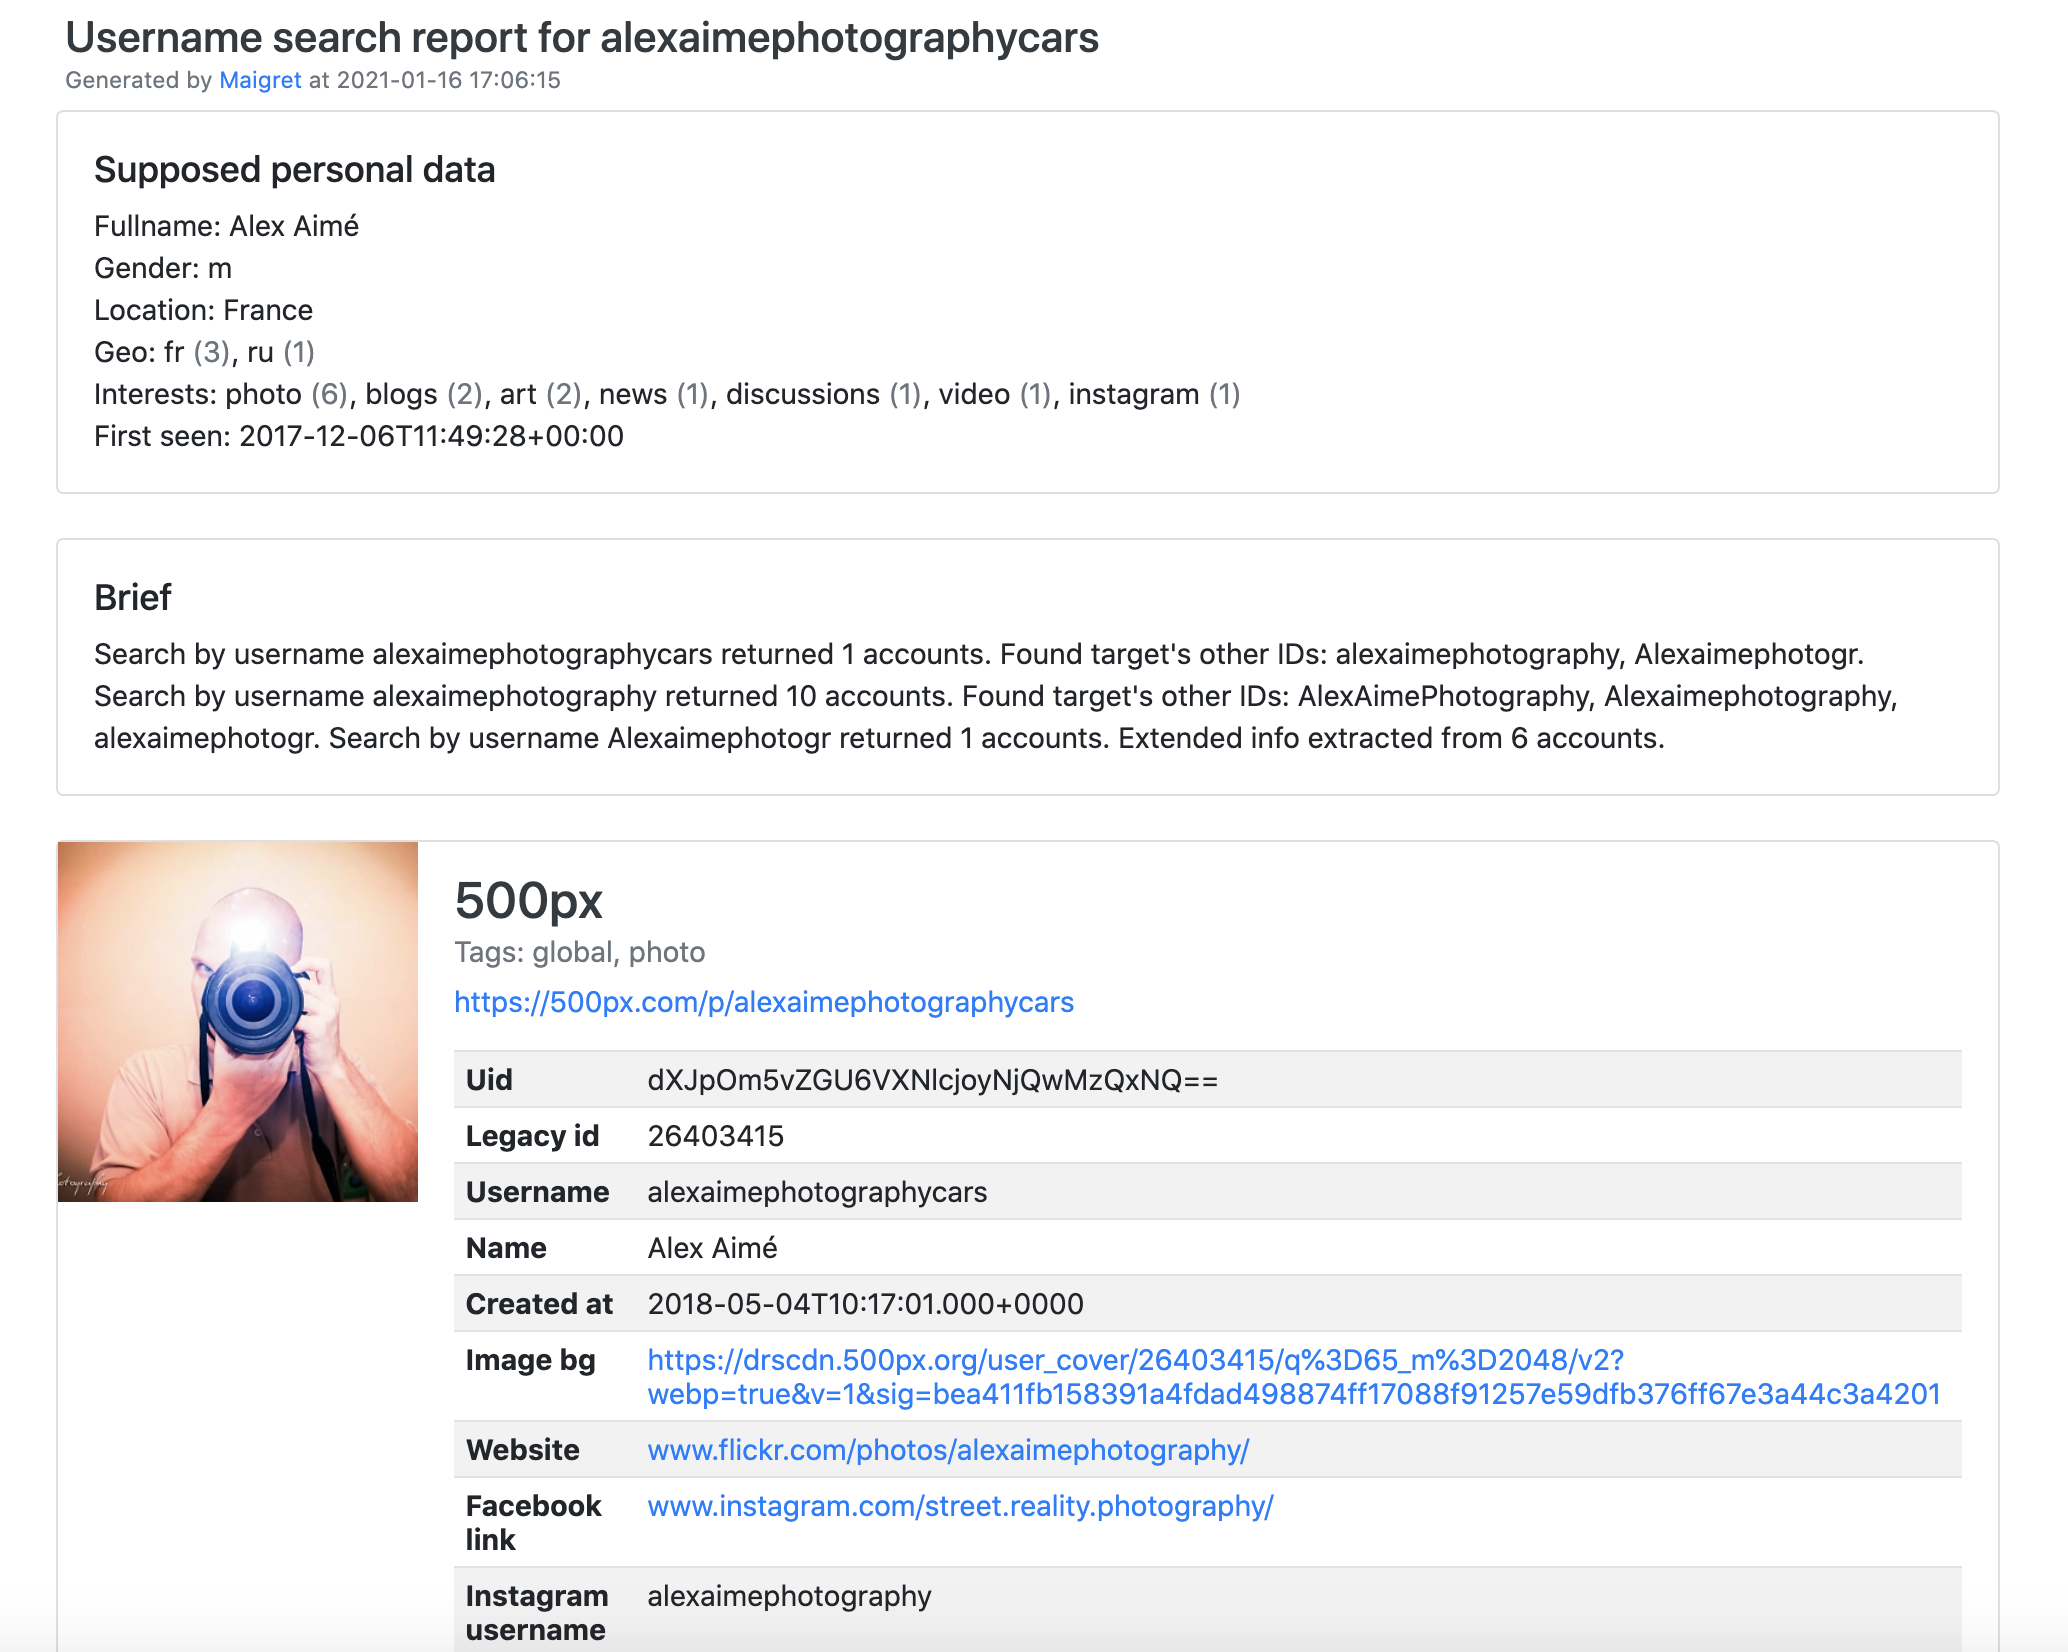 soxoj/maigret
🕵️♂️ Collect a dossier on a person by username from 6K websites
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
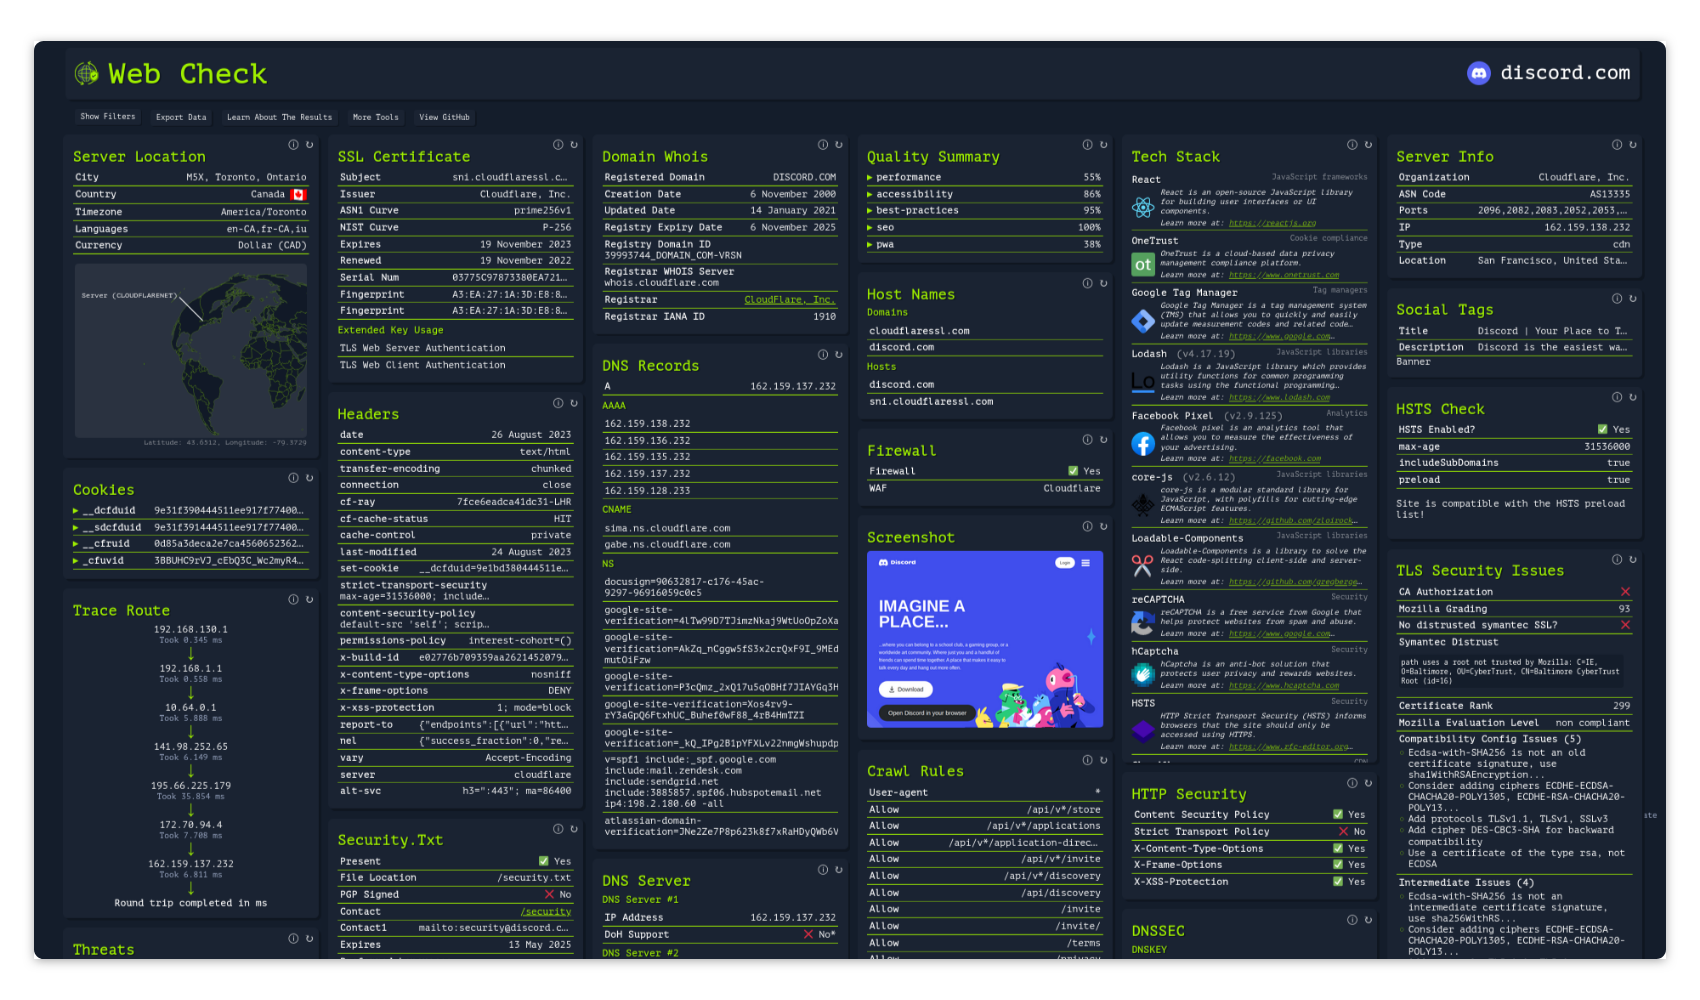 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
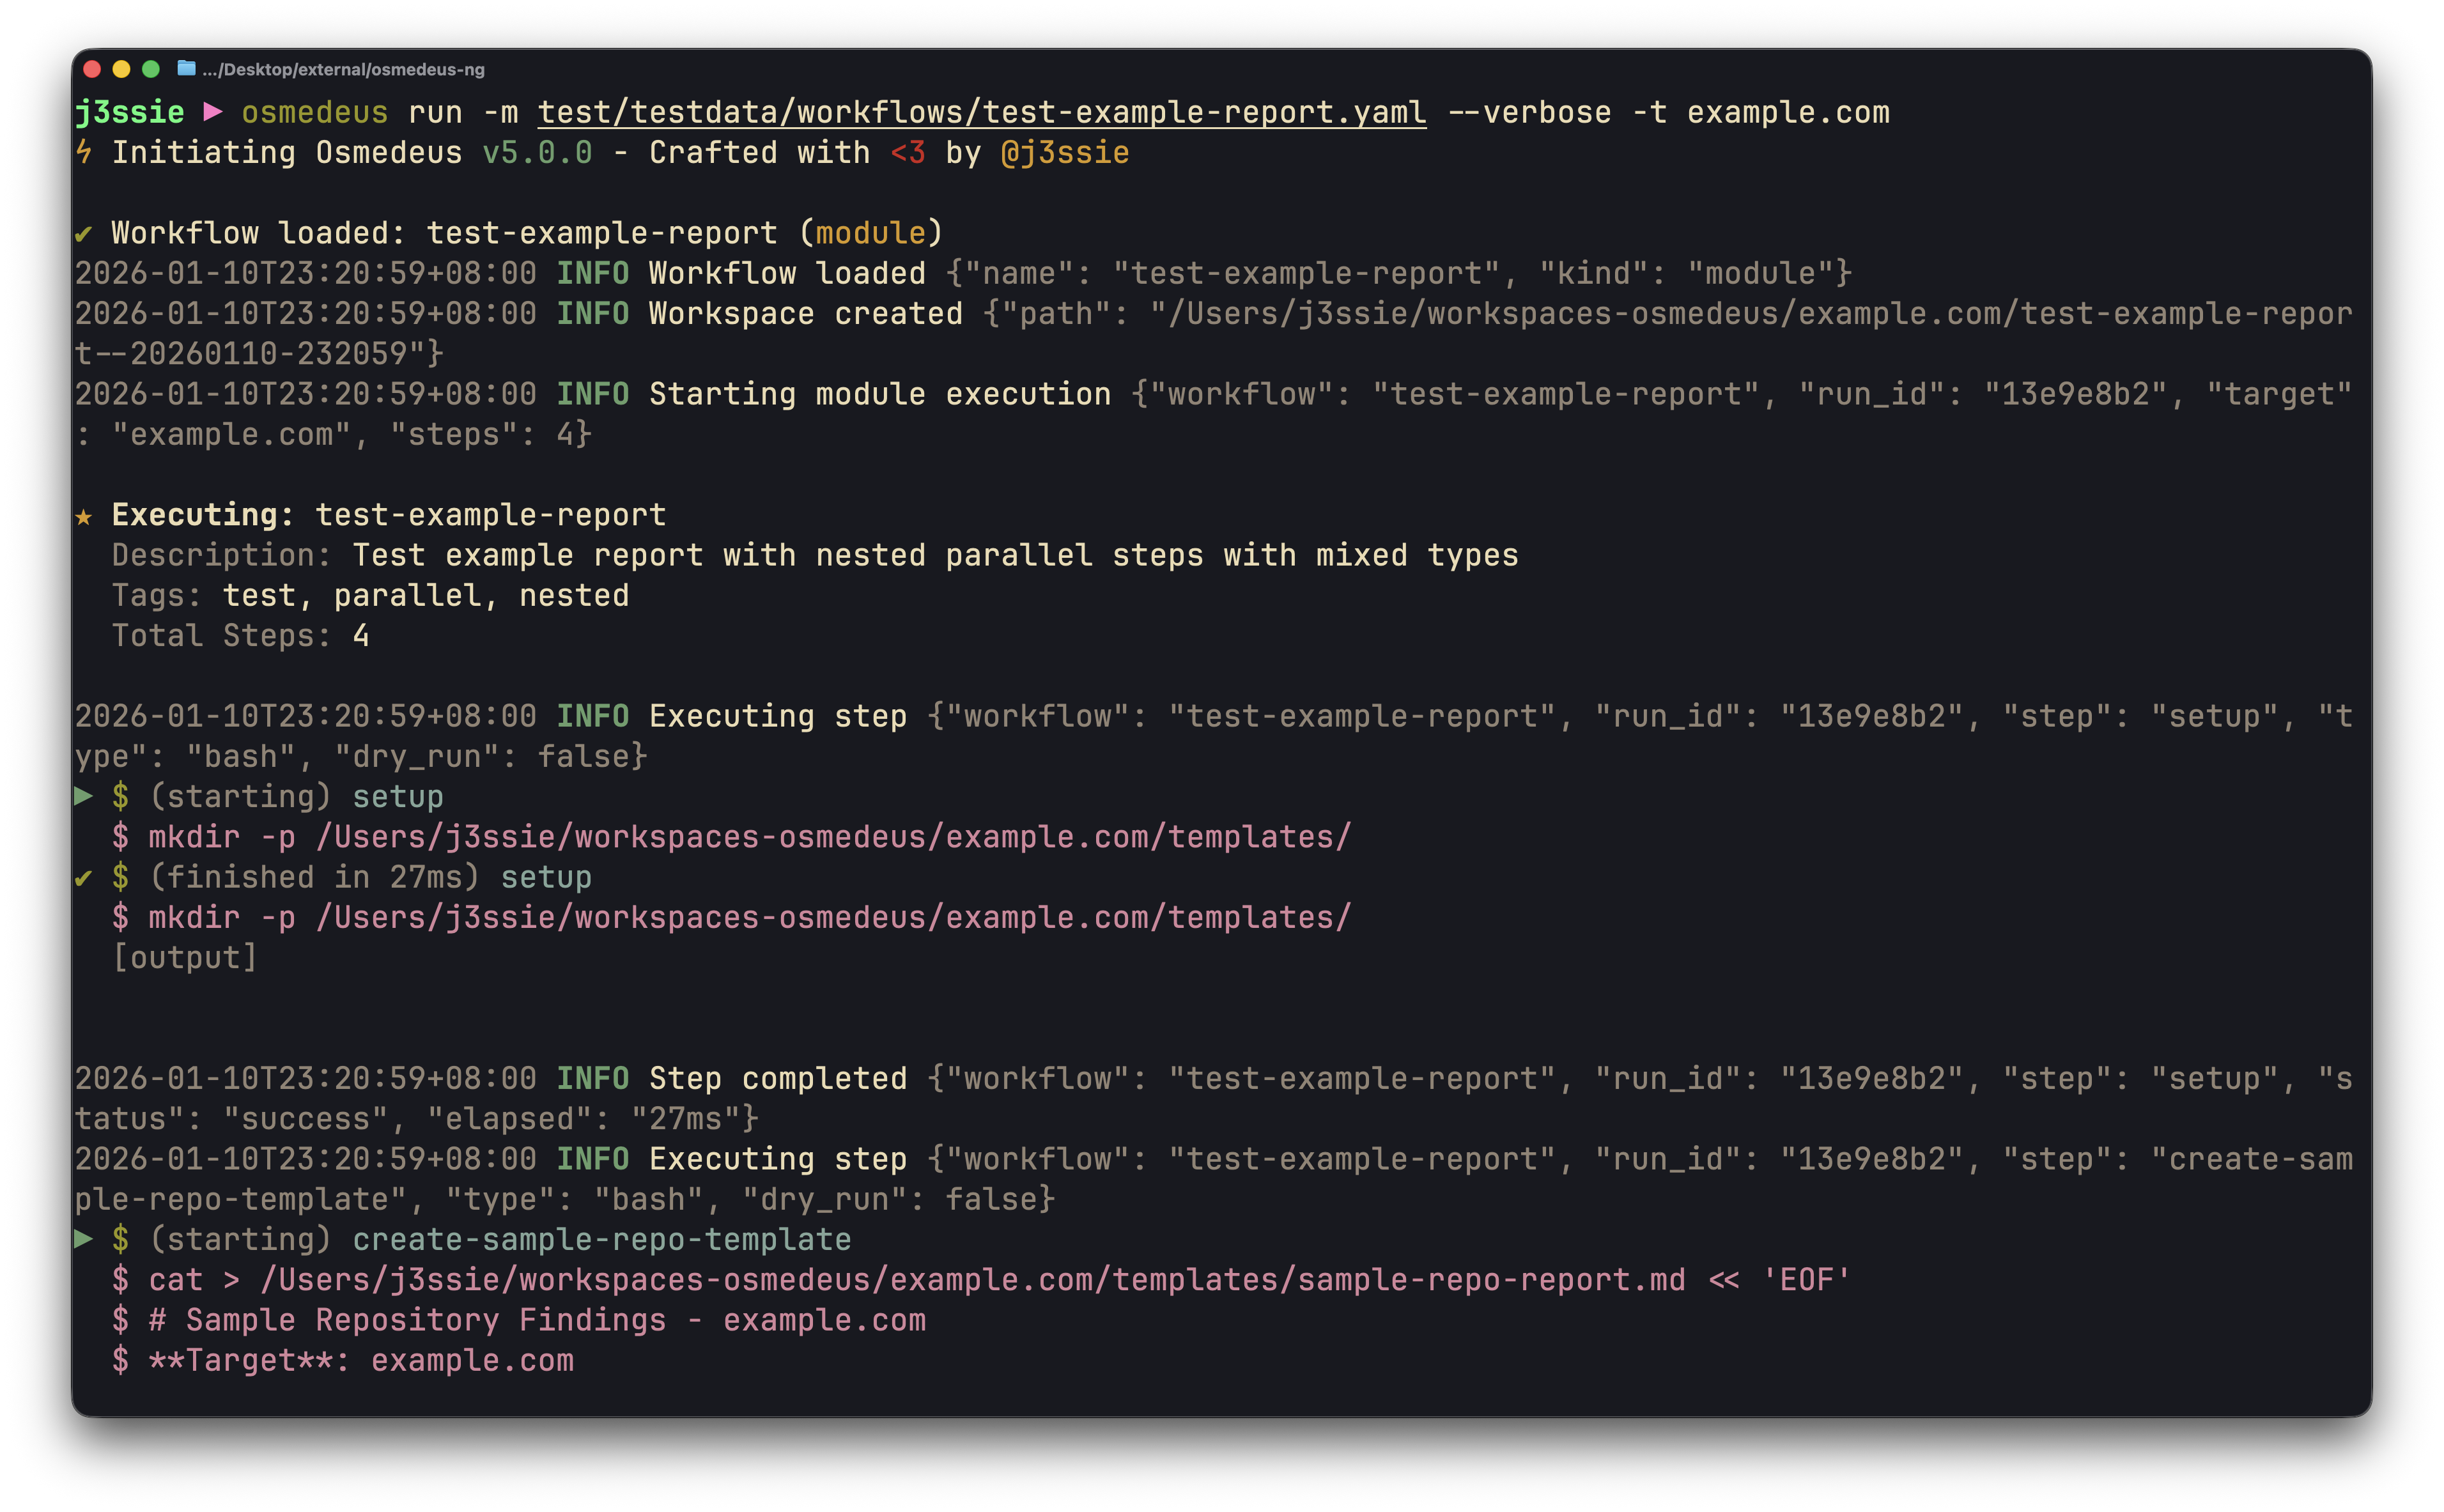 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection

 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).