
Simple Pentesting
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
educationinformation-gatheringnetwork-mapping+7
sakispat/simple-pentestingAn educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 hakluke/hakrevdns
Small, fast tool for performing reverse DNS lookups en masse.
 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
 sec-dan/cve-2025-53770-scanner
A Python-based reconnaissance scanner for safely identifying potential exposure to SharePoint vulnerability CVE-2025-53770.
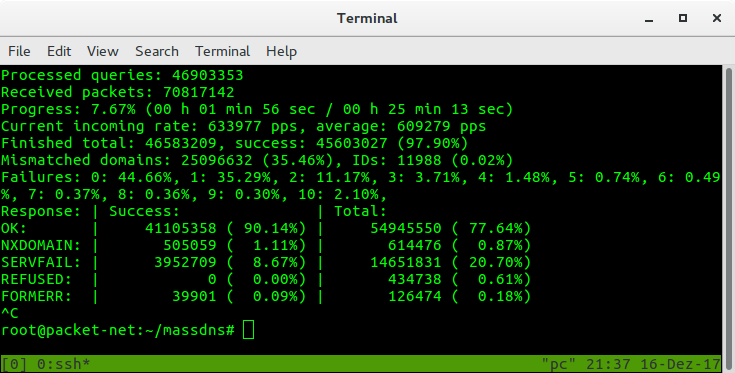 blechschmidt/massdns
A high-performance DNS stub resolver for bulk lookups and reconnaissance (subdomain enumeration)
 pry0cc/subgen
A really simple utility to concate wordlists to a domain name - to pipe into your favourite resolver!
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 cyberblackhole/domain-to-webapp
Bash script that enumerates subdomains via Subfinder, resolves IPs, and identifies live web applications hosted on a domain for reconnaissance and…
 hueristiq/xsubfind3r
Passive subdomain discovery tool that aggregates results from multiple online sources via CLI, supporting stdin/stdout, JSONL output, and API key…
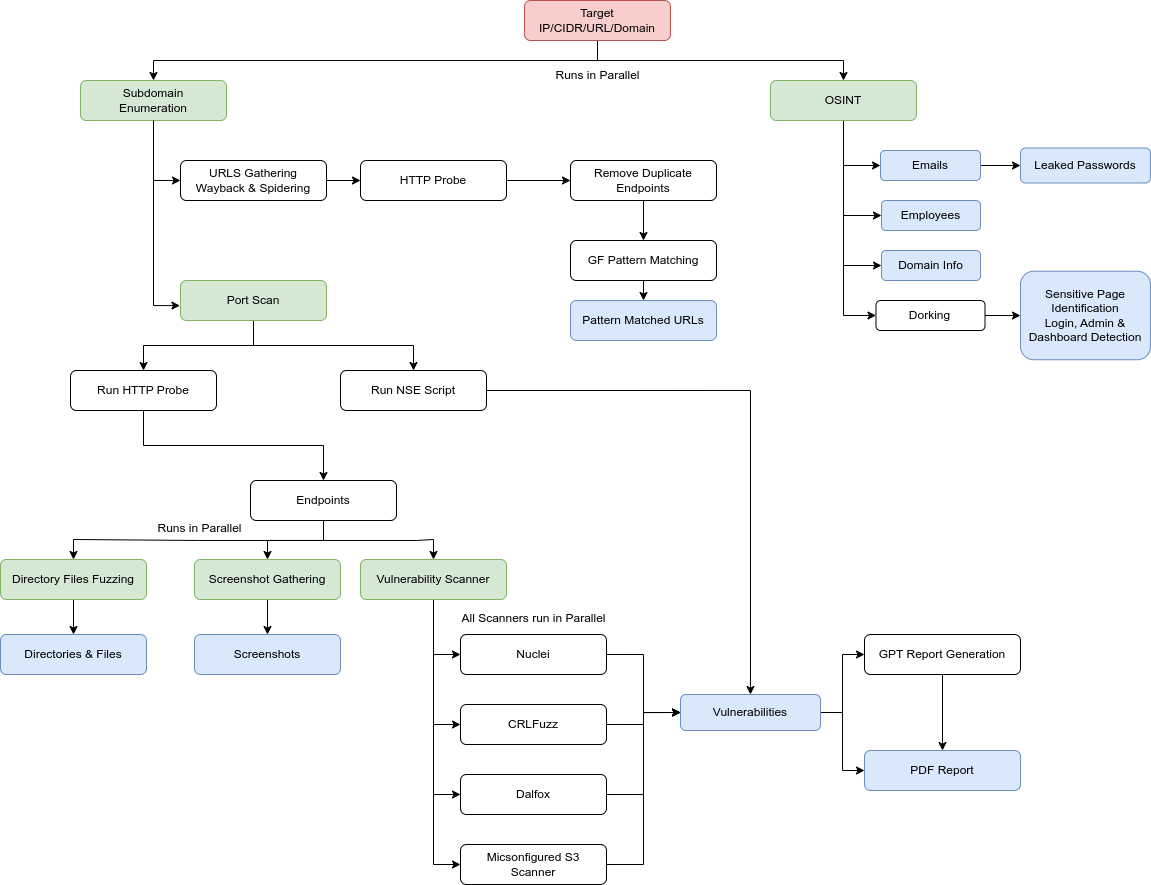 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 laramies/theharvester
E-mails, subdomains and names Harvester - OSINT