
Archived
vmp2
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
binary-analysiscode-analysisdynamic-code-analysis+3
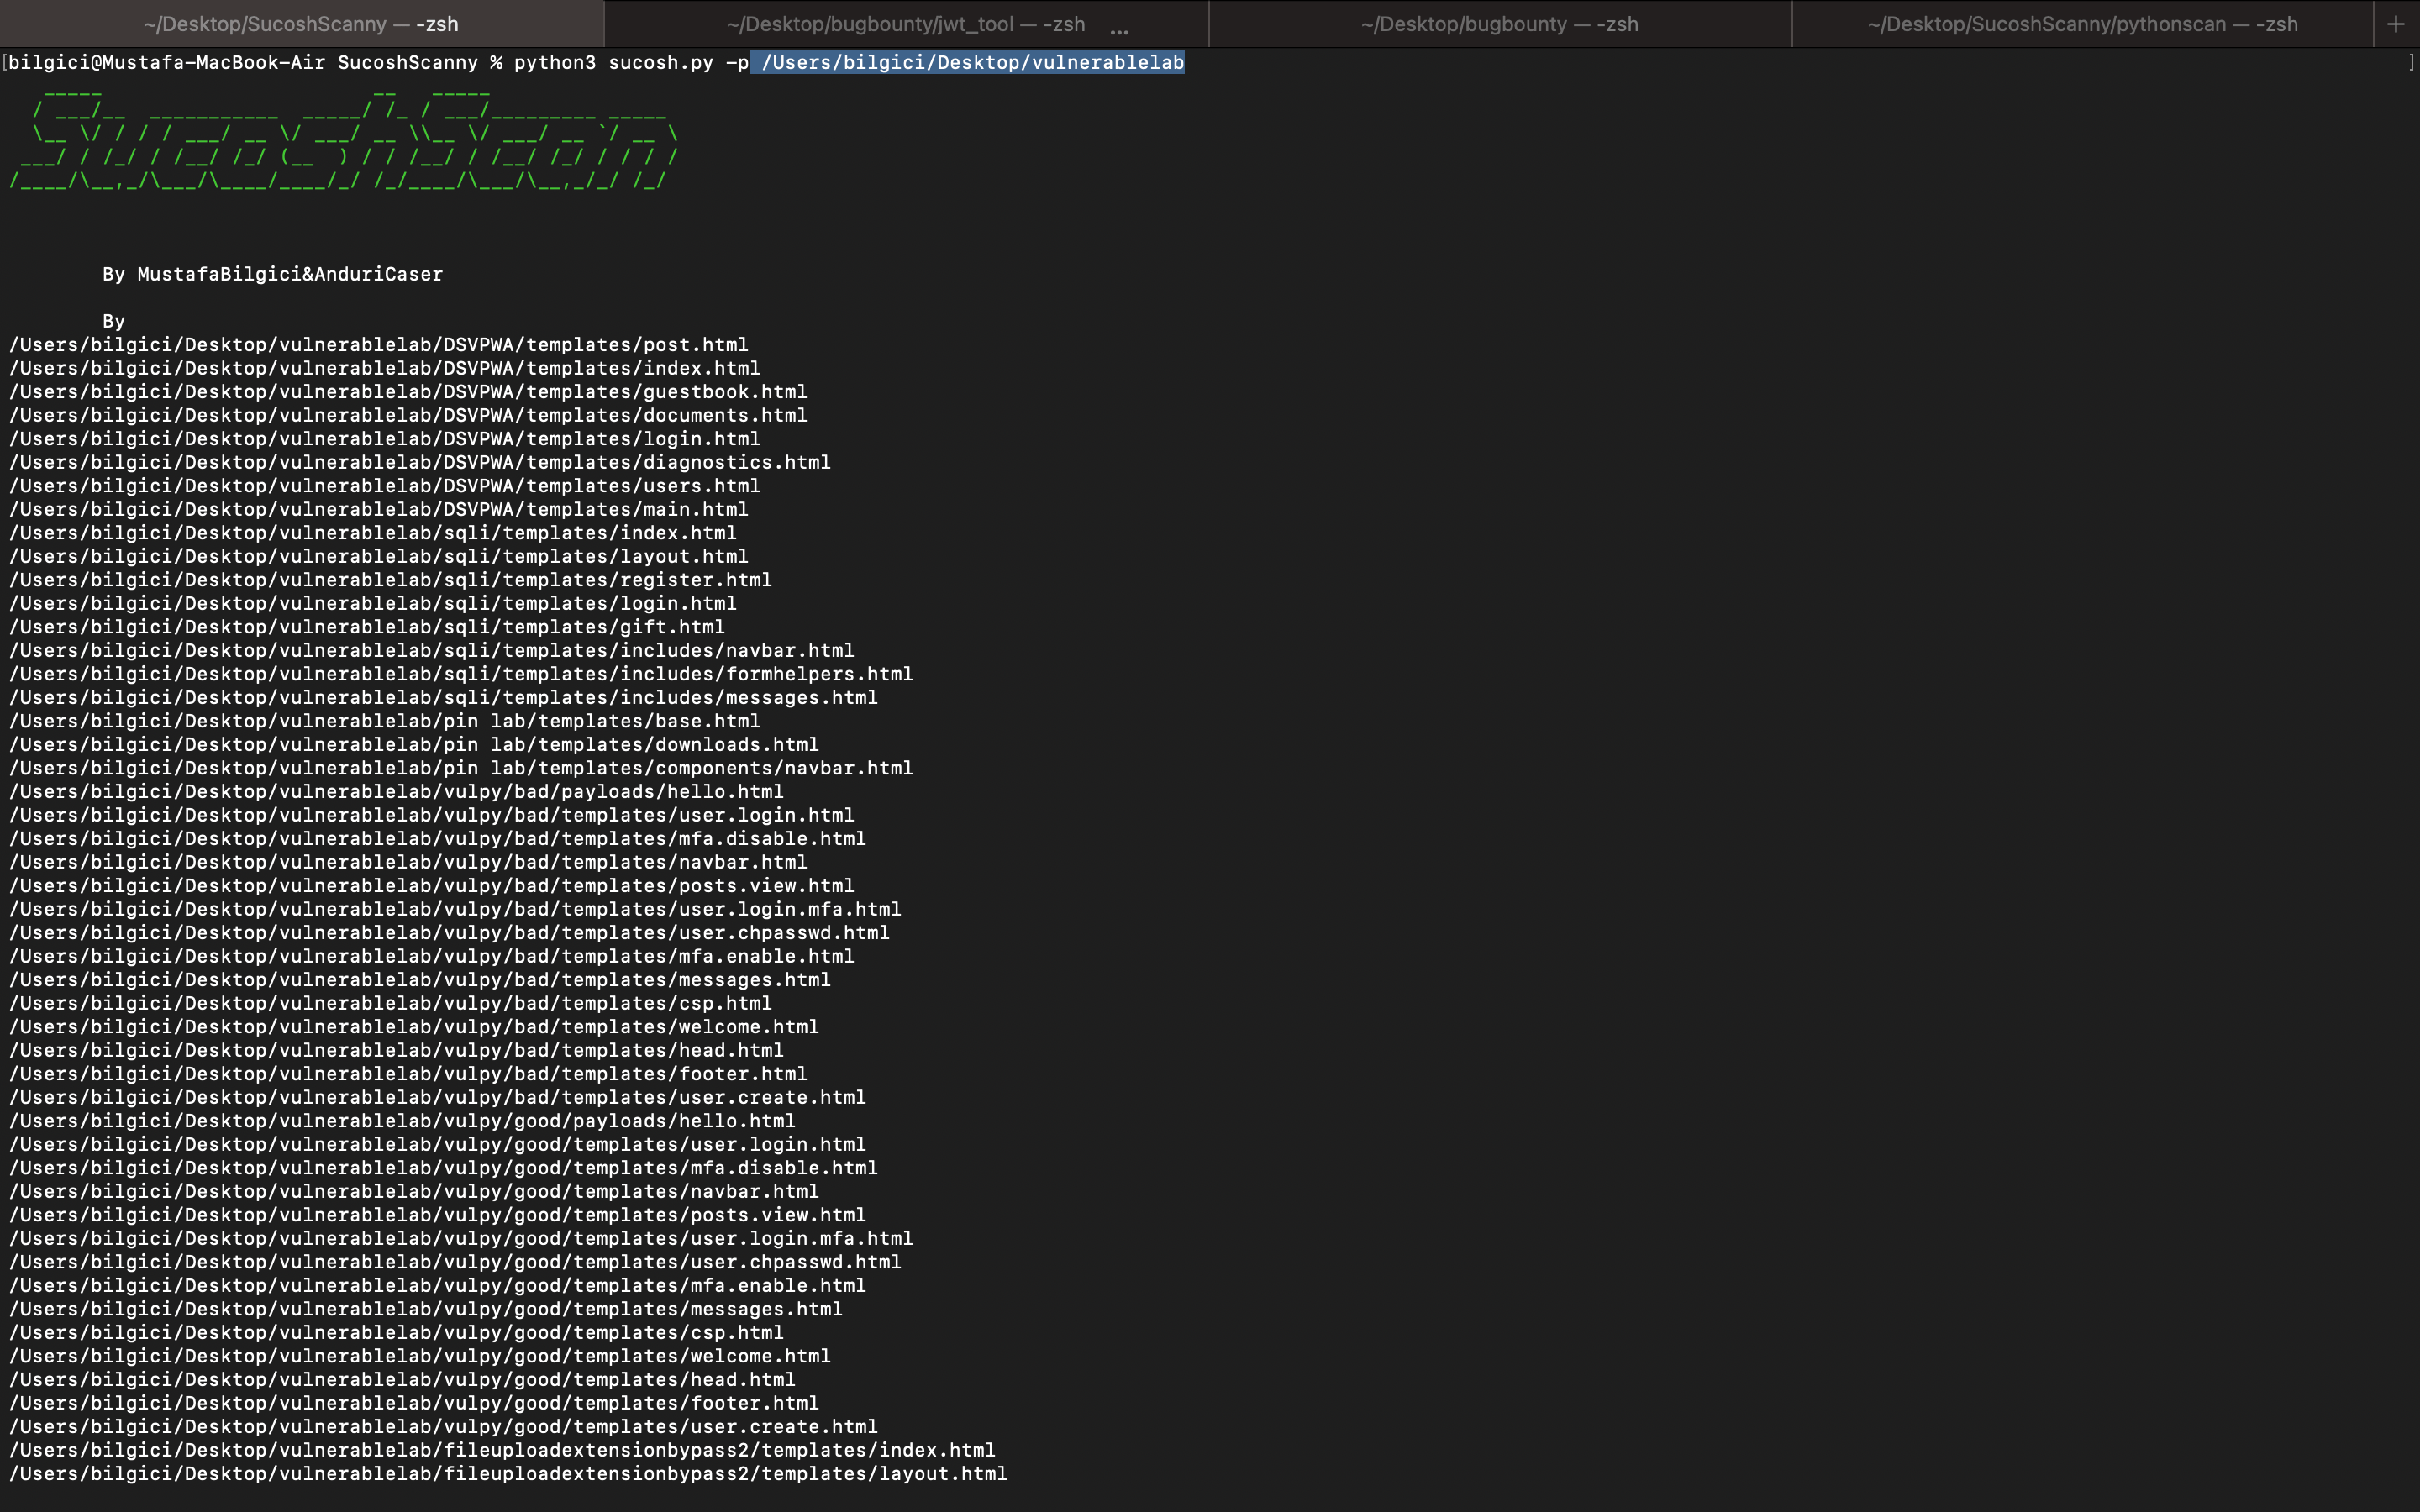 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…

 carlosalbertotuma/advisory
Public security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
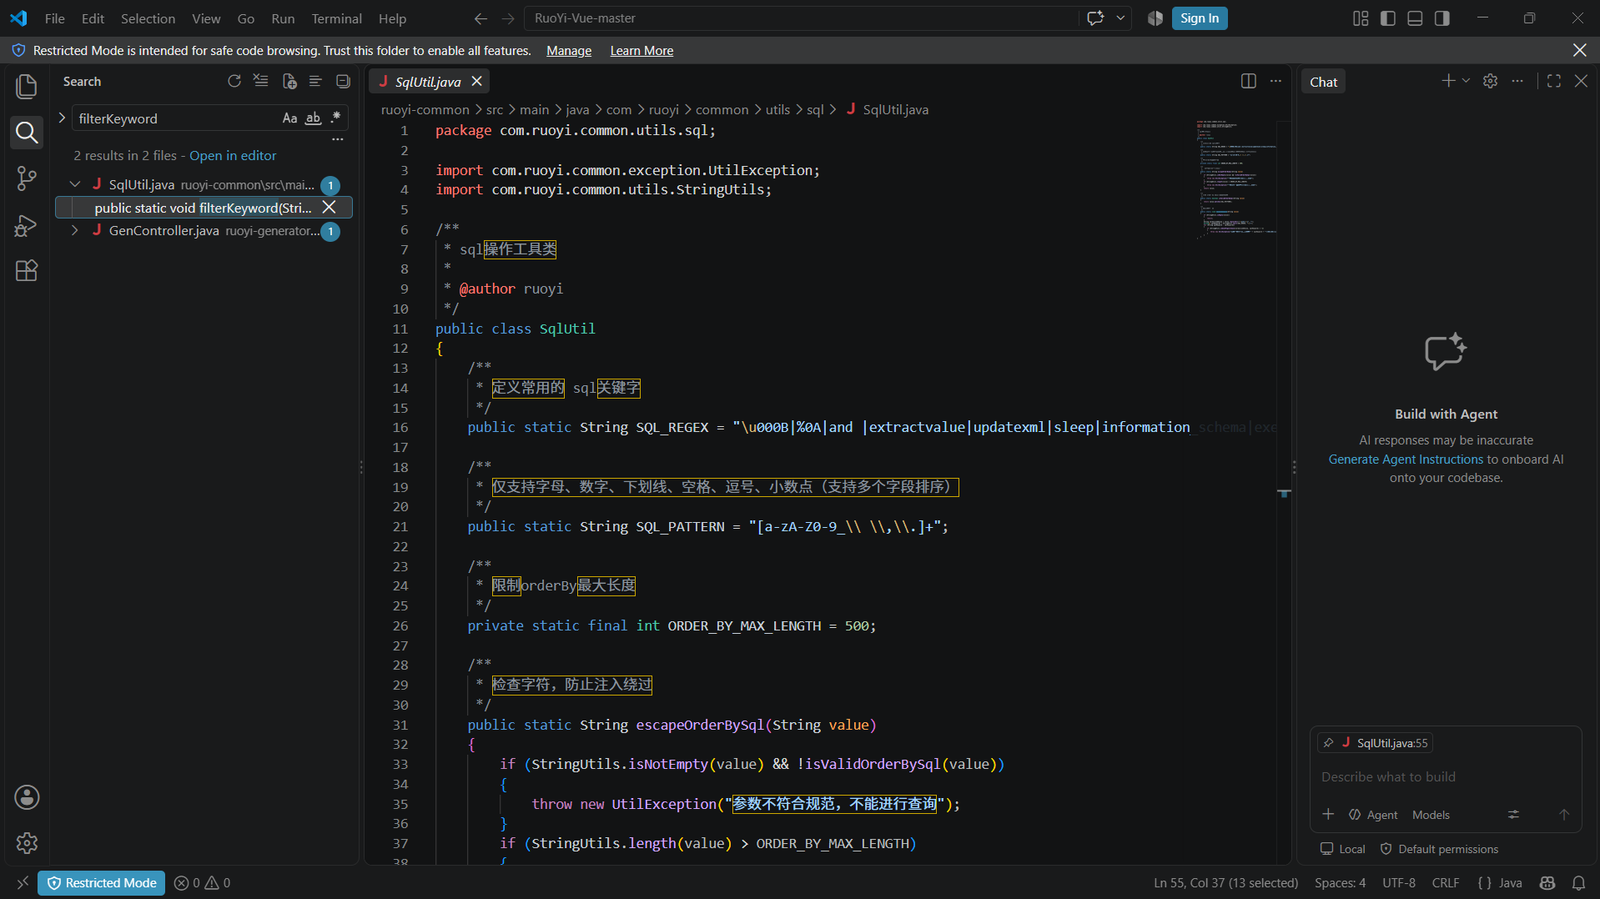 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 sassoftware/shiro
CVE-2026-49268 — Analysis and Remediation of an LDAP Injection Authentication Bypass Vulnerability
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.