

Archived
AuraBorealisApp
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
code-analysismalware-analysisstatic-code-analysis+2
iqtlabs/auraborealisappDo You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data

 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
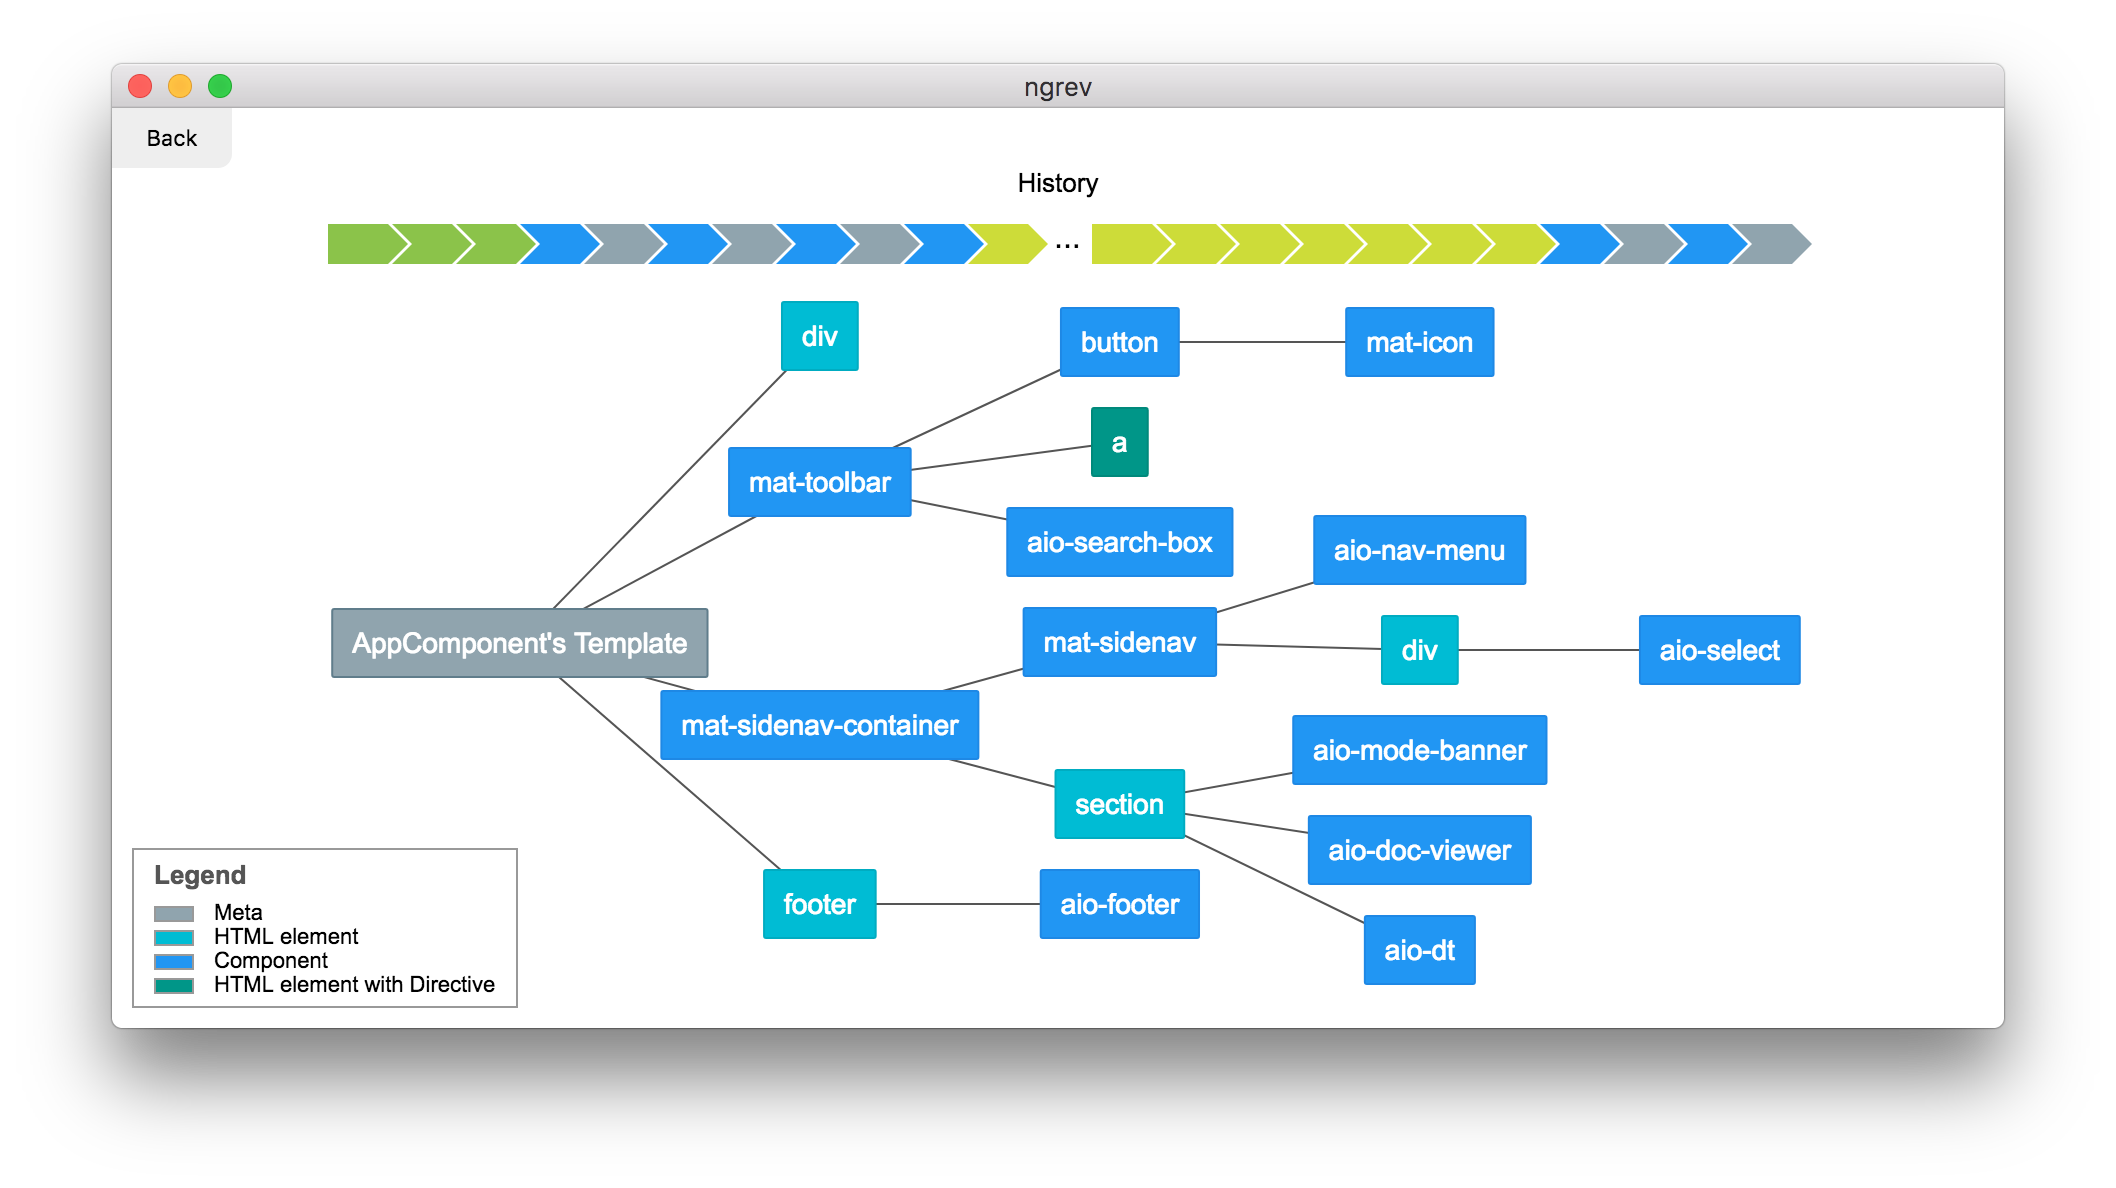 mgechev/ngrev
Tool for reverse engineering of Angular applications
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.