
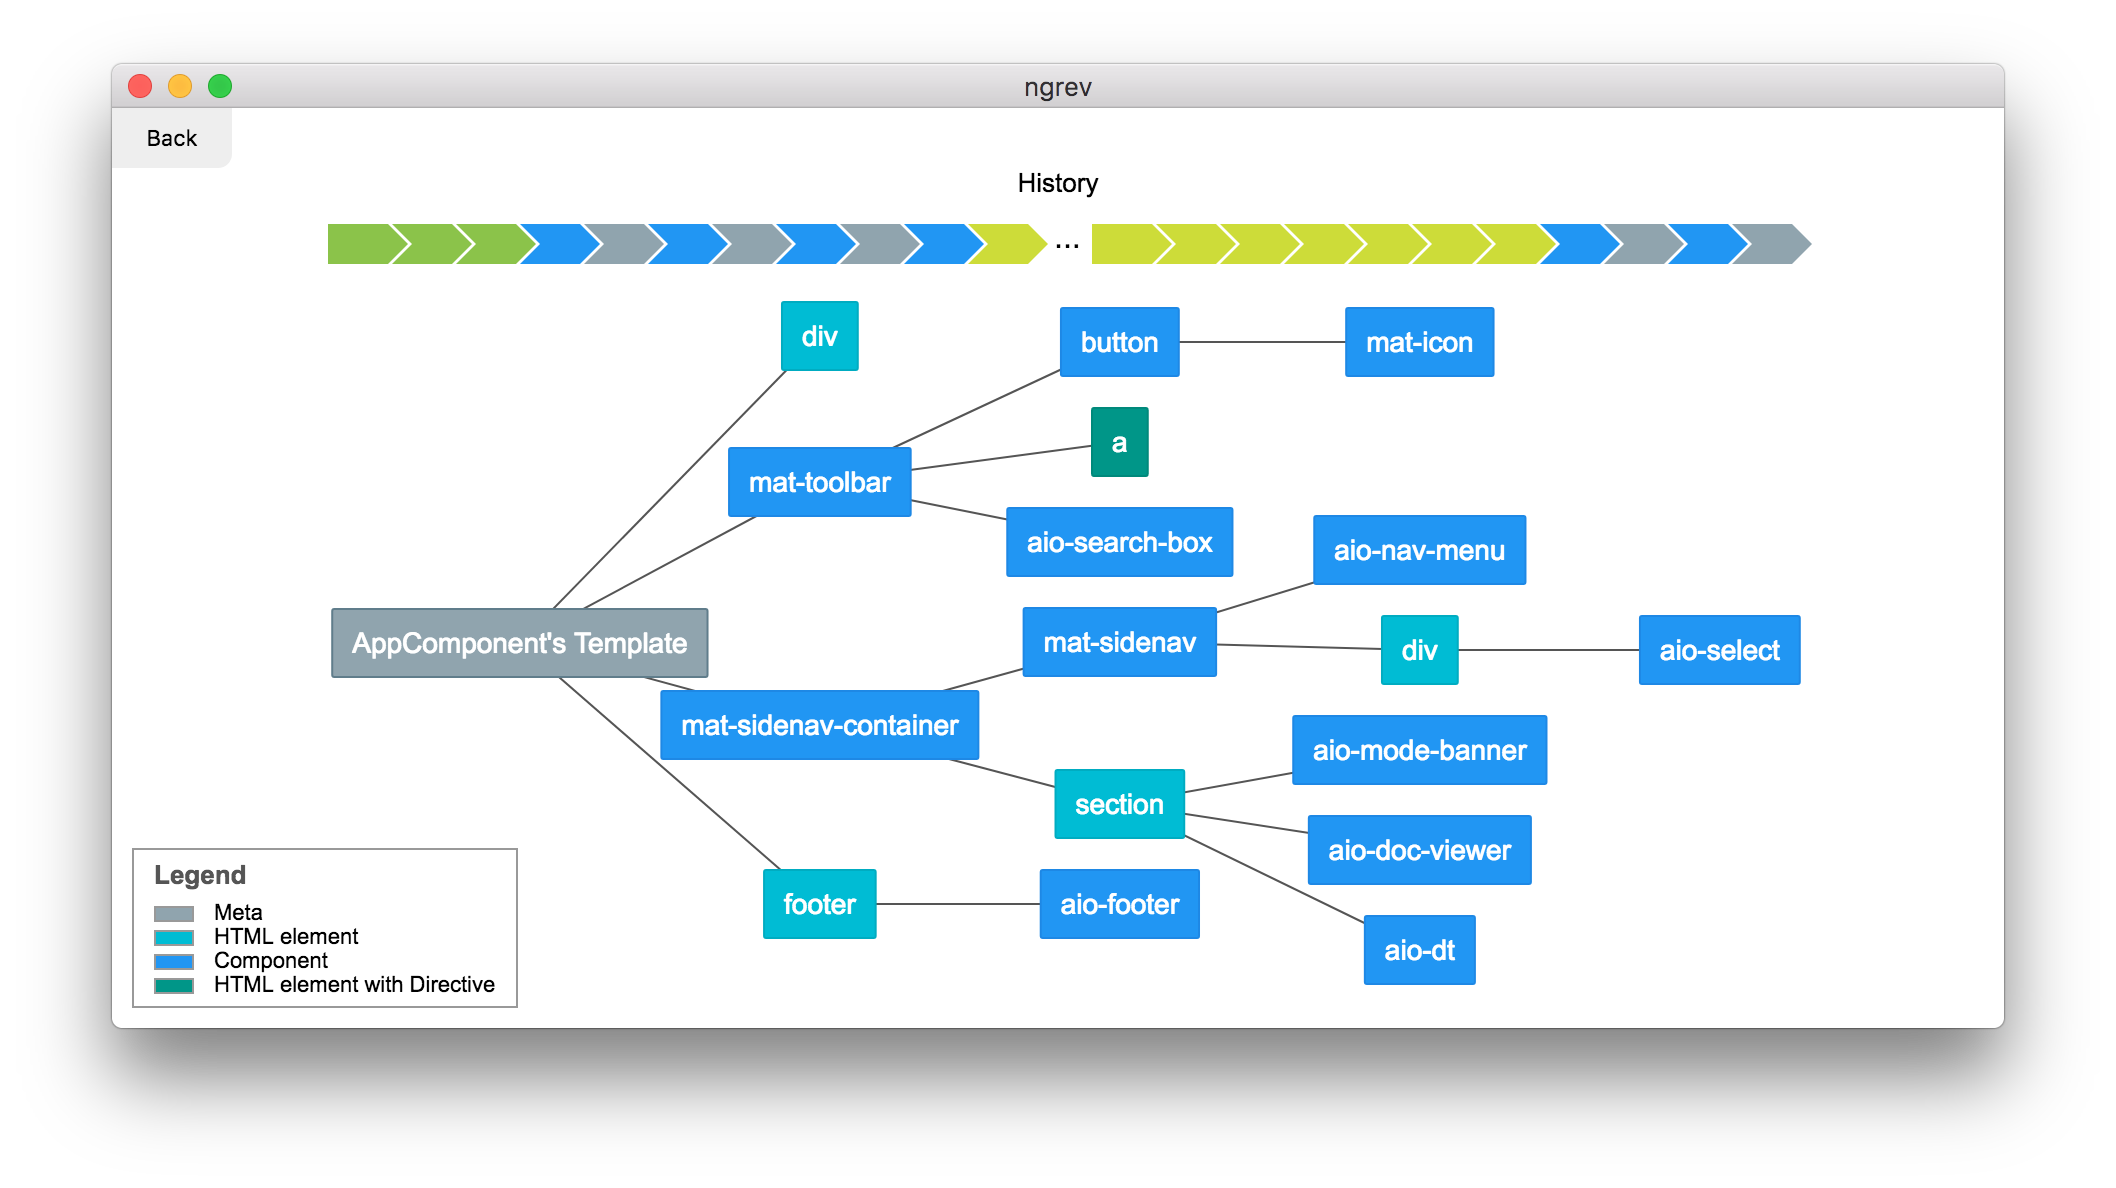
ngrev
 mgechev/ngrev
Tool for reverse engineering of Angular applications
code-analysisreverse-engineeringstatic-code-analysis
mgechev/ngrevTool for reverse engineering of Angular applications
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 s0md3v/hardcodes
find hardcoded strings from source code
 sleepthegod/cve-2026-9618-patch
Hardened PHP replacement handlers for PeachPay Stripe capture and void AJAX endpoints, adding nonce verification, capability checks, and strict order…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
 shoucheng3/codehaus-plexus__plexus-utils_cve-2022-4244_3-0-23
Java utility library with patched CVE-2022-4244 vulnerability, providing common helper classes for I/O, reflection, and CLI argument parsing in…
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 wireghoul/graudit
grep rough audit - source code auditing tool
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
 mhaskar/bughound
Static code analysis tool based on Elasticsearch