

DakshSCRA
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
code-analysisdevsecopseducation+7
45
coffeeandsecurity/dakshscraFramework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
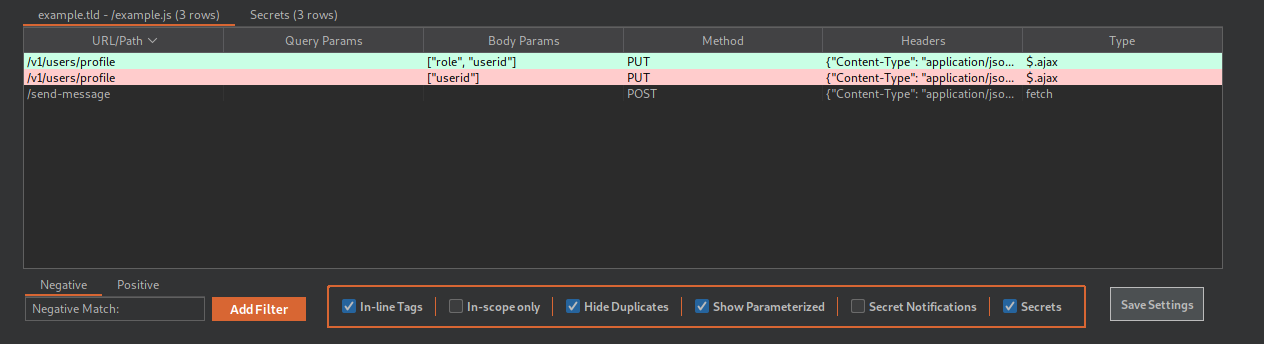 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

 owasp/riskassessmentframework
The Secure Coding Framework

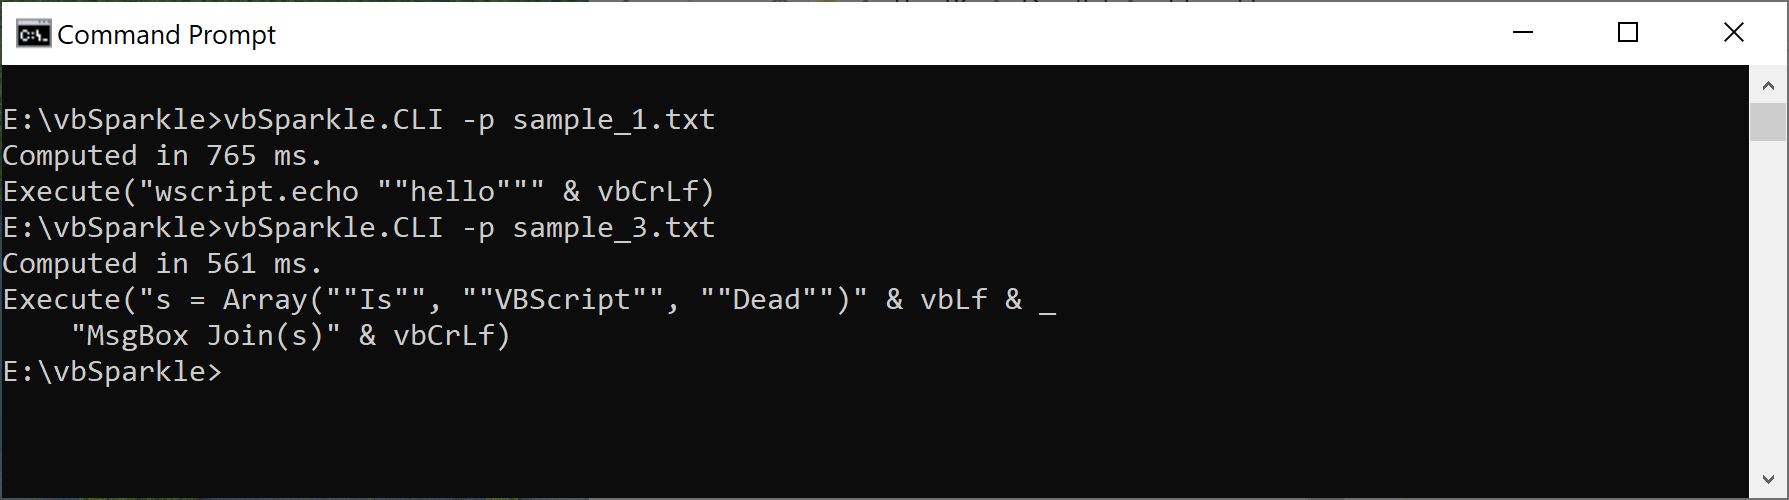 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
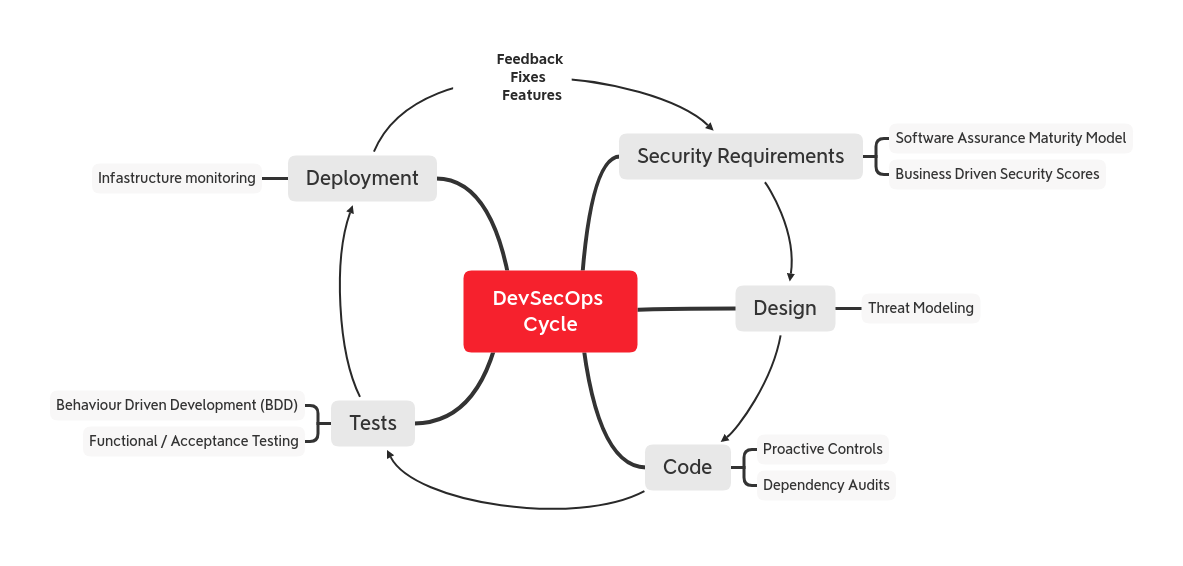 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…