

JShunter
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
api-securitydynamic-code-analysispenetration-testing+6
536
cc1a2b/jshunterjshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 wireghoul/graudit
grep rough audit - source code auditing tool
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
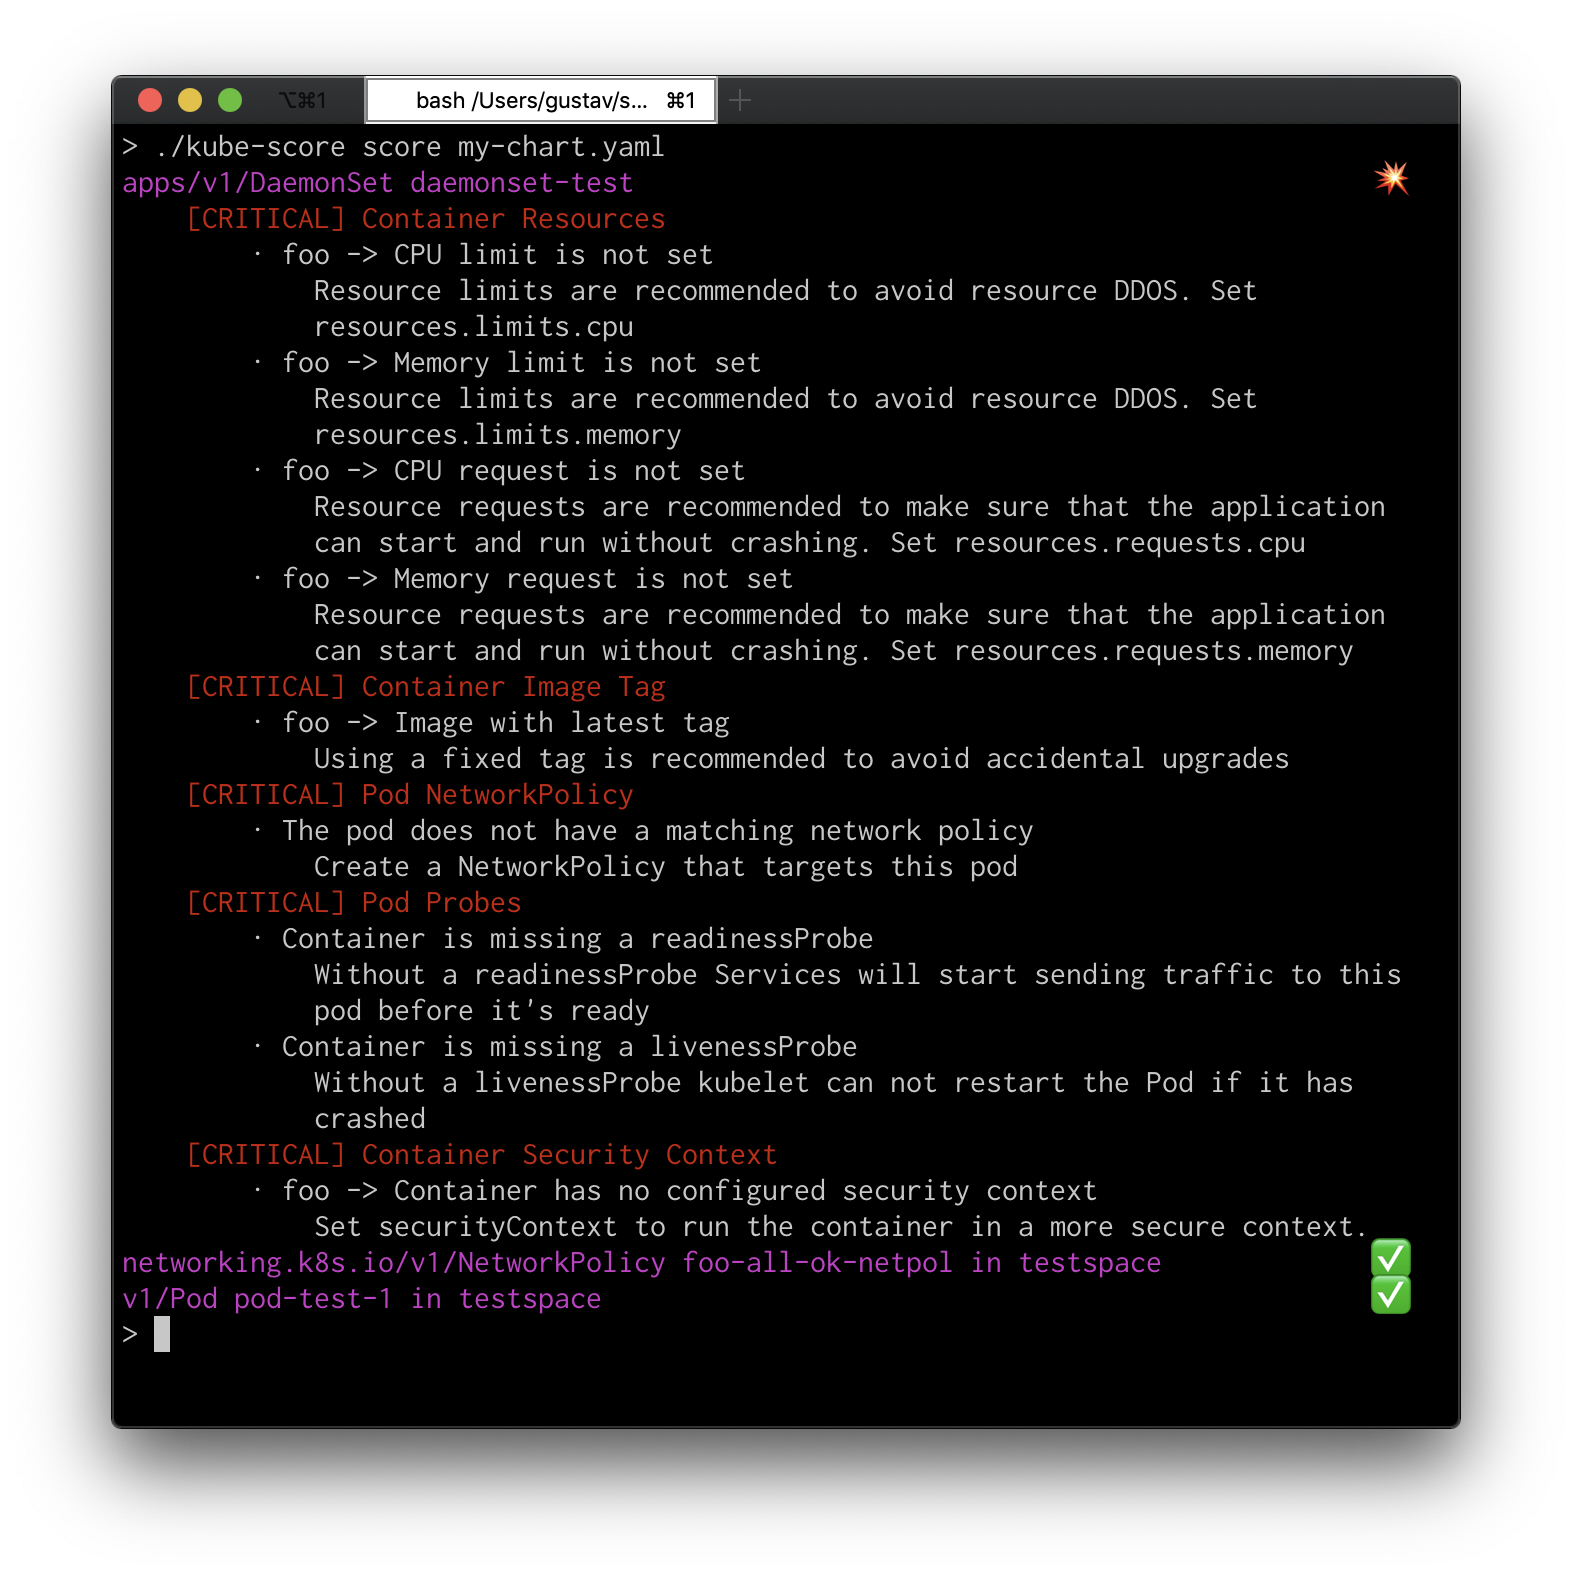 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
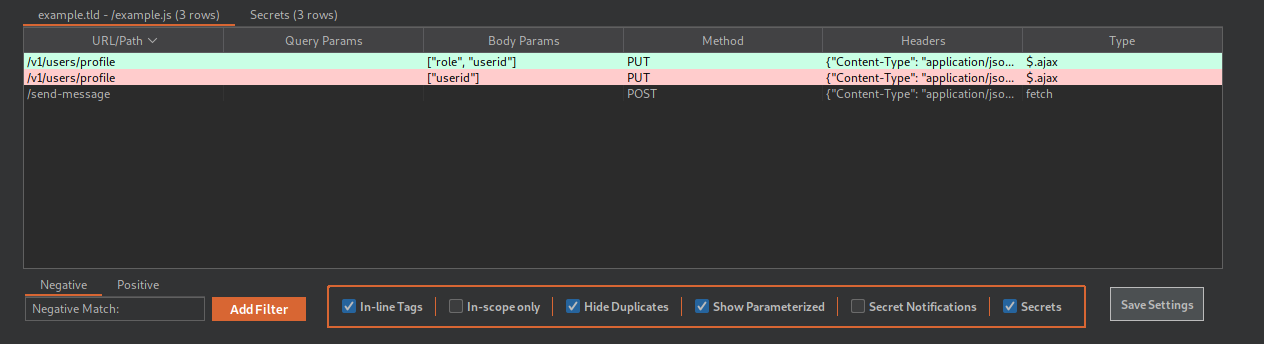 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice