

CanoP
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
ai-securitycode-analysisdefensive-tools+7
5
openbreach/canopStatic analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
 0p4n1k/noctyra
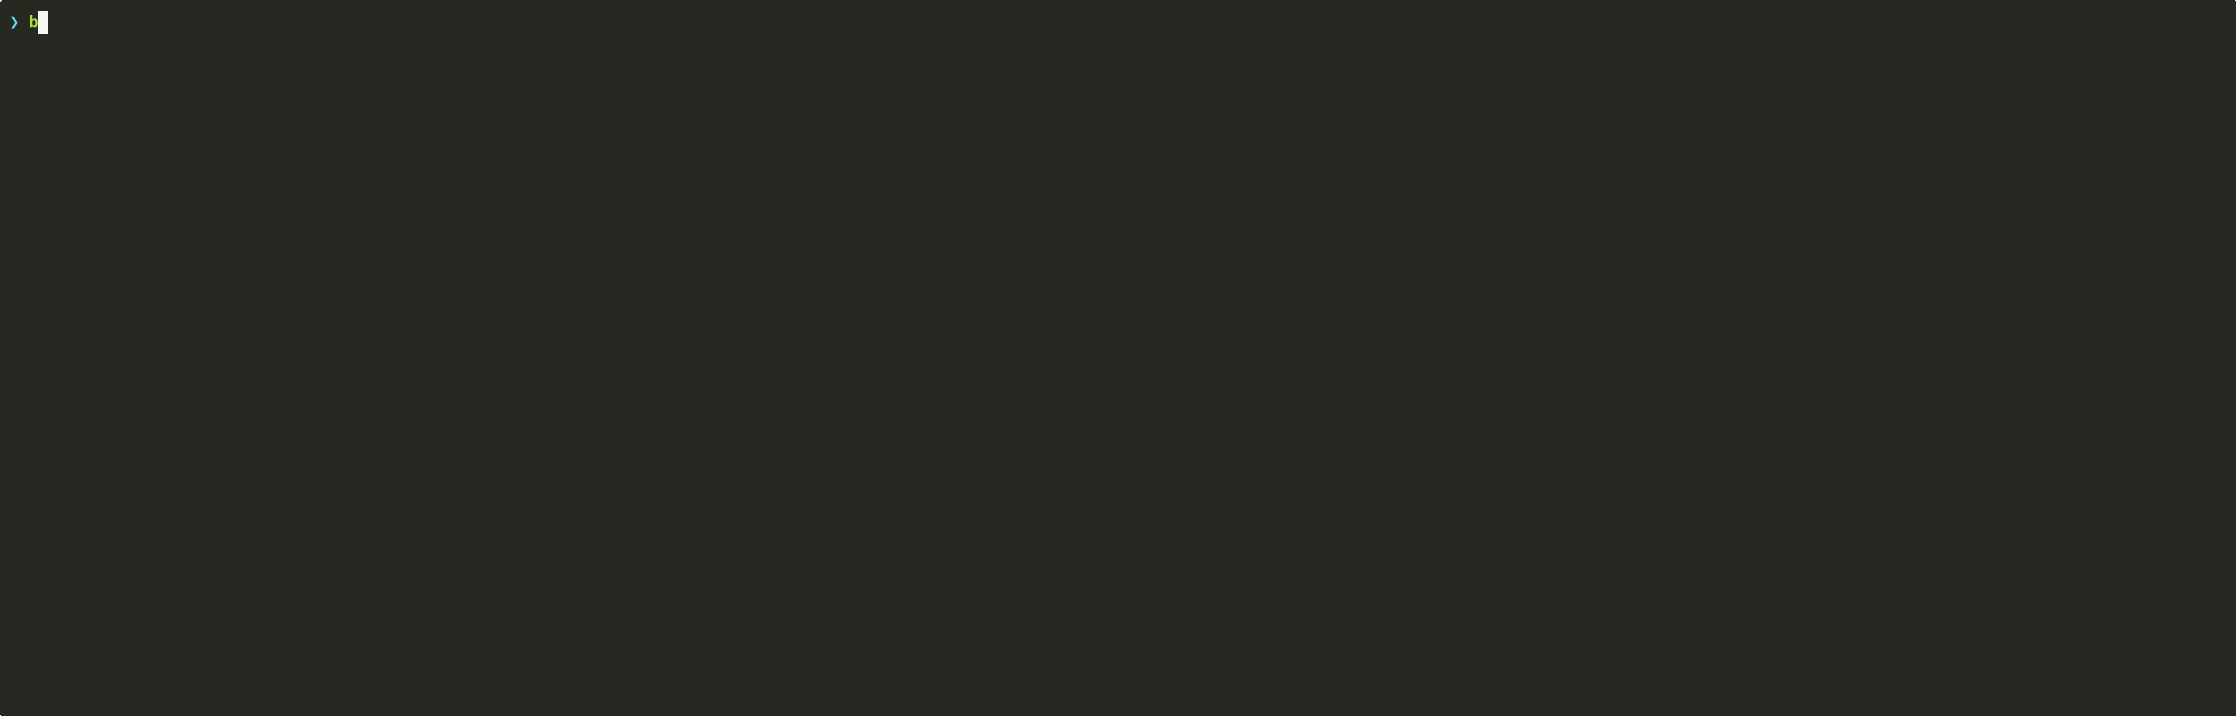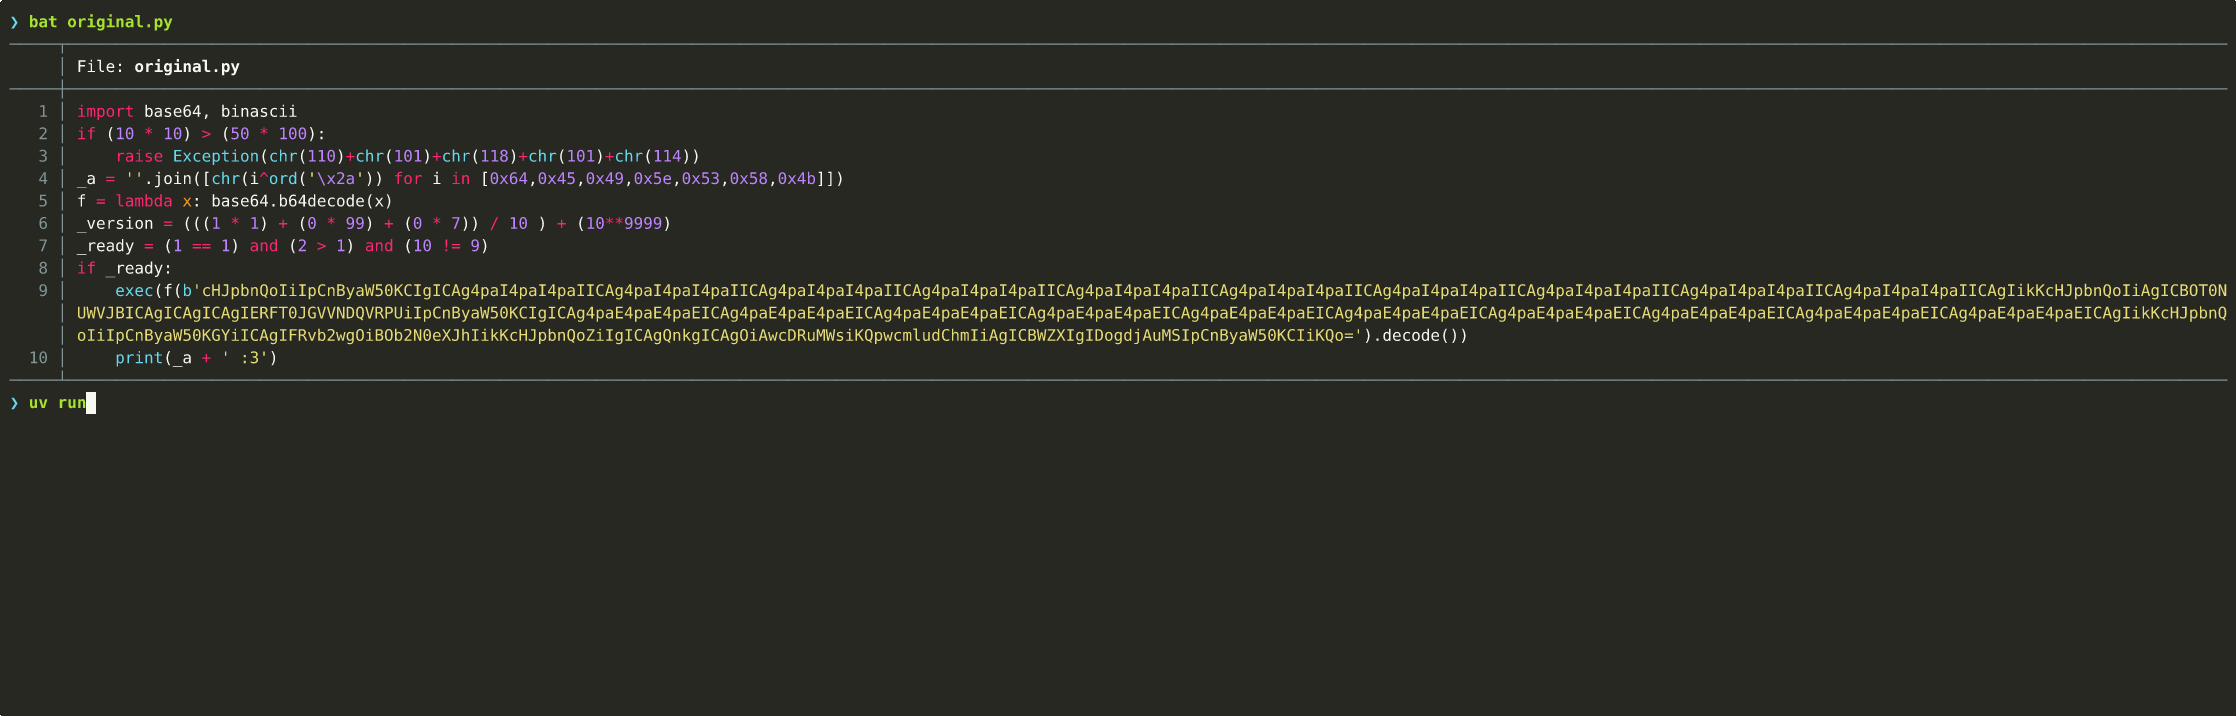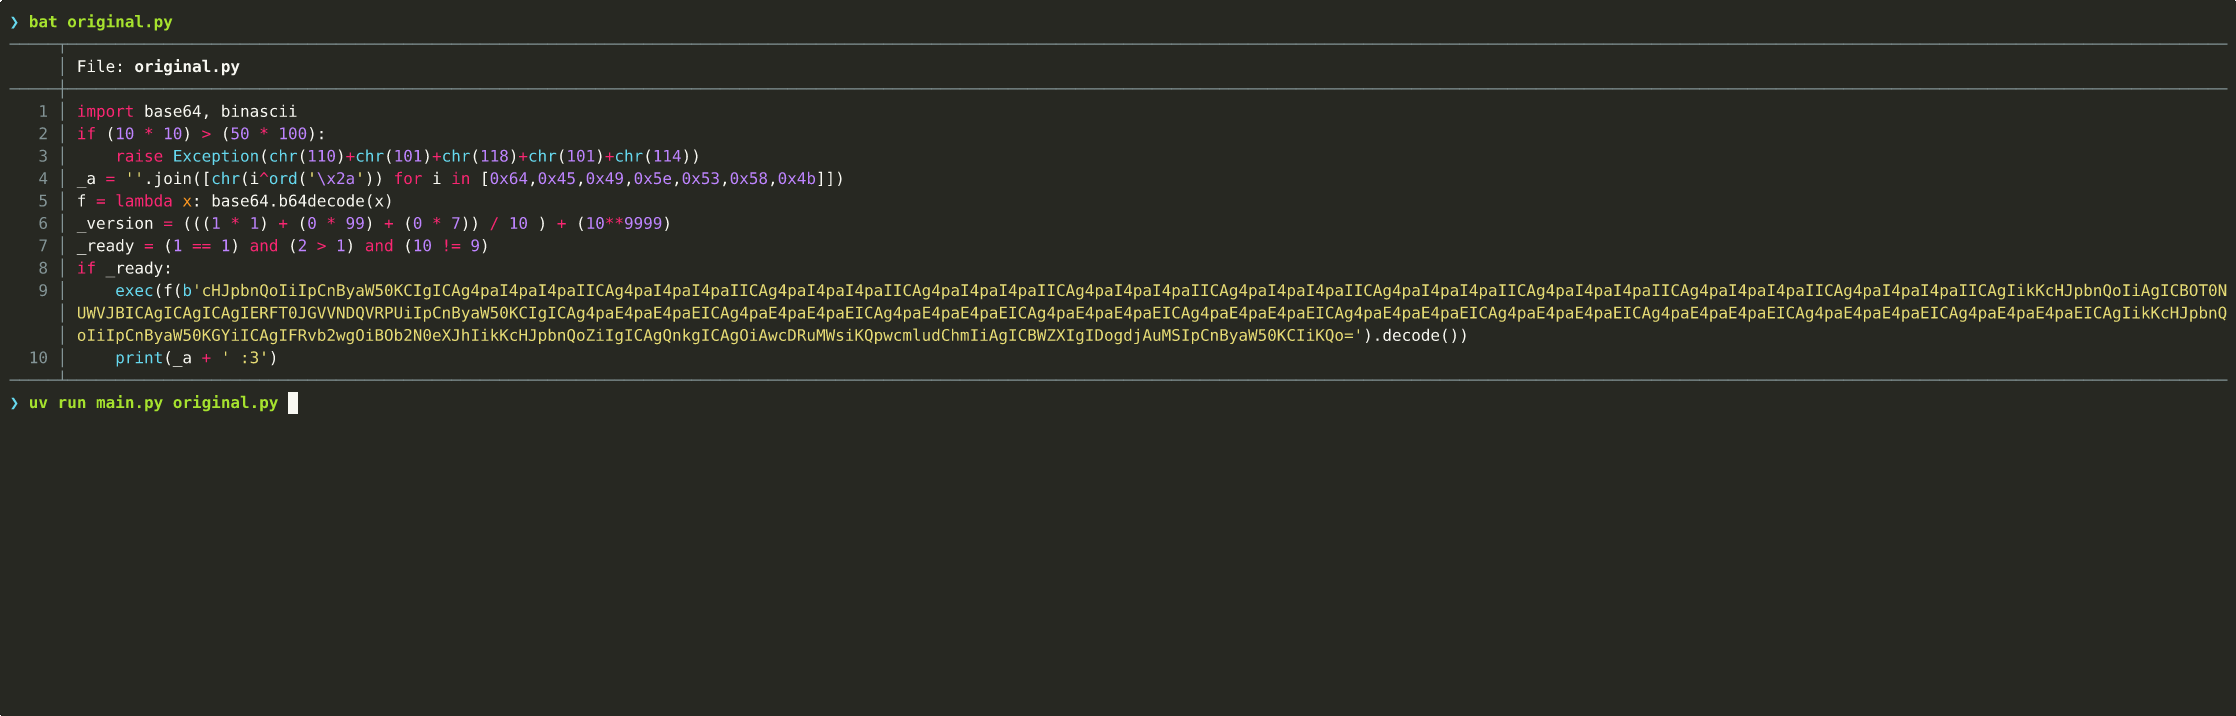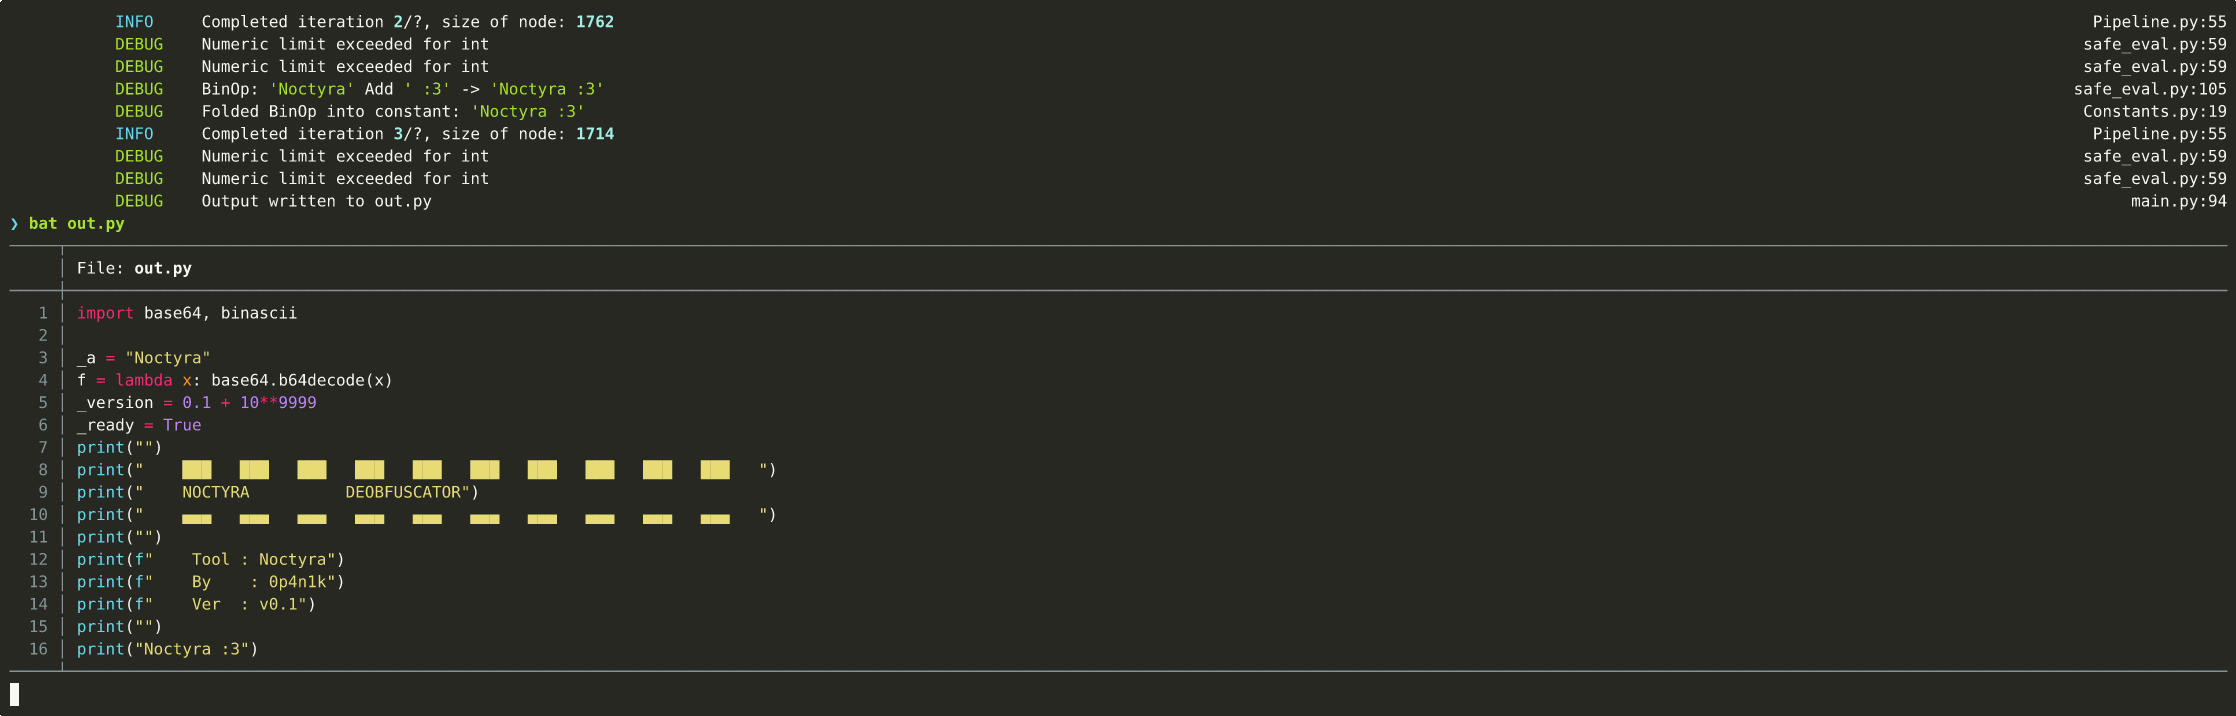
AST-based Python code transformation & deobfuscation framework
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…