
static-analysis
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
code-analysiscurated-resourcesdevsecops+5
14.9k
analysis-tools-dev/static-analysisCurated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 scastillo-jp/braces-fork
Temporary fork of braces with a minimal security patch for CVE-2026-93687, created only to validate dependency override behavior and Fortify/FoD…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
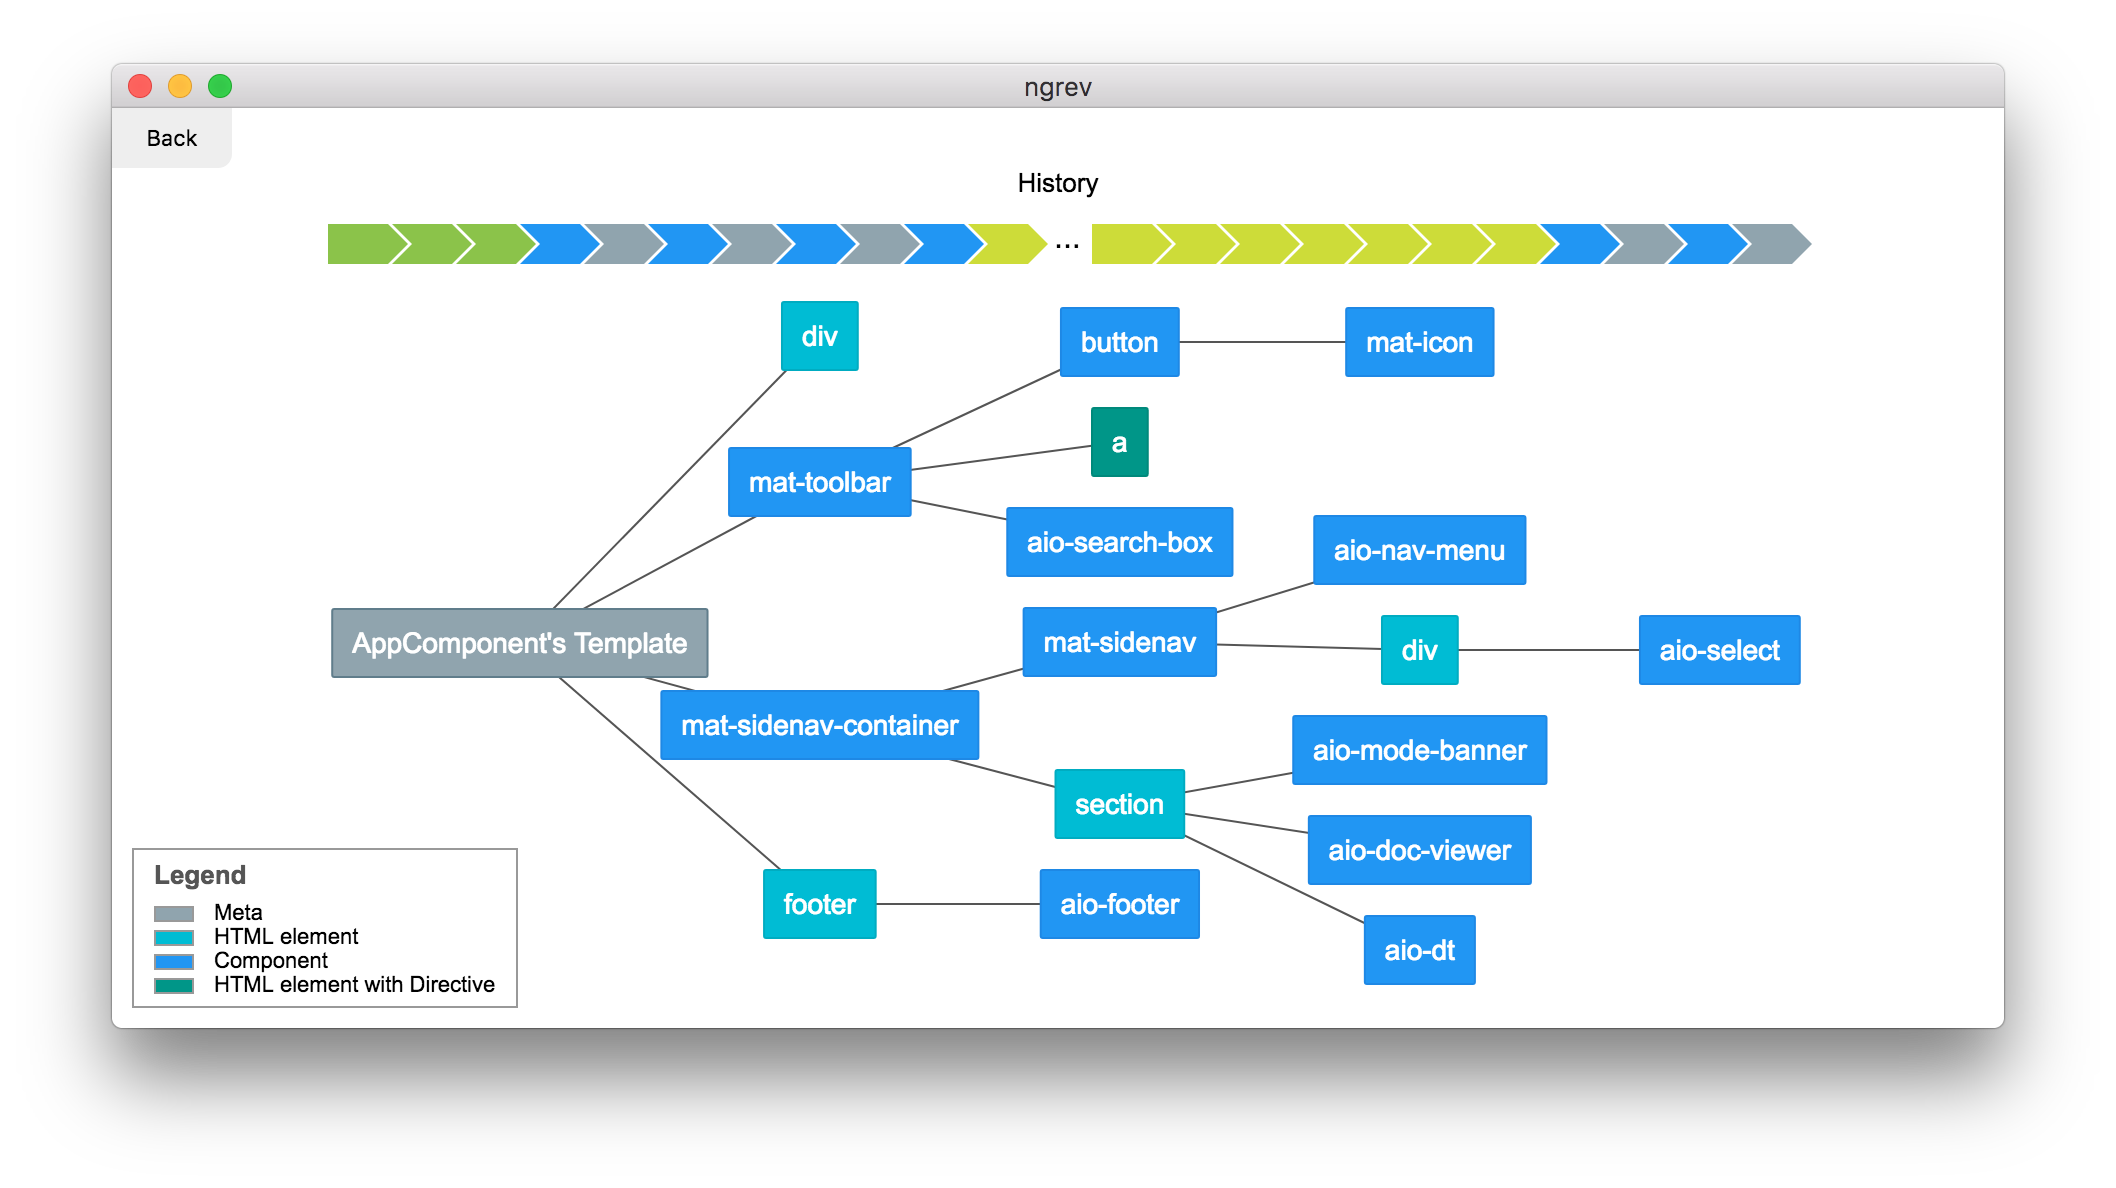 mgechev/ngrev
Tool for reverse engineering of Angular applications
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 synacktiv/weggli_rules_sstic2023
Curated weggli queries for static analysis of C/C++ code to identify dangerous functions, stack issues, and malloc overflow vulnerabilities.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…

 carlosalbertotuma/advisory
Public security advisories and PoCs for vulnerabilities discovered in open-source web software, with root-cause analysis, CVE references,…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 reverseclabs/needle
The iOS Security Testing Framework
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
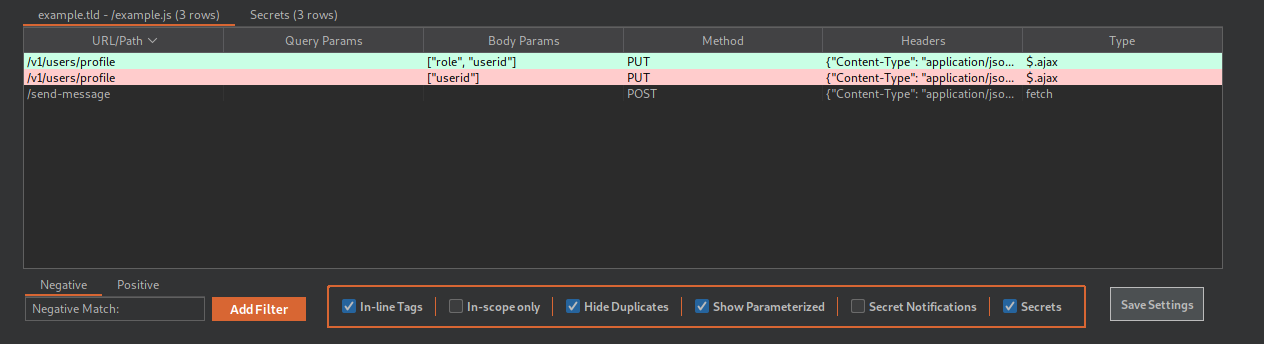 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
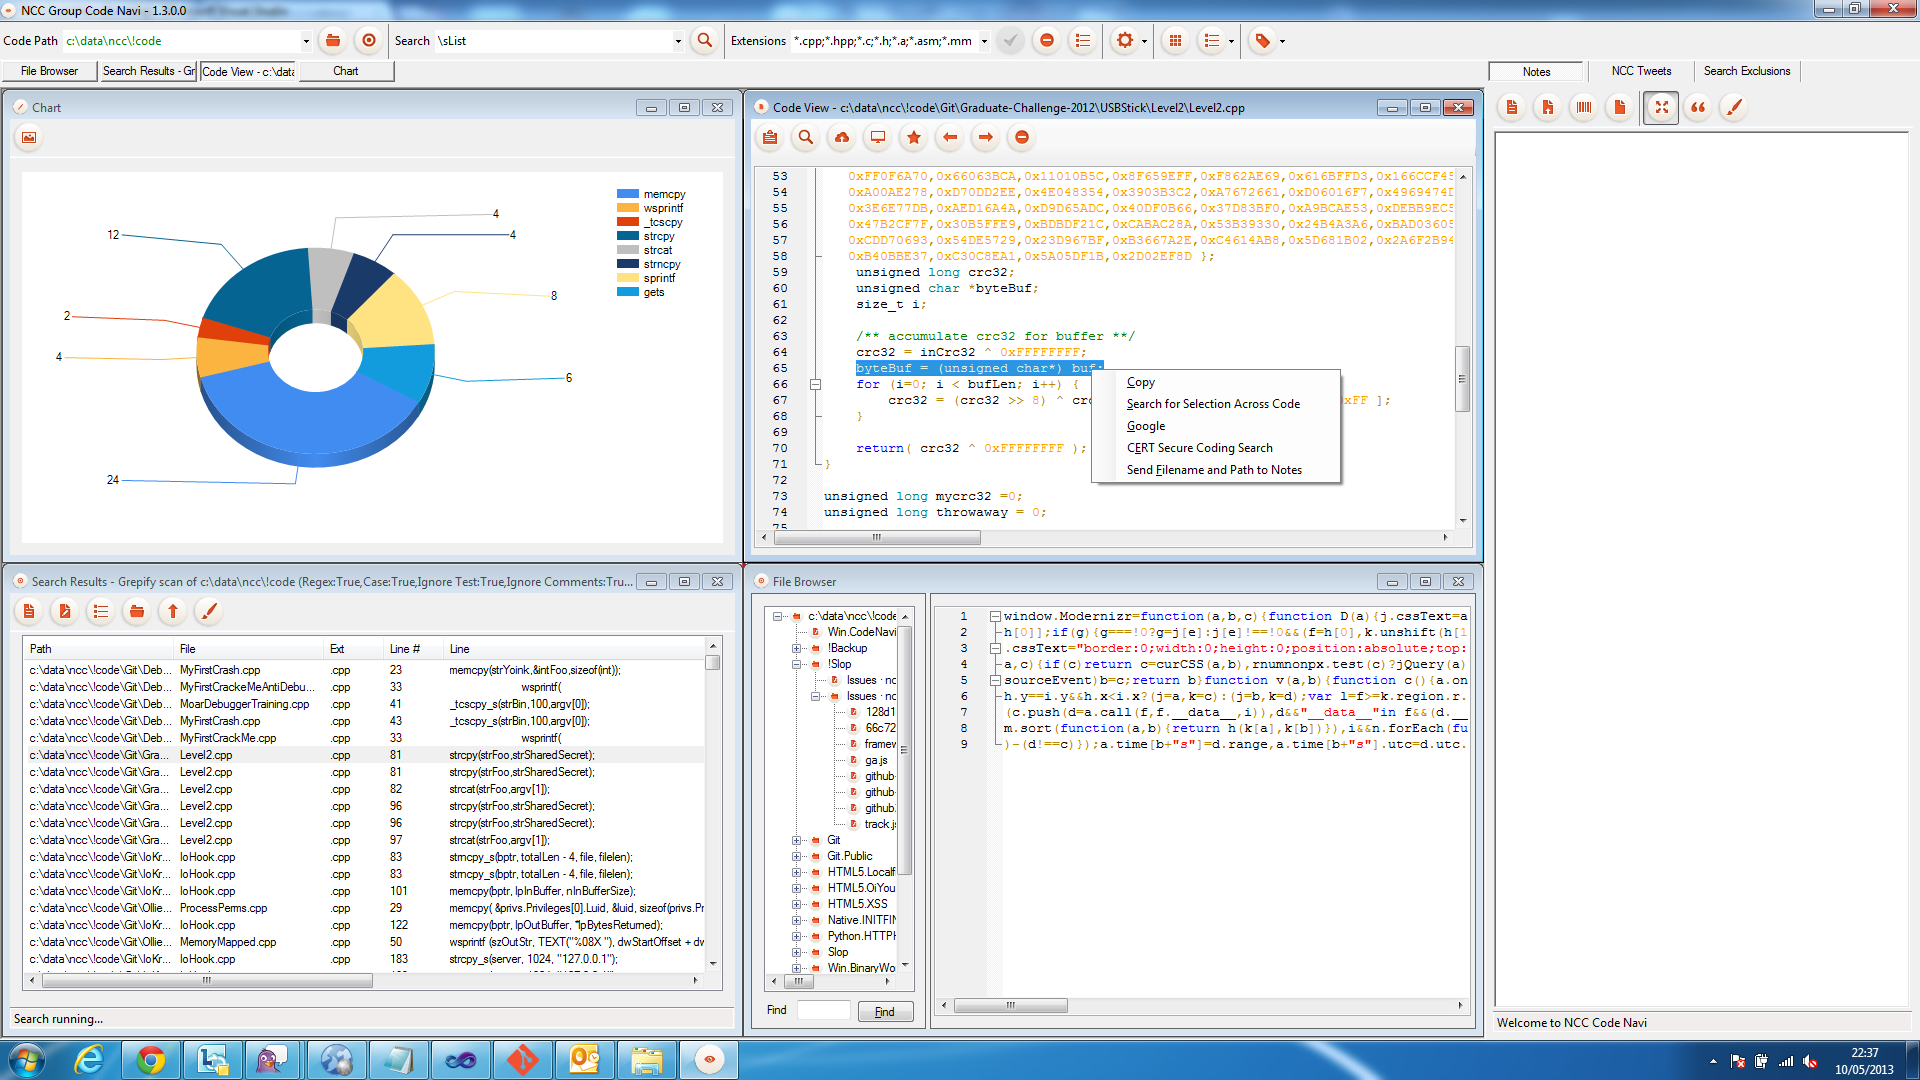 nccgroup/ncccodenavi
NCC Code Navigator