

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
16.7k
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
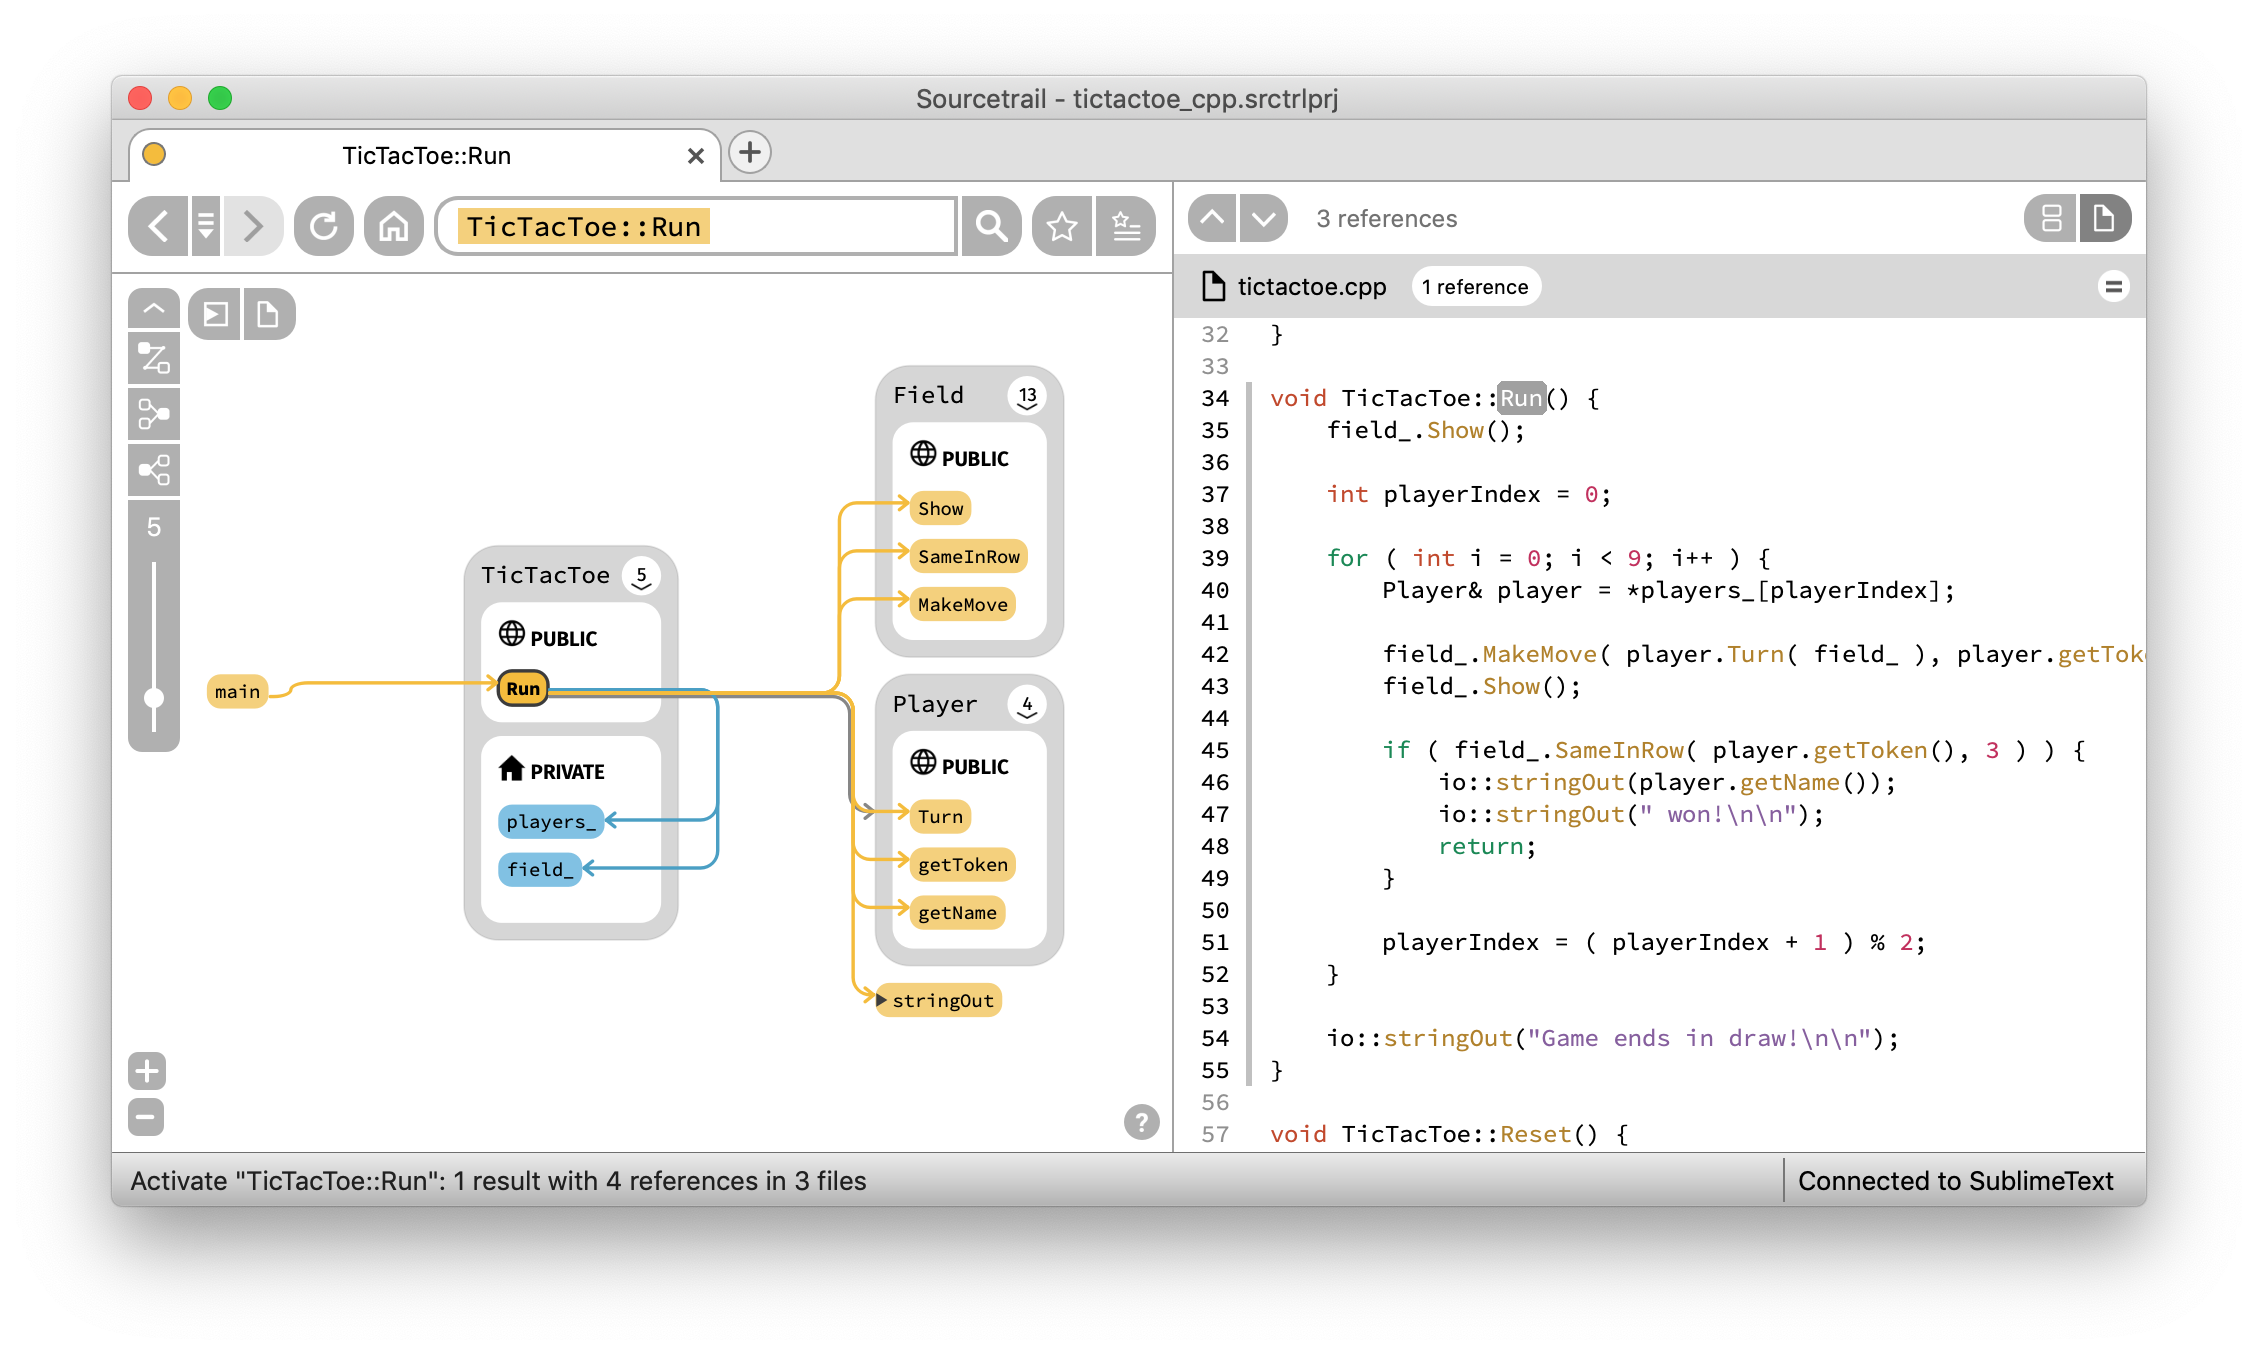 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
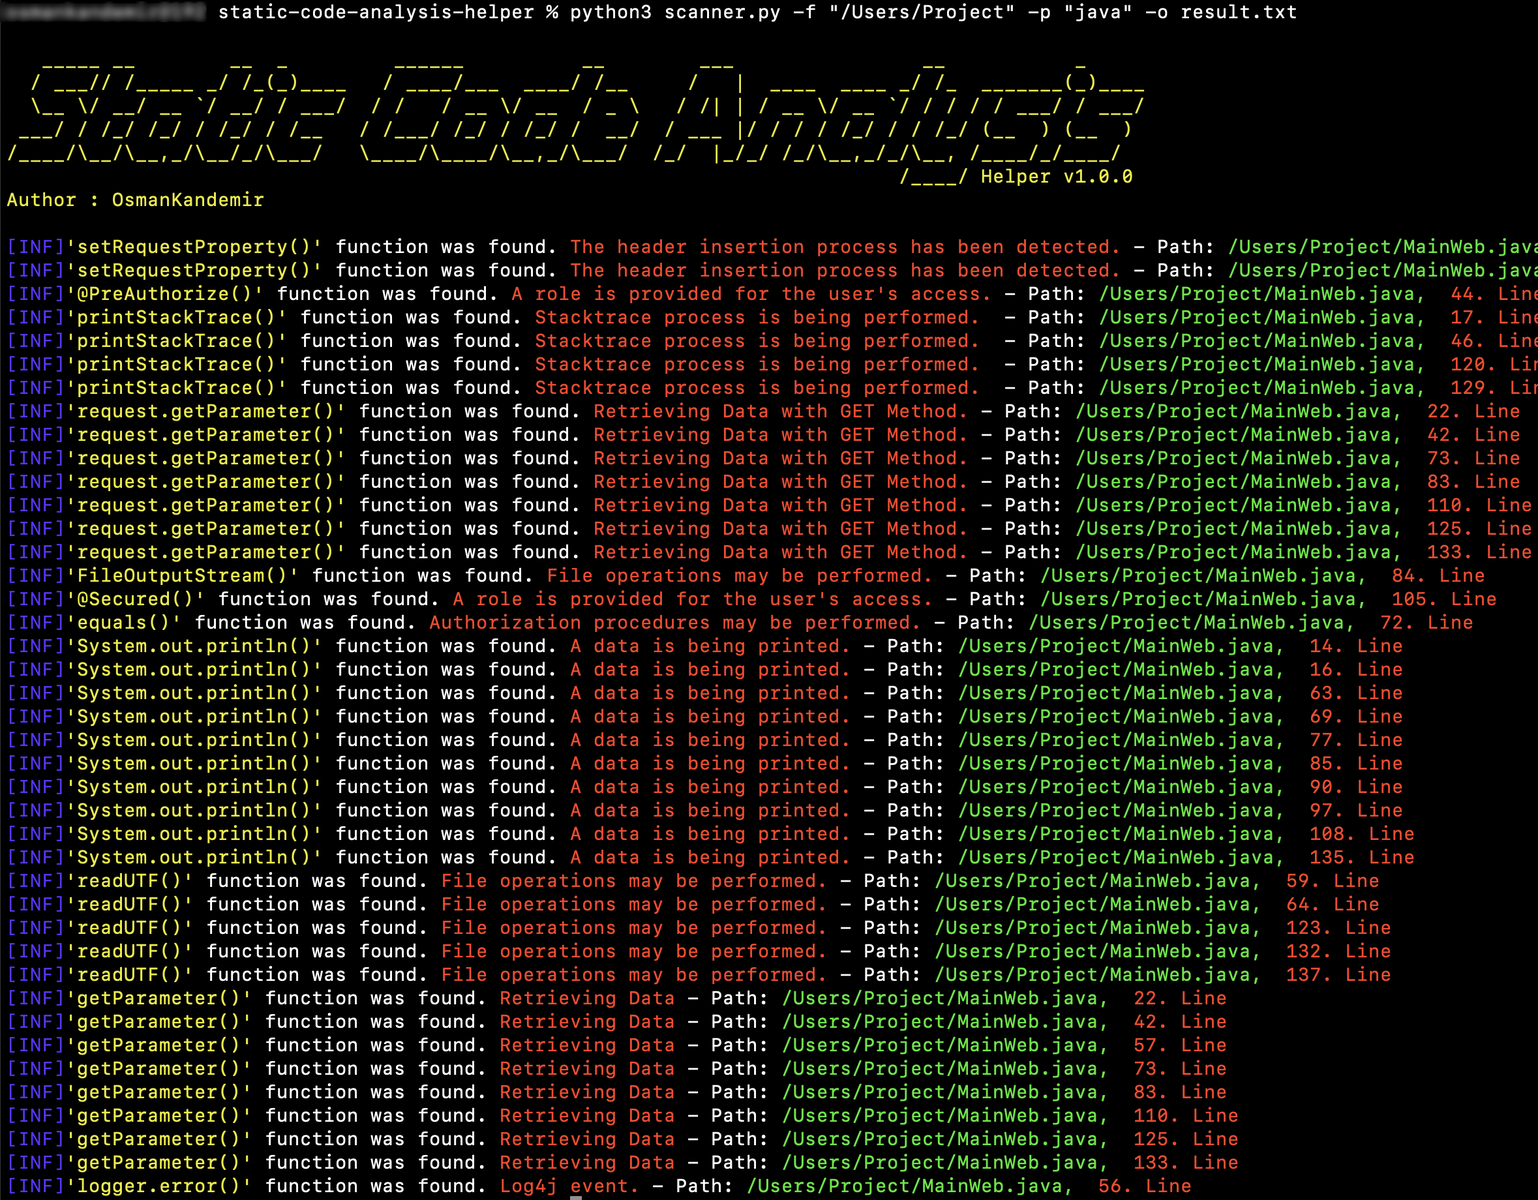 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 noveogroup/android-check
Static code analysis plugin for Android project. (Checkstyle, PMD)
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 tai-e/cve-2021-44228
Utilize Tai-e to identify the Log4shell (a.k.a. CVE-2021-44228) Vulnerability
 yousif-iq/cve-2026-39259
CVE-2026-39259
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 analysis-tools-dev/static-analysis
Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…