
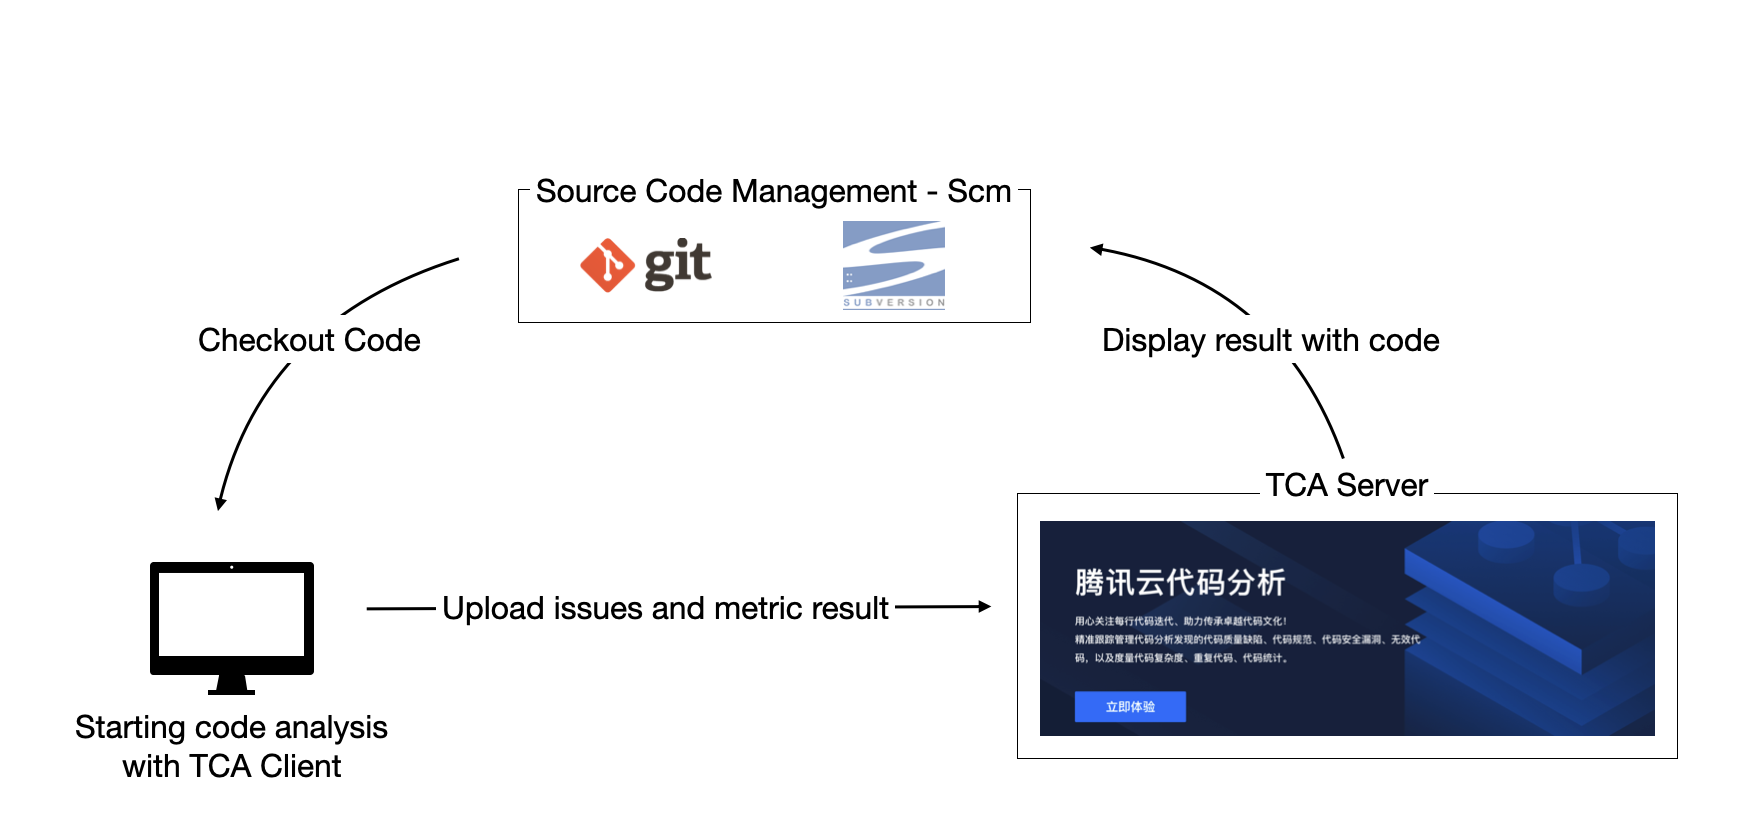
CodeAnalysis
 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
code-analysisdevsecopseducation+3
1.9k
tencent/codeanalysisEnterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
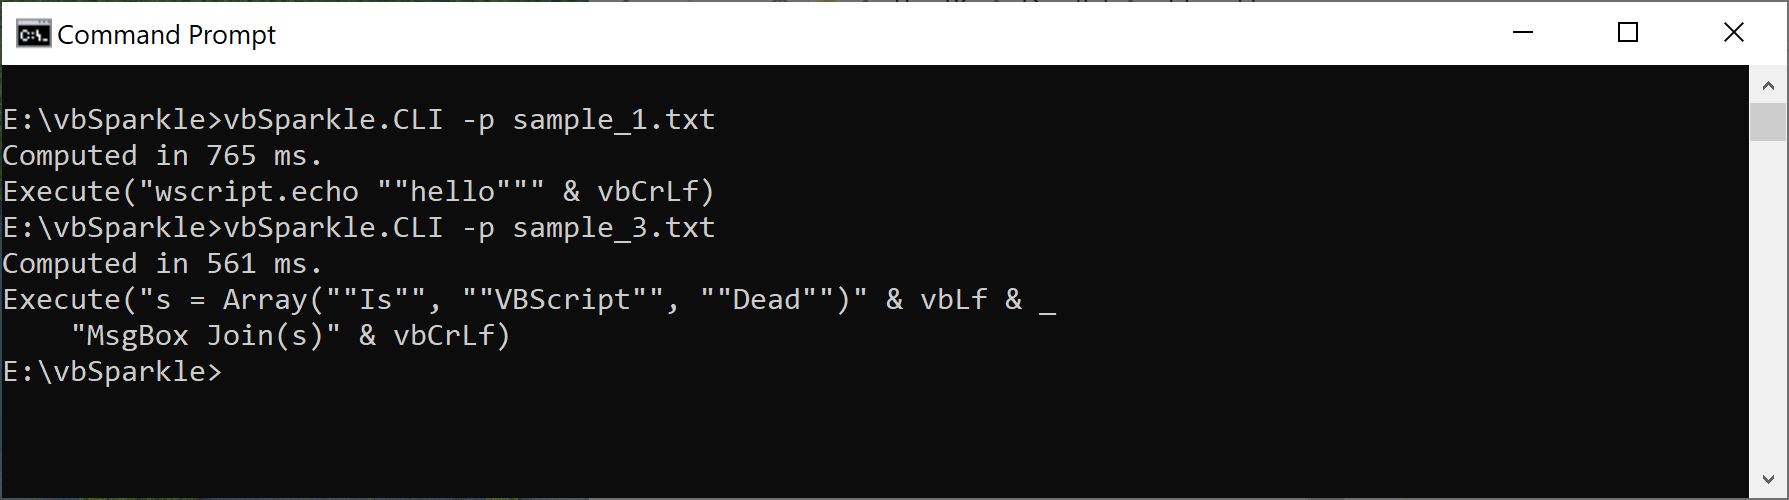 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 opsxcq/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution exploit and vulnerable container
 owasp/asst
OWASP ASST (Automated Software Security Toolkit) | A Novel Open Source Web Security Scanner.
 tai-e/cve-2021-44228
Utilize Tai-e to identify the Log4shell (a.k.a. CVE-2021-44228) Vulnerability
 yousif-iq/cve-2026-39259
CVE-2026-39259
 7alen7/cve-2026-48813-poc
Proof-of-concept exploit for terminal escape sequence injection via malicious filenames that hides Flawfinder's scan findings; fixed in version…
 0xmrma/cve-2026-32722
Bloomberg Memray’s Stored XSS via Unescaped Command-Line Metadata
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
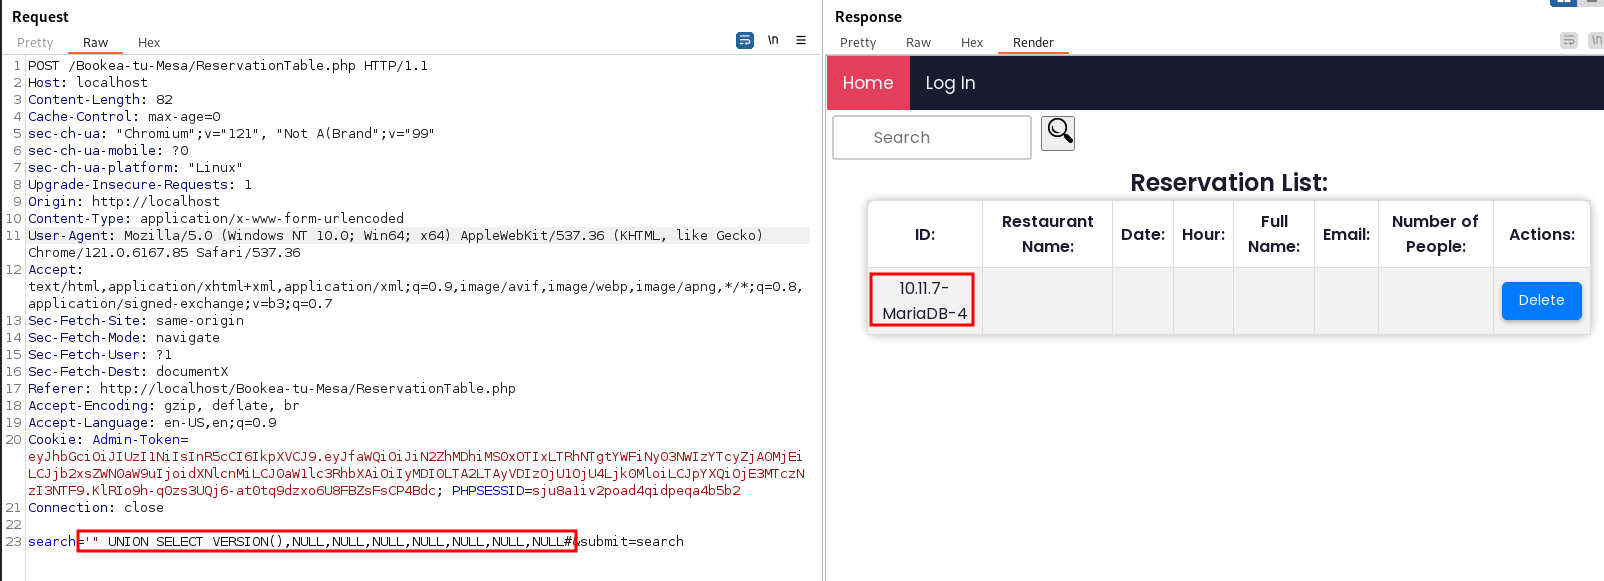 patrickdeanramos/cve-2024-41302-bookea-tu-mesa-is-vulnerable-to-sql-injection
Bookea-tu-Mesa is vulnerable to SQL Injection
 m-lito13/sealsecurity_exam
Fix prototype pollution vulnerability (CVE-2023-26136) for tough-cookie package
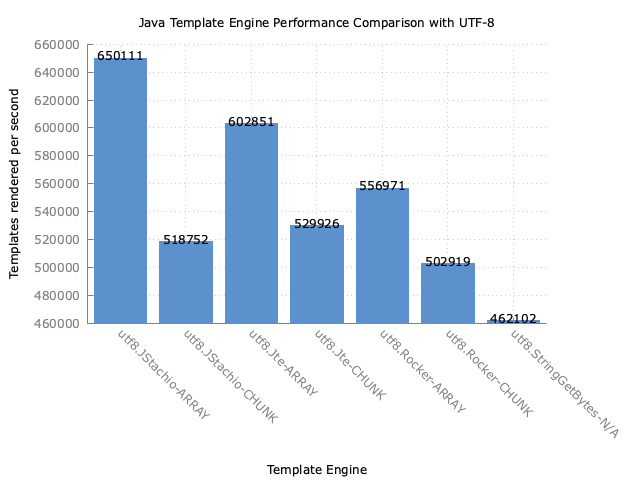 shoucheng3/jstachio__jstachio_cve-2023-33962_1-0-0
Type-safe Java Mustache templating engine with compile-time template validation, static value binding, and extensible escaping for HTML and other…