

Archived
route-sixty-sink
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
binary-analysiscode-analysisstatic-analysis+3
148
mandiant/route-sixty-sinkLink sources to sinks in C# applications.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 wireghoul/graudit
grep rough audit - source code auditing tool
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
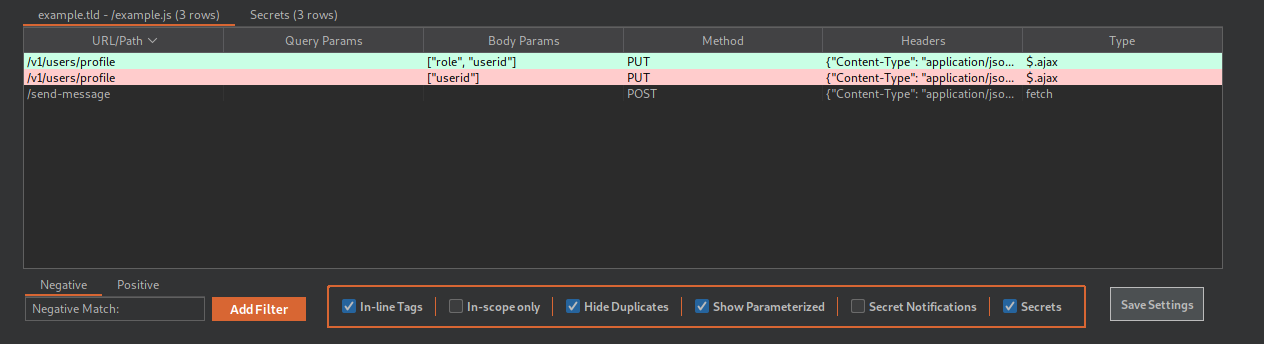 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
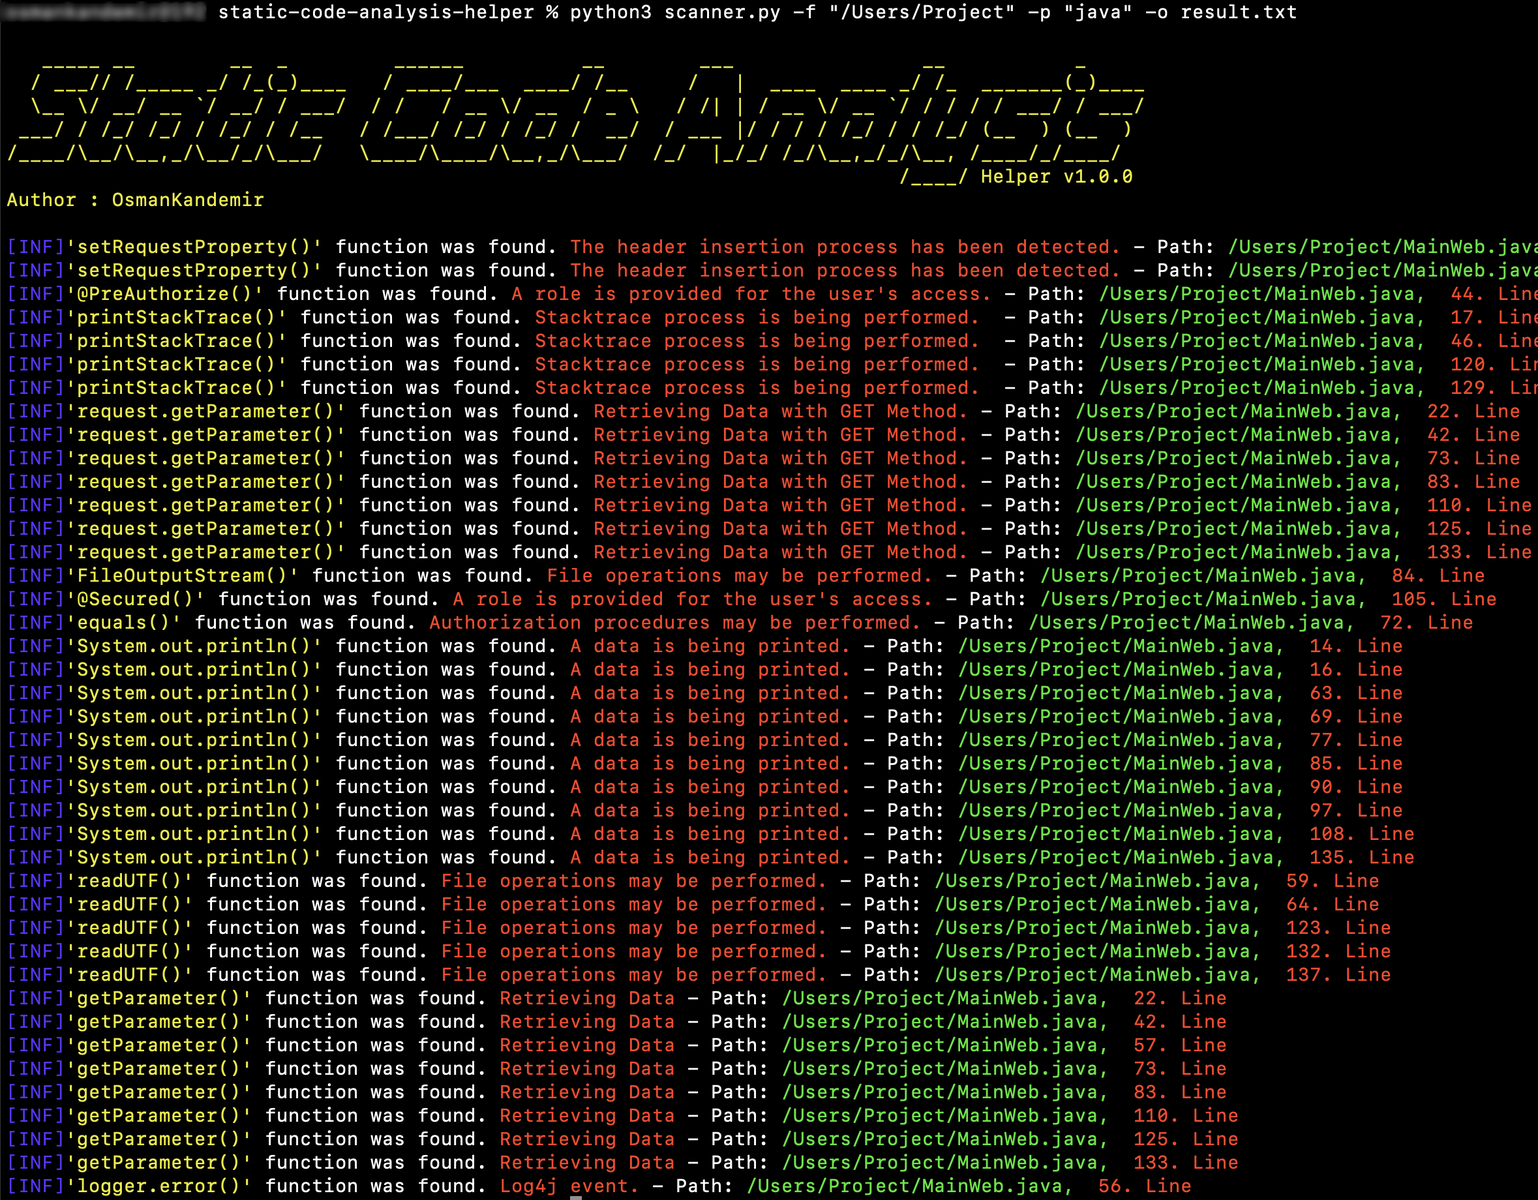 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data