

slowql
 slowql/slowql
Next-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
code-analysisconfiguration-auditingdatabase-security+6
230
slowql/slowqlNext-generation SQL static analyzer written in Rust. 282+ rules. Zero false positives. Security, performance, reliability, cost, compliance, quality.…
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 mustafabilgici/sucoshscanny
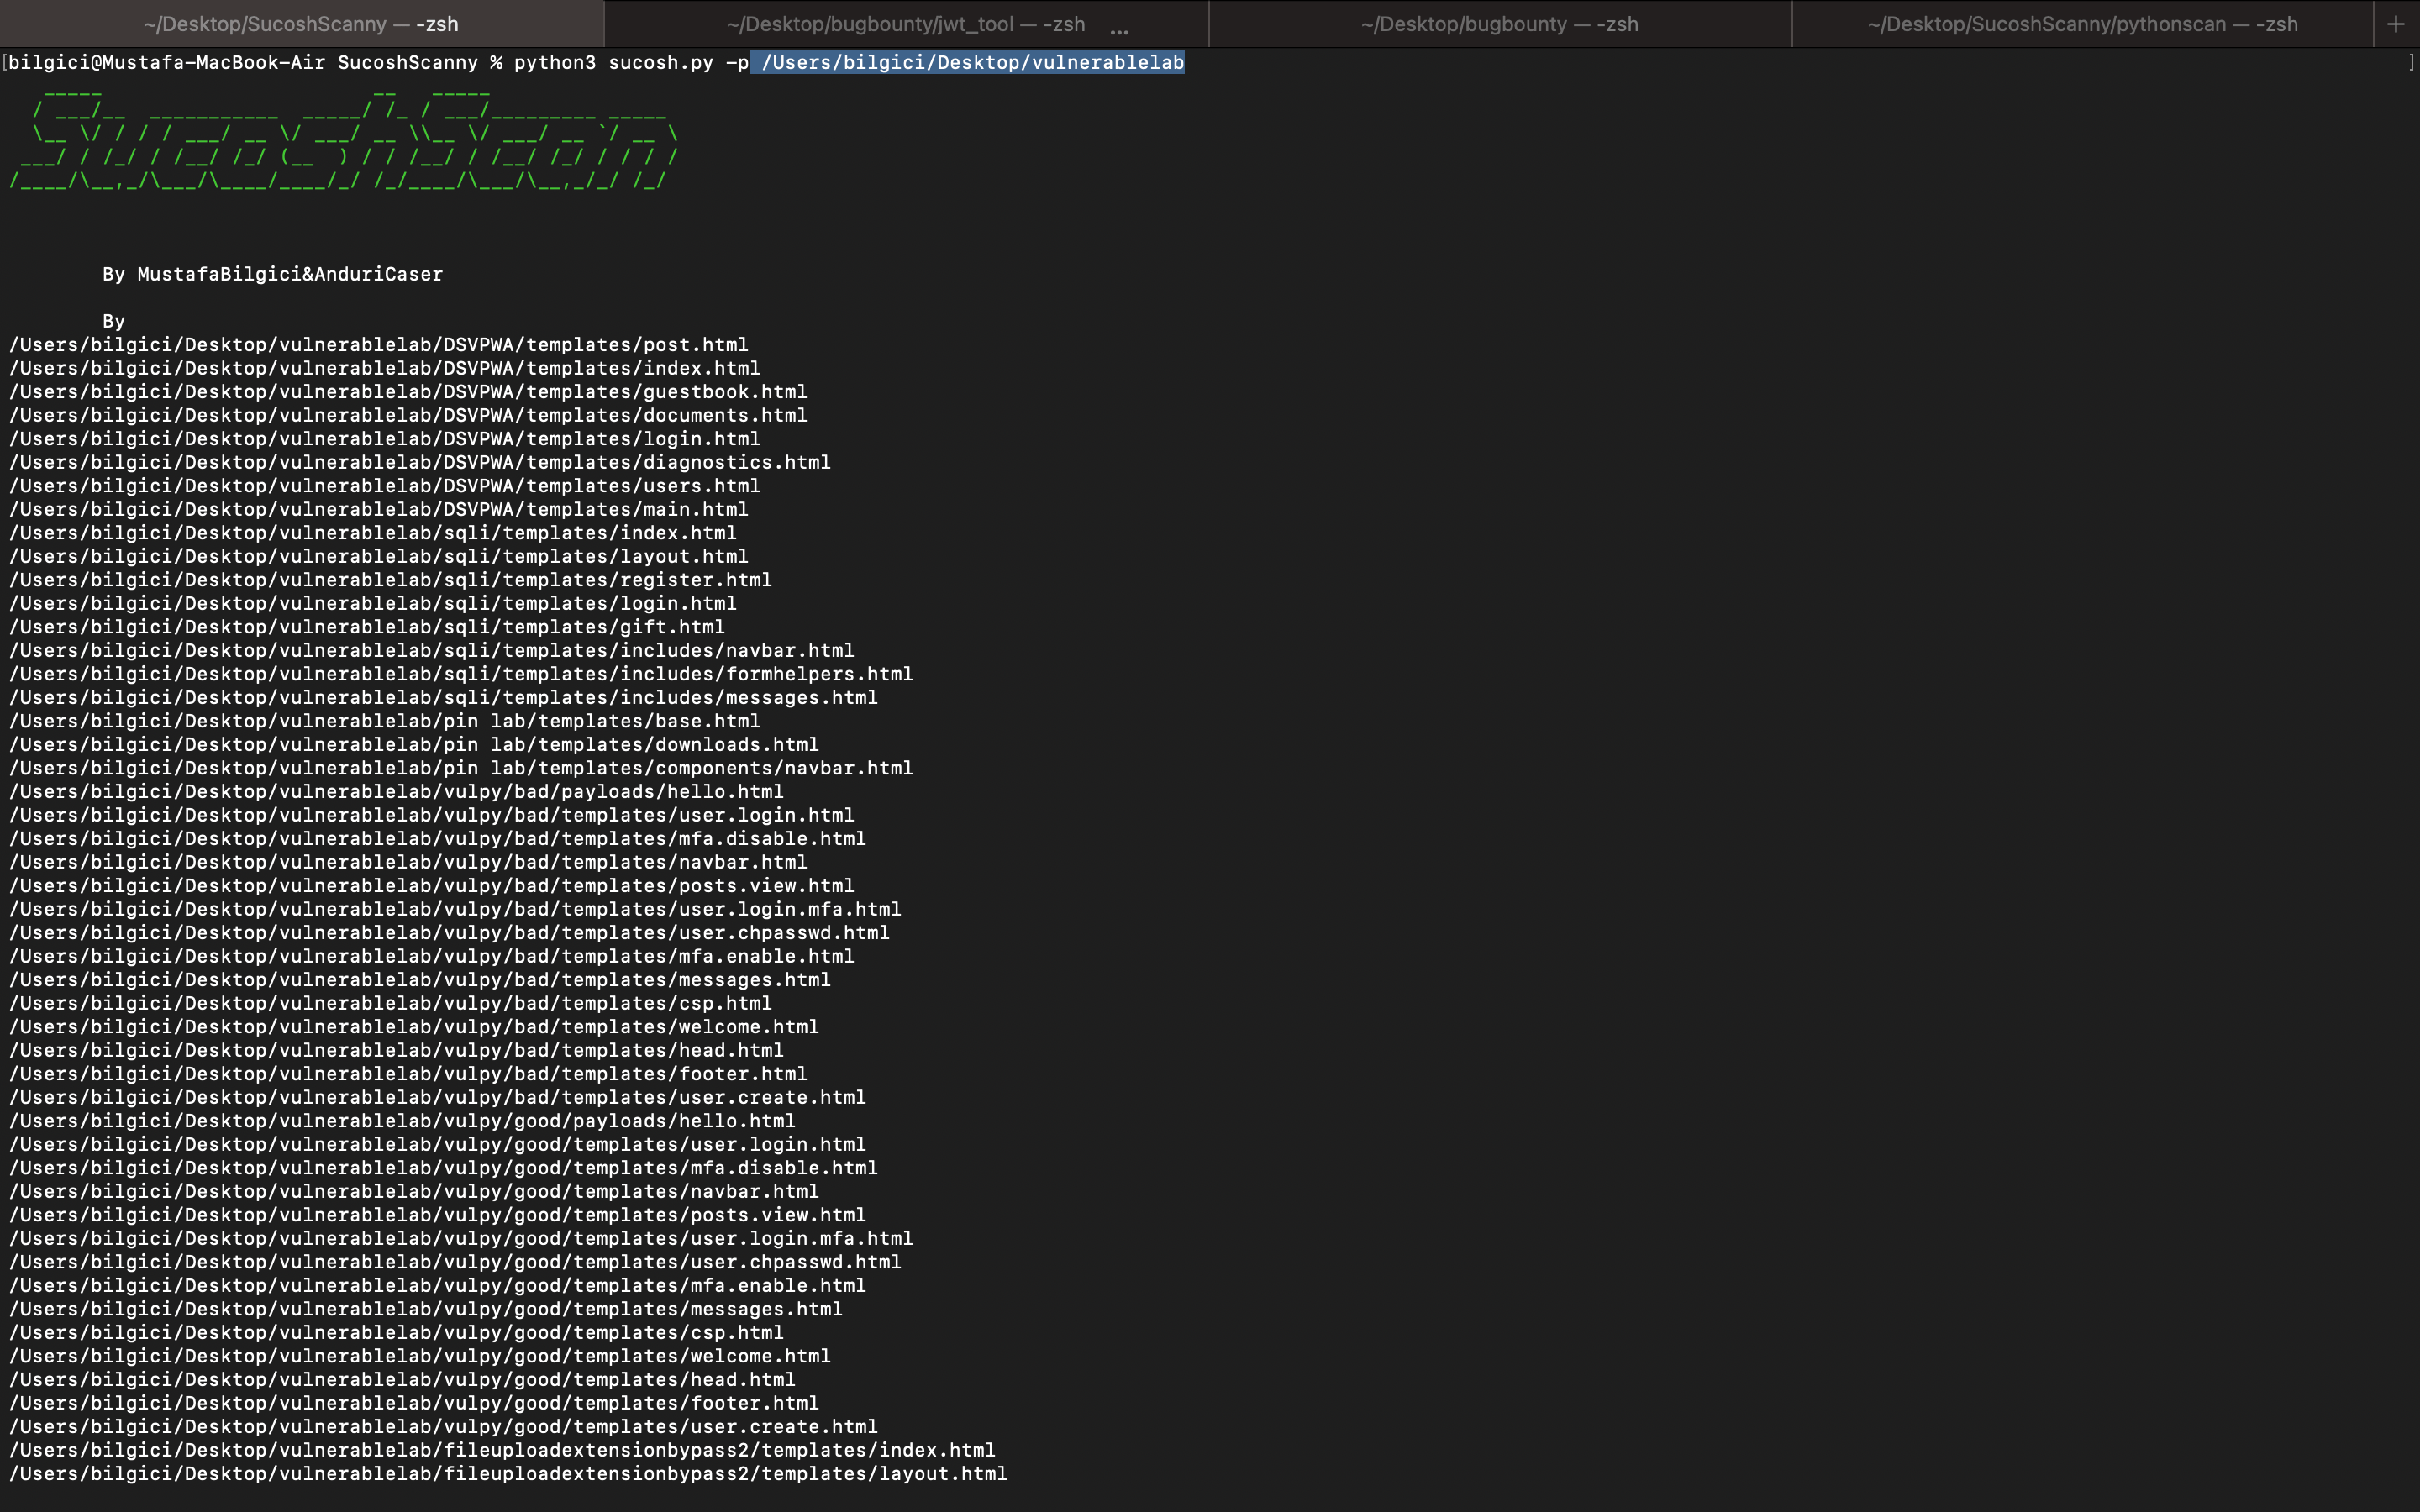
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 praetorian-inc/gokart
A static analysis tool for securing Go code
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…