
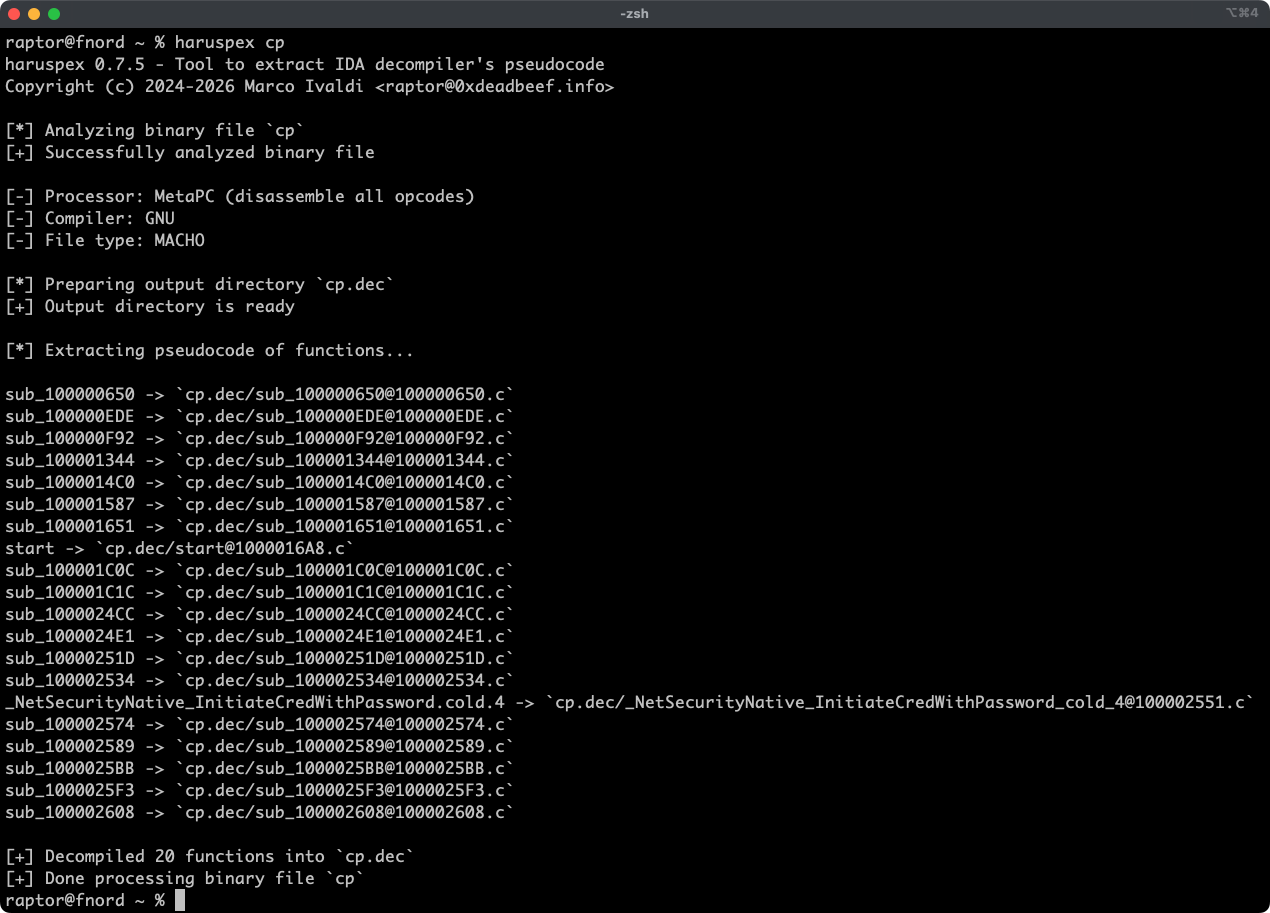
haruspex
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
binary-analysisreverse-engineeringstatic-code-analysis+1
1321 day ago
0xdea/haruspexVulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
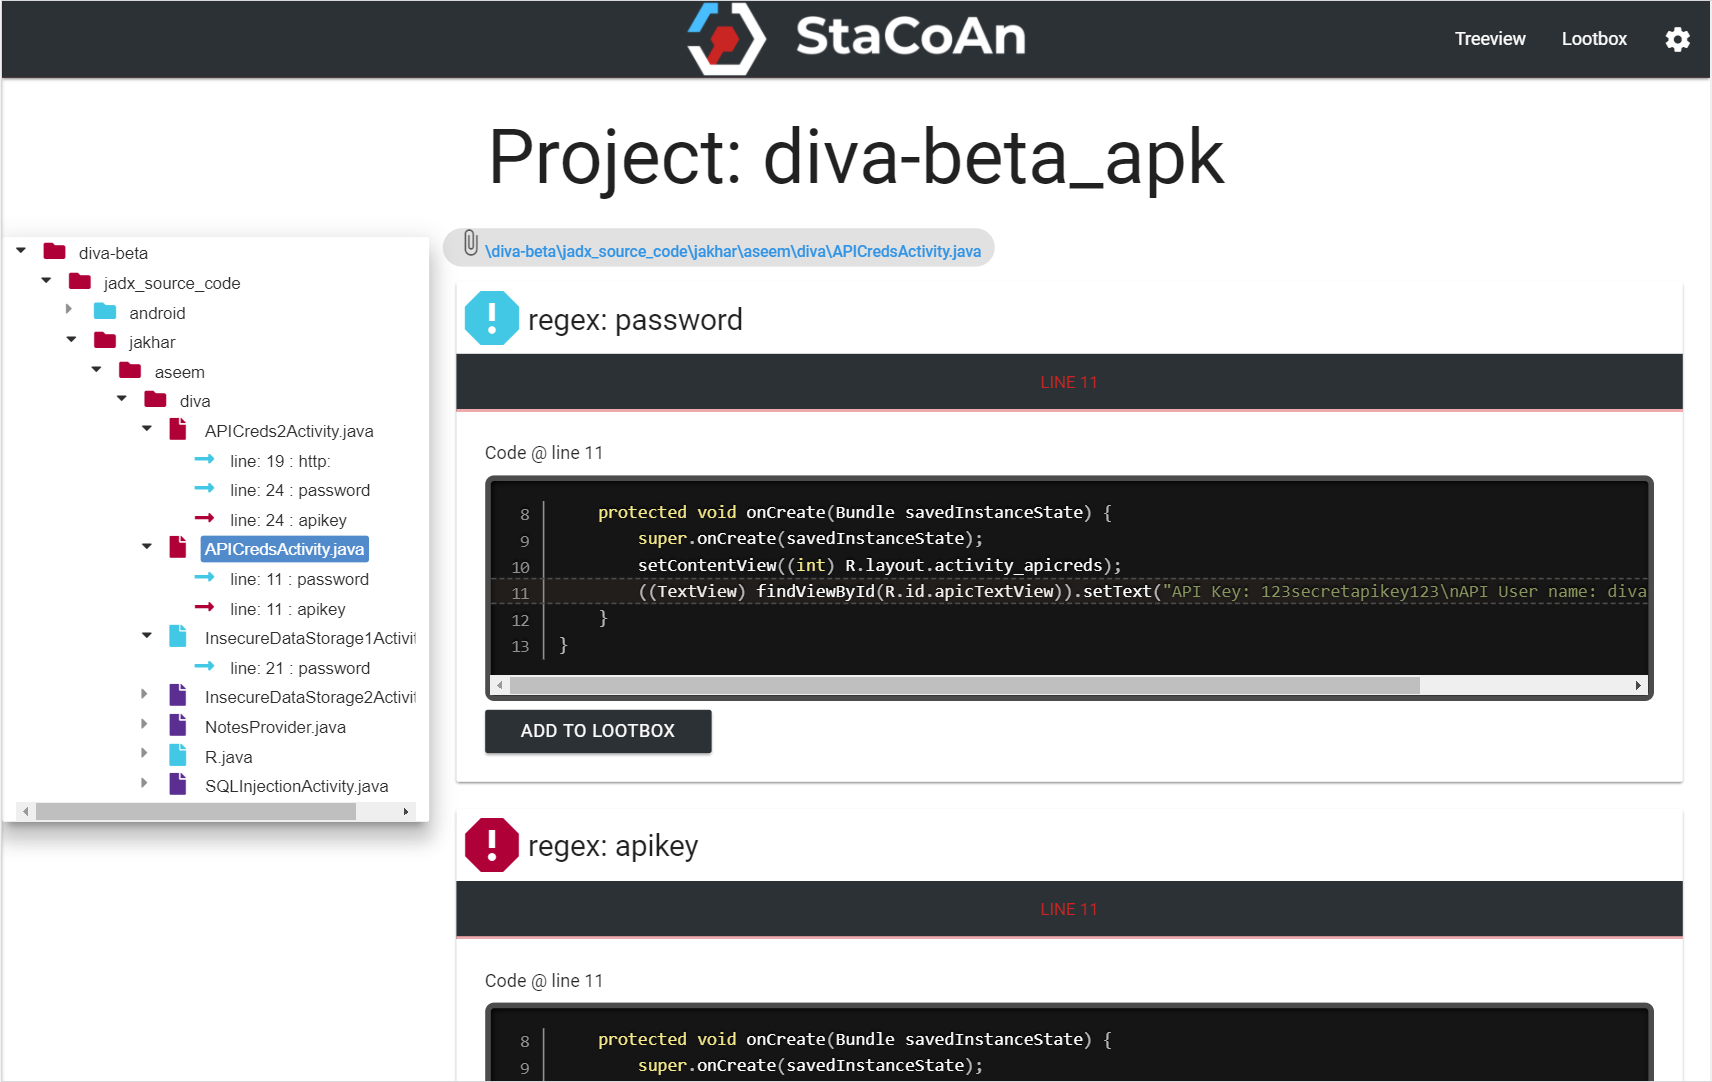 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
 0xdea/ghidra-scripts
Curated Ghidra scripts to automate reverse engineering and vulnerability analysis: locate insecure functions, extract decompiler pseudocode, fix…
 flankerhqd/jebmcp
MCP server plugin for JEB Pro that enables AI-assisted decompilation, method/field inspection, and automated renaming during APK reverse engineering.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 synacktiv/appledb_rs
Curated database of Apple internal artifacts (entitlements, frameworks, device versions) with API, CLI, and WebUI for iOS/macOS security research and…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
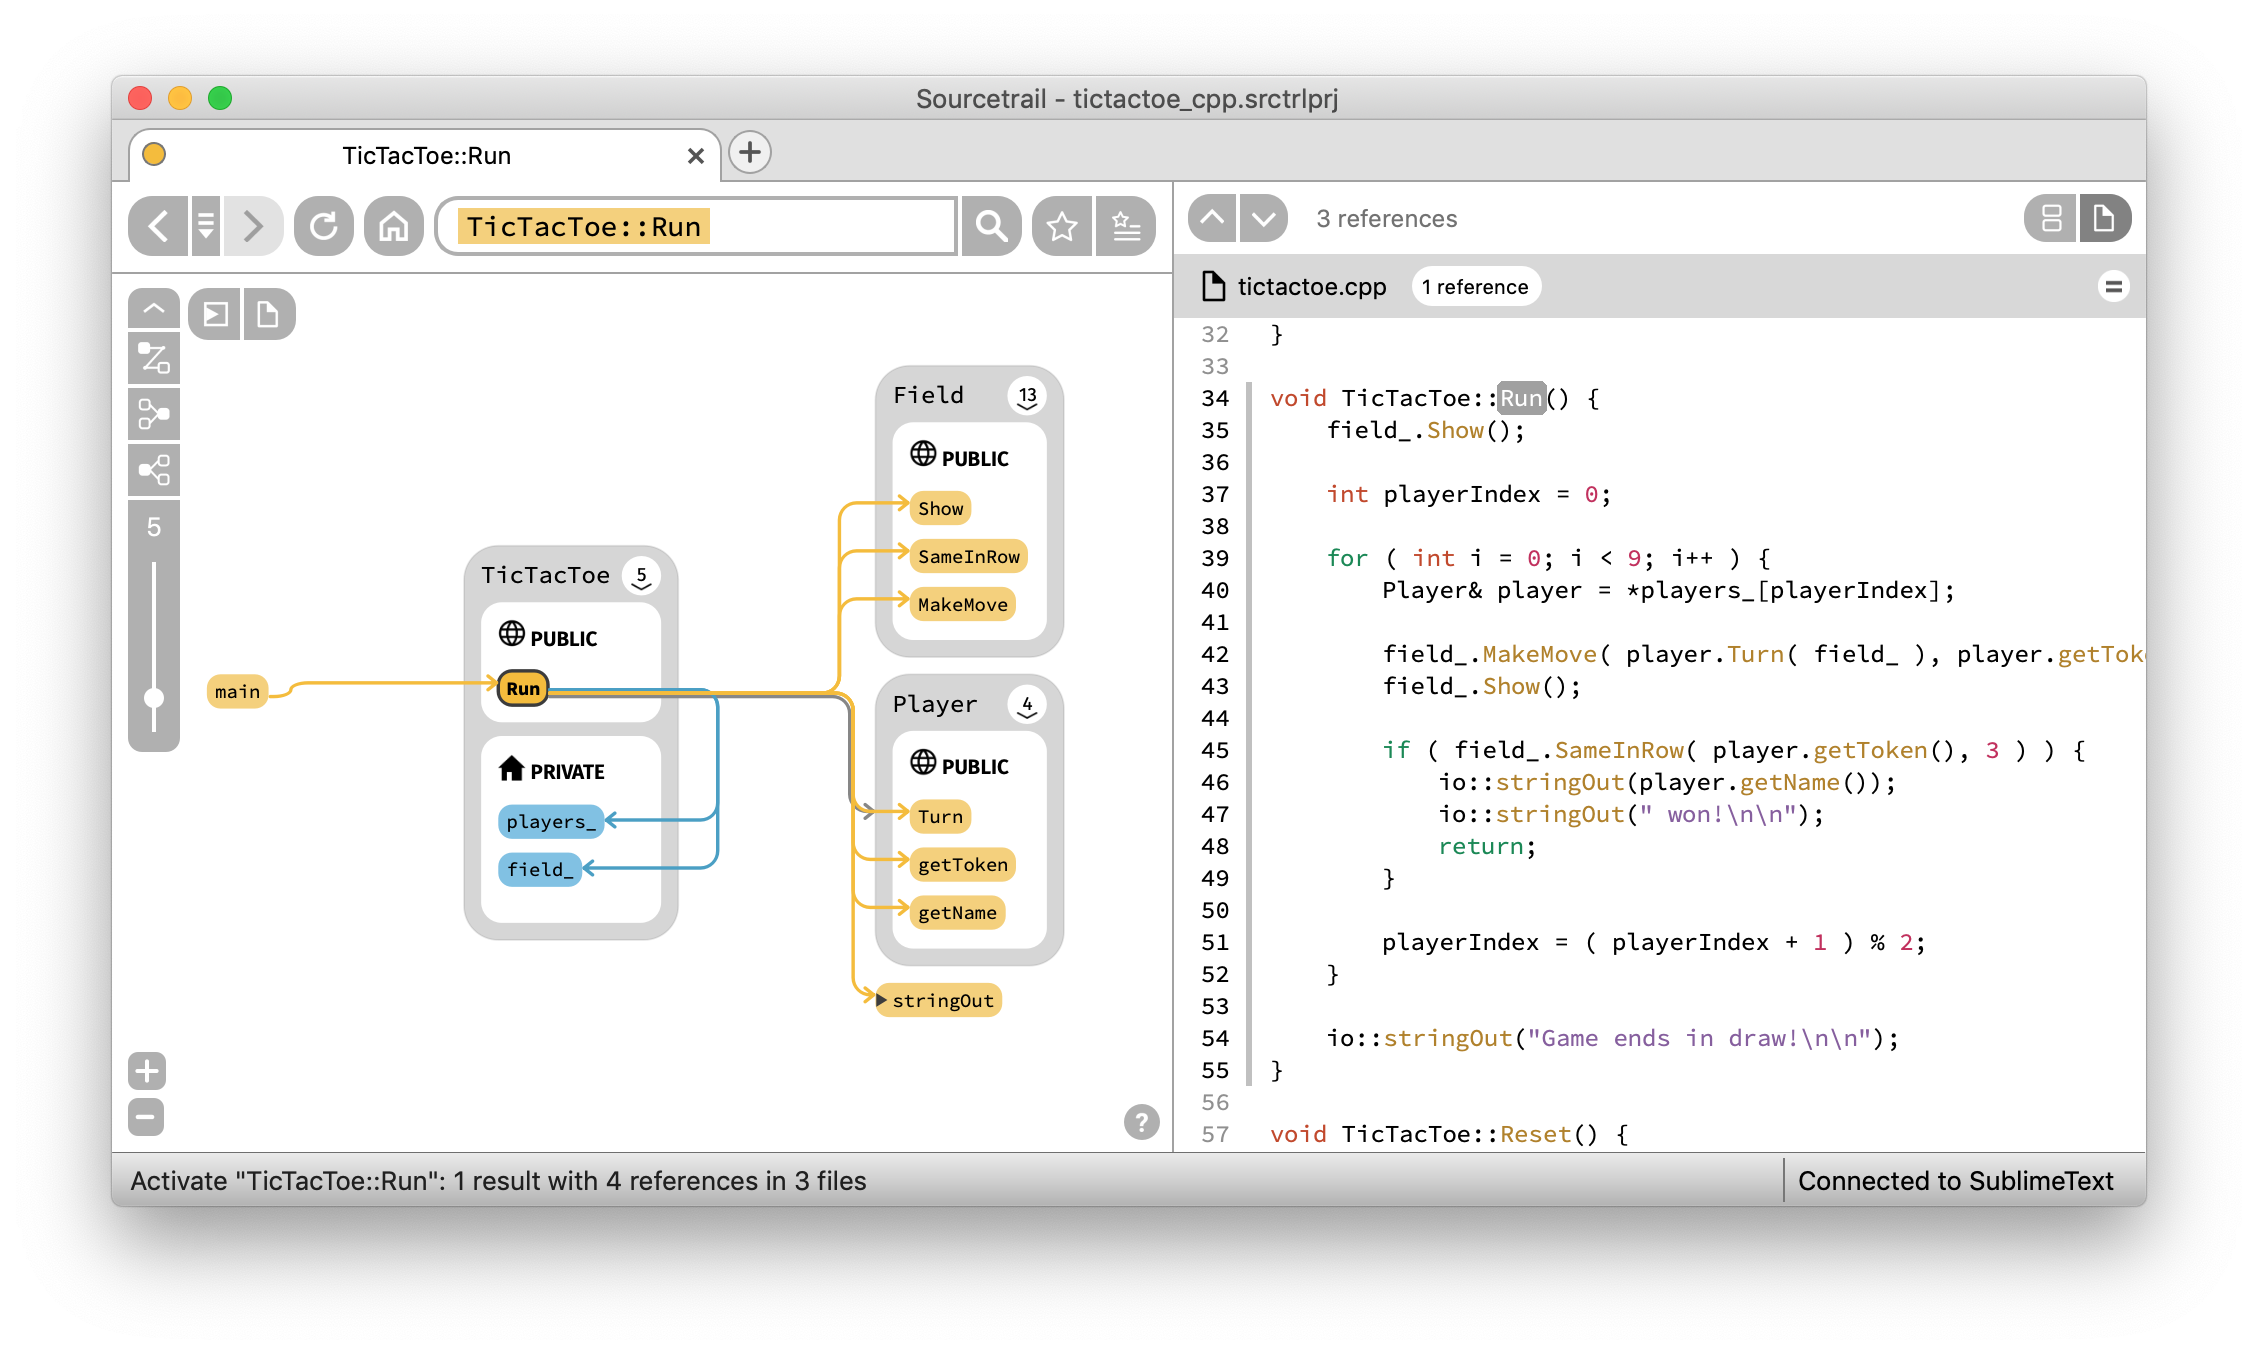 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
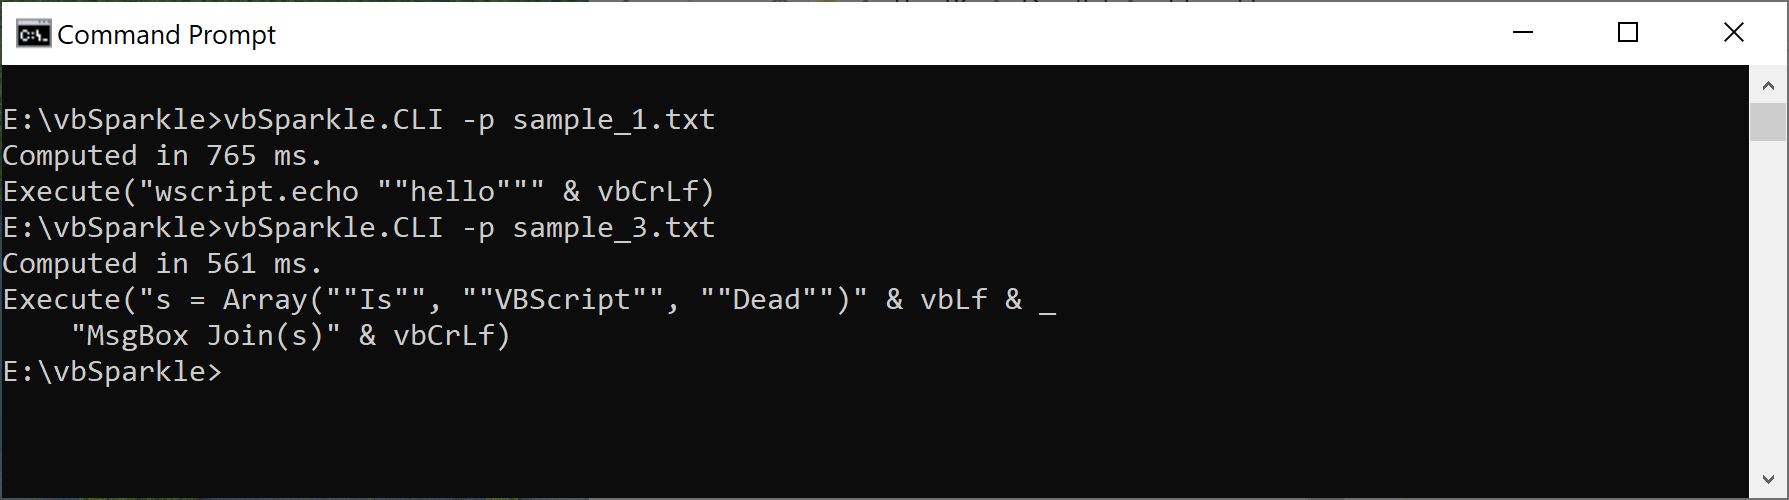 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 reverseclabs/needle
The iOS Security Testing Framework
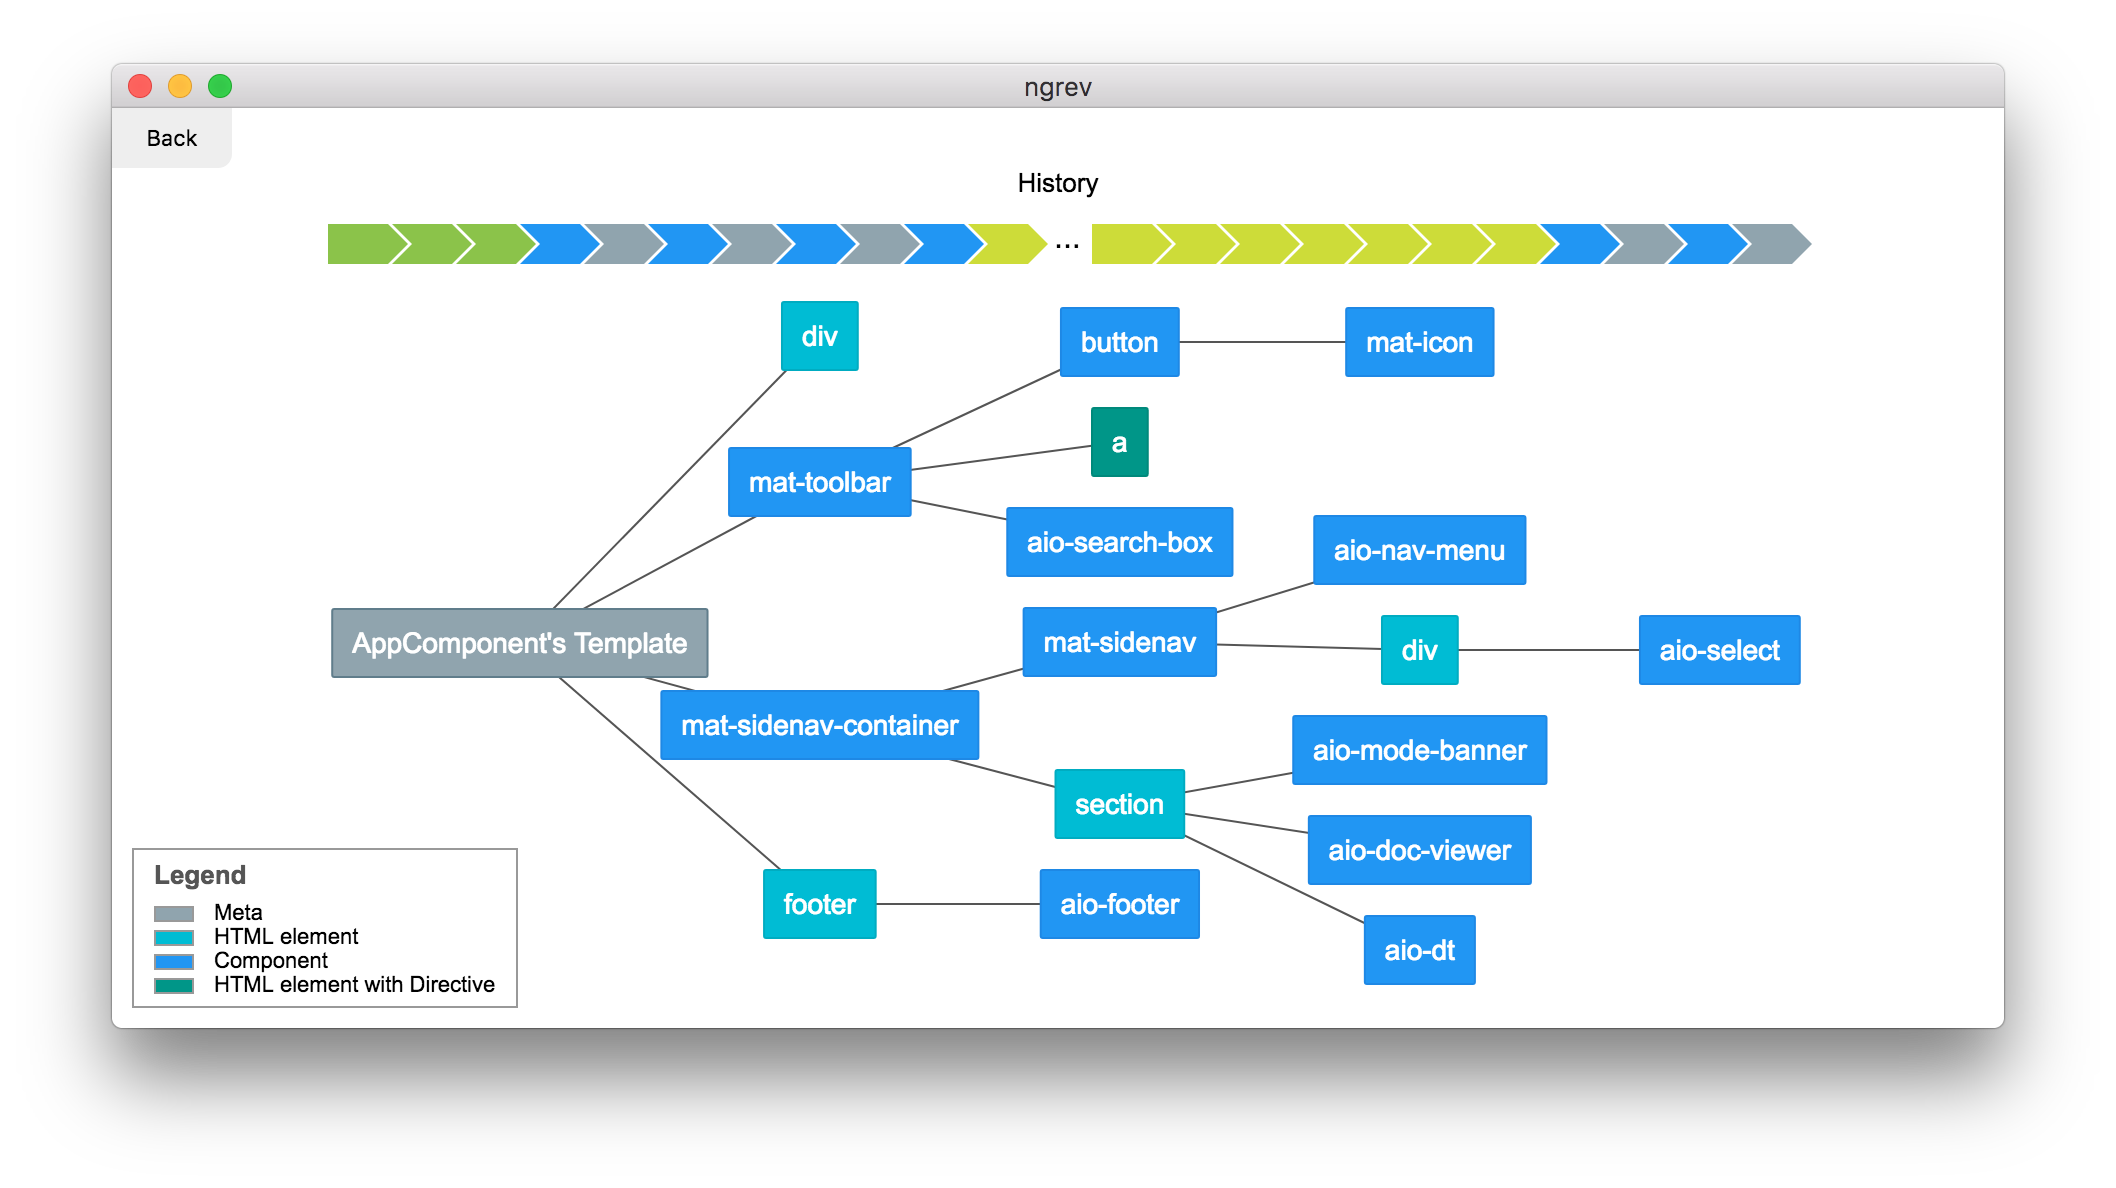 mgechev/ngrev
Tool for reverse engineering of Angular applications
 splx-ai/agentic-radar
A security scanner for your LLM agentic workflows