
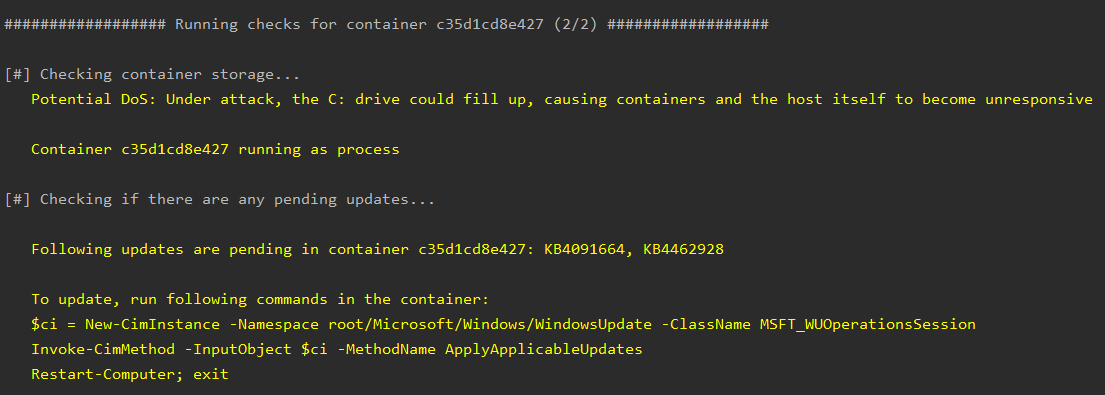
whalescan
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
container-securitydevsecopsmisconfiguration+2
155
nccgroup/whalescanWhalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
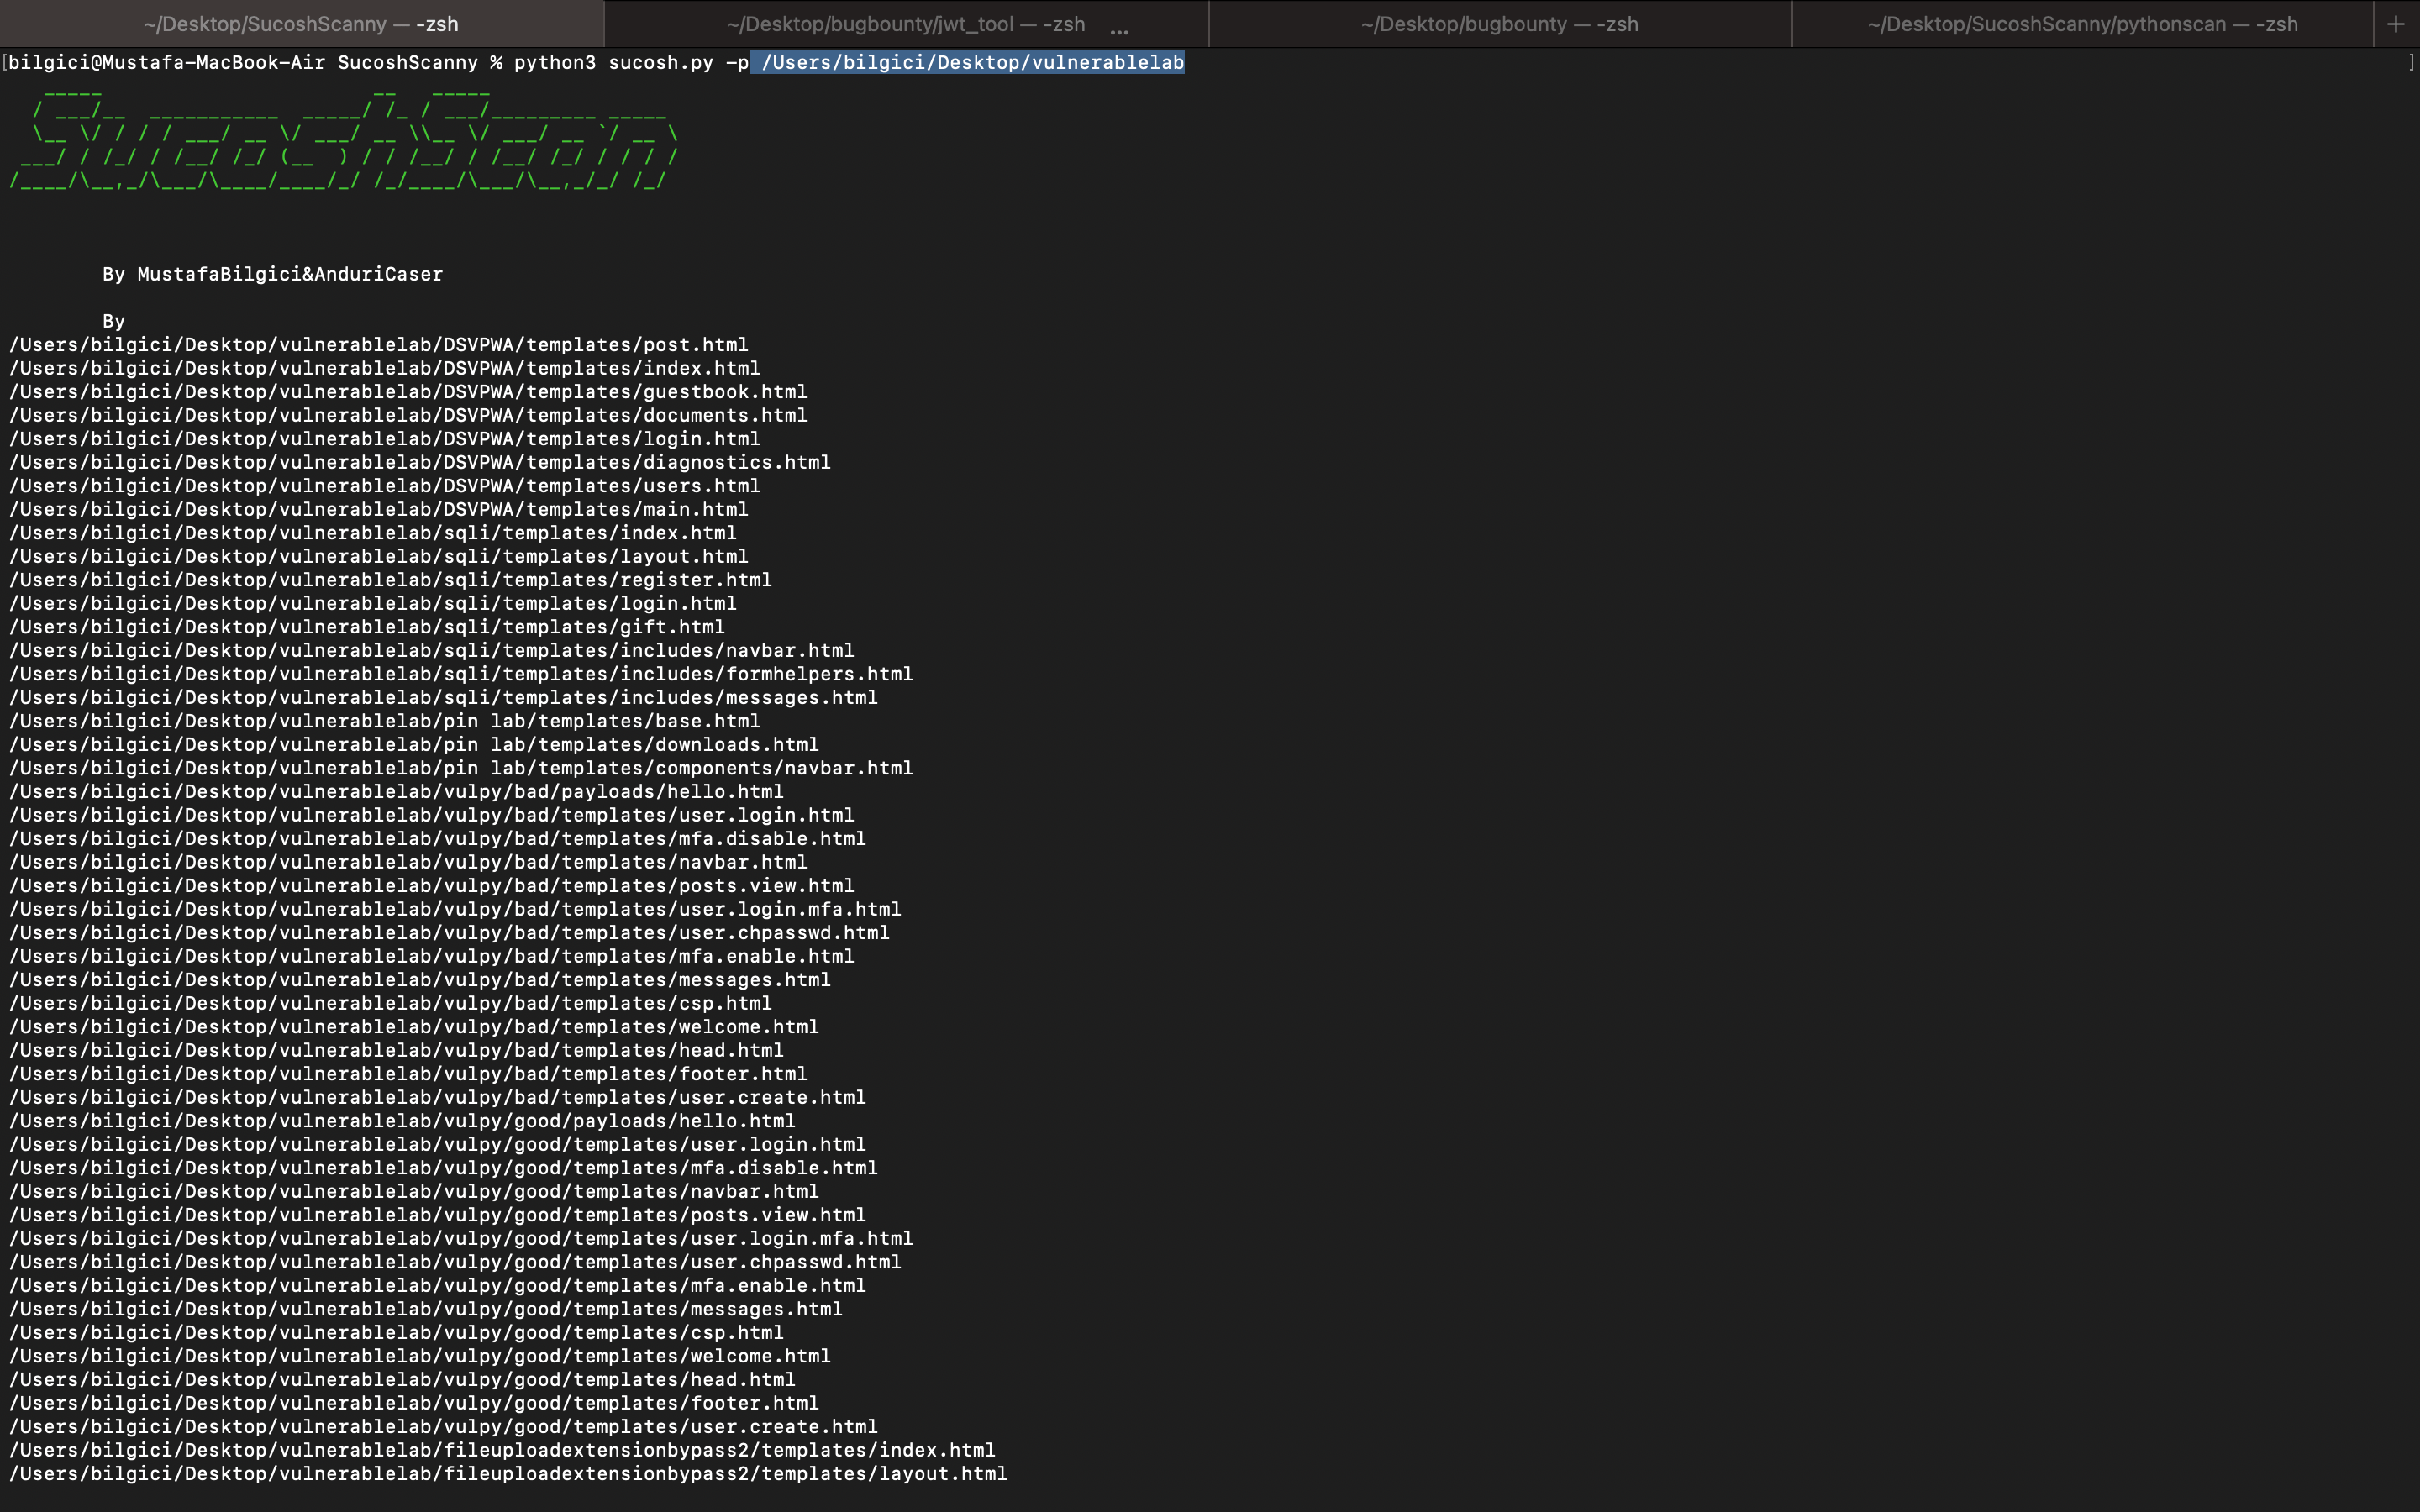 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
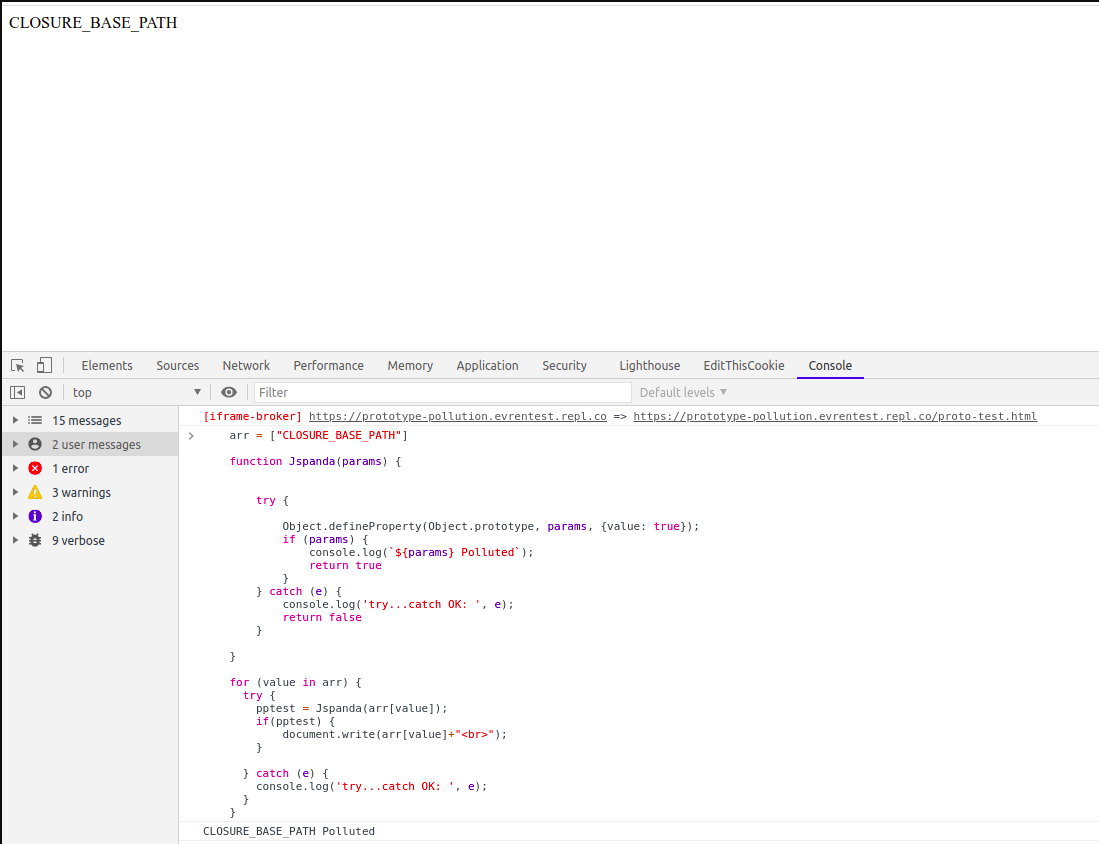 redsection/jspanda
client-side prototype pullution vulnerability scanner
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
 advanced-threat-research/creosote
Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
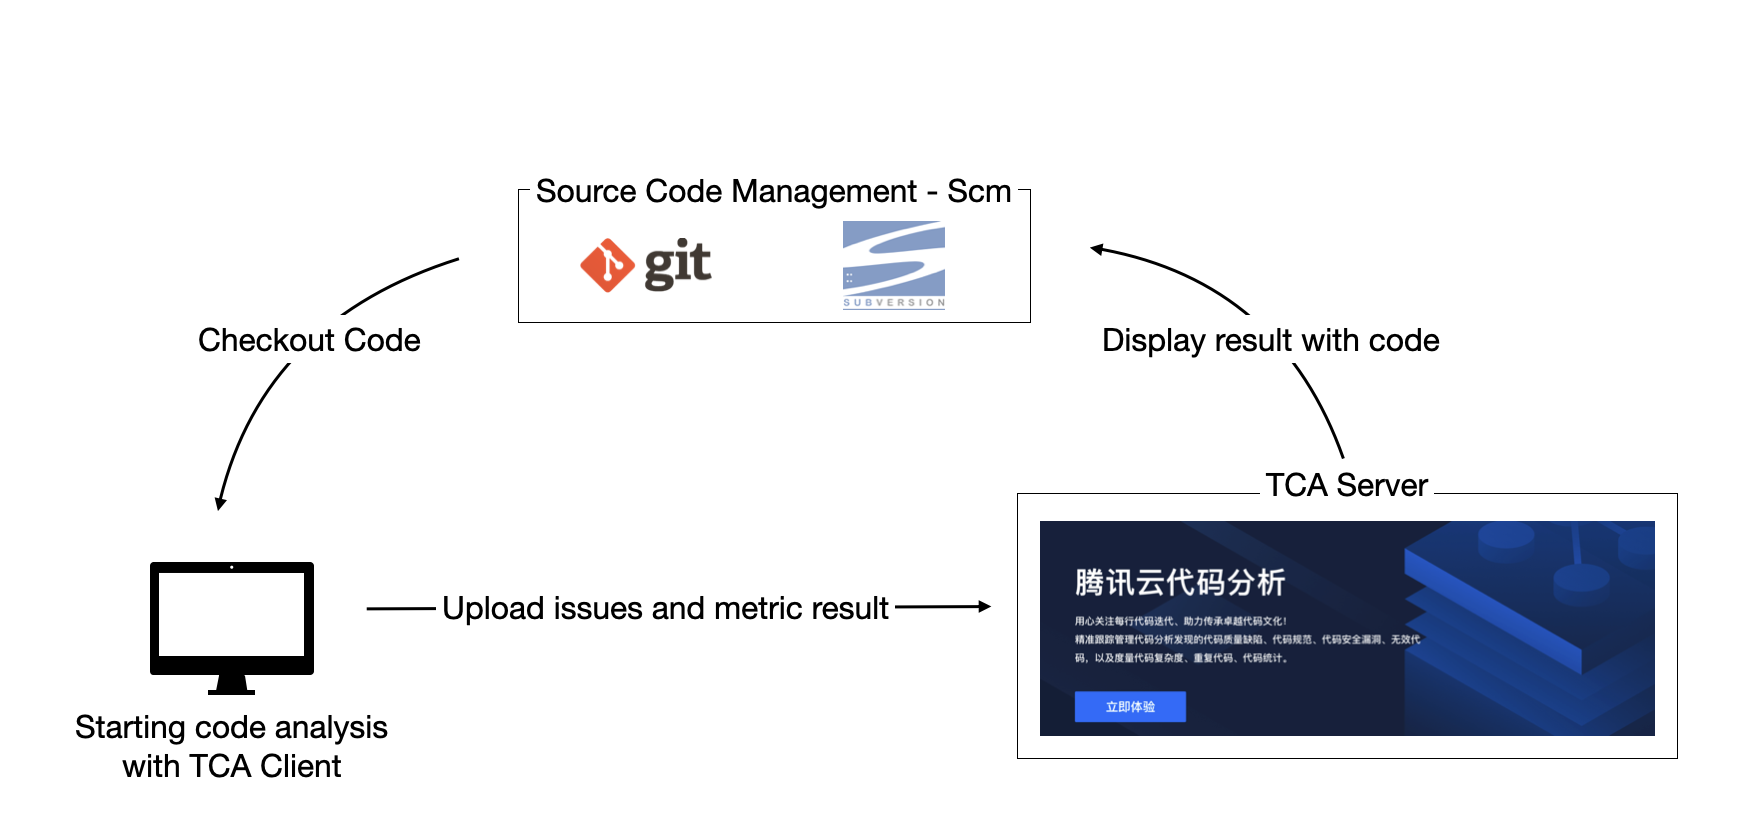 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…