

regexploit
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
fuzzingstatic-code-analysisvulnerability-analysis
doyensec/regexploitFind regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)

 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
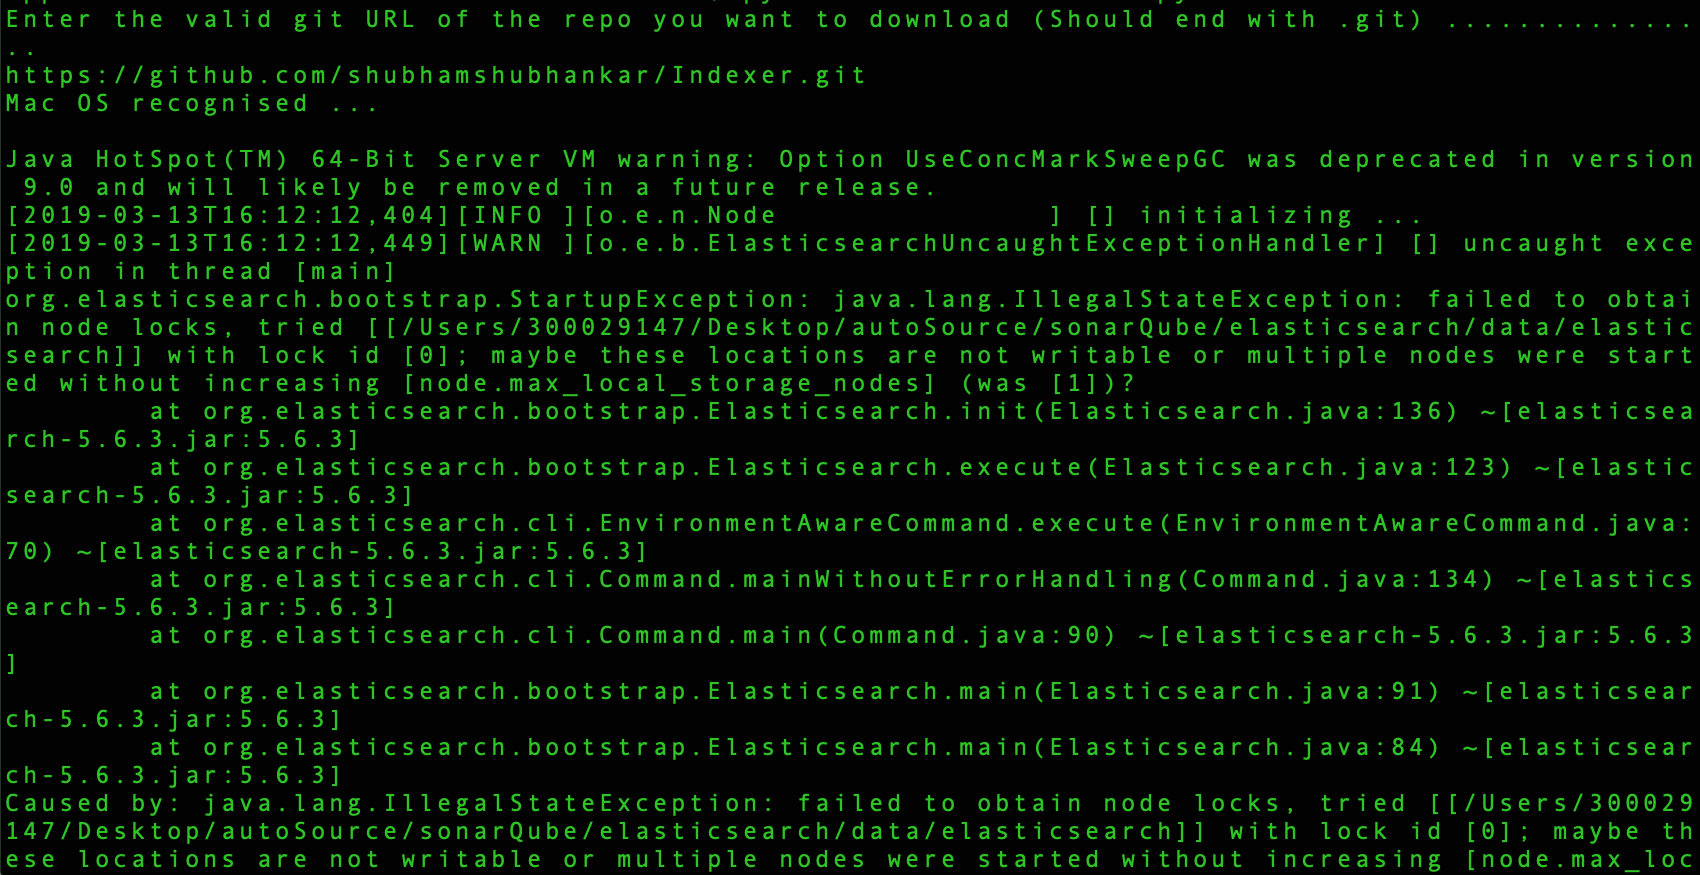 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…
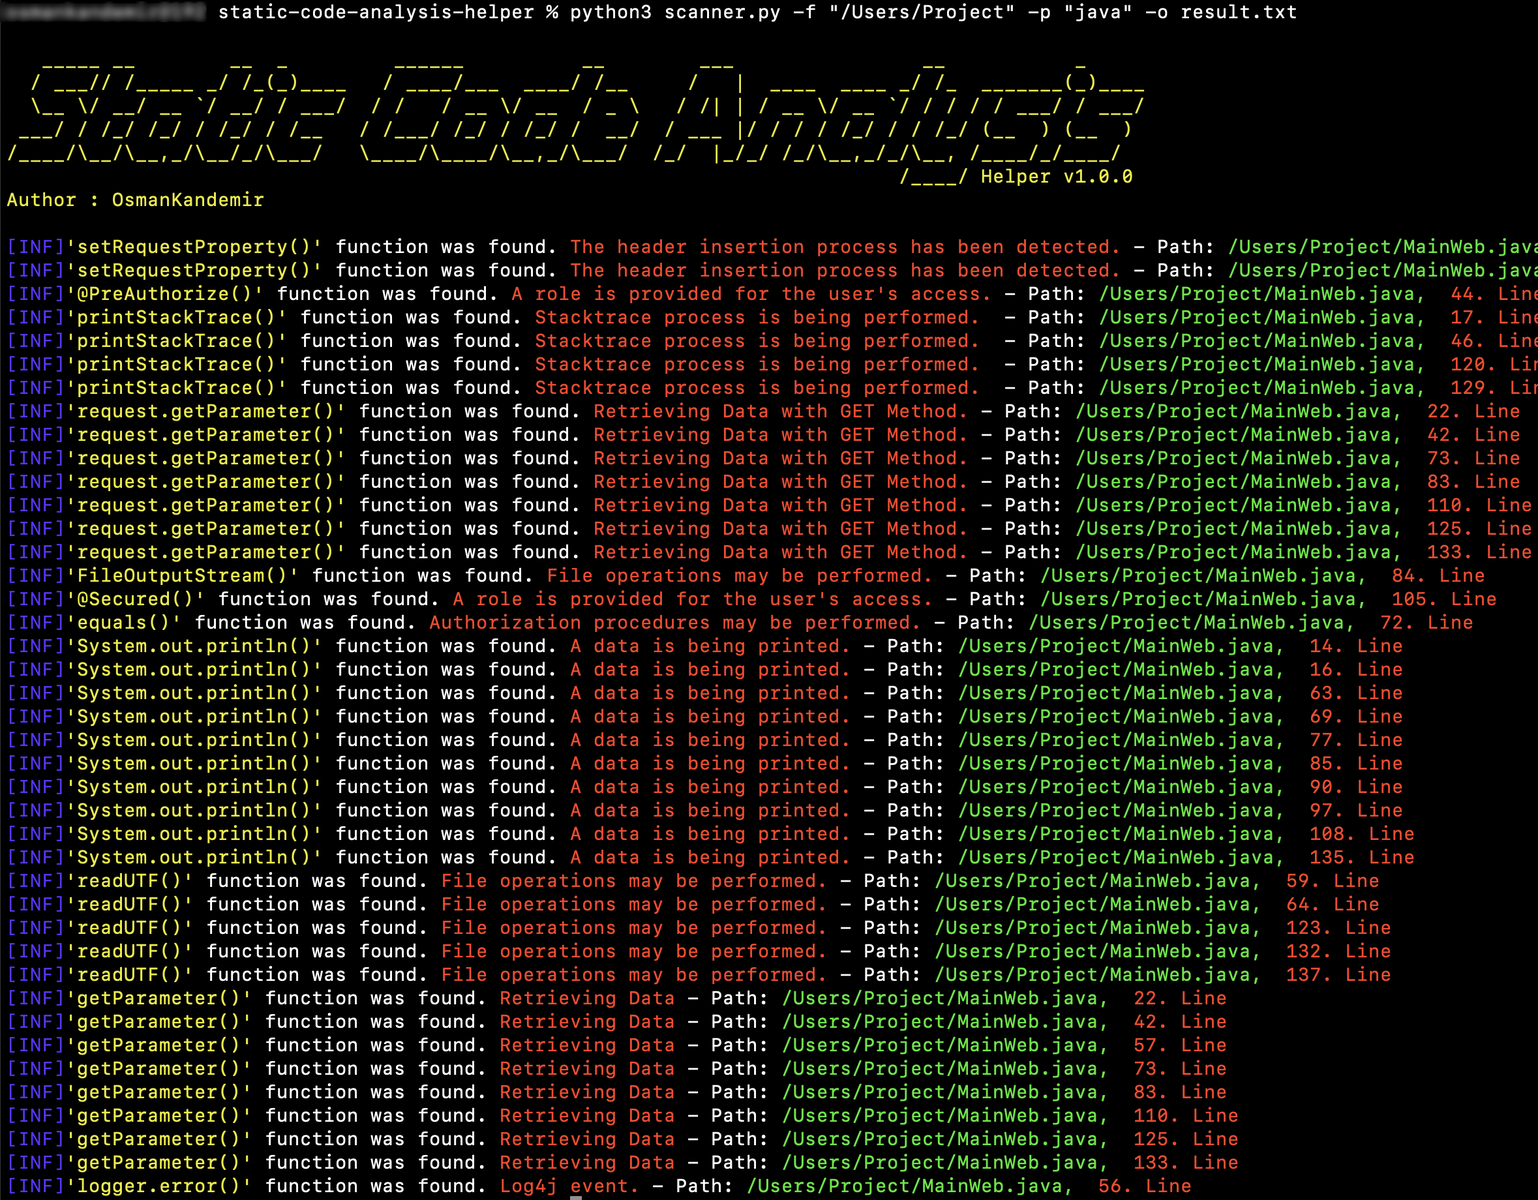 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 rvermeulen/codeql-cve-2022-35737
A CodeQL query to find CVE 2022-35737
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 s0md3v/hardcodes
find hardcoded strings from source code
 wireghoul/graudit
grep rough audit - source code auditing tool
 0x3c3e/slides
CodeQL + DTrace = Memory Disclosure Vulnerabilities in XNU
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security