

bandit
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
code-analysisstatic-code-analysisvulnerability-analysis
pycqa/banditBandit is a tool designed to find common security issues in Python code.
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
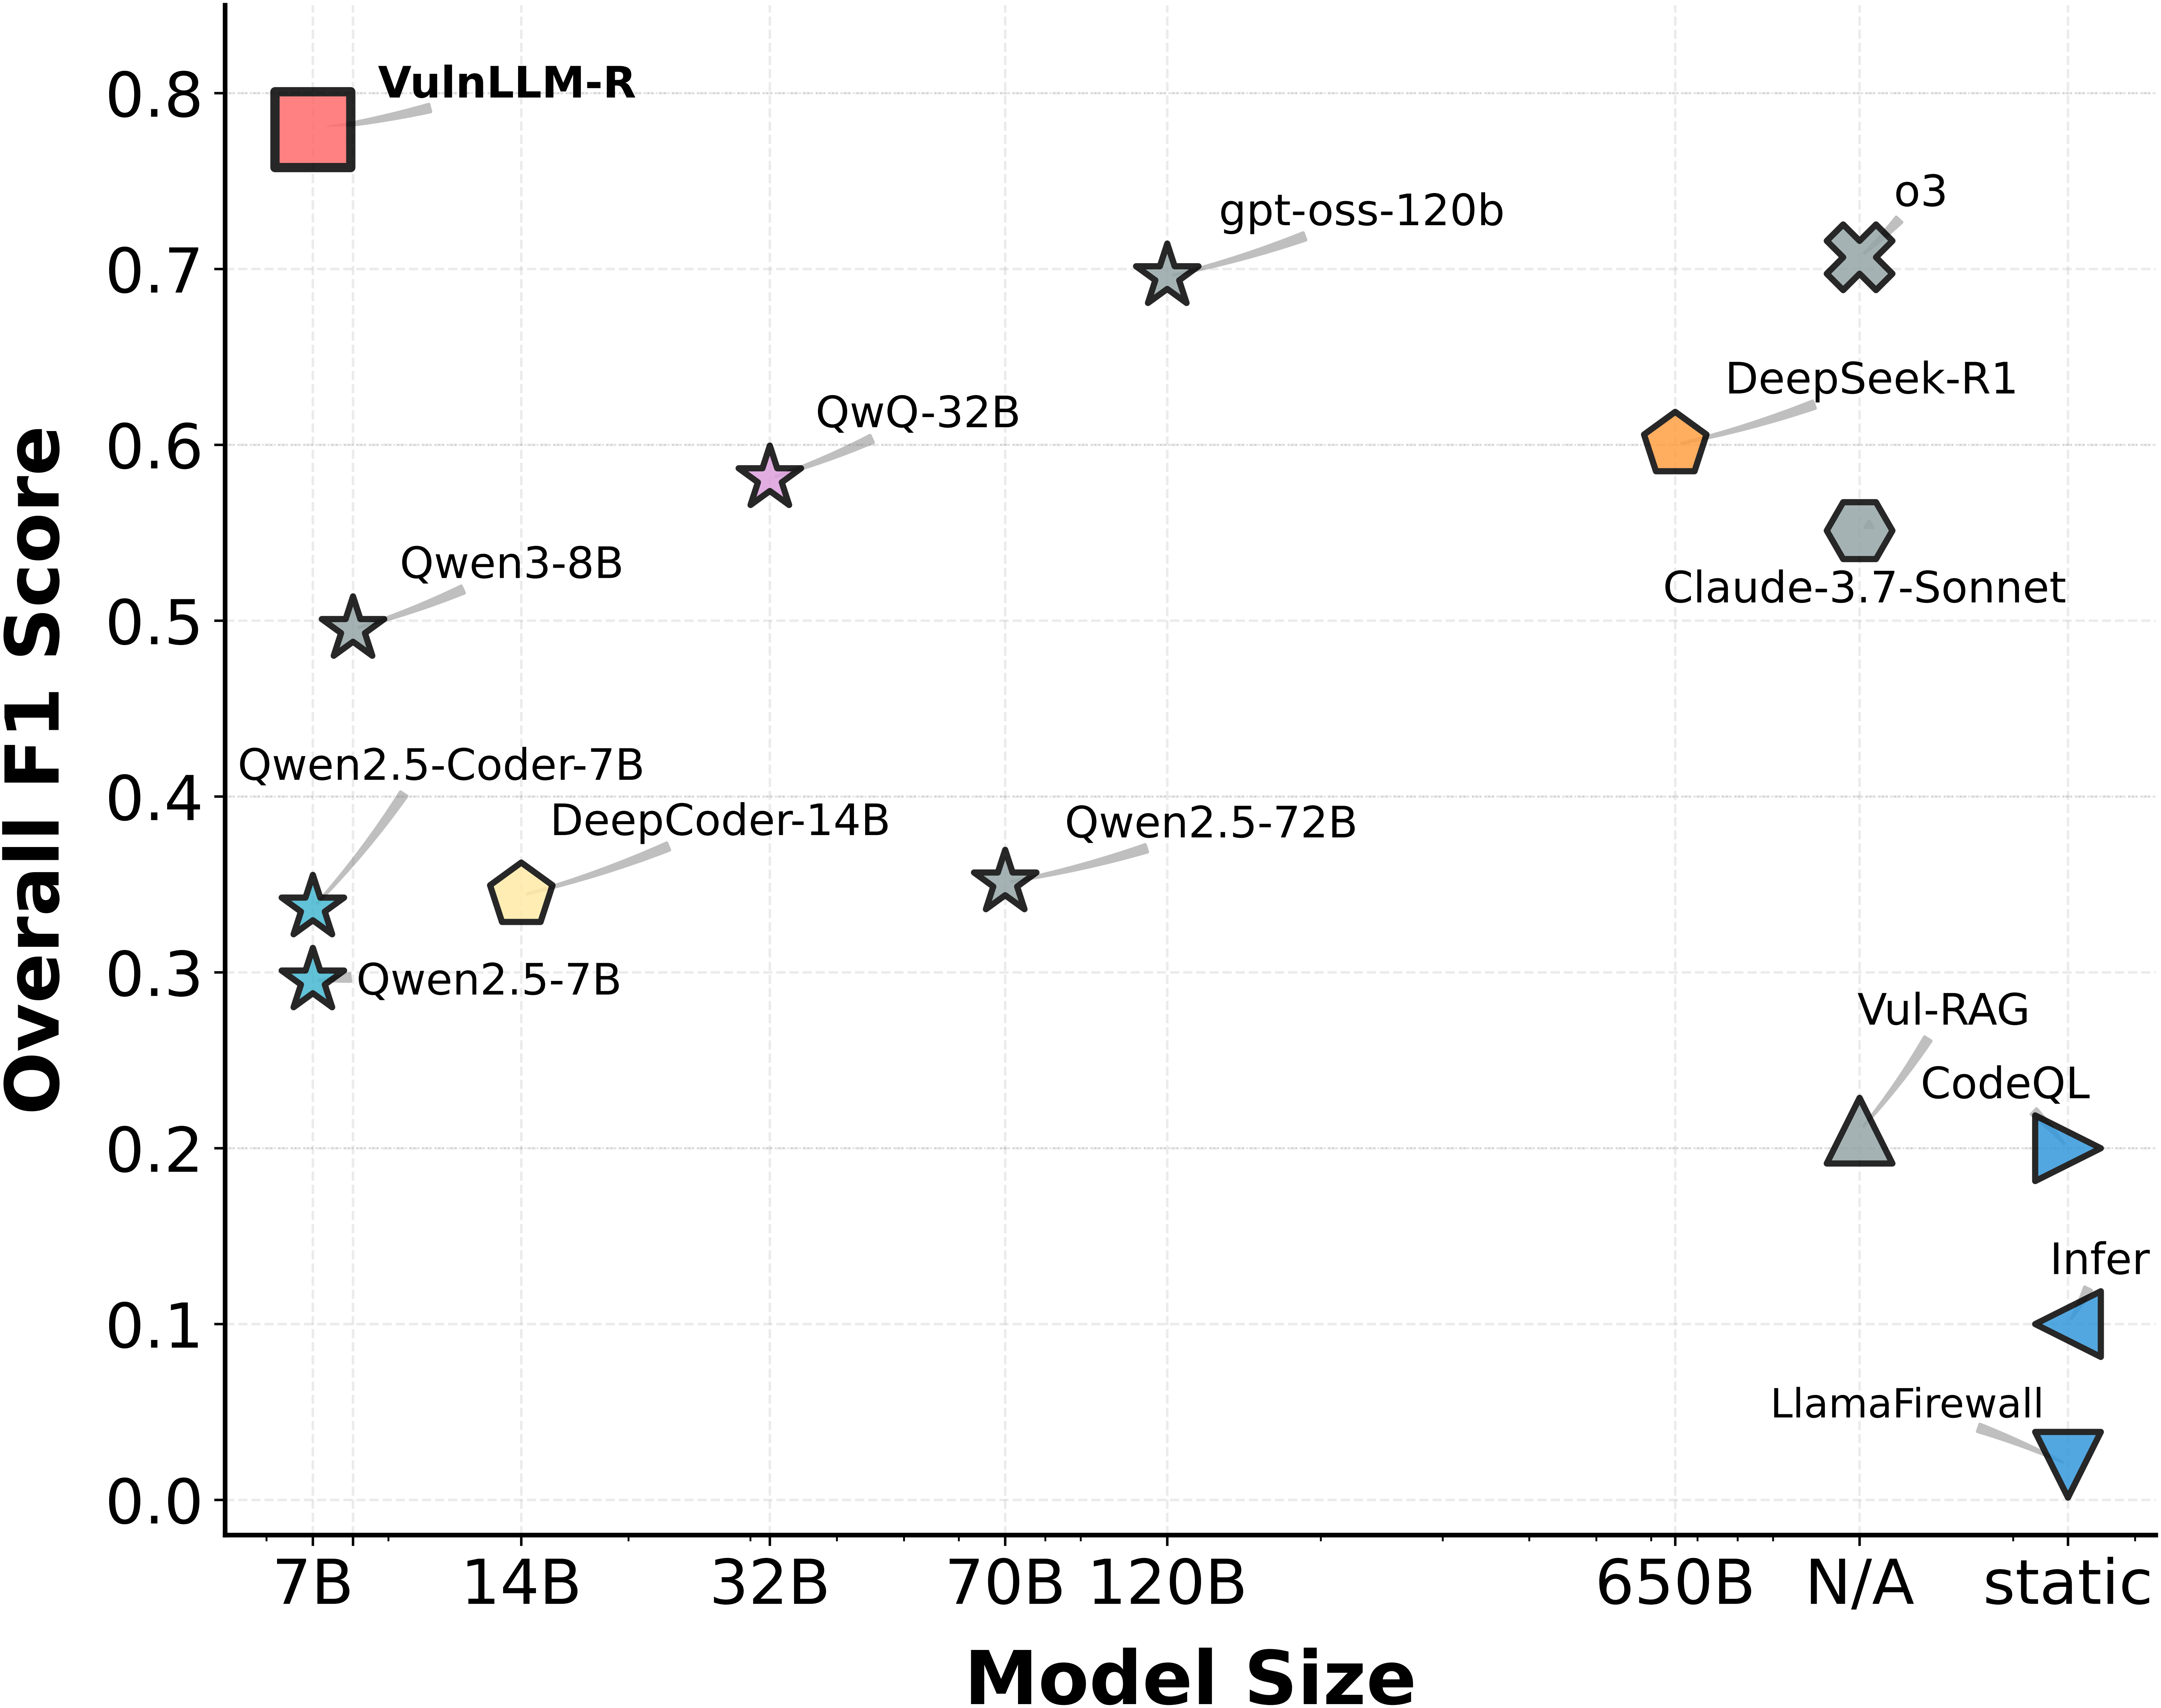 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 minhhk68/cve-2026-13158
Proof-of-concept exploit and technical advisory for an Admin+ arbitrary file upload to remote code execution vulnerability in Everest Toolkit…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
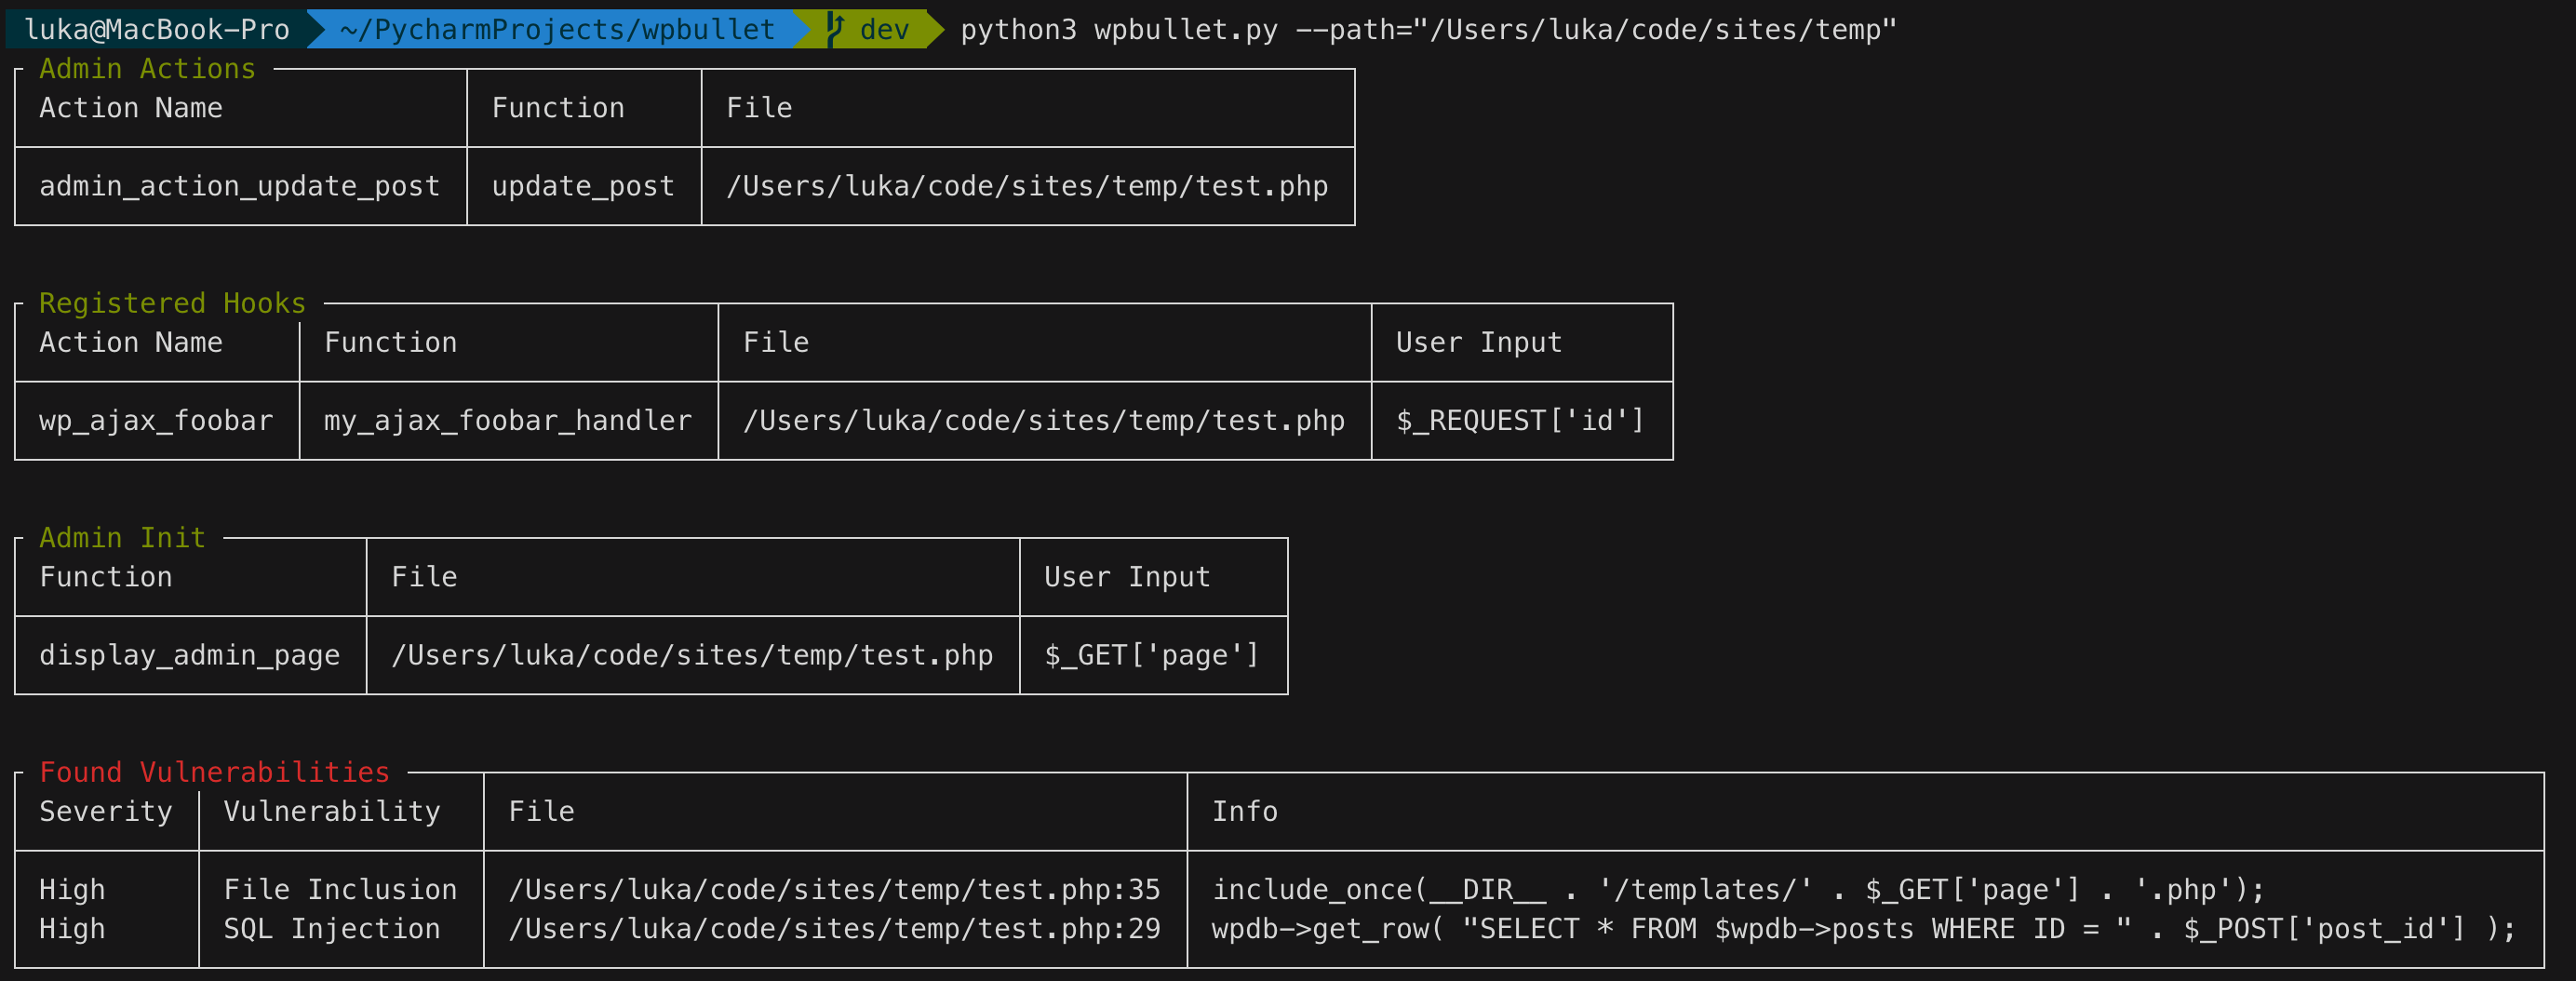 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)