
sast-rules
 gitlab-org/security-products/sast-rules
Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…
code-analysisdevsecopseducation+2
29
gitlab-org/security-products/sast-rulesCurated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…
 redsection/jspanda
client-side prototype pullution vulnerability scanner
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
 tai-e/cve-2021-44228
Utilize Tai-e to identify the Log4shell (a.k.a. CVE-2021-44228) Vulnerability
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
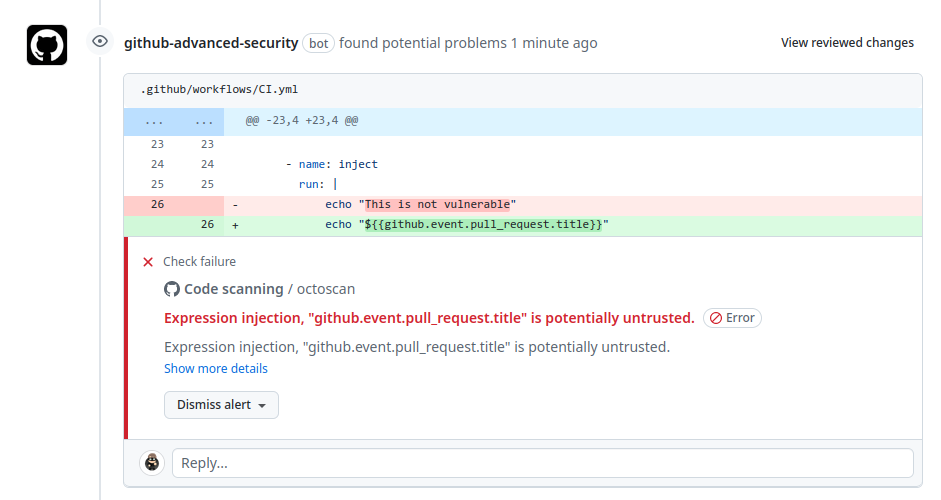 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.
 nccgroup/matt.net
Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool
 xiaoqimikko/jackson-check
jackson-databind + jackson-core 26 条安全公告自查:按坐标逐条求交集给出真正到位的版本(2.18.11/2.21.7/2.22.3/3.1.7/3.2.3,2.21.6 已不够);扫源码降噪告诉你真中几条;含 1 条 GitHub…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 abraxas/drupal-move-block-markup
Drupal 11.4.8 - High - Remote - XSS - Move Block sibling labels skip @label escaping
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography
 thrilokh-q123/cve-2025-23134_fixes_code
The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().
 ockeghem/cve-2015-6835-checker
PHP script to detect CVE-2015-6835 (session deserialization vulnerability) by analyzing source code for unsafe unserialize() calls in session…
 anna-kravets/codeql-buffer-overflow-variant
Synthetic CWE-120 stack buffer overflow variant of CVE-2020-8597 (pppd EAP) as a CodeQL static-analysis target