static-code-analysis-helper

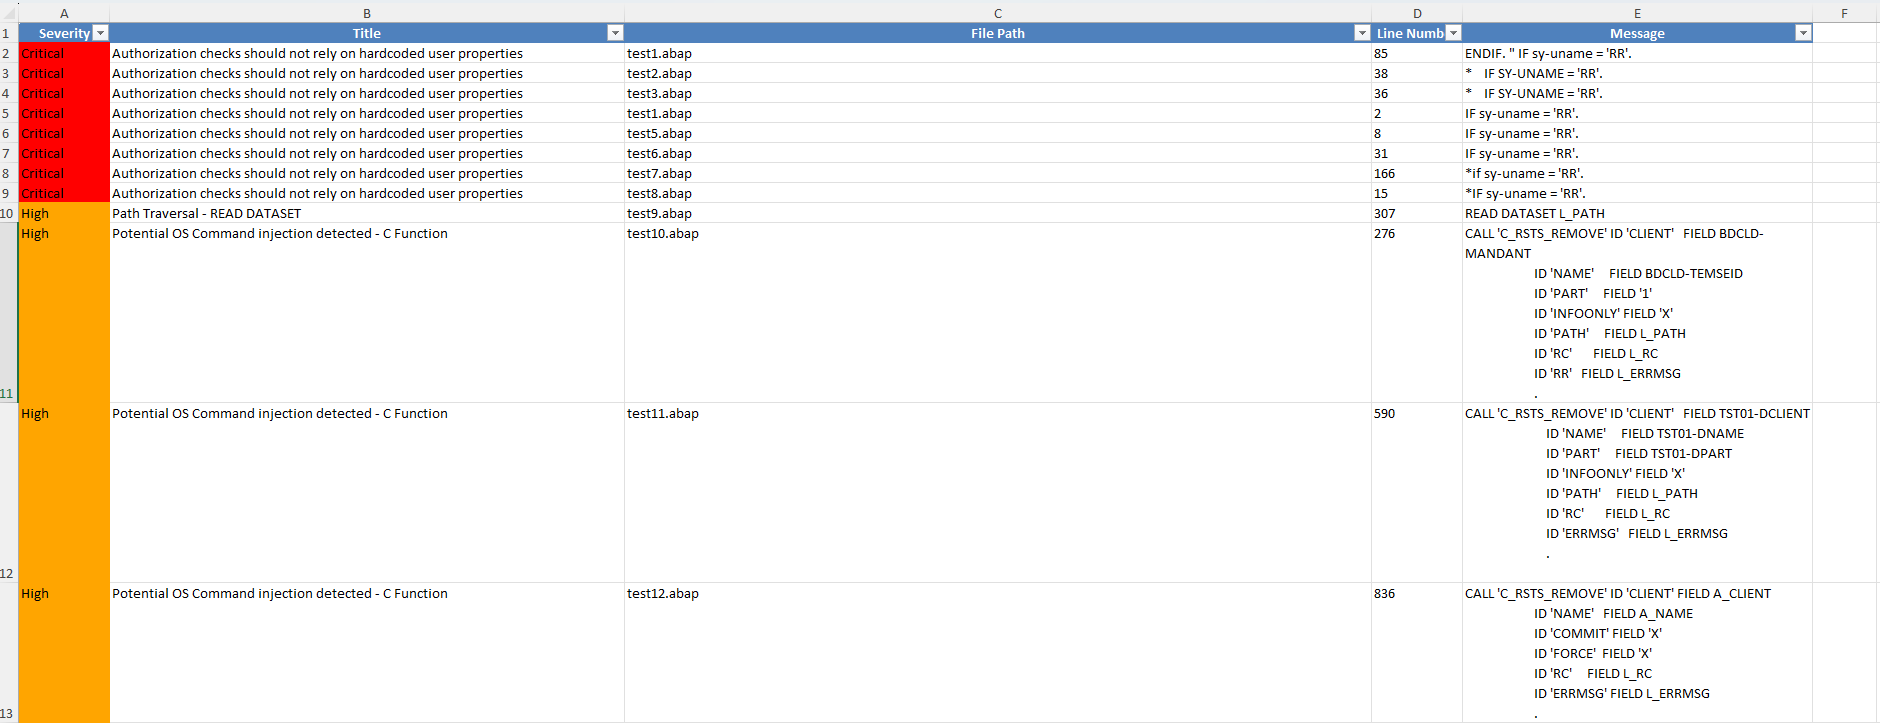
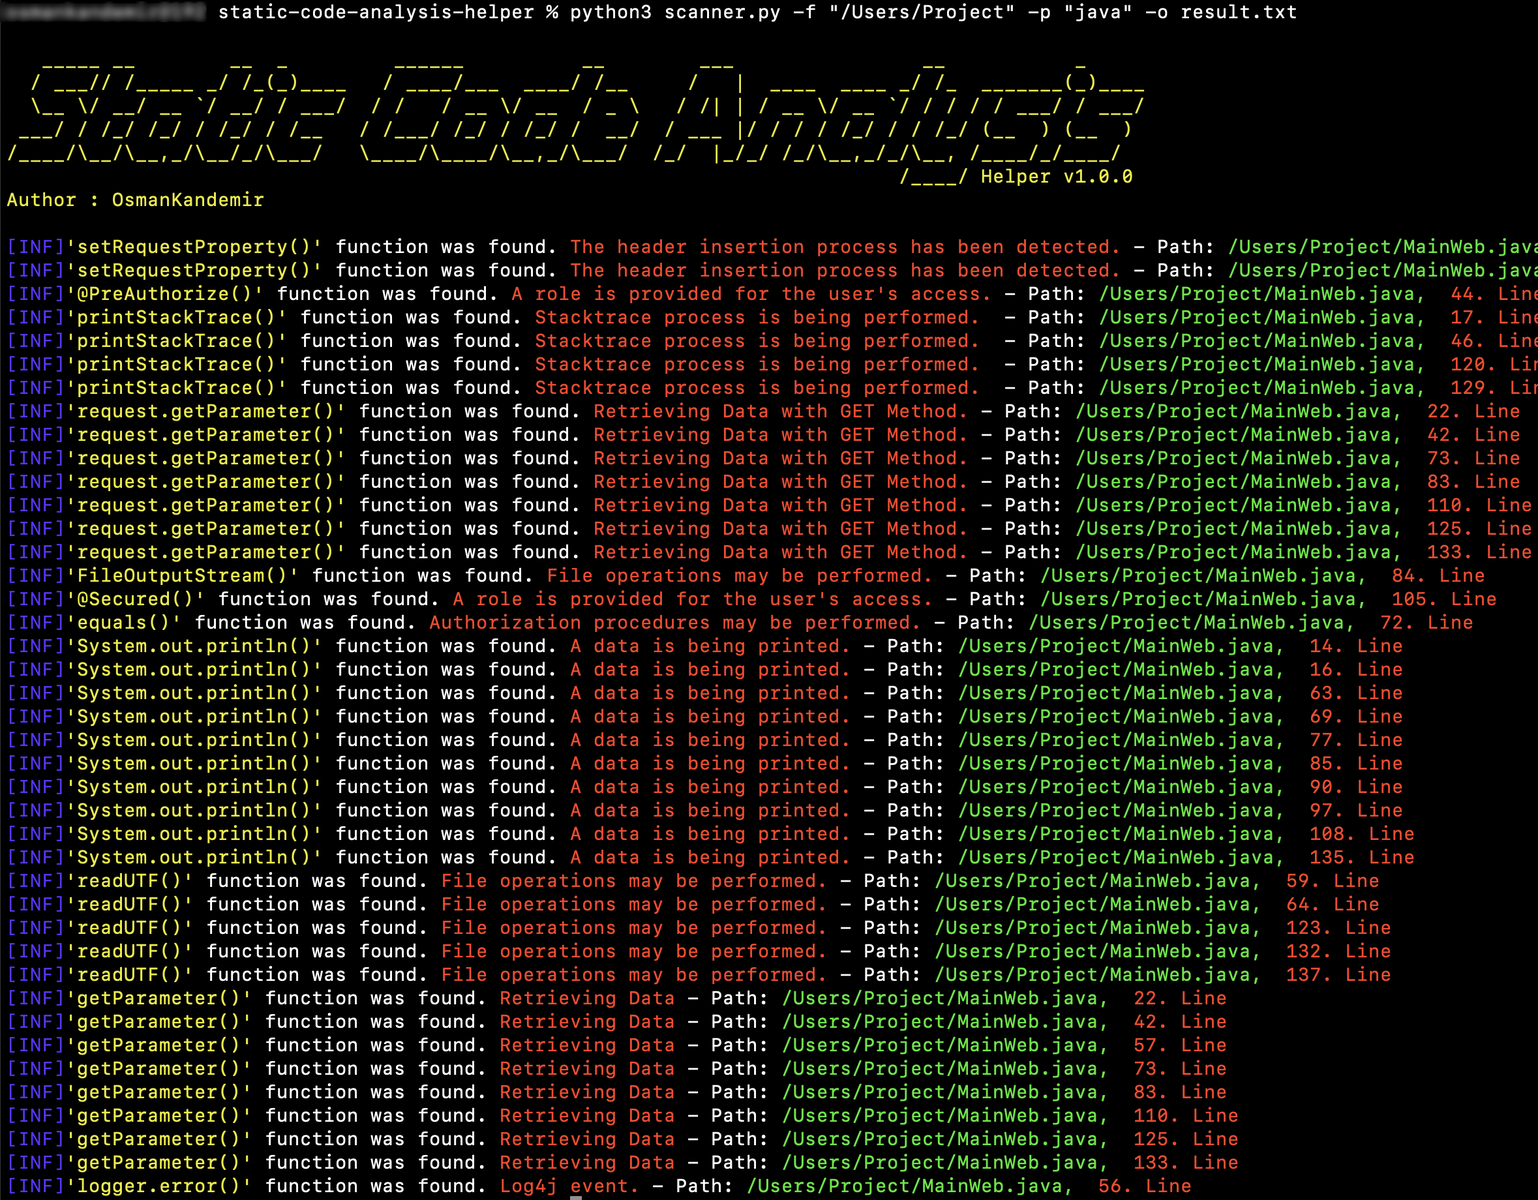
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…

Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…


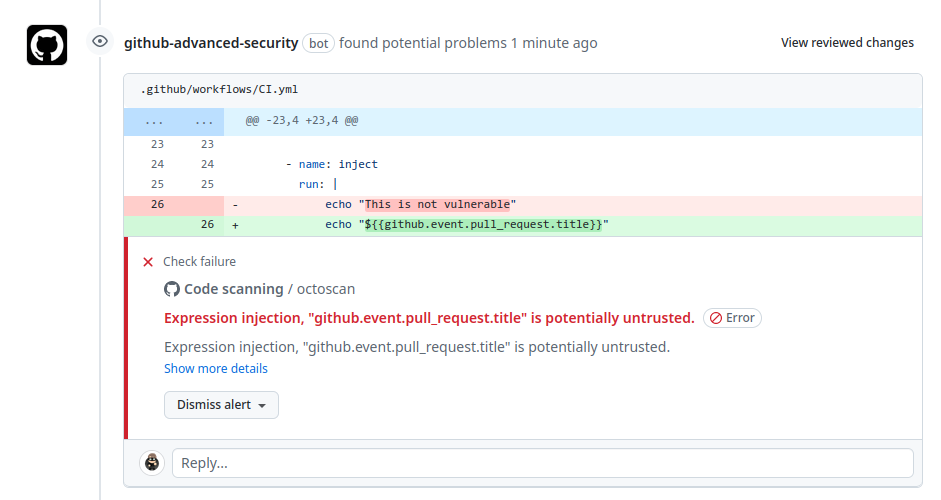
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.

jackson-databind + jackson-core 26 条安全公告自查:按坐标逐条求交集给出真正到位的版本(2.18.11/2.21.7/2.22.3/3.1.7/3.2.3,2.21.6 已不够);扫源码降噪告诉你真中几条;含 1 条 GitHub…

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Processes SARIF output from static analysis tools to detect and redact hard-coded secrets in source code, creating a clean copy without the original…

Synthetic CWE-120 stack buffer overflow variant of CVE-2020-8597 (pppd EAP) as a CodeQL static-analysis target

MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…

A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…

A Bitbucket Pipe to trigger SonarCloud analysis

解决网络安全漏洞

WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting

Link sources to sinks in C# applications.

Open-source, cross-platform, multi-purpose security auditing tool


AWS Serverless Security

Curated directory of static analysis (SAST) tools and linters for programming languages, configs, build tools, and CI, focused on improving code…