
progpilot
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
code-analysisstatic-code-analysisvulnerability-scanners
designsecurity/progpilotPHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
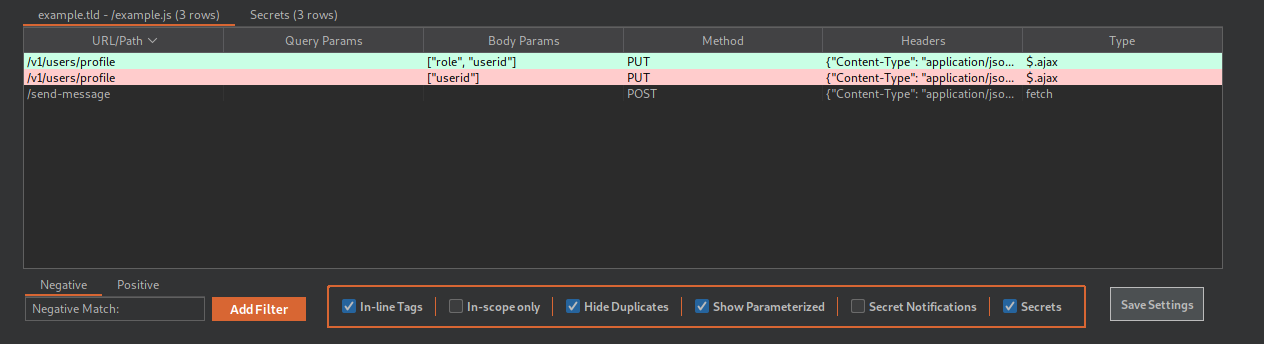 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 s0md3v/hardcodes
find hardcoded strings from source code
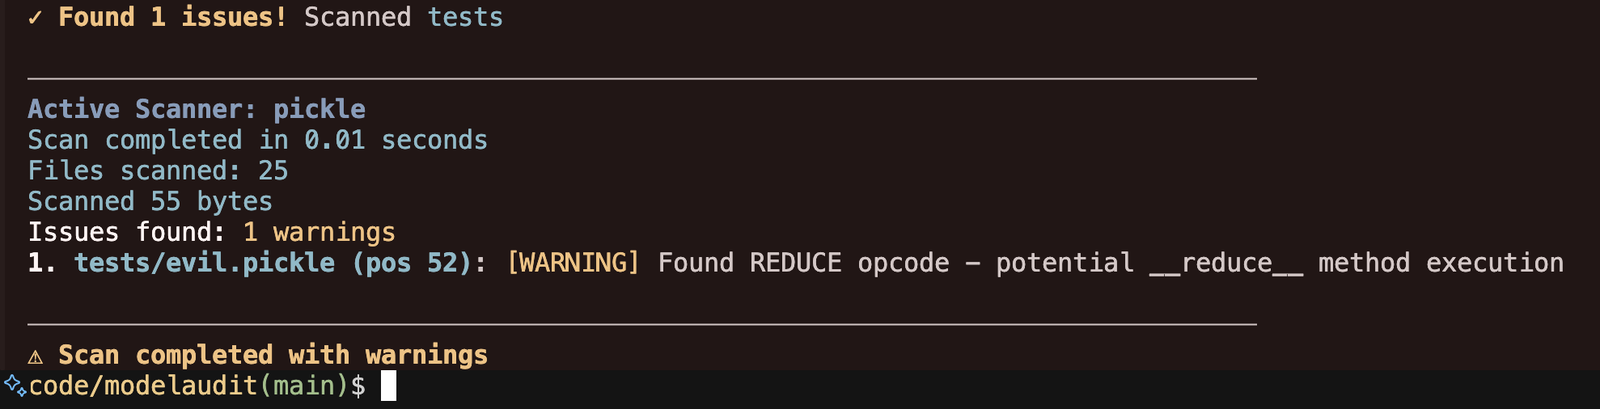 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
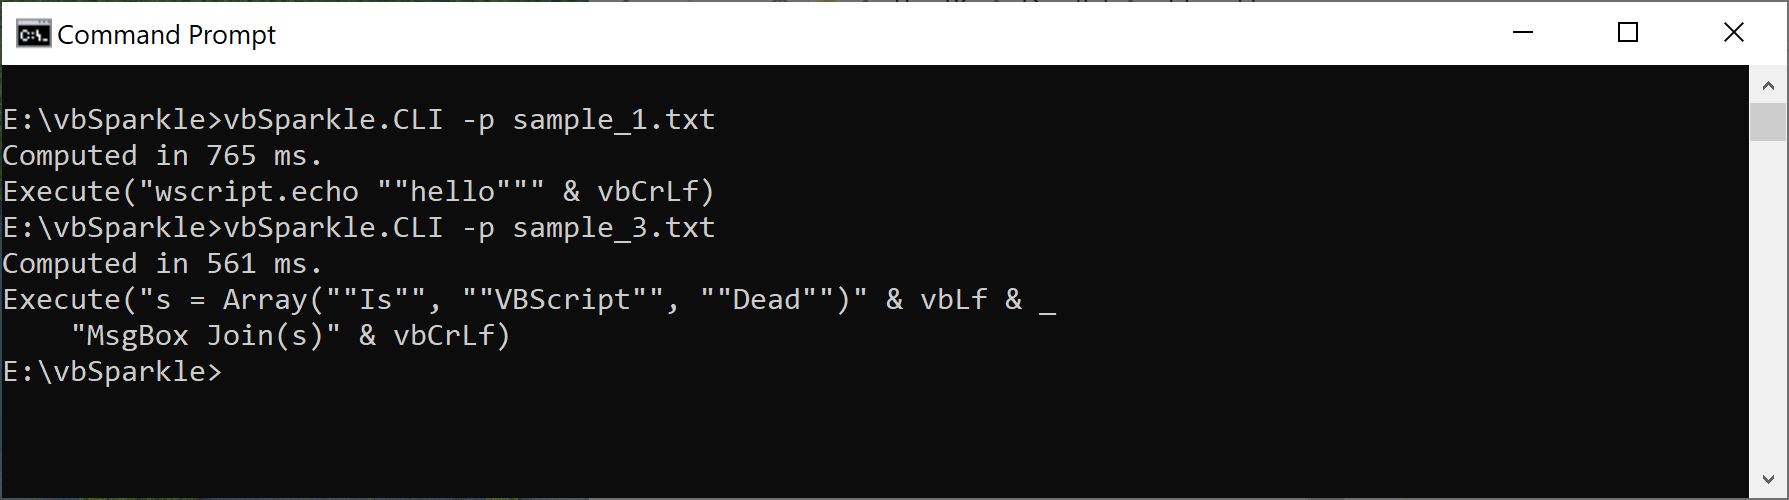 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
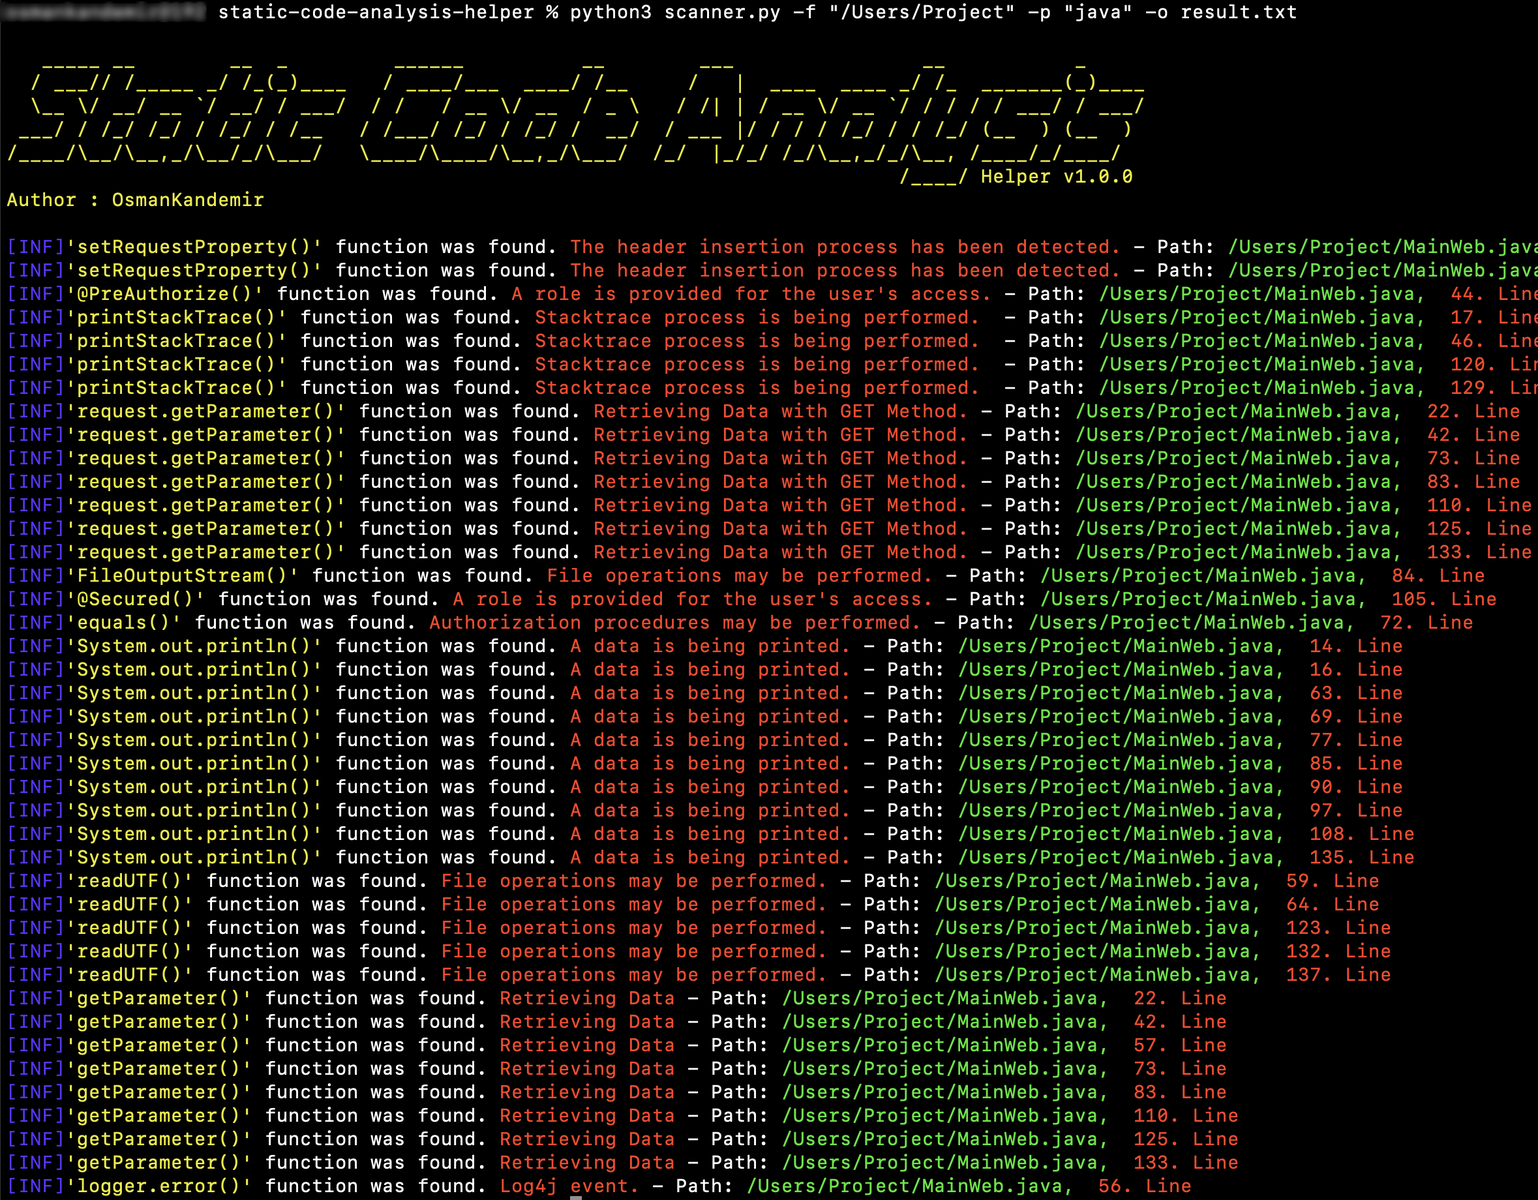 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 nccgroup/call_map
Current development for Call Map takes place at https://github.com/ajylee/call_map. Call Map is a tool for navigating Python call graphs.
 thrilokh-q123/cve-2025-23134_fixes_code
The ASN1_STRING_set() function takes an `int` length, make sure the argument is not inadvertently truncated when it is called from asn1_ex_c2i().
 sam00/cve-2026-56158-.net-framework-rce-poc-exploit
Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…
 yousif-iq/cve-2026-39259
CVE-2026-39259
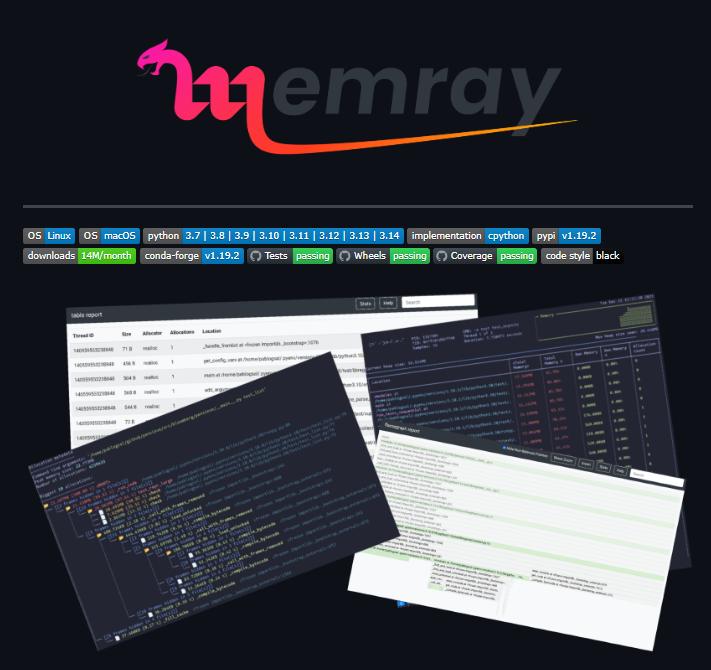 0xmrma/cve-2026-32722
Bloomberg Memray’s Stored XSS via Unescaped Command-Line Metadata
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…