
horusec
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
cloud-securitycode-analysiscontainer-security+5
1.3k
zupit/horusecHorusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 s0md3v/hardcodes
find hardcoded strings from source code
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
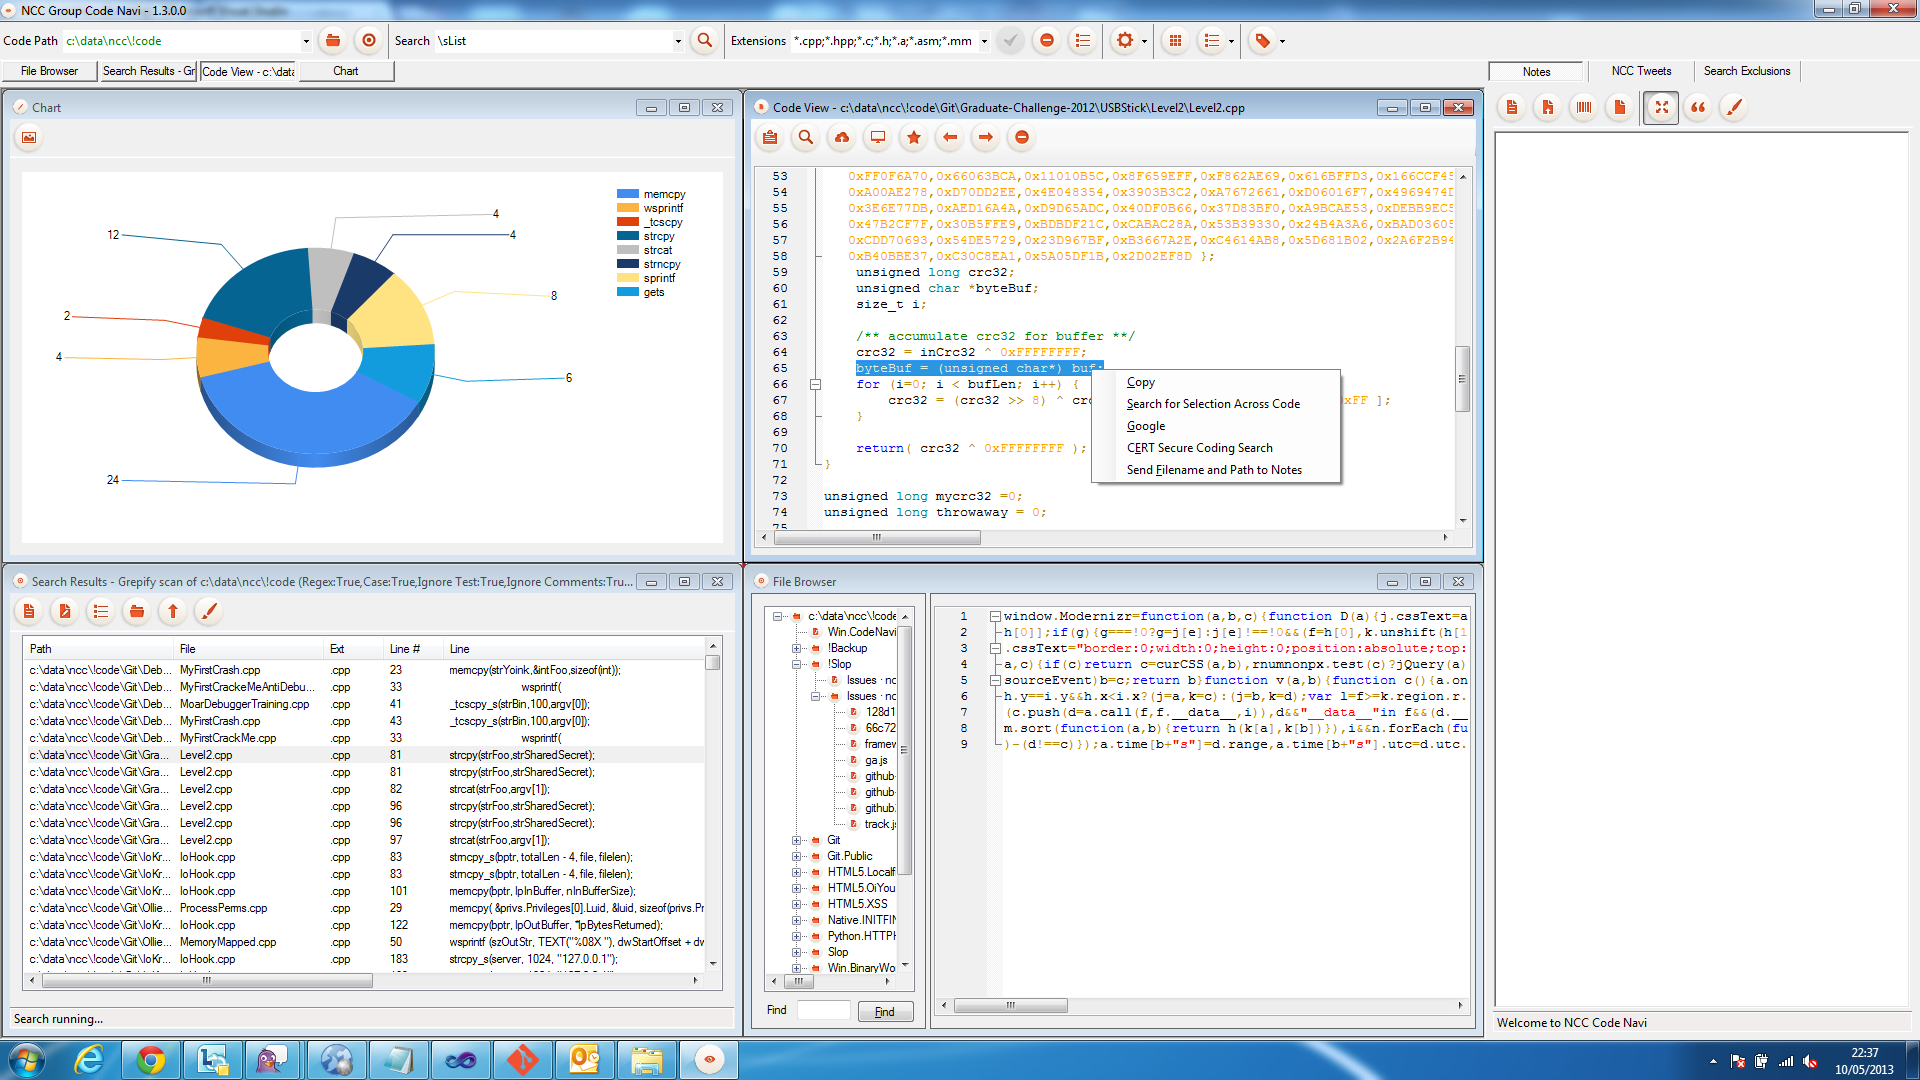 nccgroup/ncccodenavi
NCC Code Navigator
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework

 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 tenable/terrascan
Detect compliance and security violations across Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure.
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
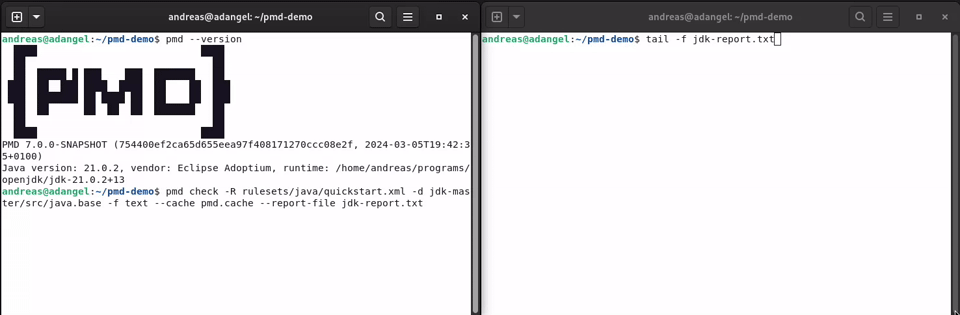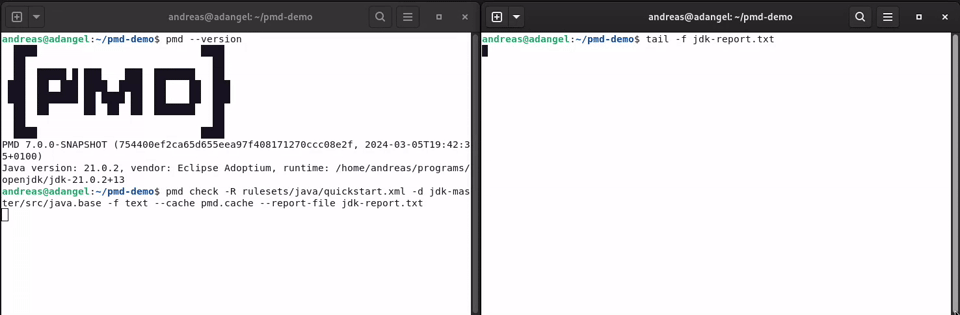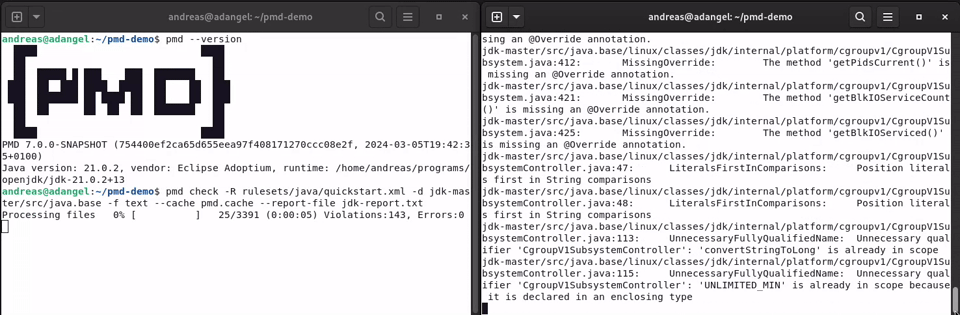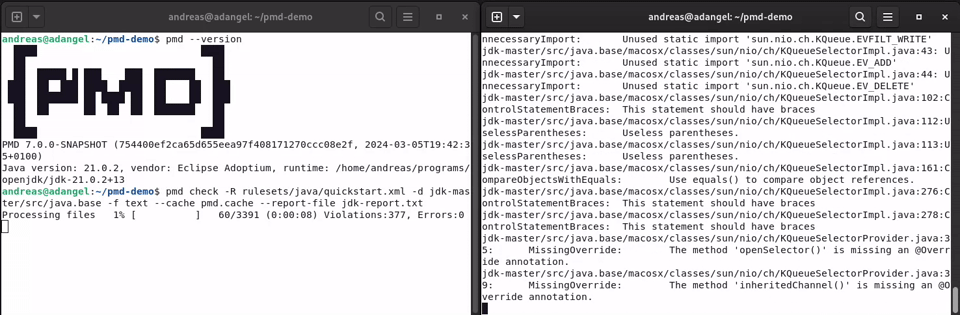 pmd/pmd
An extensible multilanguage static code analyzer.
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
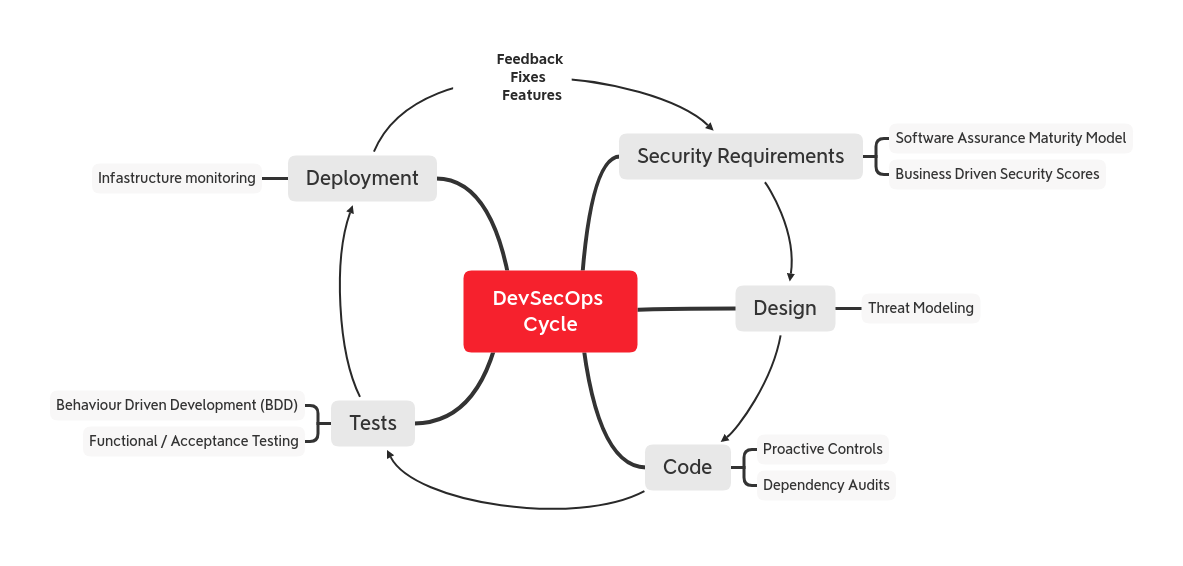 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.