

njsscan
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
code-analysisdevsecopsstatic-analysis+3
458
ajinabraham/njsscanSemantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…

 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
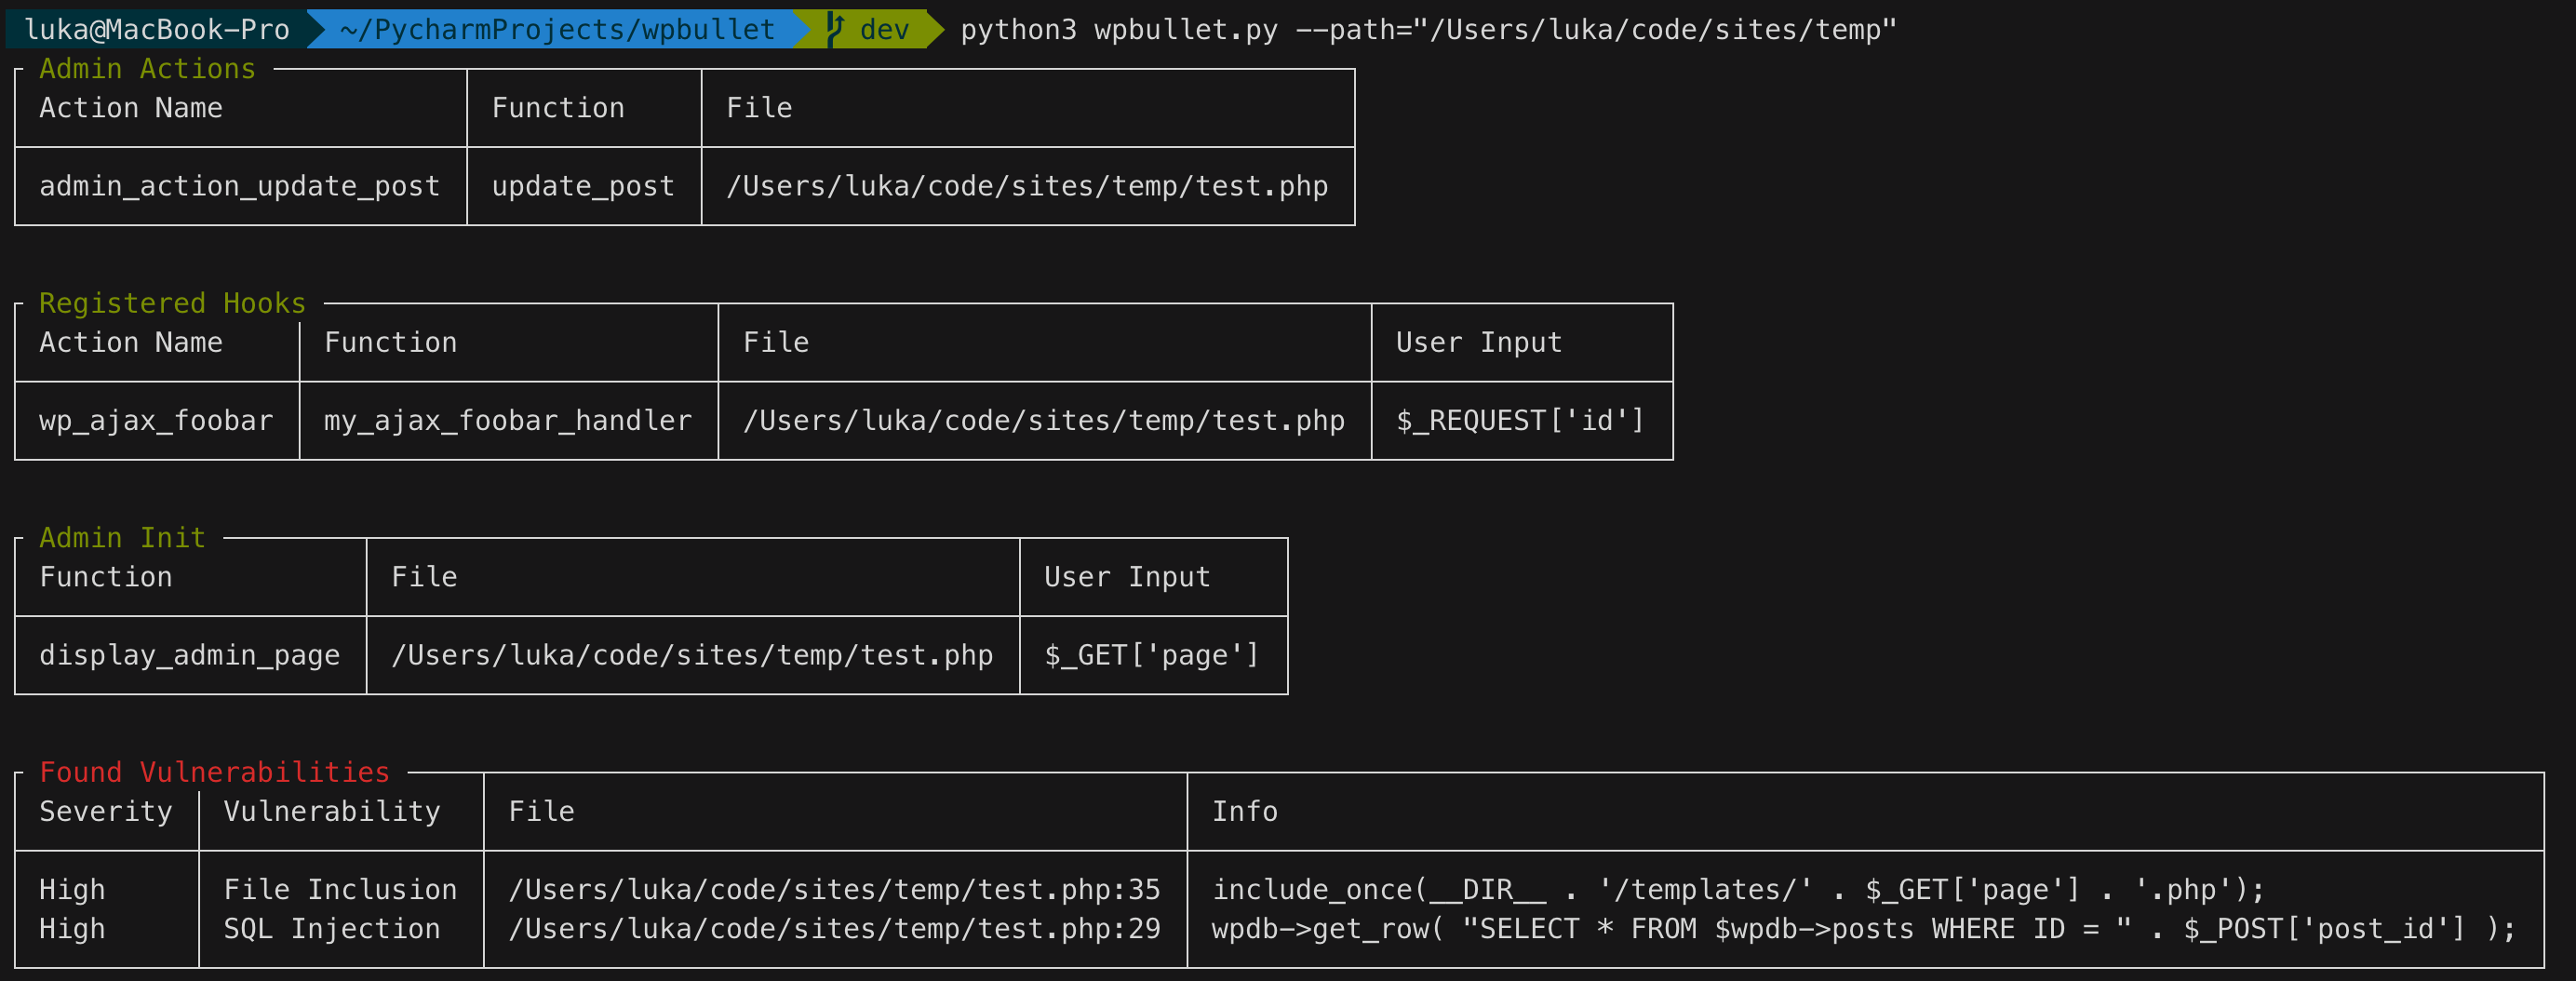 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts
 s0md3v/hardcodes
find hardcoded strings from source code
 kira2040k/php_code_analysis
Static PHP code scanner that detects SQL injection, XSS, SSRF, LFI, command injection, insecure deserialization, and other web vulnerabilities in…
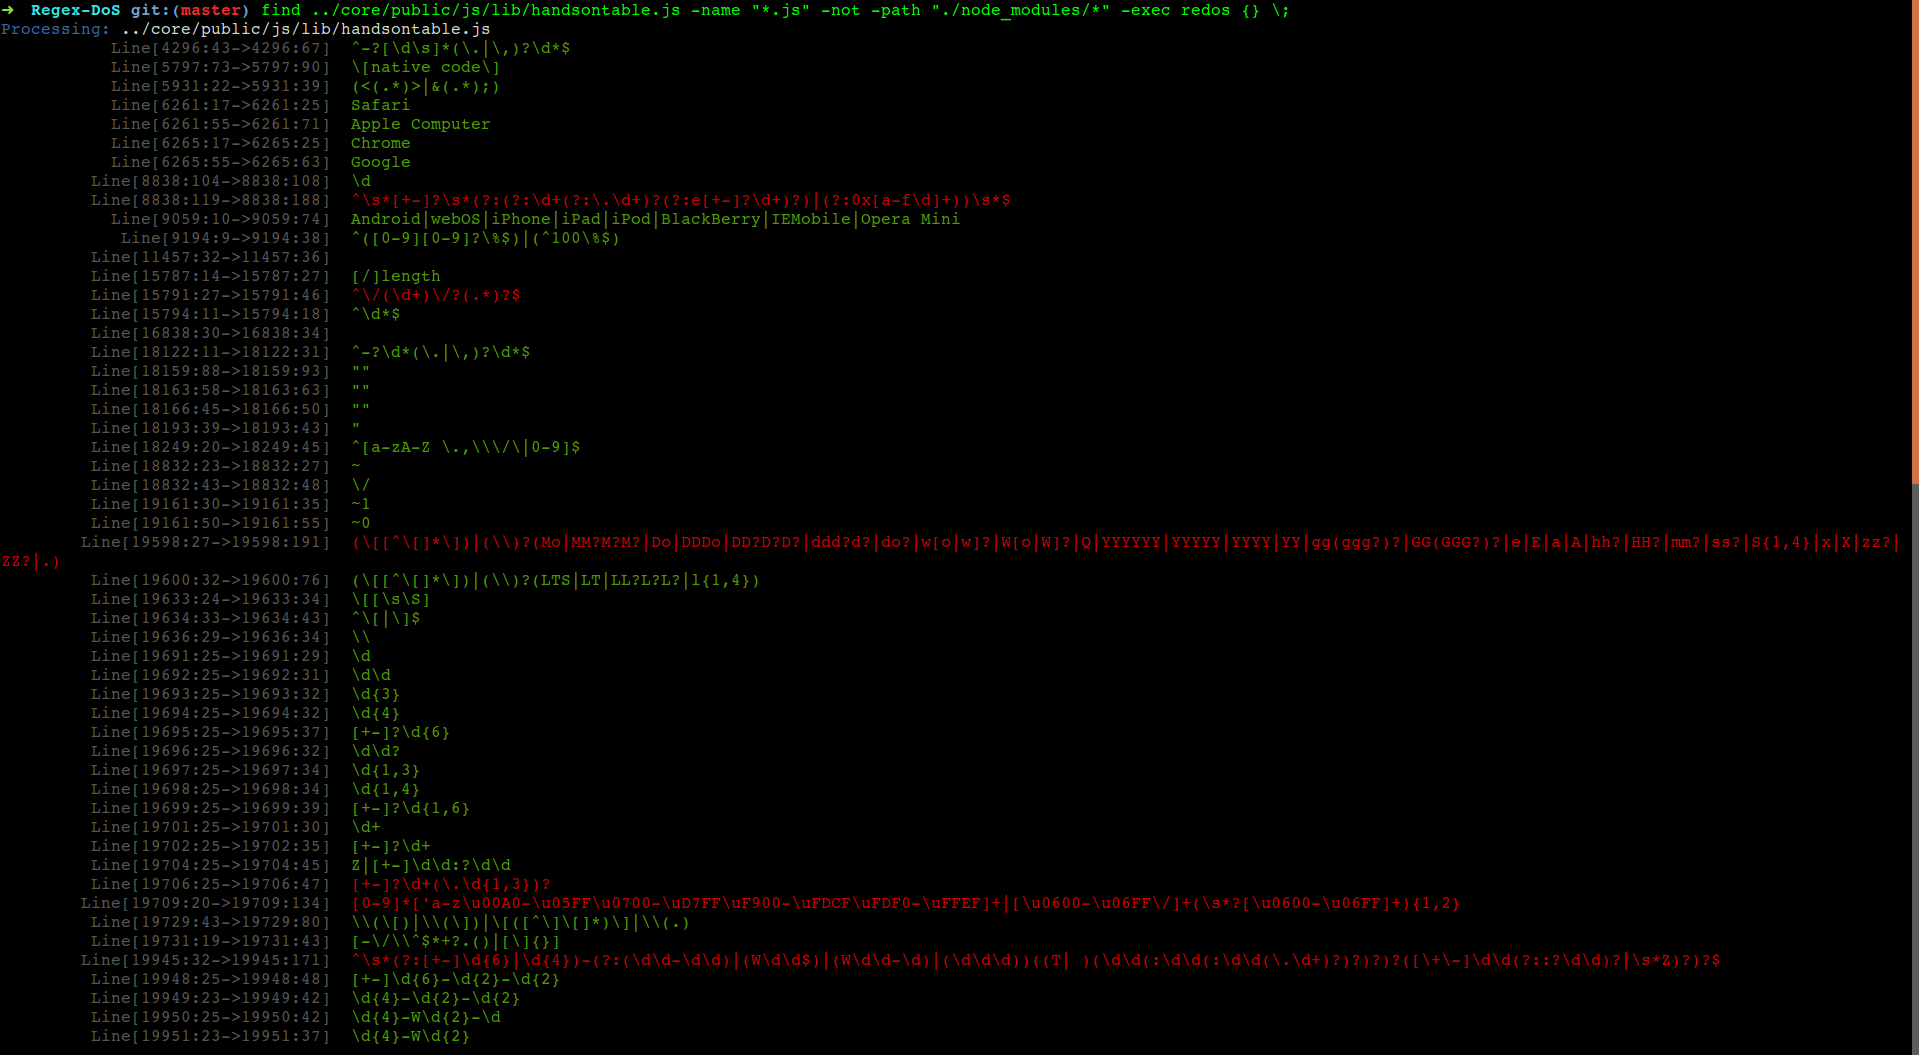 jagracey/regex-dos
:cop: :punch: RegEx Denial of Service (ReDos) Scanner
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…