

Agentic-Bug-Hunter
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
ai-securityapi-security-testingcloud-security+8
5.3k
awarexone/agentic-bug-hunterAI-powered bug bounty hunting toolkit that works with or without subscription.
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
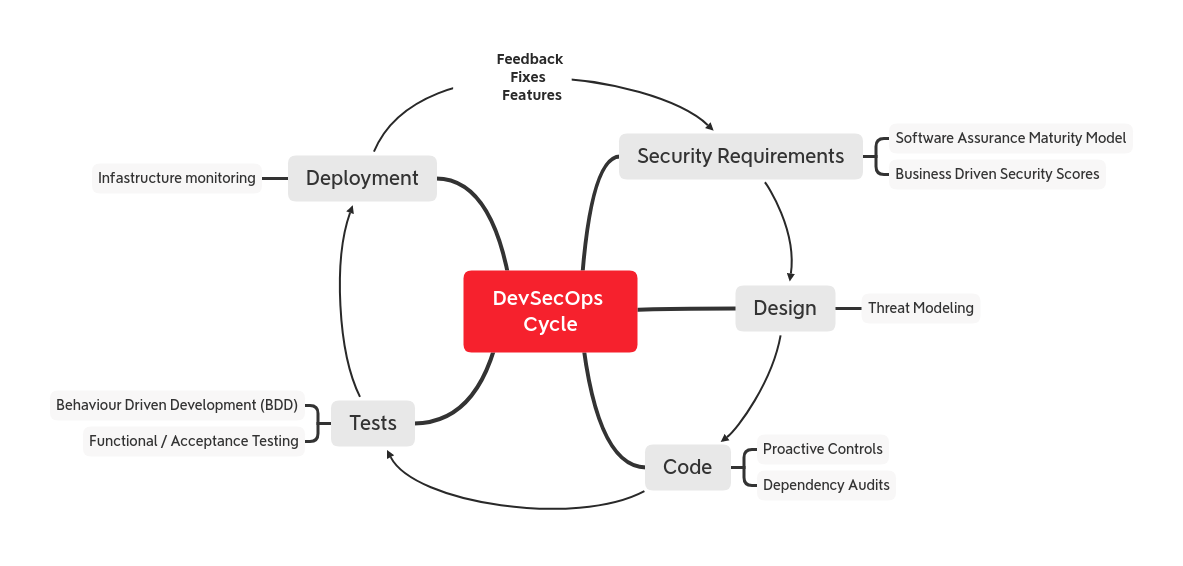 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
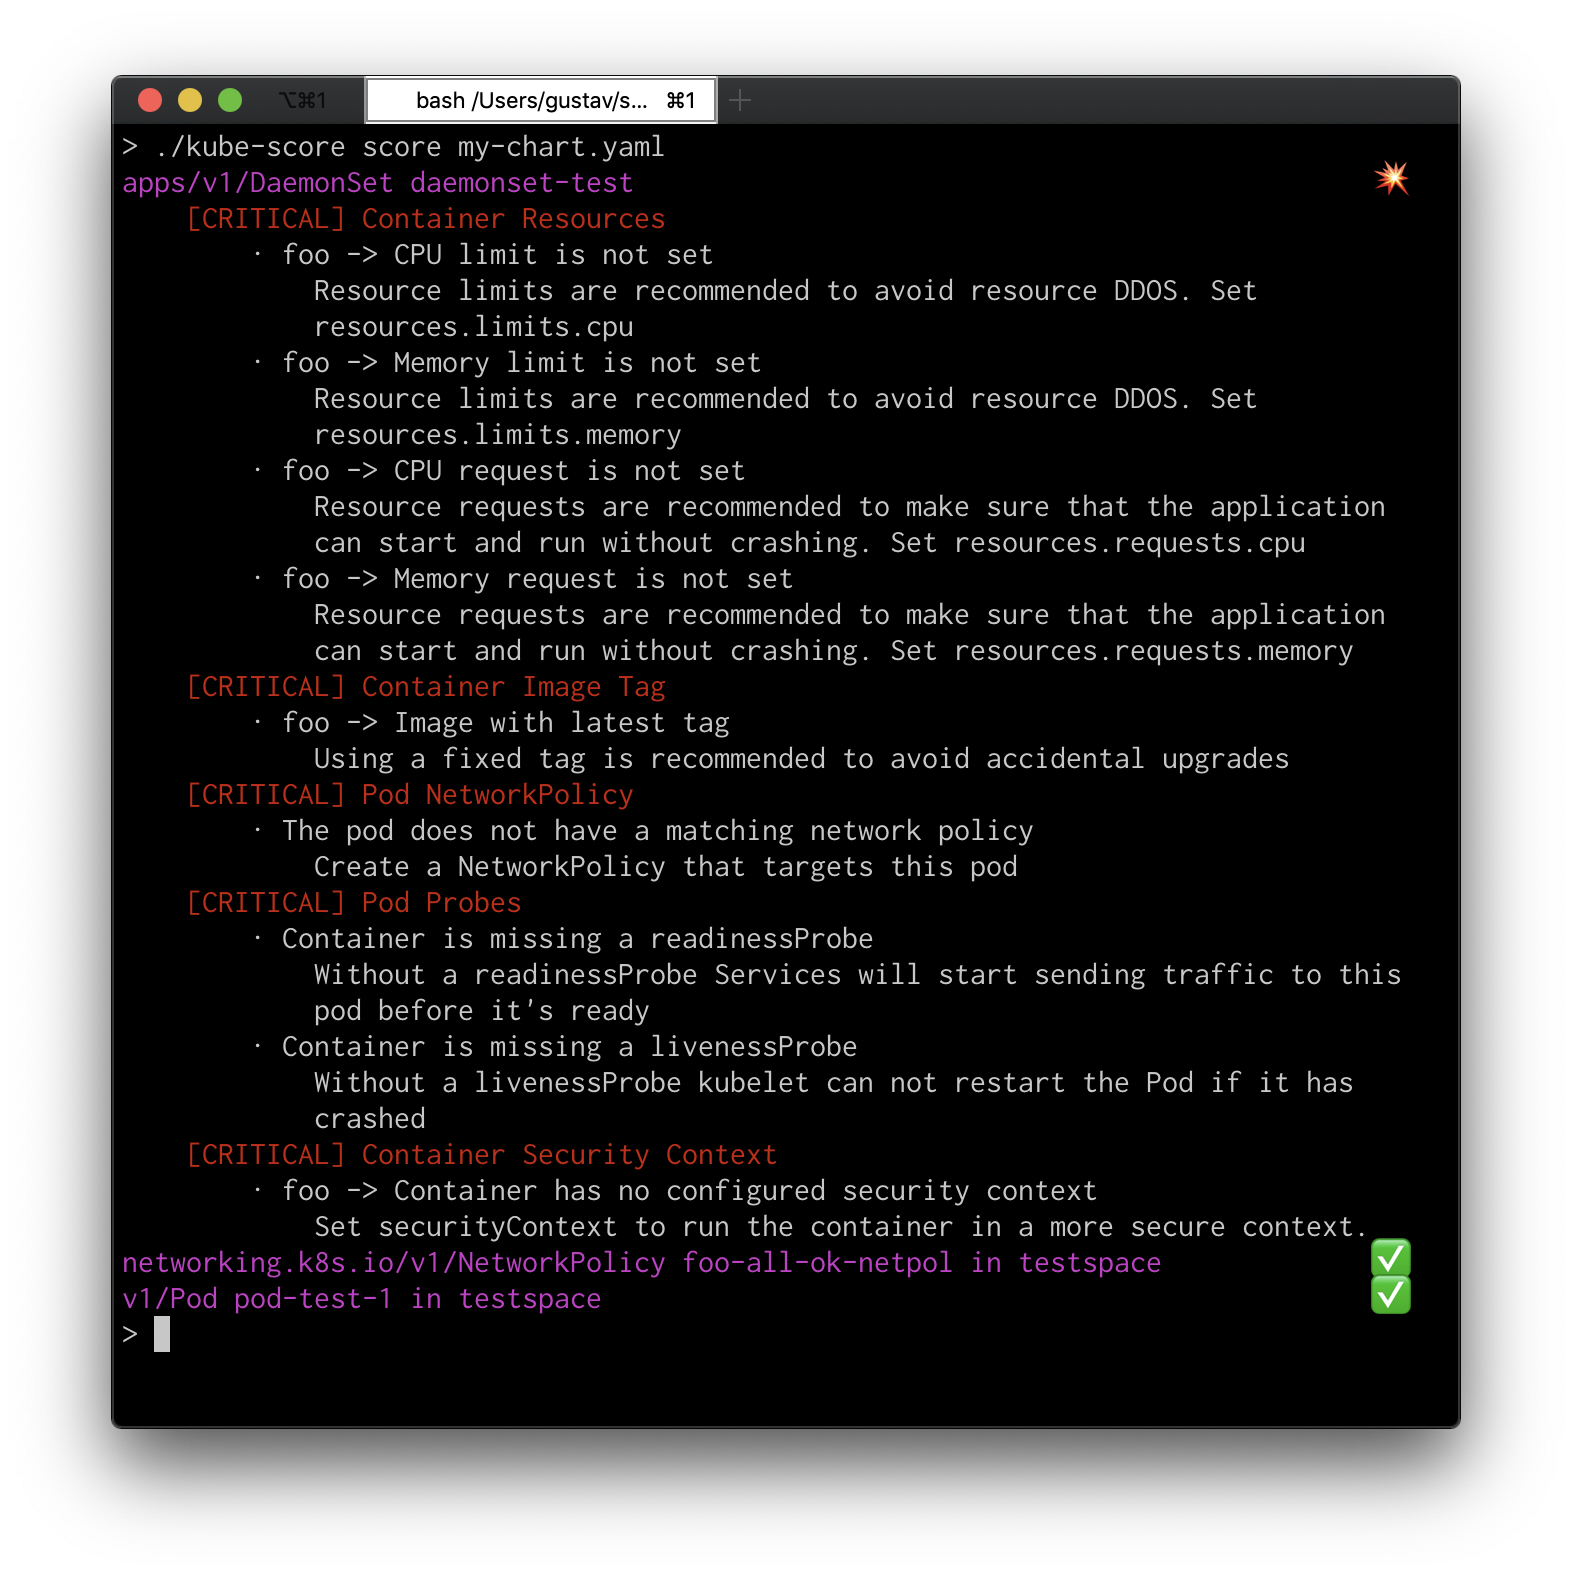 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 python-security/pyt
A Static Analysis Tool for Detecting Security Vulnerabilities in Python Web Applications
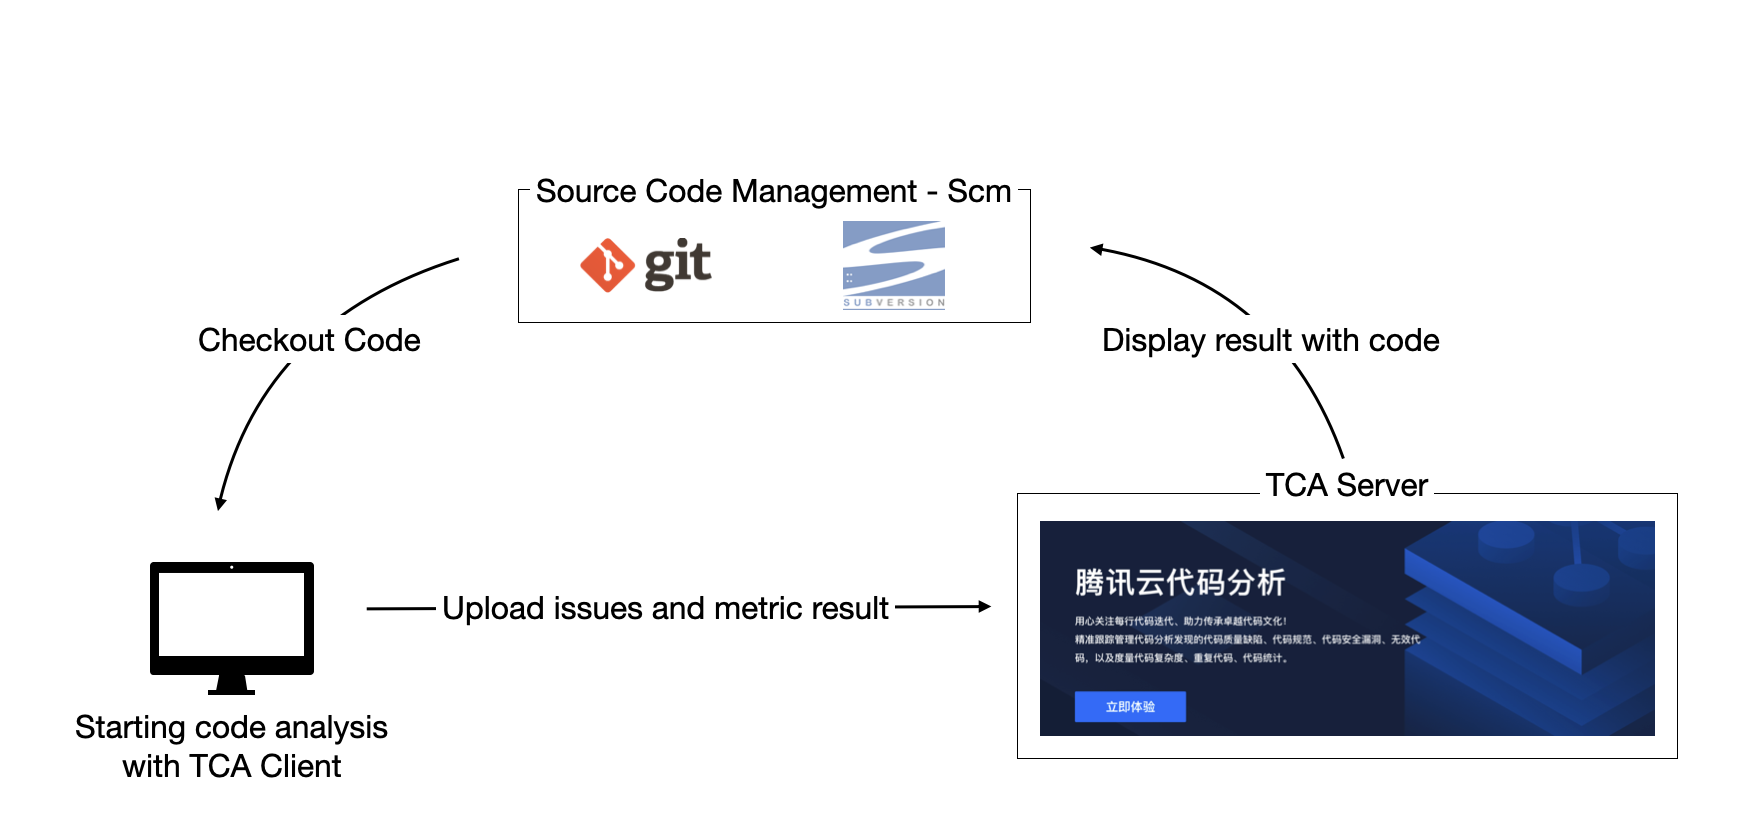 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
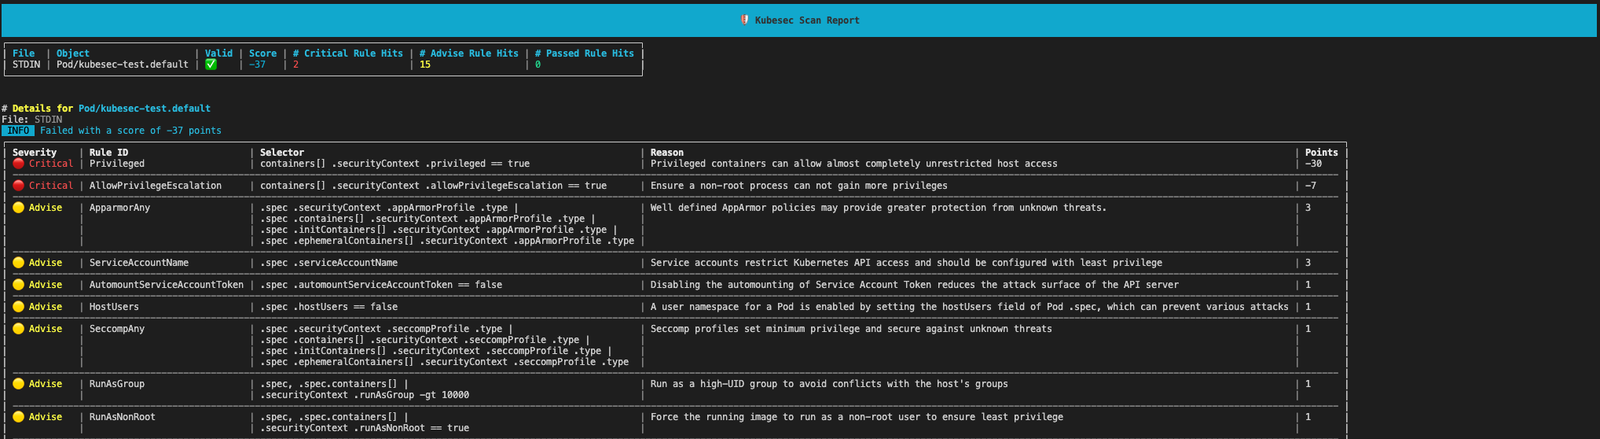 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.