
lightweight_static_analysis
 nccgroup/lightweight_static_analysis
Create useful, lightweight static analyses using open source tools + a tiny bit of your code
code-analysiseducationpenetration-testing+4
13
nccgroup/lightweight_static_analysisCreate useful, lightweight static analyses using open source tools + a tiny bit of your code
 praetorian-inc/gokart
A static analysis tool for securing Go code
 wireghoul/graudit
grep rough audit - source code auditing tool
 reverseclabs/needle
The iOS Security Testing Framework
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 vusec/ghostrace
Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 advanced-threat-research/creosote
Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 nccgroup/matt.net
Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
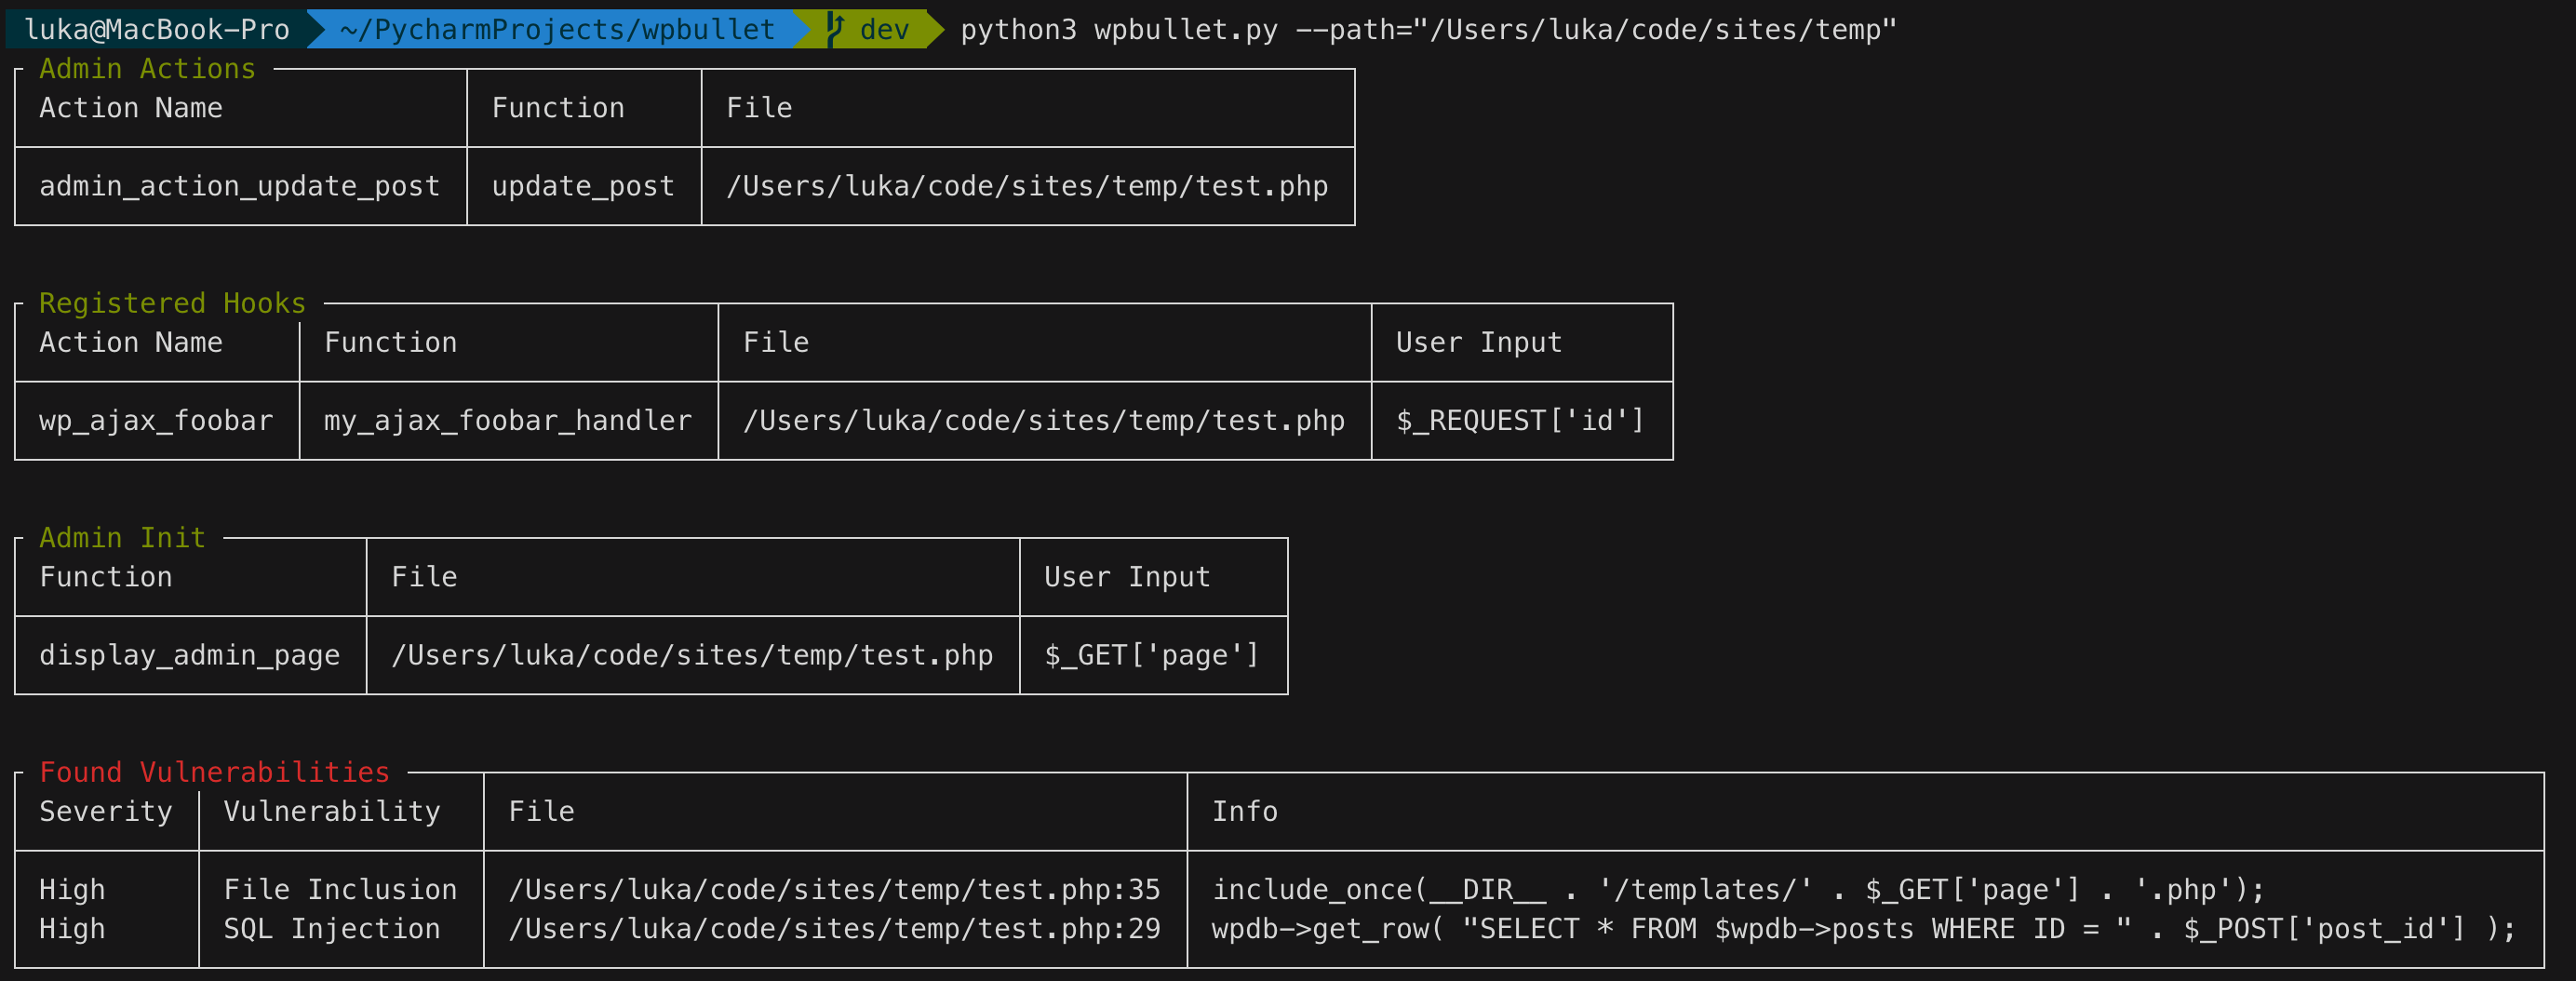 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 agrawalsmart7/scodescanner
Command-line static analysis scanner that detects critical vulnerabilities in PHP and YAML source code using custom semgrep rules, with Jira and…
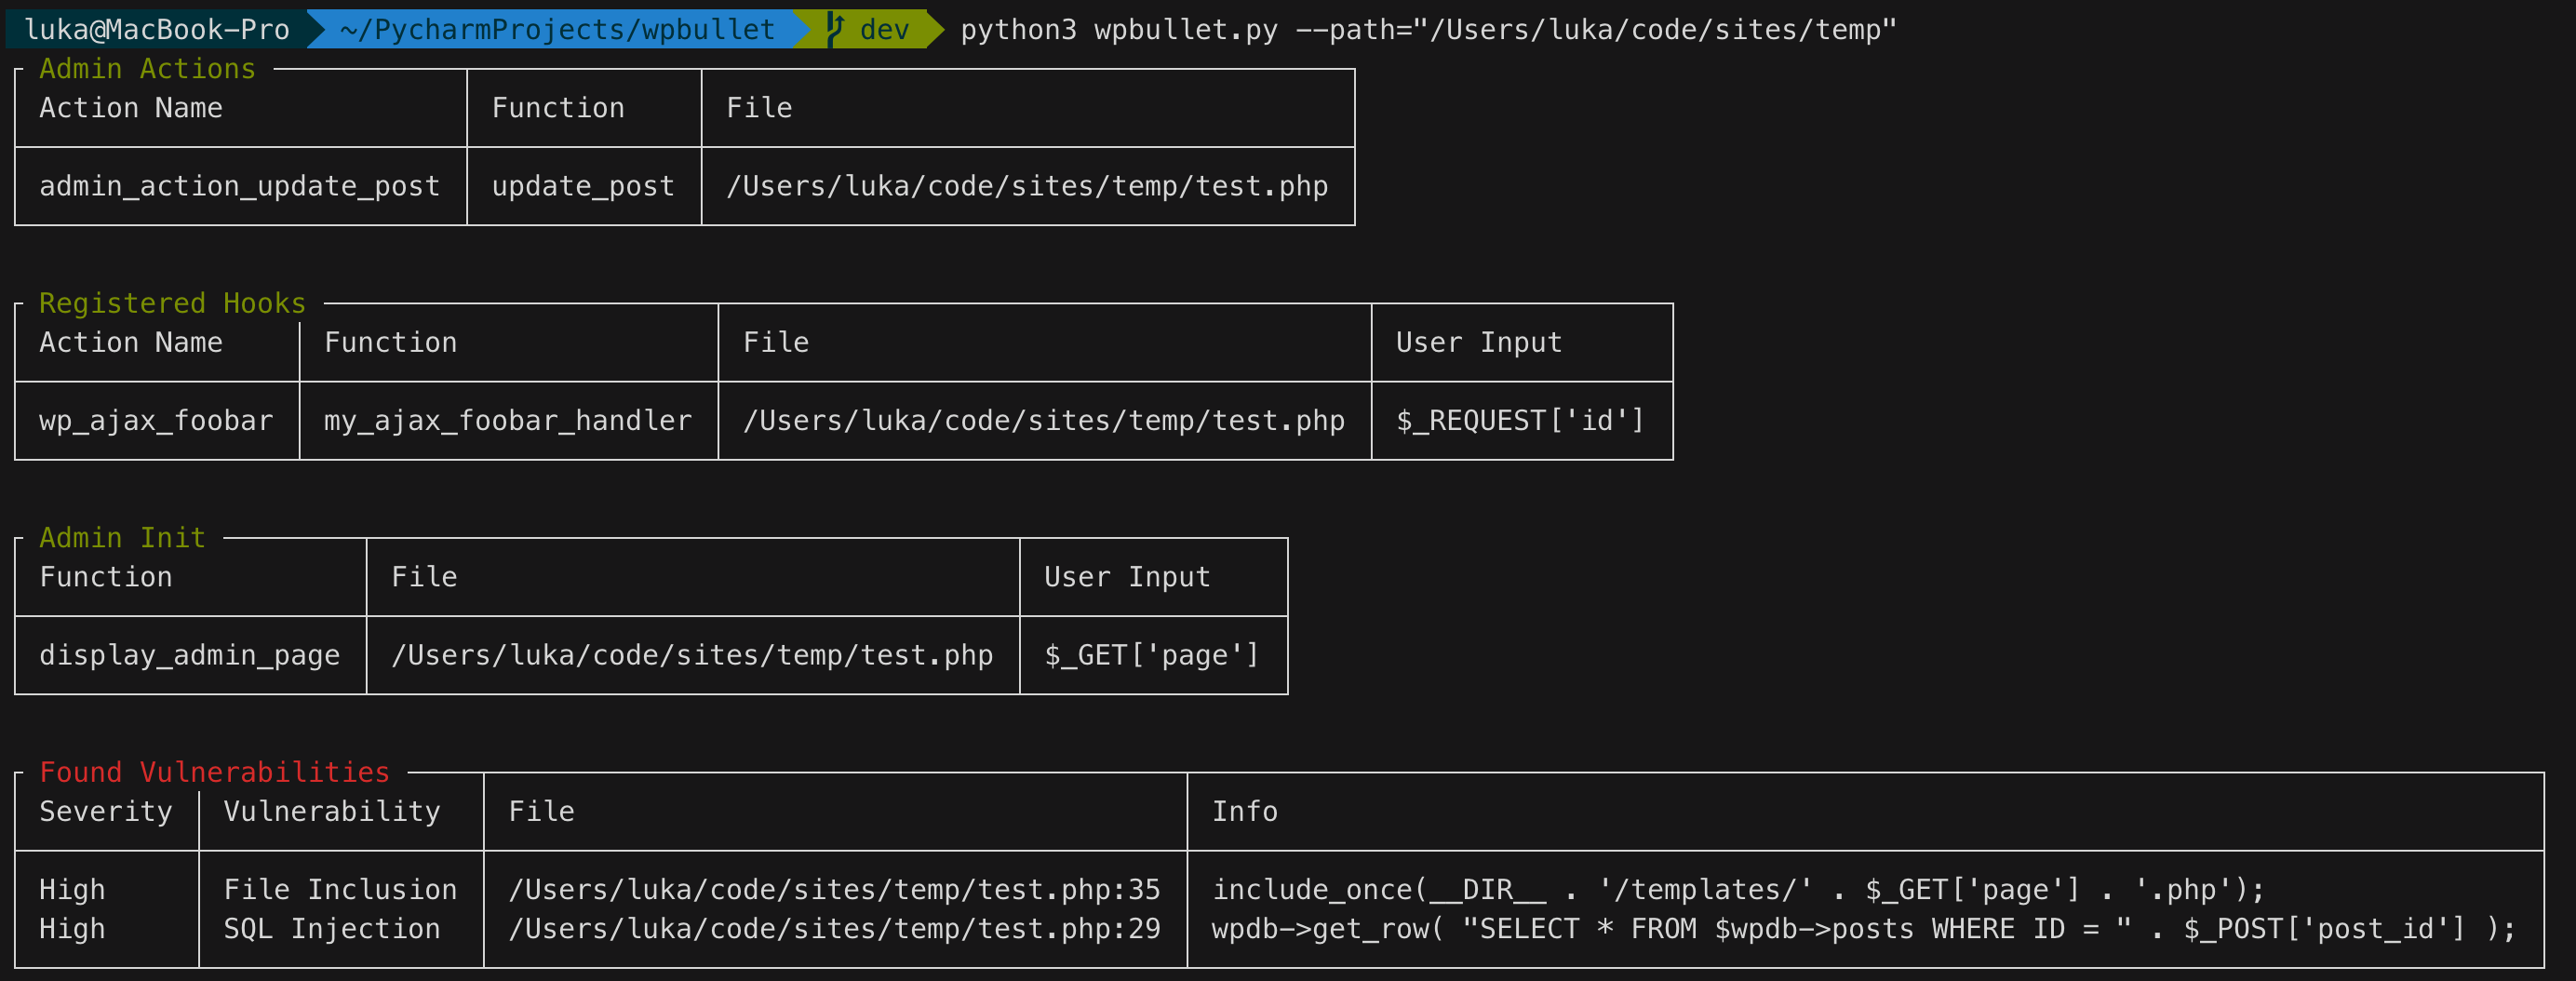 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP