

DevSecOpsGuideline
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
api-securitycloud-securitycontainer-security+6
1.1k
owasp/devsecopsguidelineThe OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 kadenzipfel/smart-contract-vulnerabilities
A collection of smart contract vulnerabilities along with prevention methods
 0xdea/semgrep-rules
A collection of my Semgrep rules to facilitate vulnerability research.
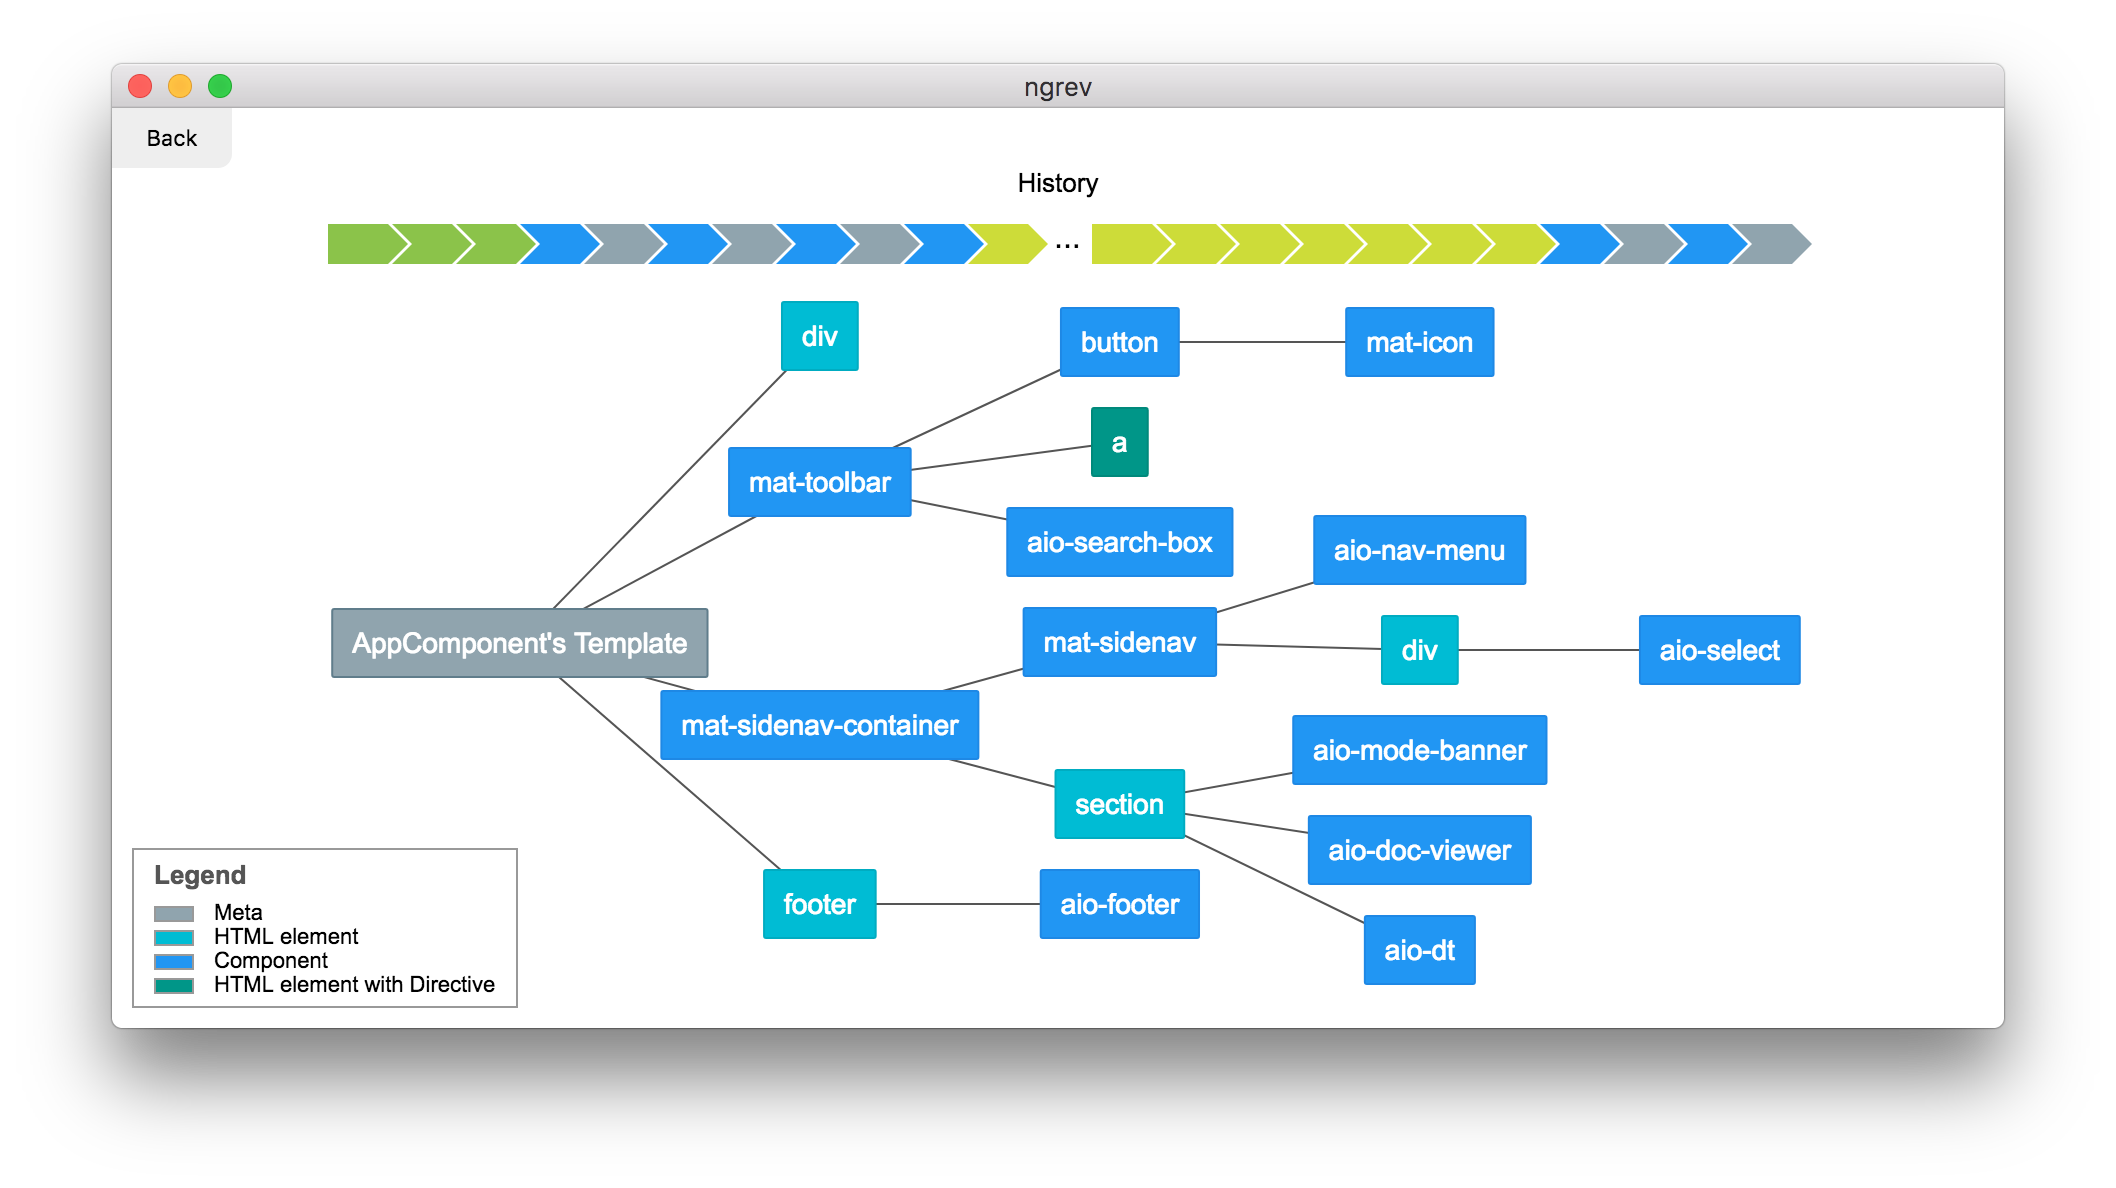 mgechev/ngrev
Tool for reverse engineering of Angular applications
 doyensec/regexploit
Find regular expressions which are vulnerable to ReDoS (Regular Expression Denial of Service)
 makenowjust-labs/recheck
Static analysis tool for detecting ReDoS (Regular Expression Denial of Service) vulnerabilities in JavaScript and Scala codebases, providing…
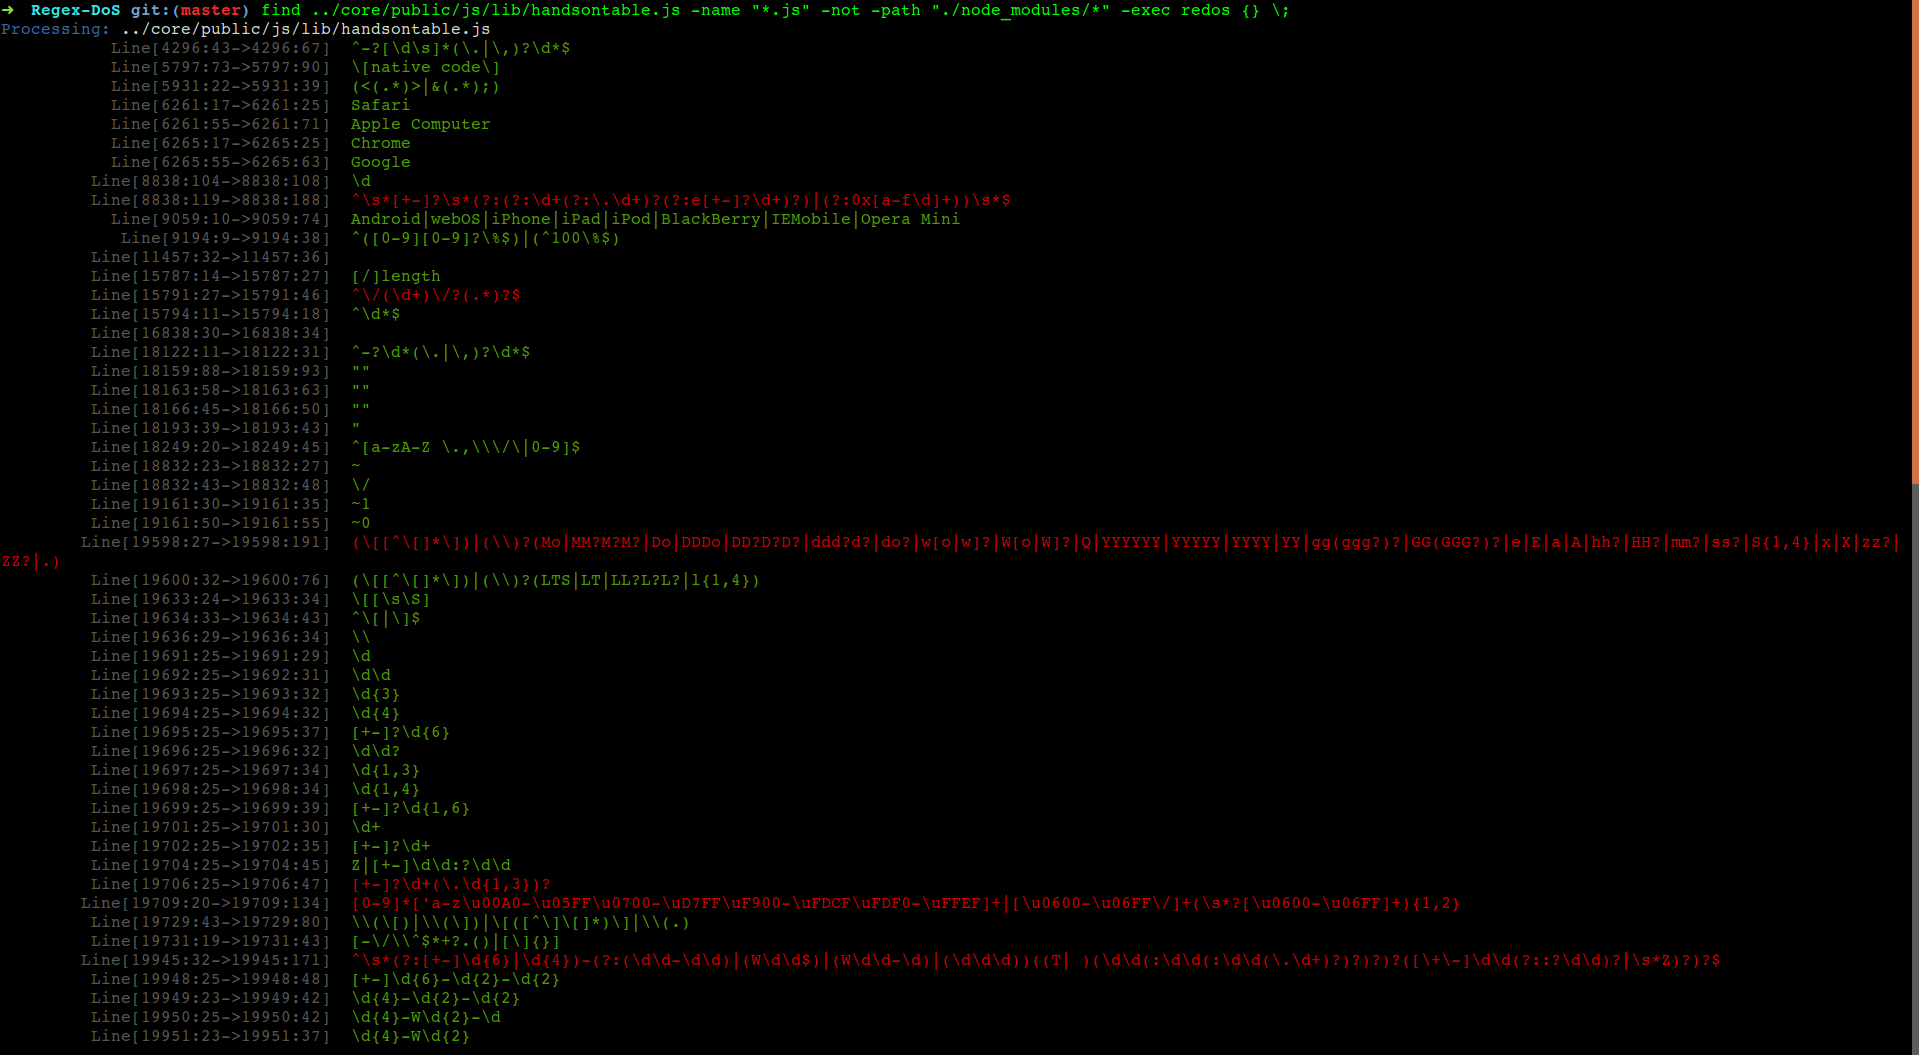 jagracey/regex-dos
:cop: :punch: RegEx Denial of Service (ReDos) Scanner
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 synacktiv/weggli_rules_sstic2023
Curated weggli queries for static analysis of C/C++ code to identify dangerous functions, stack issues, and malloc overflow vulnerabilities.
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
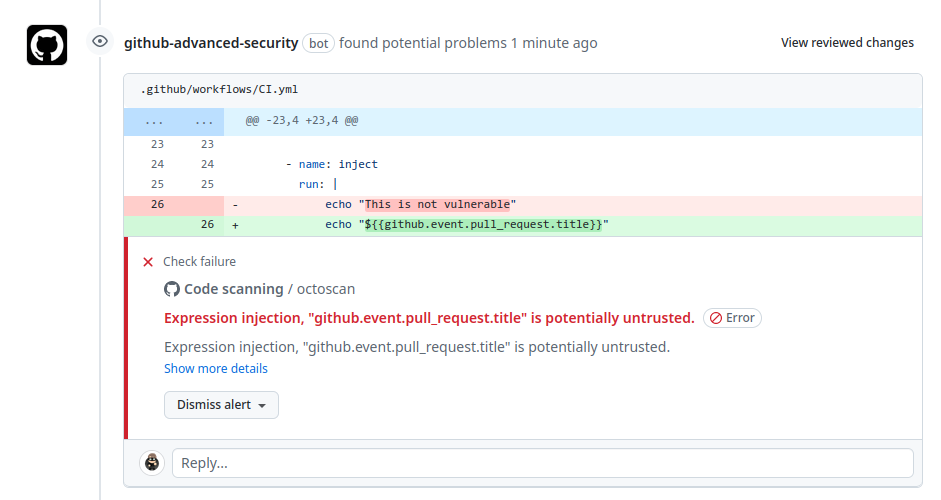 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.
 xs2024770/cve-2024-57521-ruoyi-sqli
Static code audit of CVE-2024-57521, an authenticated SQL injection in RuoYi-Vue's generator module, with source-to-sink analysis and a %0b filter…
 sassoftware/shiro
CVE-2026-49268 — Analysis and Remediation of an LDAP Injection Authentication Bypass Vulnerability
 anna-kravets/codeql-buffer-overflow-variant
Synthetic CWE-120 stack buffer overflow variant of CVE-2020-8597 (pppd EAP) as a CodeQL static-analysis target
 merbinr/cve-2023-31606
Documentation of CVE-2023-31606: a ReDoS vulnerability in Redcloth gem's sanitize_html function, with root cause analysis, CVSS 7.5 scoring, and…
 sudo-wp/sudowp-hooks-visualizer
A security-hardened fork of "Simply Show Hooks". Replaces the compromised original (CVE-2024-6297) and patches unlisted Cross-Site Scripting (XSS)…
 novoda/gradle-static-analysis-plugin
Easy setup of static analysis tools for Android and Java projects.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…