
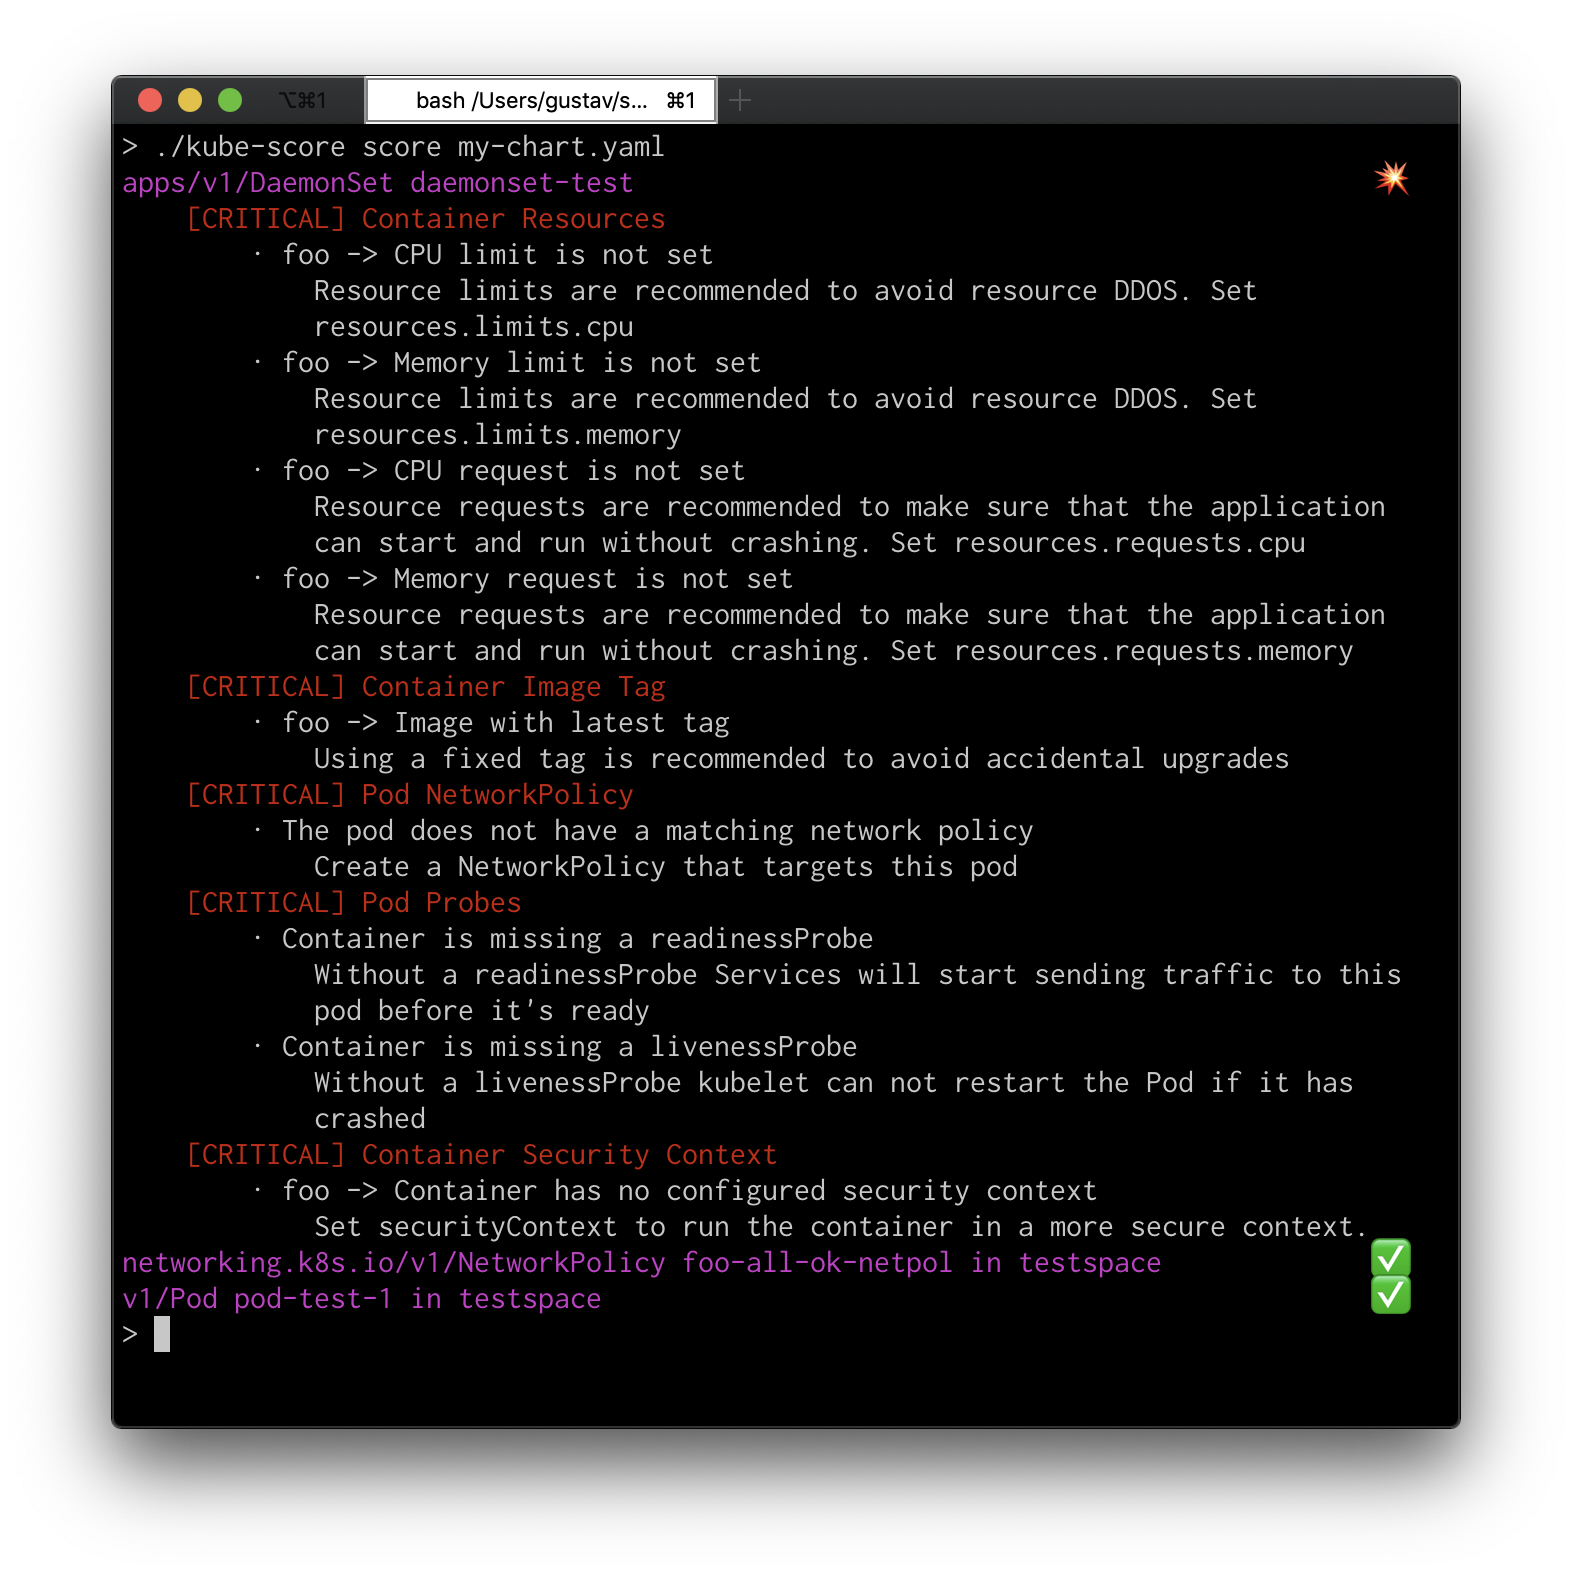
kube-score
 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
cloud-securityconfiguration-auditingcontainer-security+4
3.1k
zegl/kube-scoreKubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
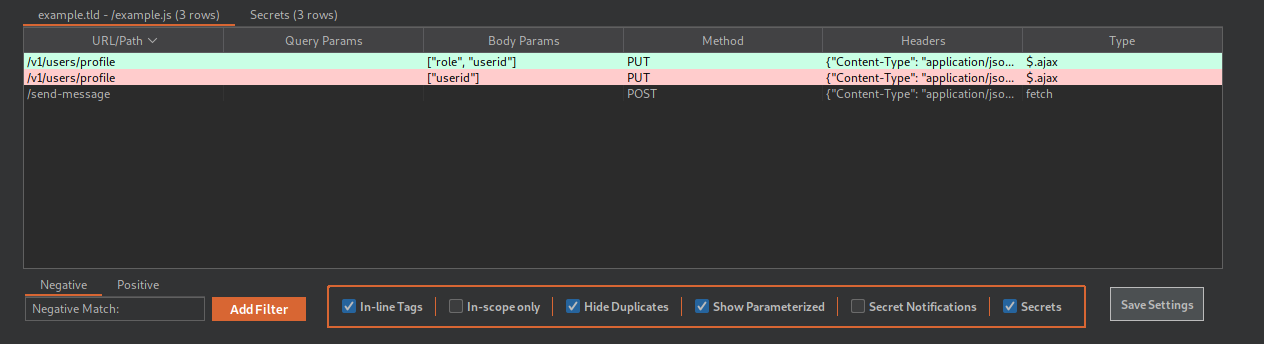 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 nccgroup/cq
Fast code security scanner designed for manual security code review by experts. Outputs line-referenced findings to text files for easy filtering and…
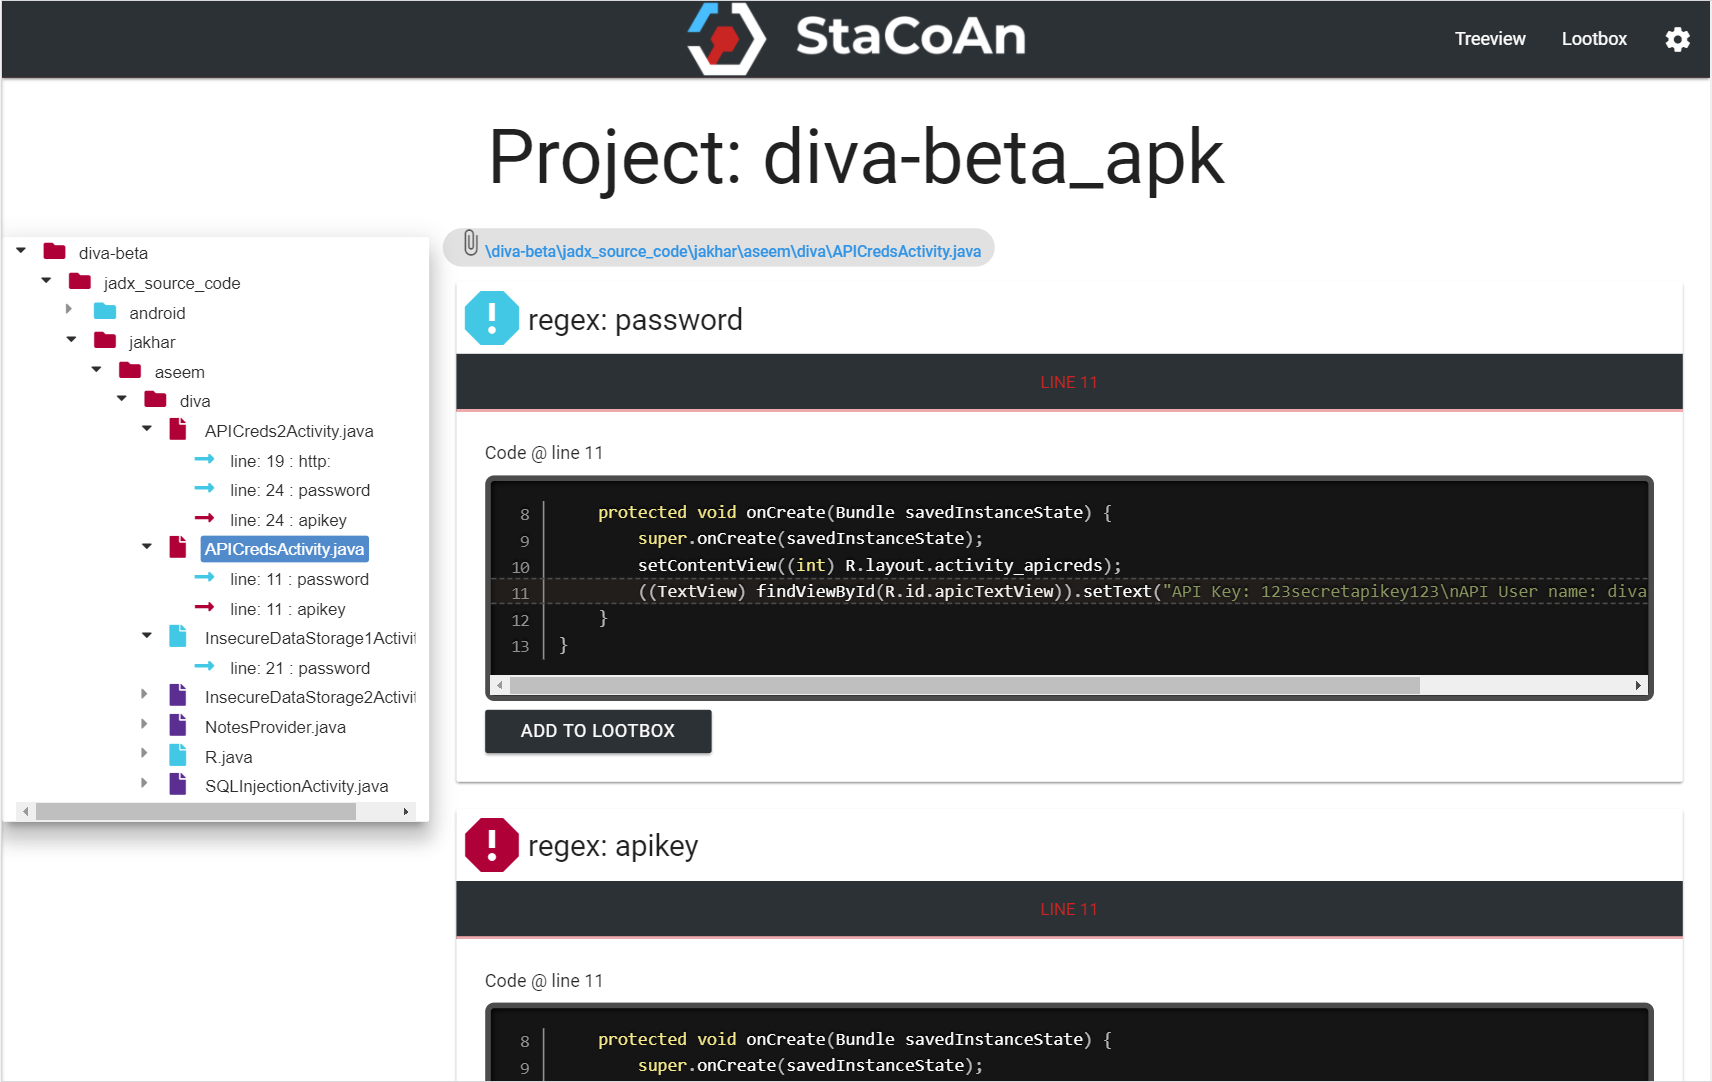 vincentcox/stacoan
StaCoAn is a crossplatform tool which aids developers, bugbounty hunters and ethical hackers performing static code analysis on mobile applications.
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 openai/codex-security
OpenAI's Codex Security CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities. npm:…
 pycqa/bandit
Bandit is a tool designed to find common security issues in Python code.
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 wireghoul/graudit
grep rough audit - source code auditing tool
 security-code-scan/security-code-scan
Vulnerability Patterns Detector for C# and VB.NET
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
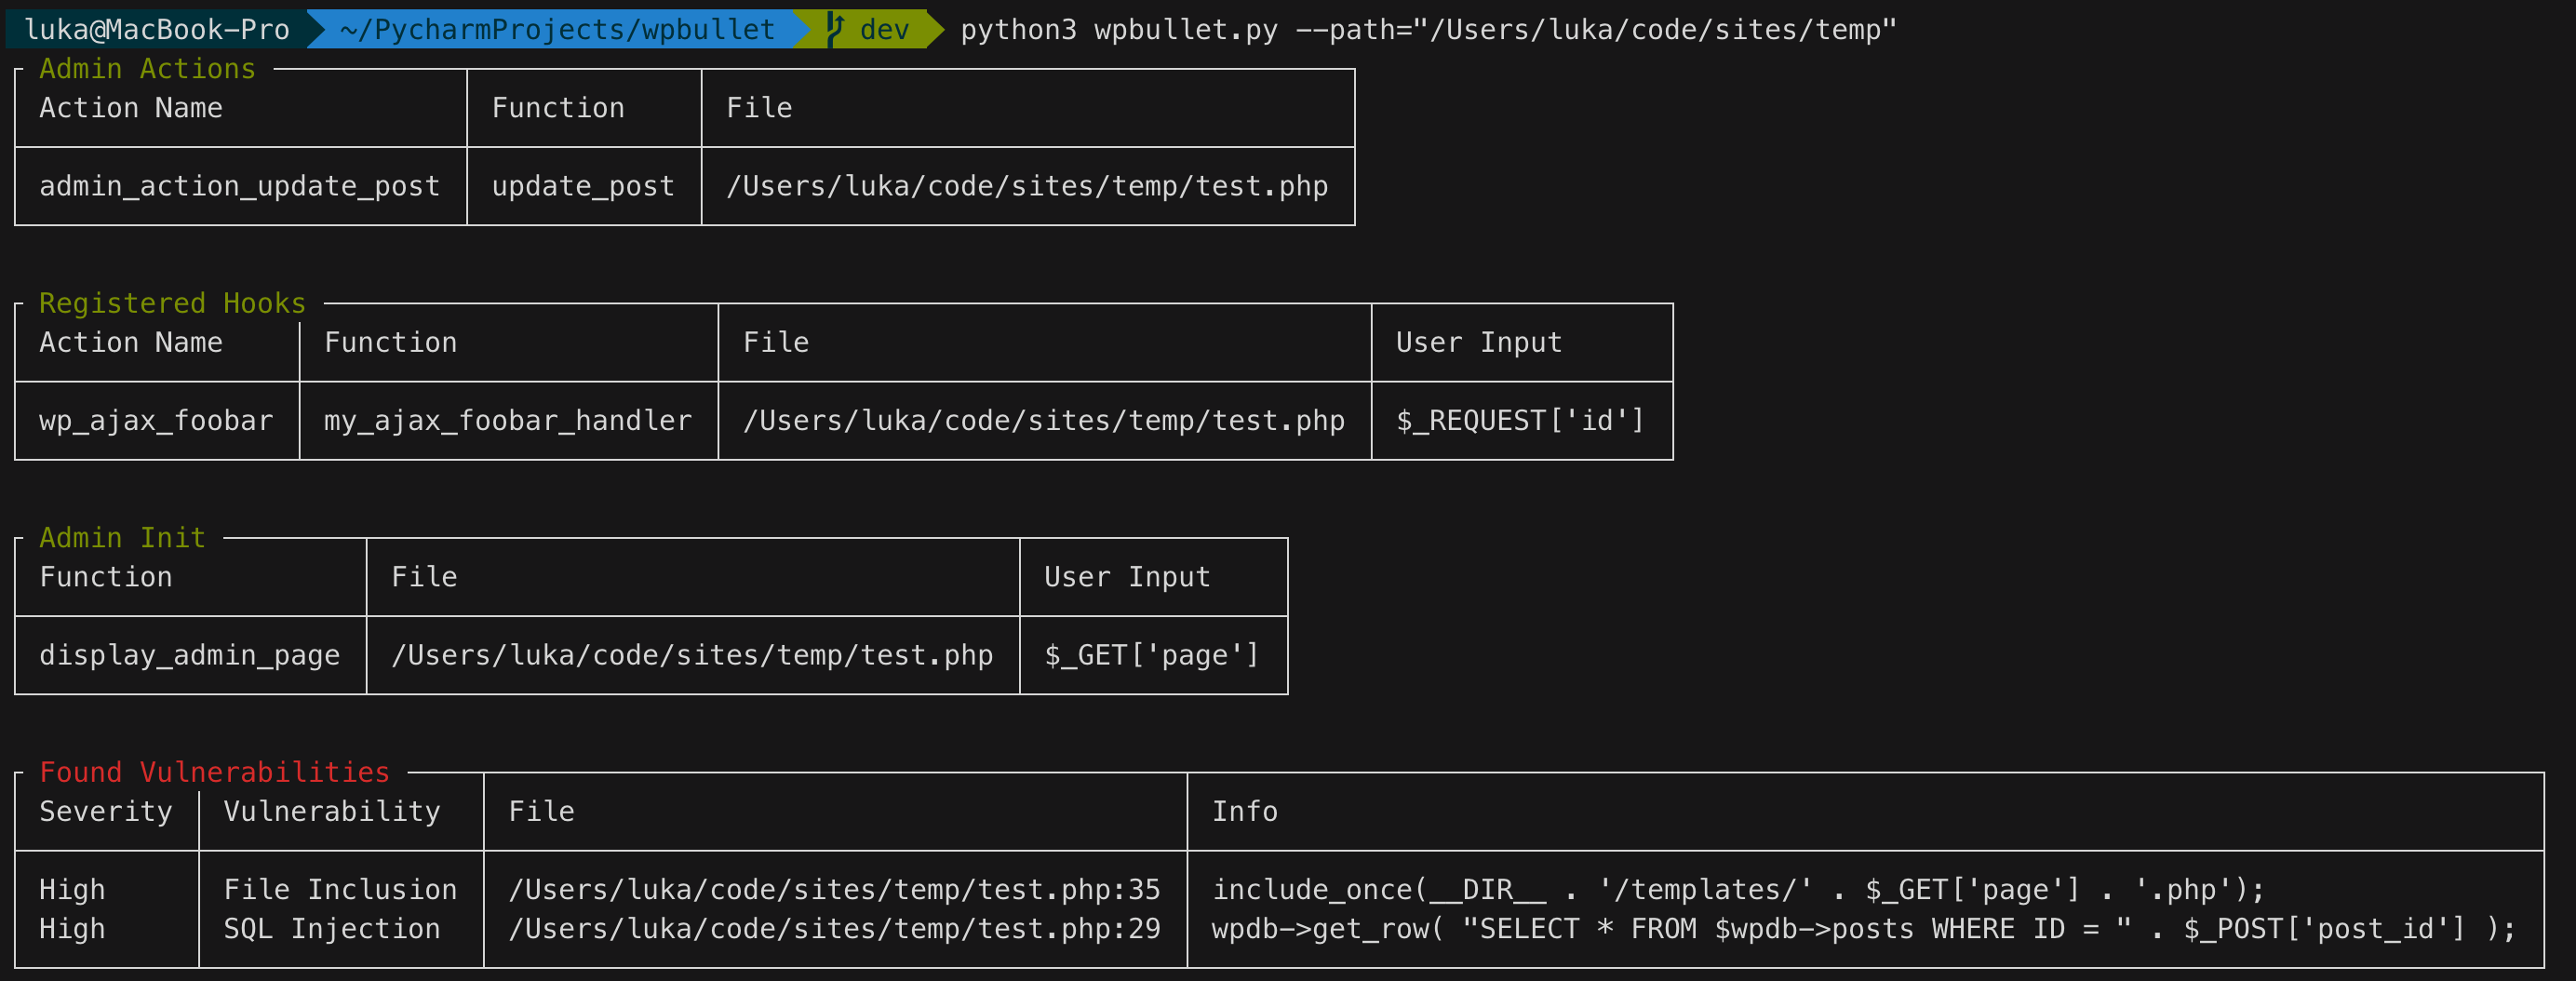 webarx-security/wpbullet
A static code analysis for WordPress (and PHP)
 trailofbits/multiplier
Indexes C/C++ build artifacts into a queryable whole-program database, exposing AST, token, and IR-level APIs for code auditing and vulnerability…
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…