
gitgalaxy
 squid-protocol1/gitgalaxy
AST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
code-analysisdevsecopsmalware-analysis+3
squid-protocol1/gitgalaxyAST-free heuristic knowledge graph engine for deep repository intelligence and zero-trust security scanning. Integrates as a GitLab CI/CD component,…
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 github/codeql
CodeQL: the libraries and queries that power security researchers around the world, as well as code scanning in GitHub Advanced Security
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
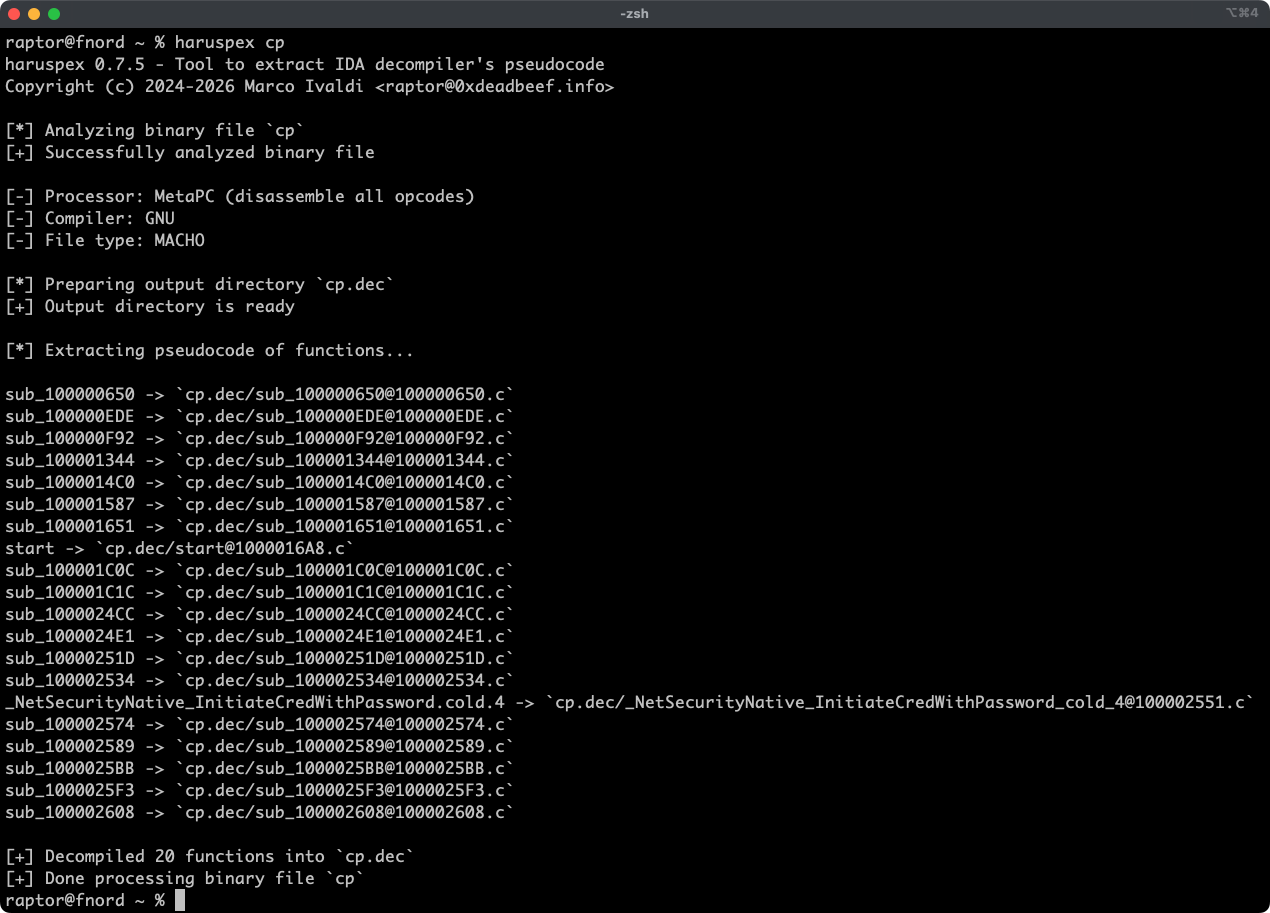 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 arian-gogani/enforcement-coverage
Finds API routes carrying weaker authorization than their siblings. Recovered CVE-2026-45316 from source. Includes the negative results.
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 gitlab-org/security-products/sast-rules
Curated Semgrep rule repository for GitLab SAST, providing static analysis patterns to detect security vulnerabilities across multiple programming…
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 rakib-nyc/nullorigin
Research-only AI watermark robustness toolkit: local reverse proxy strips C2PA/EXIF/XMP, Unicode, image/audio stego, OOXML/PDF metadata, and scans…
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…