

alter-zero
 linuztx/alter-zero
RAM efficient terminal agent harness for coding, cybersecurity, and automation.
ai-securitycode-analysiscommand-and-control+6
611 day ago
linuztx/alter-zeroRAM efficient terminal agent harness for coding, cybersecurity, and automation.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 vusec/ghostrace
Proof-of-concept and static analysis toolkit for finding speculative race condition (SCUAF) gadgets in Linux kernel. Includes 1200+ gadget dataset.
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
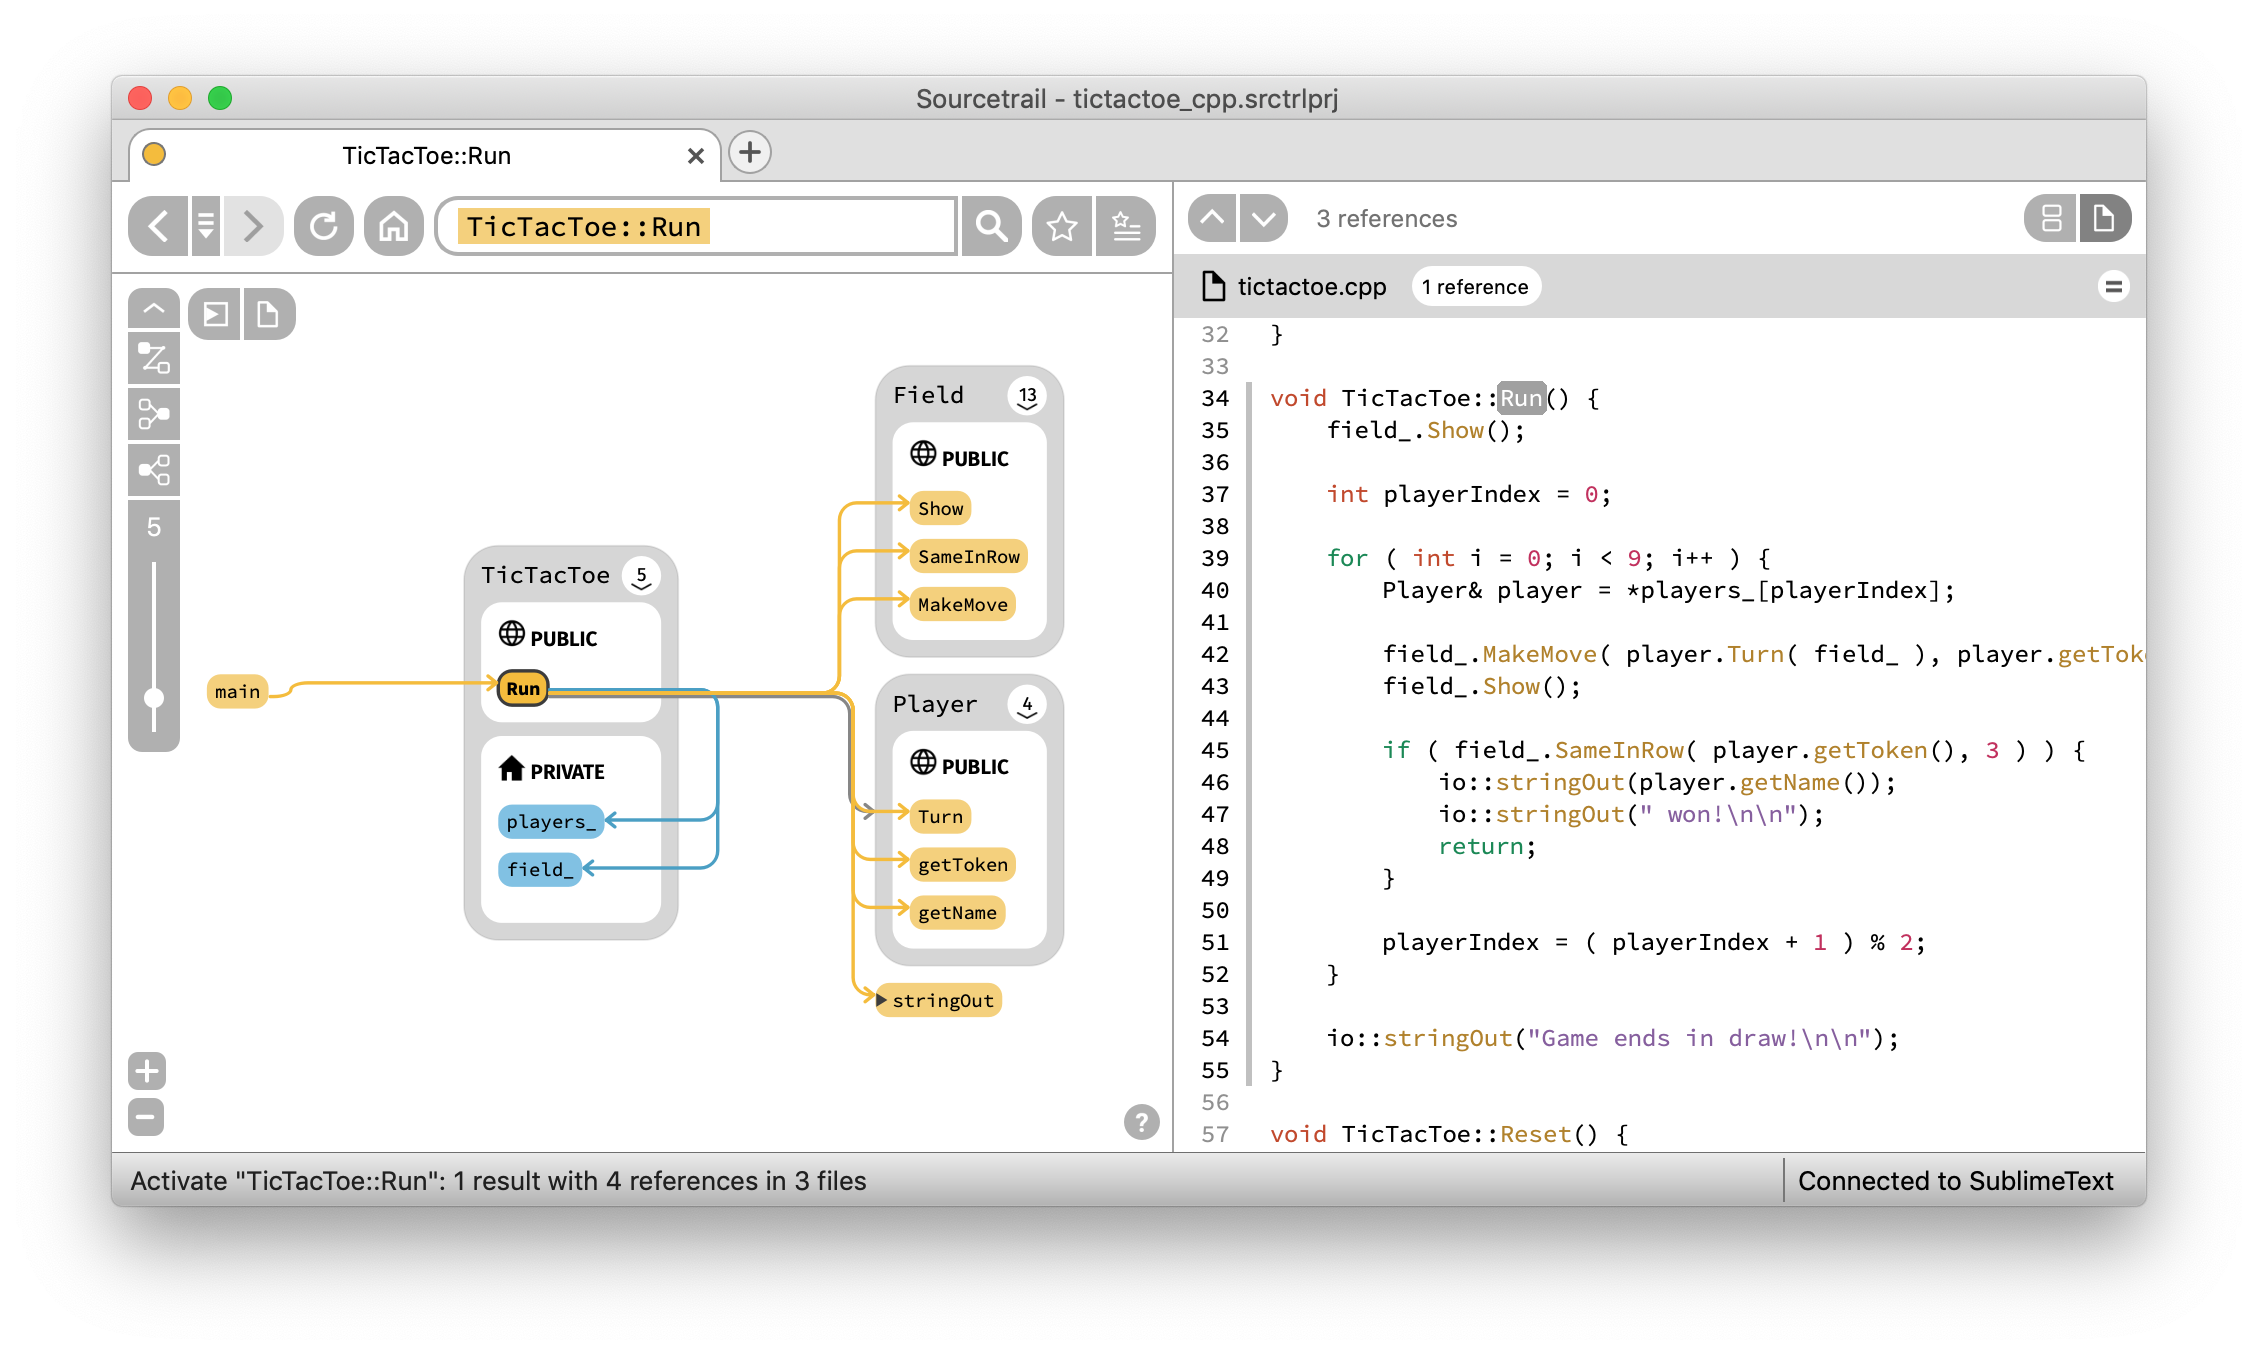 coatisoftware/sourcetrail
Sourcetrail - free and open-source interactive source explorer
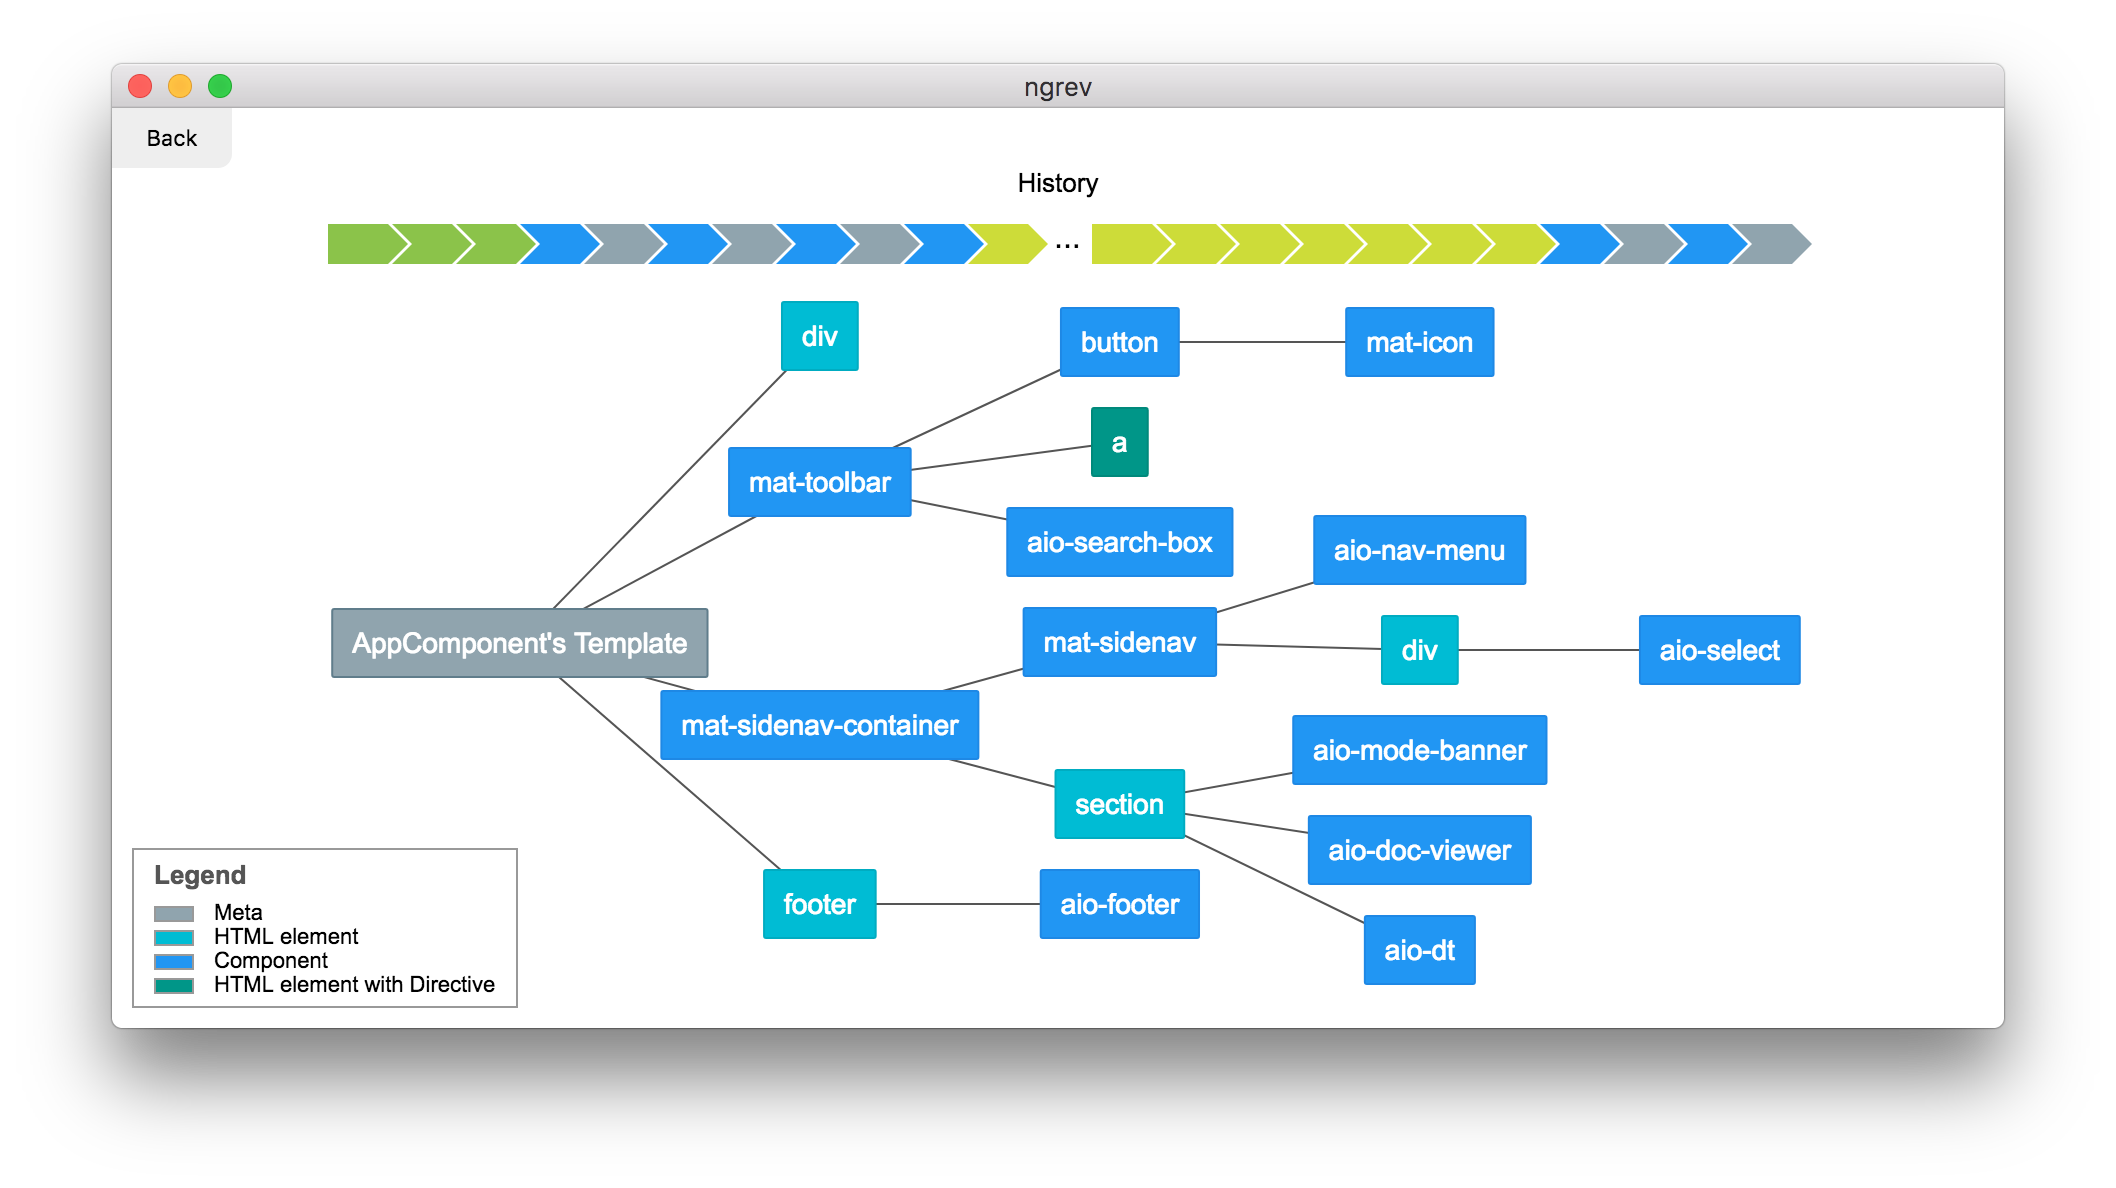 mgechev/ngrev
Tool for reverse engineering of Angular applications
 shubhamshubhankar/autosource
Automated static code analysis framework integrated with SonarQube for early vulnerability detection in source code by scanning Git repositories…